Best AI Governance Tools - Page 24

How Many AI Governance Tools Products Does G2 Track?

Total Products under this Category: 624

Category Stats (Sep 2026)

  • Average Rating: 4.66/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Harmonic Security (+0.97%) - Among all products in this category, Harmonic Security recorded the largest rating increase compared to last month

Last updated: September 26, 2026

How Does G2 Rank AI Governance Tools Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 10,600+ Authentic Reviews
  • 624+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

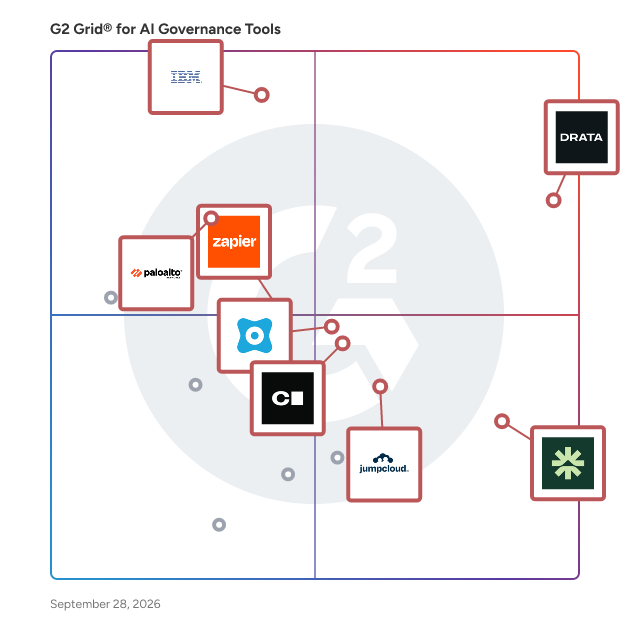
G2 Grid® for AI Governance Tools

G2 Grid® for  AI Governance Tools plotting products by satisfaction and market presence

Highlighted products: Drata, IBM watsonx.governance, Willow AI Governance Control Plane, Securiti, Cortex Cloud, JumpCloud, Coder, and Zapier.

Underlying data: [Grid® JSON](https://www.g2.com/categories/ai-governance-tools/grids.json?focus%5B%5D=drata&focus%5B%5D=ibm-watsonx-governance&focus%5B%5D=willow-ai&focus%5B%5D=securiti&focus%5B%5D=cortex-cloud&focus%5B%5D=jumpcloud&focus%5B%5D=coder&focus%5B%5D=zapier)

Kaya Governed AI Execution Platform

Kaya is the Governed AI Execution Platform for business-critical processes. It separates AI reasoning from execution: AI designs a plan, business leaders approve it, and the approved plan runs the same way every time, with an immutable audit record. Kaya delivers dependable outcomes, predictable costs, a defensible record, and transformative processes.

Who Is the Company Behind Kaya Governed AI Execution Platform?

kbie

kbie is a brand governance platform that turns a company's brand into a verified knowledge graph, keeping AI-generated content on-brand and regulation-ready. A product of Kapis AI Tech Private Limited. It works on three pillars: (1) One source of truth — one verified, machine-readable knowledge graph of your brand that every AI model reads from, instead of scattered docs; (2) Governed creation — every AI output (copy, image, campaign) is drafted from that truth and checked on-brand and compliant before it ships, so it's safe to publish by default; (3) Proof and control — per-claim provenance (Trust Layer), AEO audits of how AI describes your brand, and a learning loop where nothing enters the brand's truth without human approval. kbie is independent and model-agnostic, working across ChatGPT, Gemini, Claude and your own models. Modules: Brand Brain (a verified nine-layer brand model), Brief (on-brand content drafting), Studio (on-brand creative and images), AEO Audit, and Compliance Pulse (ad-code checks).

Who Is the Company Behind kbie?

Kelvori

Kelvori is AI governance software designed for smaller organizations to manage AI tools and risks. It starts with a free assessment of sixteen questions to identify governance gaps and generate scores across policy, risk controls, and tool management. The platform offers a centralized workspace with features like an AI register for documenting tools and use cases, risk assessments for evaluating individual applications, and a policy builder for creating tailored AI usage policies. An action tracker assigns governance tasks, while an evidence vault stores documentation, policies, and records. A governance summary generates structured reports of activities and evidence. Kelvori uses a use-case-based approach, aligning with UK ICO guidance, ISO/IEC 42001, and EU AI Act frameworks to help organizations structure governance practices. It does not provide legal advice or guarantee regulatory compliance.

Who Is the Company Behind Kelvori?

KeyForge AI

KeyForge AI is an AI-native identity governance platform designed to meet the complex needs of modern enterprises. It offers a unified control plane that manages workforce, privileged, machine, cloud, and AI-driven identities, ensuring comprehensive oversight and security. By integrating identity lifecycle management, access requests, reviews, fine-grained authorization governance, Segregation of Duties (SoD) analytics, cloud policy visibility, and just-in-time access, KeyForge AI addresses the challenges of today's hybrid enterprise environments. Key Features and Functionality: - Identity Lifecycle Management: Automates the provisioning and deprovisioning processes for various identities, including employees, contractors, bots, service accounts, and AI agents, based on policy-driven rules. - Access Request and Fulfillment: Provides intuitive interfaces for access requests, incorporating approval workflows, policy checks, and just-in-time elevation, with seamless integration through SCIM, API, file, and custom provisioning methods. - Access Reviews and Certification: Facilitates comprehensive review campaigns led by managers, application owners, and entitlement owners, featuring delegation, escalation, attestation history, and remediation tracking. - AI-Based Risk Analytics: Utilizes intelligence-led analytics to identify and prioritize risks such as toxic access, peer anomalies, over-entitlement, stale access, and policy drift across identities, roles, applications, and cloud environments. - Approval Workflows: Enables the creation of context-aware workflows for request approvals, exceptions, escalations, reassignments, and compensating controls, incorporating multi-step approvals and dynamic routing. - Connector Factory: Accelerates the onboarding of enterprise applications with a flexible connector framework supporting SCIM, REST, JDBC, files, SAP, Oracle, Workday, Salesforce, and custom enterprise applications. - Entitlement Management: Centralizes the management of entitlements, including cataloging, metadata, ownership, business descriptions, tags, sensitivity, and lifecycle governance. - Audit, Reporting, and Evidence: Delivers operational dashboards, compliance evidence, reviewer actions, certification history, and traceability from request to remediation, ensuring audit readiness. - Fine-Grained Access Governance and SoD: Goes beyond coarse roles to govern permissions, actions, policy objects, data restrictions, and Segregation of Duties conflicts at scale. - Application Access Governance: Integrates disconnected and business-critical applications into a unified governance model, providing controls centered around accounts, roles, entitlements, and ownership. - Just-In-Time and Ephemeral Access: Reduces standing privileges by supporting time-bound, purpose-bound, and approval-backed access for administrators, developers, vendors, bots, and agents. - Cloud Policy Management: Governs cloud identities, policies, secrets, and permissions across platforms, offering visibility into effective access, drift, and risk exposure. Primary Value and Solutions Provided: KeyForge AI addresses the complexities of identity governance in modern enterprises by offering a comprehensive, AI-driven platform that unifies and automates identity and access management processes. It enhances security by providing deep controls without imposing rigid operating models, ensuring that all identities—human and non-human—are governed effectively. The platform's intelligence-led decisions, embedded directly into governance operations, empower organizations to act confidently with risk insights and recommendations. By integrating various identity governance capabilities into a single control plane, KeyForge AI simplifies compliance, reduces operational overhead, and accelerates the onboarding of applications, ultimately enabling enterprises to operate securely and efficiently in the AI era.

Who Is the Company Behind KeyForge AI?
Klaveta

Klaveta is a French AI governance platform for small and mid-sized companies subject to the EU AI Act. Employees declare the AI tools they use and what they use them for. Klaveta places each use on the regulation's risk scale, generates the governance documents from the company's real context, and keeps a dated, versioned record of every measure taken. Core features: AI use register, risk qualification, AI usage policy generated from the owner's decisions, AI literacy training for teams (Article 4), regulatory deadline tracking, and an exportable evidence file. Three design principles: the inventory is declarative, so employees are never monitored; no model output is recorded without an explicit human validation; and no certification is claimed, because none exists for the EU AI Act. Database hosted in the European Union, European payment provider, French-language interface.

Who Is the Company Behind Klaveta?

Kobalt Labs

Kobalt Labs provides an AI copilot for risk and compliance teams at financial institutions.

Who Is the Company Behind Kobalt Labs?

Koi Endpoint Security

Koi Endpoint Security is a comprehensive platform designed to provide organizations with full visibility and control over all software applications installed on their endpoints. By discovering and cataloging both binary and non-binary software—including applications, code packages, AI models, OS packages, drivers, extensions, and containers—Koi enables enterprises to gain critical risk insights and effectively govern their software environment. This proactive approach allows for the identification and remediation of malicious, risky, or non-compliant software, ensuring a secure and compliant IT infrastructure. Key Features and Functionality: - Comprehensive Software Inventory: Automatically uncover and catalog all software present in the IT environment, encompassing both binary and non-binary applications. - Advanced Risk Analysis with Wings™: Utilize the proprietary Wings™ risk engine to perform in-depth analysis of software code, behavior, ownership changes, update channels, network egress, and installation sources. This enables the detection of malware, impersonation attempts, and policy deviations in real time. - Policy Management: Define and enforce organization-wide rules based on user roles, groups, and asset sensitivity. Implement approvals, cooldowns, and allow/block lists to maintain control over software installations. - Real-Time Alerts and Remediation: Detect and address malicious activity, sideloading, and risky update channels post-installation. Alert relevant stakeholders and prevent the propagation of threats across the organization. - Agentless Integration: Seamlessly integrate with existing security stacks, including Secure Web Gateways (SWG), Endpoint Detection and Response (EDR) systems, Mobile Device Management (MDM) solutions, and user-mode agents, without the need for additional agents. Primary Value and Problem Solved: Koi Endpoint Security addresses the critical challenge of managing and securing the vast array of software applications within an enterprise. Traditional security measures often lack visibility into non-binary software components, leaving organizations vulnerable to hidden malware, dangerous auto-updates, and other security risks. By providing a unified platform that offers comprehensive visibility, advanced risk analysis, and robust policy enforcement, Koi empowers organizations to regain control over their endpoints. This proactive approach not only enhances security but also ensures compliance and operational efficiency, allowing teams to utilize a wide range of software tools safely and effectively.

Who Is the Company Behind Koi Endpoint Security?

  • Seller: Koi
  • HQ Location: Tel Aviv, IL
  • LinkedIn® Page: www.linkedin.com
    212 employees on LinkedIn®

Kosmoy

Kosmoy is an AI governance platform for enterprise AI in production. It helps AI platform, security, risk and compliance teams inventory, monitor and control AI models, applications and agents. FOUR LAYERS OF CONTROL AI inventory: Register AI systems and agents with owners, providers, risk assessments and deployment context. Give teams a shared view of the AI they run. AI monitoring: Track usage, costs and behaviour across models, applications and agents. Use operational evidence to investigate issues and inform governance decisions. AI governance: Apply access controls, guardrails, model routing and logging through an AI Gateway for LLM, MCP (Model Context Protocol) and agent-to-agent traffic. AI action control: Use Action Capsule to contain autonomous agent actions with runtime isolation and a kill switch. DEPLOYMENT Run Kosmoy in your own Kubernetes environment, in the cloud or on premises. Connect inventory, policies, monitoring and runtime controls across your AI estate. START WITH ONE PRODUCTION USE CASE Bring an AI application or agent to a walkthrough. We will map its owner, model and tool access, policies, monitoring and runtime controls to your deployment requirements. Explore the platform: https://www.kosmoy.com Product documentation: https://docs.kosmoy.com Request a demo: https://www.kosmoy.com/demo/ Pricing and deployment discussion: https://www.kosmoy.com/pricing/

Who Is the Company Behind Kosmoy?

  • Seller: Kosmoy
  • HQ Location: Milan, IT
  • LinkedIn® Page: linkedin.com
    30 employees on LinkedIn®

Kovrr's AI Security and Governance Platform

The AI Security and Governance Platform connects telemetry from the browser, endpoint, and network through the AI Interaction Data Fabric into one governed view of every AI system operating across the enterprise, built to the highest privacy standards and producing the evidence leadership needs to make defensible decisions about AI at scale. Kovrr surfaces every AI asset, sanctioned or shadow, internal or third-party, then unifies discovery, policy enforcement, compliance readiness, and AI Risk Quantification (AIRQ) on one connected system.

Who Is the Company Behind Kovrr's AI Security and Governance Platform?

  • Seller: Kovrr
  • Year Founded: 2017
  • HQ Location: Tel Aviv, IL
  • Twitter: @kovrrIns
    440 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    35 employees on LinkedIn®

LangGuard

LangGuard is a deterministic runtime AI governance platform designed to provide enterprises with comprehensive oversight and control over AI agents operating within their business workflows. As AI agents increasingly perform autonomous actions—such as calling APIs, writing to databases, and triggering approvals—traditional governance infrastructures often lack the capability to monitor and manage these activities effectively. LangGuard addresses this gap by offering real-time visibility, policy enforcement, and automated remediation to ensure that AI agents operate within defined security and compliance parameters. Key Features and Functionality: - Action Surface Validation: LangGuard's SCOPE-MCP maps and classifies the complete action surface of multi-agent workflows, identifying every tool connected, operation exposed, and system of record accessible. This pre-classification aligns with Segregation of Duties (SoD) rules and regulatory requirements, providing a clear understanding of potential exposures before they become incidents. - Action Authorization Enforcement: The Arbiter component evaluates each agent action before execution. Safe actions proceed without delay, while those crossing SoD boundaries, exceeding authorization thresholds, or triggering compliance rules are routed to designated human approvers for validation prior to completion. This proactive approach ensures governance is enforced in real-time, with an automatic audit trail for transparency. - Comprehensive Visibility: LangGuard offers a centralized control plane that inventories, governs, orchestrates, and manages heterogeneous AI agents across various vendors and domains. It provides an authoritative registry of all AI agents in production, detailing ownership, tool connections, and activity logs, facilitating proactive control and incident response. Primary Value and Problem Solved: LangGuard empowers organizations to confidently deploy AI agents by providing deterministic governance over their actions, thereby mitigating risks associated with autonomous AI operations. By ensuring that every agent action is authorized and compliant with organizational policies and regulatory standards, LangGuard prevents unauthorized activities, reduces the potential for security breaches, and simplifies audit processes. This comprehensive oversight enables enterprises to harness the benefits of AI while maintaining control, compliance, and trust in their AI-driven processes.

Who Is the Company Behind LangGuard?

  • Seller: LangGuard
  • Year Founded: 2025
  • HQ Location: San Francisco, US
  • LinkedIn® Page: linkedin.com
    4 employees on LinkedIn®

LeanMCP

LeanMCP is an AI gateway and runtime governance layer for MCP (Model Context Protocol) agents. It sits between applications and LLM providers, capturing every tool call with per-agent identity tokens, audit trails, and access policy enforcement. Engineering and compliance teams use LeanMCP to observe, govern, and audit agent behavior in production environments, including meeting requirements under frameworks such as IMDA MGF and MAS FEAT.

Who Is the Company Behind LeanMCP?

Legalithm

Legalithm: EU digital compliance for AI and connected products Legalithm is compliance software for teams building or shipping AI and digital products into the European Union. Modern products rarely fall under a single regulation. An AI-enabled, internet-connected application can be caught by the EU AI Act, the Cyber Resilience Act, and the European Accessibility Act at the same time, each with its own scope, obligations, documentation, and deadlines. Legalithm brings those overlapping regimes into one platform with one consistent method: work out what applies, classify it, map the obligations to the exact article, and produce documentation you can actually defend. It is built for the teams the enterprise GRC suites overlook, startups and small and mid-sized companies that cannot afford a Big-Four engagement or a six-figure governance platform but still have to get this right. There is no demo gate and no mandatory sales call. You can run the assessment and see your obligations before you ever create an account. Three regulations, one platform EU AI Act. Check whether the AI Act applies to your system, classify its risk tier (including Annex III and high-risk cases), and map the resulting obligations to the specific articles they come from. Legalithm generates the Annex IV technical documentation an auditor or notified body will ask for, supports Article 50 transparency duties, and produces machine-readable content marking (C2PA) for AI-generated media. Cyber Resilience Act (CRA). Scope your products with digital elements against the CRA, map the security-by-design and vulnerability-handling duties, and get your reporting readiness and technical documentation in order before the obligations bite. European Accessibility Act (EAA). Determine whether the EAA applies to your product or service, map the accessibility requirements it imposes, and produce the conformity information it requires. Deterministic, and cited to the article Compliance classification is not a place for a language model to guess. Legalithm's classification is deterministic: the same answers always produce the same verdict, and every verdict cites the specific article of the regulation it was derived from. An assessment is reproducible and reviewable, your counsel or a regulator can trace exactly why a system landed where it did, rather than trusting an opaque model output. The judgment stays yours; Legalithm makes it structured, sourced, and defensible. A record you can prove, not just produce The output of an assessment is a dated, cited compliance record, and its integrity is verifiable. Each record carries a SHA-256 hash and, when you sign it, a detached Ed25519 signature whose key you hold. Anyone, your customer, an auditor, a regulator, can verify offline that the record reads exactly as it did the day it was produced, with no account, no network, and no need to trust Legalithm. A later edit breaks verification. This is what turns "we are compliant" into "here is a record that proves it, and proves it has not been altered." Built for a moving target EU regulation does not sit still. Standards are still being written and amendments keep landing. Legalithm pins each assessment to the version of the regulation text it rests on and flags when an assessment relies on text that has since changed, so a record produced months ago does not quietly go stale without anyone noticing. Deep where it counts: health-AI and medical devices Legalithm has particular depth in health-AI and medical devices, the hardest intersection in the field, where the AI Act, MDR and IVDR, the CRA for connected devices, and accessibility rules all stack on the same product. If you build medical or health software with AI, this is where generic governance tools stop being useful and Legalithm is purpose-built. Developer-native, not just a dashboard Compliance should live where your team already works. Alongside the web app, Legalithm ships a command-line tool, a Model Context Protocol (MCP) server, and a WordPress plugin, so classification, record generation, content marking, and offline verification run inside your codebase, your CI, your AI agents, and your CMS, not only in a separate portal. Trust and practicalities EU-hosted and GDPR-aligned. Self-serve, with the full assessment available before signup. Start free. At a glance Three EU regimes in one platform: AI Act, Cyber Resilience Act, European Accessibility Act Applicability checks and deterministic risk classification, cited to the article Obligation mapping and technical documentation, including Annex IV for the AI Act Dated, cited compliance record with offline SHA-256 and Ed25519 verification Version-pinning and reclassification alerts when a regulation changes Article 50 transparency and C2PA content marking CRA scoping, vulnerability-reporting readiness, and conformity documentation EAA applicability and accessibility conformity information Developer surfaces: CLI, MCP server, WordPress plugin Purpose-built depth for health-AI and medical devices (AI Act with MDR/IVDR)

Who Is the Company Behind Legalithm?

Shalaka Joshi
SJ
Researched and written by Shalaka Joshi
Updated April 9, 2026