Best Enterprise Security Information and Event Management (SIEM) Software - Page 2

How Many Security Information and Event Management (SIEM) Software Products Does G2 Track?

Total Products under this Category: 153

Category Stats (Nov 2026)

  • Average Rating: 4.47/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Singularity AI SIEM (+2.27%) - Among all products in this category, Singularity AI SIEM recorded the largest rating increase compared to last month

Last updated: November 02, 2026

How Does G2 Rank Security Information and Event Management (SIEM) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,600+ Authentic Reviews
  • 153+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

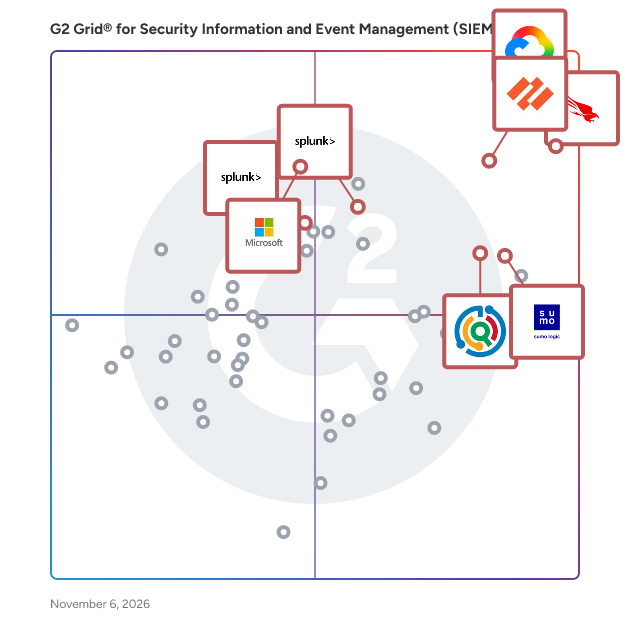
G2 Grid® for Security Information and Event Management (SIEM) Software

G2 Grid® for Security Information and Event Management (SIEM) Software plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Google Security Operations, Palo Alto Cortex XSIAM, Sumo Logic, Splunk Enterprise Security, Microsoft Sentinel, ManageEngine ADAudit Plus, and Splunk Enterprise.

Underlying data: [Grid® JSON](https://www.g2.com/categories/security-information-and-event-management-siem/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=google-security-operations&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=sumo-logic&focus%5B%5D=splunk-enterprise-security&focus%5B%5D=microsoft-sentinel&focus%5B%5D=manageengine-adaudit-plus&focus%5B%5D=splunk-enterprise&segment=enterprise)

NetWitness Platform

NetWitness is a comprehensive threat detection, investigation and response platform that combines visibility, analytics, insight, and automation into a single solution. It collects and analyzes data across all capture points (logs, packets, netflow, endpoint and IoT) and computing platforms (physical, virtual and cloud), enriching data with threat intelligence and business context.

Average Rating: 3.9/5.0

Total Reviews: 23

How Do G2 Users Rate NetWitness Platform?

  • Activity Monitoring: 8.3/10 (Category avg: 9.2/10)
  • Data Examination: 8.3/10 (Category avg: 8.7/10)
  • Ease of Use: 7.7/10 (Category avg: 8.8/10)
  • Log Management: 8.6/10 (Category avg: 9.2/10)

Who Is the Company Behind NetWitness Platform?

Who Uses This Product?

  • Company Size: 54% Large, 33% Medium

What Do G2 Reviewers Say About NetWitness Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the network packet capture feature of NetWitness for effective forensic investigations and threat hunting.
  • Users appreciate the centralized threat detection capabilities of NetWitness Platform, enhancing efficiency in threat hunting across various data sources.
  • Users value the centralized view provided by NetWitness Platform, simplifying threat hunting across various data sources.
  • Users value the centralized threat hunting capabilities of NetWitness Platform, streamlining their cybersecurity efforts effectively.
  • Users value the full network packet capture capability of NetWitness, enhancing deep forensic investigation significantly.
Cons
  • Users find the complex implementation of NetWitness Platform challenging, needing extensive technical expertise for setup and upgrades.
  • Users find the complexity of initial deployment and upgrades challenging, requiring significant technical expertise and causing instability.
  • Users find the initial setup complex, often needing advanced expertise, which can hinder deployment and upgrades.
  • Users face complex deployment difficulties with the NetWitness Platform, needing substantial expertise for initial setup and upgrades.
  • Users face complex initial setup and deployment challenges, often needing significant expertise for effective use.

What Are Recent G2 Reviews of NetWitness Platform?

What Are G2 Users Discussing About NetWitness Platform?

Cynet

Cynet is the unified, AI-powered cybersecurity platform that delivers robust and comprehensive protection for security teams while maximizing operational efficiency for managed service providers (MSPs). This platform consolidates a wide array of security capabilities into a single, user-friendly interface, ensuring that organizations can effectively safeguard their digital assets without the complexity often associated with multi-solution environments. Cynet’s platform simplifies security management by integrating various functionalities, such as endpoint protection, threat detection, and incident response, into one cohesive system. This integration not only streamlines operations but also allows organizations to allocate their resources more effectively, ultimately enhancing their overall security posture. One of the standout features of Cynet’s platform is its remarkable performance in the MITRE ATT&CK Evaluations. Cynet delivered 100% visibility and 100% analytic coverage without requiring any configuration changes three years in a row. This capability ensures that organizations can monitor their environments comprehensively and respond to threats with precision. The platform’s built-in analytics and reporting tools provide actionable insights, enabling users to make informed decisions about their cybersecurity strategies. Additionally, Cynet offers 24/7 expert support, which is crucial for organizations that may not have in-house cybersecurity expertise. This round-the-clock assistance ensures that users can quickly address any security incidents or concerns, minimizing potential downtime and damage. The combination of advanced technology and dedicated support positions Cynet as a valuable partner for SMEs and service providers looking to enhance their cybersecurity measures. In summary, Cynet’s unified, AI-powered cybersecurity platform stands out in the crowded cybersecurity market by offering a unified solution tailored to the needs of MSPs. Its comprehensive features, exceptional performance in industry evaluations, and continuous expert support make it a compelling choice for organizations seeking to bolster their cybersecurity defenses while maintaining operational efficiency.

Average Rating: 4.7/5.0

Total Reviews: 218

How Do G2 Users Rate Cynet?

  • Activity Monitoring: 9.4/10 (Category avg: 9.2/10)
  • Data Examination: 8.8/10 (Category avg: 8.7/10)
  • Ease of Use: 9.1/10 (Category avg: 8.8/10)
  • Log Management: 8.9/10 (Category avg: 9.2/10)

Who Is the Company Behind Cynet?

  • Seller: Cynet
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    335 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: SOC Analyst, Technical Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 58% Medium, 30% Small

What Do G2 Reviewers Say About Cynet?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Cynet, enjoying its simple implementation and daily operation.
  • Users appreciate the responsive SOC team and improved dashboard features, enhancing control and reducing notification noise.
  • Users value the effective threat detection of Cynet, appreciating its responsiveness and improved dashboard features.
  • Users commend Cynet's responsive customer support, quickly resolving issues and enhancing the overall experience with the product.
  • Users commend Cynet for its robust security features, seamless implementation, and excellent support, enhancing overall cybersecurity management.
Cons
  • Users find limited customization options in dashboards and integrations, affecting their overall experience with Cynet.
  • Users note feature limitations in customization and integration options, which may hinder user experience and flexibility.
  • Users find a lack of customization in dashboards and features, limiting their ability to tailor the platform effectively.
  • Users experience limited features with Cynet, particularly in reporting options and third-party integrations.
  • Users note that some missing features hinder full integration and customization, impacting overall user experience.

What Are Recent G2 Reviews of Cynet?

What Are G2 Users Discussing About Cynet?

Cisco Security Manager

Advanced Security Manager is a computer security software that secures information from unwanted intruders in a computer.

Average Rating: 4.3/5.0

Total Reviews: 21

How Do G2 Users Rate Cisco Security Manager?

  • Activity Monitoring: 8.5/10 (Category avg: 9.2/10)
  • Data Examination: 8.0/10 (Category avg: 8.7/10)
  • Ease of Use: 8.8/10 (Category avg: 8.8/10)
  • Log Management: 8.6/10 (Category avg: 9.2/10)

Who Is the Company Behind Cisco Security Manager?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO
  • Phone: 847-678-6600

Who Uses This Product?

  • Company Size: 52% Large, 43% Medium

What Are Recent G2 Reviews of Cisco Security Manager?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Pandora FMS

Pandora FMS is a unified monitoring and observability platform designed to consolidate visibility, alerting, reporting, and automation across heterogeneous IT environments. Instead of combining multiple point tools for networks, servers, applications, and cloud services, Pandora FMS centralizes data collection and operational workflows in a single console, reducing integration effort and operational complexity in on-premise, hybrid, and multi-cloud architectures. The platform collects telemetry using multiple methods, including agents, remote checks, standard protocols (e.g., SNMP/WMI), APIs, and log/event ingestion. This enables teams to monitor infrastructure and services end-to-end, correlate signals, and maintain consistent alerting policies and dashboards across distributed estates. Pandora FMS also supports capacity and trend analysis to anticipate resource constraints and identify recurring patterns, and includes AI-assisted capabilities for anomaly detection and automated thresholds to surface hard-to-spot operational signals. Pandora FMS is extensible through a large plugin ecosystem (500+ plugins and integrations), covering a wide range of enterprise and infrastructure technologies such as SAP, Oracle, Citrix, JBoss, VMware, AWS, SQL Server, Red Hat, and WebSphere. This extensibility helps organizations standardize monitoring across legacy and modern stacks without redesigning their monitoring approach per technology. Core capabilities: -Unified monitoring for networks, servers, applications, cloud services, endpoints, and logs -Centralized alerting, event correlation, dashboards, and scheduled reporting -Flexible data collection via agents, remote checks, APIs, and plugins -Scalability for distributed environments and large numbers of monitored elements -Analytics for trend/capacity planning plus AI-assisted anomaly detection and dynamic thresholds -A key differentiator is direct vendor support, which simplifies escalation and ensures continuity of expertise for deployment, tuning, and ongoing operations.

Average Rating: 4.6/5.0

Total Reviews: 226

How Do G2 Users Rate Pandora FMS?

  • Activity Monitoring: 10.0/10 (Category avg: 9.2/10)
  • Data Examination: 8.3/10 (Category avg: 8.7/10)
  • Ease of Use: 9.1/10 (Category avg: 8.8/10)
  • Log Management: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Pandora FMS?

  • Seller: Pandora FMS
  • Company Website:
  • Year Founded: 2004
  • HQ Location: Madrid, Spain
  • LinkedIn® Page: www.linkedin.com
    56 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Data Analyst
  • Top Industries: Information Technology and Services, Telecommunications
  • Company Size: 50% Medium, 37% Small

What Do G2 Reviewers Say About Pandora FMS?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the flexibility of monitoring with Pandora FMS, enabling customized alerts, dashboards, and comprehensive data visibility.
  • Users appreciate the ease of use of Pandora FMS, enabling straightforward monitoring and quick issue resolution.
  • Users value the real-time monitoring capabilities of Pandora FMS, ensuring timely alerts and efficient data management.
  • Users value the flexibility of Pandora FMS, enabling customizable monitoring and adaptable solutions for diverse needs.
  • Users value the real-time network monitoring of Pandora FMS, enhancing control and improving incident response across multiple locations.
Cons
  • Users find the learning curve steep due to a lack of template support and unclear documentation.
  • Users struggle with the complex setup of Pandora FMS, requiring time and expertise for proper configuration.
  • Users find learning difficulty in mastering all features, especially with Grafana integration and advanced monitoring setups.
  • Users find difficult learning curves due to unclear documentation and extensive features of Pandora FMS.
  • Users find the complex configuration of Pandora FMS time-consuming, especially when setting up advanced monitoring features.

What Are Recent G2 Reviews of Pandora FMS?

What Are G2 Users Discussing About Pandora FMS?

LogRhythm SIEM

Rapidly deploy LogRhythm SIEM, the leading self-hosted SIEM, to secure your organization with powerful detections, synchronized threat intelligence, automated workflows, and achieve faster, more accurate threat detection, investigation, and response (TDIR).

Average Rating: 4.2/5.0

Total Reviews: 137

How Do G2 Users Rate LogRhythm SIEM?

  • Activity Monitoring: 8.9/10 (Category avg: 9.2/10)
  • Data Examination: 8.4/10 (Category avg: 8.7/10)
  • Ease of Use: 8.3/10 (Category avg: 8.8/10)
  • Log Management: 9.0/10 (Category avg: 9.2/10)

Who Is the Company Behind LogRhythm SIEM?

  • Seller: Exabeam
  • Year Founded: 2013
  • HQ Location: Broomfield, CO
  • LinkedIn® Page: www.linkedin.com
    785 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Information Security Analyst, Cyber Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 40% Large, 40% Medium

What Are Recent G2 Reviews of LogRhythm SIEM?

What Are G2 Users Discussing About LogRhythm SIEM?

Graylog

SIEM and log management in one platform Graylog helps security and IT teams detect, investigate, and respond to threats faster, using explainable AI and real-time data correlation to turn large volumes of log data into decisions they can act on. More than 60,000 organizations worldwide use Graylog for visibility and control over their IT environments. The problem Security analysts and IT professionals spend their days sifting through vast amounts of log data to find the anomalies that matter, track incidents, and prove compliance with regulatory standards. Most of that data is noise. -Too many alerts that do not matter, and the one that does is buried. -Forensic evidence scattered across tools, so investigations stall. -Audit documentation assembled by hand the week before the deadline. Catch the patterns rules miss Anomaly detection flags unusual patterns in your data so your team sees behavior that signature-based rules leave in the blind spot. Real-time correlation connects related events as they arrive. Investigations that build themselves Guided investigations walk analysts through complex incidents. Automated workflows handle the repetitive tasks, and AI-driven summaries surface the affected assets, the incident timeline, and the high-priority findings. Analysts focus on what matters instead of excessive data. Work the alerts that matter first Risk scores rank each alert by the severity of what fired and the importance of the assets involved, so a port scan against a database of client PII outranks the same scan against a user laptop. With centralized log management, every log stays a single log, giving your team the historic evidence to complete forensic investigations in one place. One platform, three products Graylog fits the team you have: -Graylog Open for log management on an open foundation. -Graylog Enterprise for IT operations and log management at scale. -Graylog Security for detection, investigation, and response.

Average Rating: 4.4/5.0

Total Reviews: 115

How Do G2 Users Rate Graylog?

  • Activity Monitoring: 8.7/10 (Category avg: 9.2/10)
  • Data Examination: 8.3/10 (Category avg: 8.7/10)
  • Ease of Use: 8.4/10 (Category avg: 8.8/10)
  • Log Management: 9.1/10 (Category avg: 9.2/10)

Who Is the Company Behind Graylog?

  • Seller: Graylog
  • Company Website:
  • Year Founded: 2009
  • HQ Location: Houston, US
  • LinkedIn® Page: www.linkedin.com
    124 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 42% Medium, 34% Small

What Do G2 Reviewers Say About Graylog?

AI-generated summary from verified user reviews

Pros
  • Users find Graylog to be reliable and cost-effective, successfully meeting industry standards for their needs.
  • Users value the detailed insights Graylog provides, significantly enhancing their debugging efficiency for complex issues.
  • Users find the extensive detail for APIs invaluable for effective debugging in complex scenarios.
  • Users find the extensive API detail invaluable for effective debugging, preventing dead ends in complex processes.
  • Users appreciate the reliable and cost-effective pricing of Graylog, which meets industry standards effectively.
Cons
  • Users experience complexity in Graylog, often wasting time on debugging instead of saving it during API response reviews.
  • Users face debugging difficulties with Graylog, leading to time wasted instead of efficient troubleshooting.
  • Users note that integration issues with multiple platforms can hinder the effectiveness and usability of Graylog.
  • Users find the learning curve steep with Graylog, often leading to time-consuming debugging and review processes.
  • Users find that the time consumption when using Graylog can hinder productivity, especially during debugging and API review.

What Are Recent G2 Reviews of Graylog?

What Are G2 Users Discussing About Graylog?

LevelBlue USM Anywhere

LevelBlue USM Anywhere is a cloud-based security management solution that accelerates and centralizes threat detection, incident response, and compliance management for your cloud, hybrid cloud, and on-premises environments. USM Anywhere includes purpose-built cloud sensors that natively monitor your Amazon Web Services (AWS) and Microsoft Azure cloud environments. On premises, lightweight virtual sensors run on Microsoft Hyper-V and VMware ESXi to monitor your virtual private cloud and physical IT infrastructure. With USM Anywhere, you can rapidly deploy sensors into your cloud and on-premises environments while centrally managing data collection, security analysis, and threat detection from the AlienVault Secure Cloud. Five Essential Security Capabilities in a Single SaaS Platform AlienVault USM Anywhere provides five essential security capabilities in a single SaaS solution, giving you everything you need for threat detection, incident response, and compliance management—all in a single pane of glass. With USM Anywhere, you can focus on finding and responding to threats, not managing software. An elastic, cloud-based security solution, USM Anywhere can readily scale to meet your threat detection needs as your hybrid cloud environment changes and grows. 1. Asset Discovery 2. Vulnerability Assessment 3. Intrusion Detection 4. Behavioral Monitoring 5. SIEM

Average Rating: 4.4/5.0

Total Reviews: 102

How Do G2 Users Rate LevelBlue USM Anywhere?

  • Activity Monitoring: 8.9/10 (Category avg: 9.2/10)
  • Data Examination: 8.4/10 (Category avg: 8.7/10)
  • Ease of Use: 8.3/10 (Category avg: 8.8/10)
  • Log Management: 8.9/10 (Category avg: 9.2/10)

Who Is the Company Behind LevelBlue USM Anywhere?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 62% Medium, 20% Small

What Are Recent G2 Reviews of LevelBlue USM Anywhere?

What Are G2 Users Discussing About LevelBlue USM Anywhere?

SolarWinds Security Event Manager

Security Event Manager (SEM) is a powerful, real-time Security Information and Event Management (SIEM) solution designed to act as a virtual Security Operations Center (SOC). It provides active monitoring and automated threat detection across multi-vendor network devices, servers, workstations, and applications. SEM is delivered as a downloadable virtual appliance for rapid deployment, and allows IT teams to centralize log data and enable real-time event correlation right out of the box. SEM goes beyond simple alerting by offering automated remediation actions. When suspicious behavior is detected, the platform can automatically block malicious IPs, disable compromised user accounts, kill unauthorized applications, or detach unmanaged USB devices via its integrated USB Defender. This immediate response capability significantly reduces the window of vulnerability during a cyber-attack. To ensure deep visibility, SEM features built-in File Integrity Monitoring (FIM), allowing you to track sensitive file changes, deletions, and registry modifications. The platform also streamlines audit preparation with hundreds of pre-built, out-of-the-box compliance reports for major regulatory frameworks, including HIPAA, PCI DSS, SOX, ISO, DISA STIGs, and FISMA. With its intuitive text-based searching and integrated threat intelligence feed, SEM normalizes disparate log data into a readable format. This enables faster forensic analysis and historical searching, helping your team identify patterns from known bad actors and strengthen your overall security posture. Whether you are managing internal threats or external breaches, SolarWinds SEM provides the essential tools to detect, respond, and report with confidence. For organizations seeking tailored security control, SEM is highly effective as a standalone SIEM tool, providing dedicated log management and incident response. However, for those looking to eliminate silos between security and IT operations, SEM can also function as a core component of SolarWinds Observability.

Average Rating: 4.0/5.0

Total Reviews: 71

How Do G2 Users Rate SolarWinds Security Event Manager?

  • Activity Monitoring: 9.2/10 (Category avg: 9.2/10)
  • Data Examination: 8.5/10 (Category avg: 8.7/10)
  • Ease of Use: 8.2/10 (Category avg: 8.8/10)
  • Log Management: 8.9/10 (Category avg: 9.2/10)

Who Is the Company Behind SolarWinds Security Event Manager?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 51% Large, 39% Medium

What Do G2 Reviewers Say About SolarWinds Security Event Manager?

AI-generated summary from verified user reviews

Pros
  • Users praise the detection efficiency of SolarWinds Security Event Manager due to its ease of use and simple device integration.
  • Users value the ease of use of SolarWinds Security Event Manager, especially for admin tasks like adding devices.
Cons
  • Users find the licensing costs complex and note limited expert support in their region, impacting usability.
  • Users find that customer support is inadequate, particularly in terms of expert assistance and online resources.

What Are Recent G2 Reviews of SolarWinds Security Event Manager?

What Are G2 Users Discussing About SolarWinds Security Event Manager?

Logsign Unified SO Platform

Logsign Unified SO Platform integrates next-gen SIEM, threat intelligence, UEBA, and SOAR and empowers organizations to optimize and streamline their cybersecurity operations. In addition to that, the platform offers seamless integration capabilities, allowing them to effortlessly integrate their existing security software and leverage our vast integration library, expanding the Logsign USO Platform's functionality and providing a comprehensive security management experience. With these extensive capabilities, it allows organizations to improve their security posture and ensure compliance with relevant regulations and standards. - Easy-to-deploy, easy-to-use Unified SO Platform for all sizes of enterprises. - Enterprise-grade scalability, high availability - Cluster SIEM, big data infrastructure.  - On-premise solution. - 500+ predefined integrations and free plugin service. - Collects & stores high volumes of data. - Threat hunting, fast search & investigation, advanced behaviour analysis, IOC detection. - Threat Intelligence and UEBA embedded. - Real-time detection & prevention, wide correlation library based on Mitre Att&ck framework.  - Real-time monitoring, predefined dashboards & reports, meeting Compliance Requirements (PCI DSS, ISO 27001, HIPAA, SOX, and more). - Automated notifications, automated Incident response - Incident Cycle Management - Incident Response - Multiple pricing options without capacity or log source limit, feature-based pricing.

Average Rating: 4.7/5.0

Total Reviews: 53

How Do G2 Users Rate Logsign Unified SO Platform?

  • Activity Monitoring: 9.1/10 (Category avg: 9.2/10)
  • Data Examination: 8.7/10 (Category avg: 8.7/10)
  • Ease of Use: 9.6/10 (Category avg: 8.8/10)
  • Log Management: 9.6/10 (Category avg: 9.2/10)

Who Is the Company Behind Logsign Unified SO Platform?

  • Seller: Logsign
  • Year Founded: 2010
  • HQ Location: Hague, Netherlands, NL
  • LinkedIn® Page: www.linkedin.com
    41 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 50% Medium, 31% Small

What Are Recent G2 Reviews of Logsign Unified SO Platform?

What Are G2 Users Discussing About Logsign Unified SO Platform?

Trellix Enterprise Security Manager

Trellix EnterprisTrellix Enterprise Security Manager (ESM) is a highly scalable Security Information and Event Management (SIEM) solution delivering real-time visibility across systems, networks, databases, and applications. Engineered for speed, ESM collects and correlates data from over 460 integrated technologies to provide actionable threat intelligence. It stores billions of events, offering immediate ad-hoc query capabilities, rapid forensics, and historical rule validation without impacting performance. ESM empowers security operations center (SOC) teams to automate and coordinate incident response through advanced bi-directional integrations. To streamline operations, the platform includes hundreds of customizable dashboards, reports, and correlation rules. Robust compliance features help organizations seamlessly address regulatory frameworks. With flexible hybrid deployment options (on-premises, virtual, or cloud), Trellix ESM accelerates threat detection, prioritizes alerts, and unifies security operations within a single centralized platform.

Average Rating: 4.1/5.0

Total Reviews: 37

How Do G2 Users Rate Trellix Enterprise Security Manager?

  • Activity Monitoring: 7.9/10 (Category avg: 9.2/10)
  • Data Examination: 8.1/10 (Category avg: 8.7/10)
  • Ease of Use: 8.1/10 (Category avg: 8.8/10)
  • Log Management: 8.1/10 (Category avg: 9.2/10)

Who Is the Company Behind Trellix Enterprise Security Manager?

  • Seller: Trellix
  • Year Founded: 2004
  • HQ Location: Plano, TX
  • LinkedIn® Page: www.linkedin.com
    3,811 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 42% Large, 29% Medium

What Do G2 Reviewers Say About Trellix Enterprise Security Manager?

AI-generated summary from verified user reviews

Pros
  • Users value the instant access to log data, enhancing their ability to monitor and respond to security incidents efficiently.
  • Users value the dashboard customization options in Trellix Enterprise Security Manager for their clarity and efficiency.
  • Users appreciate the dashboard usability of Trellix Enterprise Security Manager, finding it clear and efficient for quick checks.
  • Users benefit from the efficient debugging capabilities of Trellix Enterprise Security Manager, resolving issues quickly and effectively.
  • Users appreciate the ease of use of Trellix Enterprise Security Manager, enjoying its intuitive dashboard and alarm features.
Cons
  • Users find difficult customization for dashboards and reports time-consuming and requires significant technical expertise for effective use.
  • Users find the difficult navigation of Trellix Enterprise Security Manager frustrating due to its outdated UI and non-scrollable windows.
  • Users find Trellix Enterprise Security Manager to be expensive, especially for large-scale deployments with limited budgets.
  • Users encounter faulty detection issues, leading to frustrating false positives and limiting the product's effectiveness.
  • Users experience integration issues that hinder customization and complicate dashboard setup, impacting overall usability.

What Are Recent G2 Reviews of Trellix Enterprise Security Manager?

What Are G2 Users Discussing About Trellix Enterprise Security Manager?

Guardsix

Guardsix is the sovereign security platform for lean European teams, bringing log management and audit-ready compliance to regulated industries, critical national infrastructure operators, and the Managed Security Service Providers (MSSPs) that serve them throughout Europe and beyond. Headquartered in Copenhagen, Denmark, Guardsix delivers sovereign-by-design security for organisations that carry real operational responsibility. The company employs several hundred cyber security specialists and keeps every organisation it serves in full control of their data, deployment, and operations. Guardsix provides a unified Command Centre platform combining: • Security Information and Event Management (SIEM) • Network Detection and Response (NDR) • Security Orchestration, Automation and Response (SOAR) • Fleet for enabling multi-tenant management • Governance for Healthcare internal risk compliance monitoring The platform is built to support European data sovereignty, regulatory compliance and operational control, with predictable node-based pricing and deployment options spanning on-premises, air-gapped, hybrid and cloud environments. Guardsix solutions help organisations: • Simplify audit readiness for regulations such as NIS2, DORA, and GDPR. • Support lean security teams with efficient log management and simplified workflows. • Scale security operations without increased complexity or ingestion-led pricing surprises. • Keep security data under European jurisdiction and control — where it lives, who operates it, and under whose laws. • Deploy on their own terms, on-prem and in infrastructure they control, keeping migration a real option at every renewal. • See clearly across their whole environment, with SIEM, NDR, SOAR, Fleet, and Governance in one sovereign platform rather than a stack of point tools. Guardsix maintains SOC 2 Type II attestation and designs its solutions in accordance with European data protection requirements. With a strong partner-first model, Guardsix works closely with regional MSSPs and service providers, combining sovereign-by-design security technology with European integrity and deployment flexibility.

Average Rating: 4.3/5.0

Total Reviews: 105

How Do G2 Users Rate Guardsix?

  • Activity Monitoring: 8.2/10 (Category avg: 9.2/10)
  • Data Examination: 8.0/10 (Category avg: 8.7/10)
  • Ease of Use: 8.3/10 (Category avg: 8.8/10)
  • Log Management: 8.6/10 (Category avg: 9.2/10)

Who Is the Company Behind Guardsix?

  • Seller: guardsix
  • Company Website:
  • Year Founded: 2001
  • HQ Location: Copenhagen, Capital Region
  • LinkedIn® Page: linkedin.com
    180 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 44% Medium, 31% Small

What Do G2 Reviewers Say About Guardsix?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Guardsix, highlighting its simple interface and efficient incident management capabilities.
  • Users value the seamless integration and context-centric log management of Logpoint, enhancing efficiency and insights significantly.
  • Users commend the excellent customer support of Logpoint, ensuring quick resolutions and satisfaction throughout their experience.
  • Users highly value the easy integrations of Guardsix, enhancing their overall cybersecurity ecosystem and efficiency.
  • Users commend the efficiency of Logpoint, citing its seamless integration and rapid log normalization as major advantages.
Cons
  • Users find poor interface design frustrating, as it hinders usability and lacks essential features compared to competitors.
  • Users find the UX improvement necessary, citing slow interface and poor log presentation as major issues.
  • Users find the interface complexity challenging at first, but anticipate improvements in future updates.
  • Users find the confusing interface of Guardsix challenging, affecting their overall experience and efficiency.
  • Users note a lack of technical information with Guardsix, making it difficult to properly design and size their systems.

What Are Recent G2 Reviews of Guardsix?

What Are G2 Users Discussing About Guardsix?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated