Best Risk-Based Vulnerability Management Software for Small Business - Page 2

How Many Risk-Based Vulnerability Management Software Products Does G2 Track?

Total Products under this Category: 218

Category Stats (Oct 2026)

  • Average Rating: 4.5/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: BMC Helix Automation Console (+4.67%) - Among all products in this category, BMC Helix Automation Console recorded the largest rating increase compared to last month

Last updated: October 16, 2026

How Does G2 Rank Risk-Based Vulnerability Management Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,400+ Authentic Reviews
  • 218+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

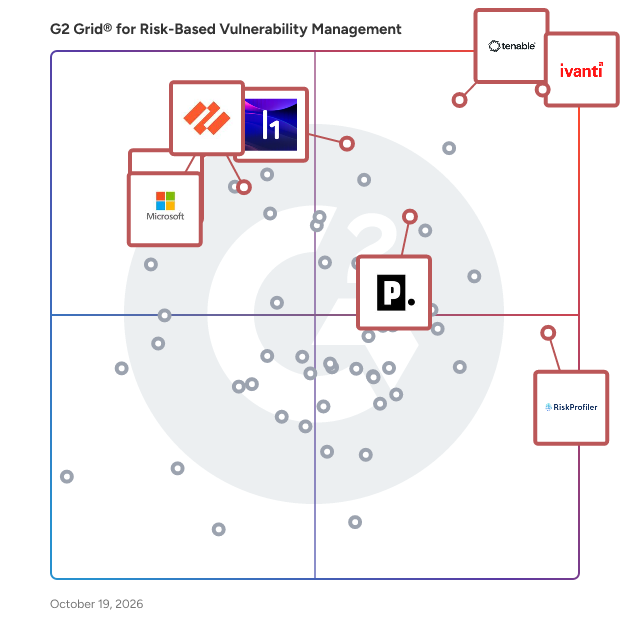
G2 Grid® for Risk-Based Vulnerability Management Software

G2 Grid® for Risk-Based Vulnerability Management Software plotting products by satisfaction and market presence

Highlighted products: Ivanti Autonomous Endpoint Management, Tenable Vulnerability Management, Palo Alto Cortex XSIAM, RiskProfiler - External Threat Exposure Management, H1 Platform, Pentera, Cortex Cloud, and Microsoft Defender Vulnerability Management.

Underlying data: [Grid® JSON](https://www.g2.com/categories/risk-based-vulnerability-management/grids.json?focus%5B%5D=ivanti-autonomous-endpoint-management&focus%5B%5D=tenable-vulnerability-management&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=h1-platform&focus%5B%5D=pentera&focus%5B%5D=cortex-cloud&focus%5B%5D=microsoft-defender-vulnerability-management&segment=small-business)

Saner CVEM

Prevention-first Vulnerability and Exposure Management for unified visibility, prioritization, compliance, and remediation Saner Continuous Vulnerability and Exposure Management unifies asset exposure, posture anomaly detection, vulnerability assessment, compliance management, risk prioritization, patching, and endpoint actions in one dashboard. Saner CVEM is built to help teams continuously detect, assess, prioritize, and remediate vulnerabilities and other security risks from a unified console Why Choose Saner CVEM? • Unified dashboard with interactive views across visibility, detection, prioritization, and remediation for a single source of truth • Complete asset visibility across endpoint and non-endpoint devices, operating system applications, third-party applications, and lifecycle changes • Continuous risk discovery with rapid scans, daily-updated risk intelligence, and posture anomaly detection that helps surface outliers and misconfigurations faster • Context-driven prioritization with SSVC categories such as Act, Attend, Track, and Track* so teams can focus on the risks that deserve action first. • Continuous compliance management with built-in templates, customizable profiles, daily checks, and deviation tracking across common frameworks. • Integrated patching and remediation with vulnerability-to-patch mapping, automated deployment workflows, and endpoint actions from the same ecosystem. • Machine-learning-assisted analysis to identify deeper risk patterns, detect unusual posture, and support smarter remediation decisions. • Customizable, audit-ready reporting for security, IT, and compliance teams that need clearer evidence and easier tracking. • Flexible deployment on cloud or on-premises, with remediation support across Windows, Linux, macOS, and AIX environments.

Average Rating: 4.5/5.0

Total Reviews: 72

How Do G2 Users Rate Saner CVEM?

  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.2/10)
  • Reporting: 8.3/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 9.4/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 9.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Saner CVEM?

  • Seller: SecPod
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Redwood City, California
  • Twitter: @secpod
    542 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    182 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Small, 38% Medium

What Do G2 Reviewers Say About Saner CVEM?

AI-generated summary from verified user reviews

Pros
  • Users value the automatic security updates from Saner CVEM, ensuring timely compliance for remote workforce systems.
  • Users appreciate the advanced automation features of Saner CVEM, streamlining security patch management for remote systems.
  • Users value the ease of use of Saner CVEM, enabling quick detection and mitigation of vulnerabilities effortlessly.
  • Users highlight the exceptional customer support from Saner CVEM, enhancing security and helping organizations stay protected.
  • Users value the automated compliance management of Saner CVEM, enhancing efficiency and reducing manual intervention significantly.
Cons
  • Users often face integration issues with Saner CVEM, leading to frustrations during setup and ongoing maintenance.
  • Users note limited features in Saner CVEM, especially in multi-tenant support and integration capabilities, impacting efficiency.
  • Users experience slow performance when loading large data sets and during initial setup, affecting usability.
  • Users experience slow scanning, especially with initial dashboard load times and large data sets affecting daily checks.
  • Users find the limited cloud integration challenging, requiring workarounds and custom scripts for effective use.

What Are Recent G2 Reviews of Saner CVEM?

What Are G2 Users Discussing About Saner CVEM?

vRx by Vicarius

vRx by Vicarius goes beyond patch management to offer the most advanced vulnerability remediation solution in the market. vRx offers 3 built-in methods to keep you covered at all times: 1) Automated Patching: vRx catalogs all your apps and finds the patches they need, and applies them - automatically and on the schedule or frequency of your choosing. 2) Scripting: For more complex vulnerabilities or configuration based vulnerabilities, vRx includes a fully fledged scripting engine. 3) Patchless Protection: x_protect or patchless protection is a compensating control that reduces the risk of an affected app even when a patch is not yet developed or cannot be deployed vRx helps 500+ customers across 50 countries find AND immediately remediate vulns that impact their business.

Average Rating: 4.9/5.0

Total Reviews: 61

How Do G2 Users Rate vRx by Vicarius?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)
  • Reporting: 8.7/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 9.2/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 9.6/10 (Category avg: 8.8/10)

Who Is the Company Behind vRx by Vicarius?

  • Seller: Vicarius
  • Company Website:
  • Year Founded: 2016
  • HQ Location: New York, New York
  • Twitter: @vicariusltd
    2,018 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    100 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 44% Medium, 32% Small

What Do G2 Reviewers Say About vRx by Vicarius?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of vRx, praising its quick setup and user-friendly interface.
  • Users appreciate the high level of automation in vRx, streamlining vulnerability management from detection to remediation.
  • Users value the automated patch management in vRx by Vicarius, which enhances efficiency and reduces manual workload.
  • Users value the automated vulnerability identification in vRx by Vicarius, enhancing efficiency in patch management and remediation.
  • Users value the automated vulnerability identification and patch management in vRx, enhancing efficiency and support significantly.
Cons
  • Users feel that vRx lacks essential features like advanced reporting and Windows store application support, requiring further development.
  • Users note inadequate reporting, citing simplicity and a need for enhanced customization and compliance options.
  • Users find the complexity of setup and advanced analytics challenging, particularly for those with limited technical expertise.
  • Users experience dashboard issues that hinder customization and adaptability, particularly for non-technical audiences.
  • Users face inaccurate information regarding reporting and risk scoring, leading to confusion about vulnerabilities management.

What Are Recent G2 Reviews of vRx by Vicarius?

What Are G2 Users Discussing About vRx by Vicarius?

Cyrisma

Cyrisma helps MSPs and MSSPs turn cyber risk and compliance into revenue. Its unified platform combines vulnerability management, data and asset discovery, compliance tracking, secure configuration, and dark web monitoring into one continuous experience - enabling partners to identify, prioritize, and remediate cyber risk efficiently. With executive-ready reporting, risk monetization insights, and elegant visuals, Cyrisma helps MSPs demonstrate measurable value, strengthen client relationships, and scale their security services profitably.

Average Rating: 4.6/5.0

Total Reviews: 60

How Do G2 Users Rate Cyrisma?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Reporting: 8.2/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 8.8/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 8.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Cyrisma?

  • Seller: Cyrisma
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Rochester, NY
  • Twitter: @Cyrisma_USA
    43 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    14 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 75% Small, 22% Medium

What Do G2 Reviewers Say About Cyrisma?

AI-generated summary from verified user reviews

Pros
  • Users value the time-saving integration of Cyrisma, streamlining cybersecurity processes and enhancing overall efficiency.
  • Users value the ease of use of Cyrisma, benefiting from its intuitive interface and seamless integration.
  • Users value the fantastic customer support from Cyrisma, noting its helpfulness and product improvement initiatives.
  • Users value the actionable vulnerability intelligence and integrated patch management features of Cyrisma for efficiency and effectiveness.
  • Users appreciate CYRISMA for its actionable vulnerability intelligence, making it easy to identify and address critical security issues.
Cons
  • Users find a lack of essential features, particularly in UI navigation, data correlation, and patch management capabilities.
  • Users find Cyrisma to be not user-friendly, struggling with navigation, deployment, and overall support for their needs.
  • Users face integration issues with Cyrisma, including broken data scans and delayed API functionality for automation.
  • Users report limited flexibility in Cyrisma, especially with data scanning and agent deployment, hindering efficiency.
  • Users express frustration with the poor customer support from Cyrisma, hindering their ability to effectively use the product.

What Are Recent G2 Reviews of Cyrisma?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

CloudBees

The Complete DevOps solution. CloudBees empowers your software delivery teams to transform your business. CloudBees solution brings together development, operations, IT, security, and business teams to: Create fast with scalable repeatable workflows. Continuously improve customer experiences by progressively delivering features with speed and control. Command everything with higher-order visibility, management, and intelligence across tools, teams, pipelines, and process... all at enterprise scale.

Average Rating: 4.4/5.0

Total Reviews: 592

How Do G2 Users Rate CloudBees?

  • Has the product been a good partner in doing business?: 8.5/10 (Category avg: 9.2/10)
  • Reporting: 9.6/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 8.8/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind CloudBees?

  • Seller: CloudBees
  • Company Website:
  • Year Founded: 2010
  • HQ Location: San Jose, CA
  • Twitter: @CloudBees
    39,175 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    485 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, DevOps Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Large, 41% Medium

What Do G2 Reviewers Say About CloudBees?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the centralized management and robust security of CloudBees, enhancing their CI/CD lifecycle and workflows.
  • Users value the reliability of CloudBees, benefiting from its scalable tools and robust security in CI/CD processes.
  • Users value the customization options of CloudBees, enhancing integration and efficiency across various tools and workflows.
  • Users find CloudBees' ease of use exceptional, enabling seamless integration and efficient workflow management across teams.
  • Users value the seamless integrations of CloudBees with major DevOps tools, enhancing workflow automation and efficiency.
Cons
  • Users struggle with the complex interface of CloudBees, making understanding and configuration quite challenging.
  • Users face complexity in understanding and configuration of CloudBees, requiring significant time and specialized expertise.
  • Users find the complex setup of CloudBees time-consuming and difficult to navigate, requiring specialized expertise.
  • Users find the complex user interface of CloudBees challenging, complicating understanding and configuration processes.
  • Users face configuration issues with CloudBees, finding it complex and time-consuming to manage effectively.

What Are Recent G2 Reviews of CloudBees?

What Are G2 Users Discussing About CloudBees?

Check Point Exposure Management

Exposure Management is changing how organizations react to vulnerabilities that put them in risk. Attackers exploit exposed assets, leaked credentials, and misconfigurations within hours using sophisticated AI attack tools. Meanwhile, security teams are left sorting through dashboards, alerts, and disconnected tools. For a limited time only, we are providing an Agentic Exposure Validation Scan at no cost. It delivers proven, evidence-backed findings your team can act on immediately. Request scan here - https://checkpoint.cyberint.com/limited-time-offer-aev-scan Check Point Exposure Management closes that gap by combining billions of external intelligence signals into a Unified Intelligence Fabric. The platform continuously identifies, validates, prioritizes, and safely remediates the exposures attackers are most likely to exploit. With Cyber Asset Attack Surface Management (CAASM), security teams gain a real-time inventory across cloud, SaaS, on-premises infrastructure, endpoints, and identities through 150+ agentless integrations. Unlike traditional vulnerability management, Check Point prioritizes exposures based on real-world exploitability, active threat intelligence, business context, and existing security controls, eliminating duplicate alerts and reducing remediation noise. It does so while maintaining business continuity. Safe-by-design remediation then validates every action before enforcement, enabling capabilities such as virtual patching, IPS activation, configuration hardening, and policy enforcement without disrupting business operations. Organizations using the platform achieve a 93% true positive rate, 12-hour average takedown MTTR, and 504 safe remediations per organization every month. Built around Gartner's Continuous Threat Exposure Management (CTEM) framework, Check Point helps organizations move from visibility to measurable risk reduction. Gartner predicts organizations adopting CTEM with mobilization will experience 50% fewer successful cyberattacks by 2028. Ready to see Exposure Management in action? Get a 15-minute demo: https://l.cyberint.com/exposure-management-demo

Average Rating: 4.6/5.0

Total Reviews: 198

How Do G2 Users Rate Check Point Exposure Management?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Reporting: 8.8/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 9.3/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 9.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Check Point Exposure Management?

Who Uses This Product?

  • Who Uses This: Cyber Security Analyst, Security Threat Analyst
  • Top Industries: Banking, Financial Services
  • Company Size: 66% Large, 21% Medium

What Do G2 Reviewers Say About Check Point Exposure Management?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Check Point Exposure Management, enjoying its intuitive interface for threat detection.
  • Users value the comprehensive threat intelligence from Cyberint, enhancing detection and response to potential threats effectively.
  • Users commend the enhanced threat detection capabilities of Check Point Exposure Management, improving situational awareness and response efficiency.
  • Users value the comprehensive intelligence feeds of Check Point Exposure Management, enhancing threat detection and situational awareness.
  • Users value the responsive and proactive customer support from Cyberint, enhancing their overall threat management experience.
Cons
  • Users face challenges with inefficient alerts due to false positives, complicating the verification process for analysts.
  • Users experience false positives that necessitate additional validation time, complicating the overall alert management process.
  • Users find the inefficient alert system complicates handling excessive alerts and delays threat intel on compromised accounts.
  • Users note integration issues with Check Point Exposure Management, particularly regarding centralizing alerts and connecting security tools.
  • Users note the limited features of Check Point Exposure Management, specifically regarding alert tuning and user account restrictions.

What Are Recent G2 Reviews of Check Point Exposure Management?

What Are G2 Users Discussing About Check Point Exposure Management?

BugBase

BugBase is a Continuous Vulnerability Assessment Platform that conducts comprehensive security operations such as bug bounty programs and next-gen pentesting (VAPT) to assist startups and enterprises in effectively identifying, managing and mitigating vulnerabilities.

Average Rating: 4.5/5.0

Total Reviews: 45

How Do G2 Users Rate BugBase?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.2/10)
  • Reporting: 9.1/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 9.2/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 9.4/10 (Category avg: 8.8/10)

Who Is the Company Behind BugBase?

  • Seller: BugBase
  • Year Founded: 2021
  • HQ Location: Singapore, US
  • Twitter: @BugBase
    1,673 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    43 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Computer Software
  • Company Size: 60% Small, 21% Medium

What Do G2 Reviewers Say About BugBase?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the user-friendly interface of BugBase, making it ideal for new bug bounty hunters.
  • Users appreciate the simple and user-friendly interface of BugBase, making it ideal for new bug bounty hunters.
  • Users value the enhanced cybersecurity of BugBase, benefiting from secure bounty programs and robust vulnerability detection.
  • Users value the user-friendly interface and powerful features of BugBase, enhancing security and project efficiency.
  • Users value the easy integrations of BugBase, simplifying workflows and enhancing security across various tools and technologies.
Cons
  • Users experience slow performance on BugBase, facing lagging issues and delayed support responses that hinder their productivity.
  • Users feel that BugBase is expensive and lacks competitive pricing compared to other bug bounty platforms.
  • Users find the difficult setup of BugBase challenging, particularly for those lacking technical expertise in vulnerability assessment.
  • Users face a steep learning curve with BugBase, which can hinder the experience for those new to bug bounty programs.
  • Users report poor customer support with BugBase, causing frustration and hindering their bug hunting experience.

What Are Recent G2 Reviews of BugBase?

Fortra VM

Fortra VM is a proactive, risk-based vulnerability management solution that helps organizations identify, assess, and prioritize security weaknesses across their infrastructure. Beyond basic scanning, Fortra VM provides contextual risk prioritization through its Security GPA rating system, Peer Insight for industry benchmarking, and threat ranking to identify exploitation vectors that are used in real world attacks. Conveniently delivered via SAAS, Fortra VM creates easily understood reporting for efficient and effective remediation.

Average Rating: 4.3/5.0

Total Reviews: 67

How Do G2 Users Rate Fortra VM?

  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.2/10)
  • Reporting: 8.6/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 8.6/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 8.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Fortra VM?

  • Seller: Fortra
  • Year Founded: 1982
  • HQ Location: Eden Prairie, Minnesota
  • Twitter: @fortraofficial
    2,773 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,784 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services, Banking
  • Company Size: 45% Medium, 35% Small

What Do G2 Reviewers Say About Fortra VM?

AI-generated summary from verified user reviews

Pros
  • Users are thrilled with Fortra VM, particularly praising its excellent customer support since its lightweight usage began in 2020.
  • Users value the data security of Fortra VM, using it effectively for vulnerability assessments and remediation planning.
  • Users find Fortra VM easy to use, appreciating its lightweight design and excellent customer support.
  • Users appreciate the incident management capabilities of Fortra VM, effectively addressing vulnerabilities and enhancing security posture.
  • Users find Fortra VM's security vulnerability scans invaluable for assessing and improving their endpoint security posture.

What Are Recent G2 Reviews of Fortra VM?

What Are G2 Users Discussing About Fortra VM?

IBM QRadar EDR

IBM Security QRadar EDR (formerly ReaQta) combines automation and dashboards to minimize analyst workloads, detect anomalous endpoint behavior and remediate threats in near real time. IBM Security QRadar EDR is available on AWS Marketplace. With visibility across endpoints, it combines expected features, like MITRE ATT&CK mapping and attack visualizations, with dual-engine AI and automation. For teams that need extended support, managed detection and response (MDR) services offers 24/7 monitoring and response to help keep users protected. IBM Security QRadar EDR (formerly ReaQta) can be deployed as SaaS, on-premises and in air-gapped environments. For more information, visit https://www.ibm.com/products/qradar-edr

Average Rating: 4.2/5.0

Total Reviews: 45

How Do G2 Users Rate IBM QRadar EDR?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.2/10)
  • Reporting: 9.5/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 8.3/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 8.5/10 (Category avg: 8.8/10)

Who Is the Company Behind IBM QRadar EDR?

  • Seller: IBM
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • Twitter: @IBMSecurity
    74,660 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 45% Small, 40% Medium

What Do G2 Reviewers Say About IBM QRadar EDR?

AI-generated summary from verified user reviews

Pros
  • Users find the advanced threat detection of IBM QRadar EDR essential for maintaining system security and integrity.
  • Users appreciate the ease of use of IBM QRadar EDR, noting its simple installation and effective logging capabilities.
  • Users value the advanced threat detection and endpoint protection of IBM QRadar EDR, ensuring robust security and continuous updates.
  • Users praise the advanced threat detection capabilities of IBM QRadar EDR, enhancing security and responsiveness significantly.
  • Users value the robust threat detection of IBM QRadar EDR, enhancing security against cyber threats effectively.
Cons
  • Users find IBM QRadar EDR too expensive for small and mid-sized businesses, limiting accessibility and affordability.
  • Users find difficult learning due to initial setup challenges and a need for programming knowledge, complicating effective use.
  • Users find IBM QRadar EDR to be resource intensive, leading to increased costs and implementation challenges.
  • Users experience many false positives with QRadar EDR, requiring additional manual investigation and attention from the team.
  • Users experience high resource usage with IBM QRadar EDR, requiring powerful devices for optimal performance.

What Are Recent G2 Reviews of IBM QRadar EDR?

Tenable Security Center

Tenable Security Center (formerly Tenable.sc) is the industry's most comprehensive risk-based vulnerability management (RBVM) solution, enabling you to: • See all your vulnerabilities and continuously assess all assets the moment they join the network -- including transient devices that aren’t regularly connected • Predict what matters by understanding vulnerabilities in the context of business risk, as well as the criticality of affected assets • Act on each high priority vulnerability to effectively manage risk, and measure KPIs to effectively communicate effectiveness Legacy vulnerability management tools weren't designed to handle the modern attack surface and the growing number of threats that come with them. Instead, they’re limited to a theoretical view of risk, leading security teams to waste the majority of their time chasing after the wrong issues while missing many of the most critical vulnerabilities that pose the greatest risk to the business. By taking a risk-based approach to vulnerability management, Tenable.sc enables security teams to focus on the vulnerabilities and assets that matter most, so they can address the organization’s true business risk instead of wasting their valuable time on vulnerabilities that have a low likelihood of being exploited. Tenable delivers the most comprehensive risk-based vulnerability management solution available to help you prioritize your remediation efforts, so you can take decisive action to reduce the greatest amount of business risk with the least amount of effort.

Average Rating: 4.6/5.0

Total Reviews: 74

How Do G2 Users Rate Tenable Security Center?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.2/10)
  • Reporting: 8.6/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 9.5/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 9.4/10 (Category avg: 8.8/10)

Who Is the Company Behind Tenable Security Center?

  • Seller: Tenable
  • HQ Location: Columbia, MD
  • Twitter: @TenableSecurity
    87,752 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,361 employees on LinkedIn®
  • Ownership: NASDAQ: TENB

Who Uses This Product?

  • Top Industries: Computer & Network Security, Banking
  • Company Size: 58% Large, 25% Medium

What Do G2 Reviewers Say About Tenable Security Center?

AI-generated summary from verified user reviews

Pros
  • Users value the informative dashboard and features like compliance scans and easy scanner management in Tenable Security Center.
  • Users appreciate the compliance management features of Tenable Security Center, aiding in ISO 27001 and audit conformity.
  • Users appreciate the responsive customer support for swiftly resolving queries and addressing licensing issues.
  • Users value the compliance scanning capabilities of Tenable Security Center, ensuring adherence to audit requirements effectively.
  • Users value the informative dashboard of Tenable Security Center, appreciating its comprehensive overview of vital data.
Cons
  • Users find the complexity of installation and documentation a significant hurdle, impacting their overall experience with Tenable Security Center.
  • Users find the complex documentation of Tenable Security Center challenging, making issue resolution time-consuming.
  • Users find the complex setup process of Tenable Security Center to be time-consuming and challenging to navigate.
  • Users experience a difficult setup process, requiring significant time and effort to install and integrate Tenable Security Center.
  • Users report integration issues with Tenable Security Center, citing complex installation and challenging documentation as obstacles.

What Are Recent G2 Reviews of Tenable Security Center?

What Are G2 Users Discussing About Tenable Security Center?

HostedScan.com

HostedScan provides 24x7 alerts and detection for security vulnerabilities. Industry-standard, open-source, vulnerability scans. Automated alerts when something changes. Manage target list manually or import automatically from providers, such as AWS, DigitalOcean, and Linode, with read-only access. Manage and audit risks with dashboarding and reporting.

Average Rating: 4.3/5.0

Total Reviews: 13

How Do G2 Users Rate HostedScan.com?

  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.2/10)
  • Reporting: 8.3/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 7.5/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 7.5/10 (Category avg: 8.8/10)

Who Is the Company Behind HostedScan.com?

  • Seller: HostedScan
  • Year Founded: 2019
  • HQ Location: Seattle, Washington
  • Twitter: @hostedscan
    59 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    4 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 85% Small, 15% Medium

What Are Recent G2 Reviews of HostedScan.com?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated
Reviews & FAQs

Reviews Summary: The Best Risk-Based Vulnerability Management Software for Small-Business Businesses

Thanks to 5275 Risk-Based Vulnerability Management software reviews and associated data from users working for small-sized companies, at G2 we have some of the most definitive data on the best Risk-Based Vulnerability Management software for the smaller space. We have identified 24 individual Risk-Based Vulnerability Management products offering the features, pricing and support that Small-Business companies look for when comparing Risk-Based Vulnerability Management software and solutions. These reviews are generated using the qualitative and quantitative feedback from G2 members working in small-sized companies and who have used these Risk-Based Vulnerability Management software products.

When G2 reviewers submit their Risk-Based Vulnerability Management software reviews, they often provide information on the type of company they work for and what market segment they belong to. We break these different market segments into three distinct groups:

  • Small Business Risk-Based Vulnerability Management Software Reviews (< 50 employees)
  • smaller Risk-Based Vulnerability Management Software Reviews (51-1,000 employees)
  • Enterprise Risk-Based Vulnerability Management Software Reviews (1,001+ employees)

smaller businesses have their own unique requirements when it comes to Risk-Based Vulnerability Management software compared to small or enterprise companies. That is why these individual small-sized company Risk-Based Vulnerability Management software reviews are especially helpful when comparing product set up, ease of use and overall cost.

Below you will find FAQs and review snippets for Risk-Based Vulnerability Management software products that work well in smaller environments. These reviews are written by real G2 users working for these Small-Business companies who have real-world experience with these Risk-Based Vulnerability Management software products.

FAQs About Risk-Based Vulnerability Management Software for Small-Business Businesses

Q. What are the best Risk-Based Vulnerability Management software products for small-sized businesses, according to G2 reviewers?
  • Ivanti Autonomous Endpoint Management - 4.4-stars, 60 reviews (20% from smaller reviewers)
  • Tenable Vulnerability Management - 4.7-stars, 17 reviews (15% from smaller reviewers)
  • RiskProfiler - External Threat Exposure Management - 5.0-stars, 39 reviews (33% from smaller reviewers)
  • Pentera - 4.6-stars, 13 reviews (19% from smaller reviewers)
  • Cortex Cloud - 4.4-stars, 12 reviews (27% from smaller reviewers)
Q. What are the least-liked Risk-Based Vulnerability Management software products for professionals at small-sized companies, based on the overall G2 rating?
  • HostedScan.com - 4.2-stars, 10 reviews (83% from smaller reviewers)
  • Tenable Security Center - 4.4-stars, 10 reviews (15% from smaller reviewers)
  • IBM QRadar EDR - 4.0-stars, 18 reviews (49% from smaller reviewers)
  • Fortra VM - 4.3-stars, 18 reviews (32% from smaller reviewers)
  • BugBase - 4.4-stars, 11 reviews (55% from smaller reviewers)
Q. What are the highest-rated Risk-Based Vulnerability Management software tool features according to employees at Small-Business companies?
  • Risk Scoring - 4.5-stars
  • Risk-Prioritization - 4.5-stars
  • Vulnerability Scanning - 4.5-stars
Q. What are the features that are rated lowest by employees at Small-Business companies?
  • Automated Remediation - 4.0-stars
  • Workflow Automation - 4.1-stars
  • Test Automation - 4.2-stars
Q. How many Risk-Based Vulnerability Management software reviews are from users working in smaller companies?

517 out of all Risk-Based Vulnerability Management software reviews on G2 are from users working in Small-Business companies (10%).

Here's What Reviewers Working at smaller Businesses Have to Say About Risk-Based Vulnerability Management Software

What Small-Business Professionals Liked What Small-Business Professionals Disliked

Qualys VMDR: “Ability to quickly prioritize Vulnerabilities and being able to present executive-friendly metrics with the usage of dynamic dashboards that showcase the riskiest areas of our customers”

Read Review

VulScan: “It didn't work very much. We never got it to watch rk and does not work without an h8ur long install and only if you have a domain controller”

Read Review

Semperis Purple Knight: “Although there are numerous tools capable of auditing Active Directory, Purple distinguishes itself by not only conducting audits but also offering detailed explanations for every vulnerability it uncovers. Additionally, it provides clear guidance on how to address these issues. Purple knight is also easy to implement, it leads you to give the missing permission, and is running pretty quick And the best of it, the tool is free, thank you Semperis.”

Read Review

Cyrisma: “I find it very difficult to navigate the system and setting up of the reports. There is limited device updating offered by CYRISMA. I have yet to get my system working after years of using and asking for help. There is minimal effort from CYRISMA customer success with the product. I had a call with the new account manager and have not heard back from him since the last call. Also, he knew I was having issues and yet he still thought it was good to follow up again in 3 months. I have yet to hear back from him to date. It has been a disappointing experience of the product support in order to have success with it. Could be a great product if I knew how it works. I am disappointed.”

Read Review

VulScan: “Friendly GUI console. Easy to work and easy to setup”

Read Review

Titania Nipper InfraSight: “I find it challenging that Titania Nipper InfraSight is a desktop-based application. It should be a web application.”

Read Review

Recommendations To Others Problems Solved & Benefits

Strobes Security: “Very reliable and the team behind this is very accommodative and support you in every situation.”

Read Review

Tenable Vulnerability Management: “Tenable Vulnerability Management provides a comprehensive view of vulnerability management, helping to determine the impact on the company and manage associated risks. I also value its user-friendly graphical interface and the organization of information in the modules.”

Read Review

Cisco Vulnerability Management (formerly Kenna.VM): “Good product”

Read Review

Ivanti Autonomous Endpoint Management: “Provides the ability to manage remote and on-prem devices easily. Can create different patching policies to ensure devices are properly patched, and build bots to perform self-healing, perform actions based on different query criteria. Edge intelligence is useful to pull realtime information off of devices and see who may be having issues before anything is reported.”

Read Review

InsightVM (Nexpose): “Don't forget to consider the cloud portion of InsightVM versus the on-prem only version (Nexpose). I've found the cloud portion allows for folks who don't need to be in the tool daily (managers and executives) to still get value without needing to learn a new tool. It is also super useful for dashboarding.”

Read Review

Tenable Vulnerability Management: “Tenable helps us identify, prioritize, and track vulnerabilities across our environment. This improves visibility, supports faster remediation, and reduces the risk of critical vulnerabilities remaining unresolved.”

Read Review