Best Privileged Access Management (PAM) Software - Page 8

How Many Privileged Access Management (PAM) Software Products Does G2 Track?

Total Products under this Category: 179

Category Stats (Sep 2026)

  • Average Rating: 4.49/5 (↓0.01 vs Aug 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Heimdal (+0.09%) - Among all products in this category, Heimdal recorded the largest rating increase compared to last month

Last updated: September 15, 2026

How Does G2 Rank Privileged Access Management (PAM) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 13,400+ Authentic Reviews
  • 179+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

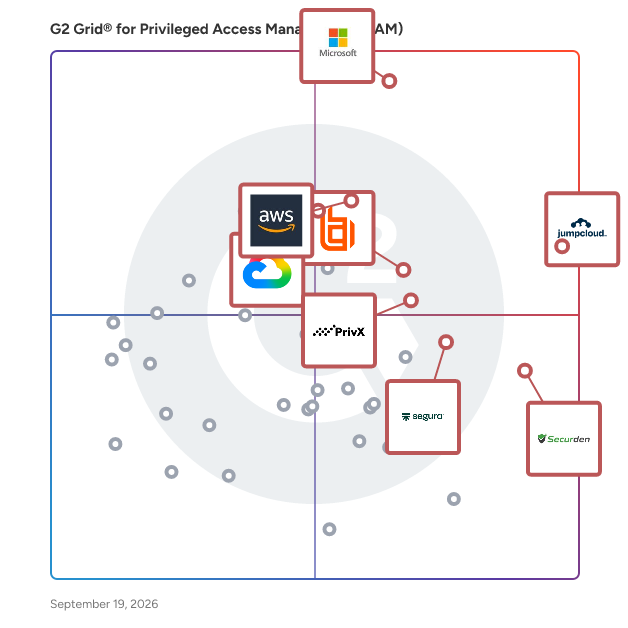
G2 Grid® for Privileged Access Management (PAM) Software

G2 Grid® for Privileged Access Management (PAM) Software plotting products by satisfaction and market presence

Highlighted products: Microsoft Entra ID, JumpCloud, Securden Unified PAM, AWS Secrets Manager, BeyondTrust Remote Support, SSH PrivX, Google Cloud Identity & Access Management (IAM), and Segura 360° Privilege Platform.

Underlying data: [Grid® JSON](https://www.g2.com/categories/privileged-access-management-pam/grids.json?focus%5B%5D=microsoft-entra-id&focus%5B%5D=jumpcloud&focus%5B%5D=securden-unified-pam&focus%5B%5D=aws-secrets-manager&focus%5B%5D=beyondtrust-remote-support&focus%5B%5D=ssh-privx&focus%5B%5D=google-cloud-identity-access-management-iam&focus%5B%5D=segura-360-privilege-platform)

CA Trusted Access Manager for Z

CA Trusted Access Manager for Z helps deliver trusted systems and improve business efficiency through comprehensive privileged access management for your mainframe

Who Is the Company Behind CA Trusted Access Manager for Z?

  • Seller: Broadcom
  • Year Founded: 1991
  • HQ Location: San Jose, CA
  • Twitter: @broadcom
    63,909 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    44,602 employees on LinkedIn®
  • Ownership: NASDAQ: CA

CloudEnv

Simple End-to-End Encrypted Cloud ENV Variables. Keep your ENV vars synced and versioned with your team (without Git). Simple CLI – Get started in seconds, not minutes. Trusted IP Addresses let you receive an email request before authorizing a new IP address access to your secrets.

Who Is the Company Behind CloudEnv?

  • Seller: CloudEnv
  • Year Founded: 2020
  • HQ Location: San Diego, US
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Cloud Suite

Who Is the Company Behind Cloud Suite?

  • Seller: Delinea
  • Year Founded: 2004
  • HQ Location: San Francisco
  • Twitter: @DelineaInc
    897 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,385 employees on LinkedIn®

Devolutions PAM

Devolutions PAM is a privileged access management (PAM) solution that helps small and midsize businesses discover, secure, rotate, and audit privileged accounts across their infrastructure. It belongs to the privileged access management software category and is designed for IT teams, security teams, and managed service providers that need to control and monitor elevated access to critical systems without the complexity typically associated with enterprise PAM tools. Privileged accounts such as administrator, shared, and service accounts hold elevated access and are common targets for attackers and sources of insider risk. Devolutions PAM addresses this by identifying privileged accounts, securing their credentials, automating password rotation, controlling how and when they are used, and recording activity for accountability. It is delivered as part of the Privileged Access Management package and runs on a Devolutions workspace, either the cloud-hosted Devolutions Cloud or the self-hosted Devolutions Server, while integrating with Remote Desktop Manager for connection launching and Devolutions Gateway for secure tunneling. Common use cases include enforcing least-privilege and just-in-time access, eliminating standing privileges, rotating and vaulting privileged credentials, recording privileged sessions, and demonstrating compliance through audit logs. Key features and benefits include: - Discovery of privileged accounts across the environment - Automated password rotation and secure credential vaulting - Just-in-time privilege elevation and check-out approval workflows that reduce standing access - Session recording and tamper-resistant audit logs for monitoring and compliance - Granular role-based access control, allowing users to connect to resources without seeing the underlying credentials Devolutions PAM is designed to provide privileged access controls typically found in enterprise products in a form that is practical for smaller organizations to adopt and operate. Because it integrates with the broader Devolutions suite, organizations can extend from credential management into full privileged access management within a single ecosystem, moving from standing privileges toward zero-standing-privilege access under centralized governance, role-based control, and auditing.

Who Is the Company Behind Devolutions PAM?

  • Seller: Devolutions
  • Year Founded: 2010
  • HQ Location: Lavaltrie, Quebec
  • Twitter: @DevolutionsInc
    1,249 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    234 employees on LinkedIn®

EmpowerID Privileged Access Management

Privileged accounts are both a necessity and a liability. These accounts, with their nearly-unlimited access to system resources are essential for everyday IT operations, yet abuse of privileged accounts is attributed as the cause of 62% of security breaches.

Who Is the Company Behind EmpowerID Privileged Access Management?

  • Seller: EmpowerID
  • Year Founded: 2005
  • HQ Location: Dublin, US
  • Twitter: @EmpowerID
    384 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    88 employees on LinkedIn®

Evo Security

vo Security is a multi-tenant Identity and Access Management (IAM) platform built exclusively for Managed Service Providers (MSPs) and Managed Security Service Providers (MSSPs). Headquartered in Austin, Texas, and backed by industry leaders, we were founded by cybersecurity professionals determined to help IT service providers protect their small to mid-market clients from the most common cyberthreat: compromised credentials. Our platform combines Multi-Factor Authentication (MFA), Single Sign-On (SSO), RADIUS Authentication, Help Desk Verification, and Privileged Access Management (PAM) into a single, user-friendly interface. By delivering these core security tools in one solution, Evo Security saves MSPs time, reduces complexity, and boosts profitability with better gross margins. Most importantly, Evo Security tackles the rising threat of stolen credentials by simplifying how MSPs and MSSPs manage user access. We help administrators and end-users alike enjoy a seamless experience, reinforcing the crucial balance between strong security and efficient operations—all from a single dashboard built with the IT channel in mind. One agent. One dashboard. Total identity management. Built for MSPs.

Who Is the Company Behind Evo Security?

FilePilot Enterprise Vault

Team credential vault for secure server access — no shared passwords, full audit trail. FilePilot Enterprise Vault is a free, open-source, self-hosted credential server that lets teams share access to FTP, SFTP, FTPS, SCP, S3, and WebDAV servers without ever passing around raw passwords or keys. Instead of emailing credentials, admins provision connection profiles once and issue each teammate a scoped, revocable access token. Every credential is protected with two-tier AES-256-GCM envelope encryption, organized into isolated Vault Groups — each with its own encryption key, IP allowlist, and choice of KMS provider (AWS, Azure, GCP, or HashiCorp Vault). Role-based access control (Admin, Manager, Operator, Auditor) with 20+ granular permissions ensures people only touch what they're supposed to, enforced server-side on every API call. Built for compliance-sensitive teams, the Vault keeps a tamper-evident, hash-chained audit log of every action, streams events to your SIEM via HMAC-signed webhooks, and supports legal/preservation holds to freeze data for regulatory review. A built-in compliance dashboard summarizes encryption, access, audit, and session posture in one view — ready for SOC 2 or HIPAA audits. Setup takes minutes via a browser-based wizard, with support for SQLite, PostgreSQL, or MySQL. Real-time WebSocket sync means token revocations, file reverts, and hold status changes take effect instantly across connected clients. Deploy it anywhere — Docker, on-prem, or your own cloud — with no per-seat cost, no telemetry, and full MIT-licensed source. Best for: Engineering, DevOps, and IT teams who need centralized, auditable, role-based access to shared infrastructure credentials without relying on password managers or spreadsheets. Key features: Central credential vault with encrypted, per-group storage Role-based access control with 20+ fine-grained permissions Scoped, revocable, expiring access tokens Tamper-evident hash-chain audit logging + SIEM webhook integration Legal hold / write-freeze for compliance investigations File version history with one-click remote revert Multi-KMS support (AWS, Azure, GCP, HashiCorp Vault) Self-hosted, MIT licensed, zero telemetry

Who Is the Company Behind FilePilot Enterprise Vault?

  • Seller: GitHub
  • Year Founded: 2008
  • HQ Location: San Francisco, CA
  • Twitter: @github
    2,673,925 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    6,653 employees on LinkedIn®

Fischer Identity

Fischer Identity is a leading developer of enterprise Identity and Access Management (IAM) solutions based on the Zero Trust model. Our products simplify, accelerate and automate the complex task of IAM with cloud-based solutions leveraging the AWS infrastructure without limits of scalability or reach, and ensures constant access to innovation. Fischer Identity solutions are flexible and empowers your organization to build a secure identity management program. Zero Trust starts with Identity.

Average Rating: 4.3/5.0

Total Reviews: 3

Who Is the Company Behind Fischer Identity?

Who Uses This Product?

  • Company Size: 67% Small, 33% Medium

What Are Recent G2 Reviews of Fischer Identity?

FUDO PAM

Fudo Security, a global leader in Privileged Access Management (PAM) and Zero Trust Remote Access solutions, is transforming how organizations secure critical infrastructure and sensitive systems. With deployments in over 35 countries and a rapidly growing partner network, Fudo offers a powerful yet accessible approach to managing privileged accounts, enabling secure remote access, and detecting insider threats in real time.

Who Is the Company Behind FUDO PAM?

  • Seller: Wheel Systems
  • Year Founded: 2012
  • HQ Location: Newark, US
  • Twitter: @wheelsystems
    169 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    80 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of FUDO PAM?

What Are G2 Users Discussing About FUDO PAM?

Gardiyan Privileged Access Management

Gardiyan Privileged Access Management, is a comprehensive cybersecurity platform designed to protect, manage, and audit privileged accounts (admin, root, etc.) that access an institution's most critical data and servers within a centralized "Secure Zone." Built with a Zero Trust architecture, Gardiyan PAM provides dynamic protection against internal and external threats while ensuring compliance with legal regulations such as KVKK and GDPR. The product routes and monitors all access to servers (Windows, Linux, Unix), databases, and network devices through a secure proxy without the need for a VPN. Highlighted Features and Capabilities: Agentless and Flexible Architecture: Operates without requiring any agent software to be installed on target systems (Servers or Clients). This enables rapid installation and deployment without altering the existing network structure. Full Session Recording and Monitoring: Records all sessions conducted via RDP, SSH, VNC, and Telnet protocols as video. Sessions can be monitored live and terminated instantly by an administrator if necessary. Thanks to OCR technology, text and commands within the video recordings are searchable. Centralized Password Management (Vault): Stores privileged account passwords in an isolated and encrypted area. Passwords are rotated automatically or on a scheduled basis according to defined policies. Users can connect securely to target systems via SSO without ever seeing the password. Two-Factor Authentication (2FA/MFA): Integrates with OTP (One-Time Password) solutions like Google Authenticator to enhance access security. It offers multi-factor authentication for remote connections. Advanced Authorization and Approval Mechanism: Access to critical servers can be tied to the approval of specific managers. Unauthorized actions are prevented through the "Four-Eyes Principle" and time-restricted authorization. Third-Party and Vendor Access Management: Provides suppliers and external firm employees (Vendors) with time-restricted and fully controlled access to the internal network via an HTML5-based browser interface, eliminating the need for a VPN. Detailed Reporting and Analytics: Features a dynamic reporting module that answers "Who accessed what, and when?". User activities, inventory status, and system logs can be exported in PDF, Excel, and JSON formats. Benefits: Regulatory Compliance: Ensures full compliance with KVKK and ISO 27001 audits by storing access logs and video recordings in an immutable format. Risk Mitigation: Closes security vulnerabilities caused by shared or unmanaged passwords and reduces the cyber-attack surface. Operational Speed: Lightens the workload of IT teams by providing the ability to manage tens of thousands of assets from a single web interface.

Who Is the Company Behind Gardiyan Privileged Access Management?

Google Workforce Identity Federation Secure access

Workforce Identity Federation Provide employees and your extended workforce with secure access to Google Cloud services and resources using your existing identity management solutions.

Who Is the Company Behind Google Workforce Identity Federation Secure access?

  • Seller: Google
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • Twitter: @google
    31,899,995 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

HashiCorp Boundary

As your infrastructure, applications, and third-party systems expand, platform teams need a method to secure access to them. The key to modern secure remote access? Identity. Platform teams typically use Boundary to: Adopt identity-based remote access management for dynamic environments Standardize on integrations with Vault for credential brokering and OIDC providers for user authentication Scale access to more infrastructure resources with less effort with dynamic service discovery

Who Is the Company Behind HashiCorp Boundary?

  • Seller: HashiCorp
  • Year Founded: 2012
  • HQ Location: San Francisco, CA
  • Twitter: @hashicorp
    103,221 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    9,110 employees on LinkedIn®
  • Ownership: NASDAQ: HCP

Heimdal Privileged Access Management

Founded in 2014, Heimdal Security protects users and companies from cyber-criminal actions, by keeping critical information and intellectual property safe. Heimdal Security is headquartered in København, Denmark.

Who Is the Company Behind Heimdal Privileged Access Management?

  • Seller: Heimdal®
  • Year Founded: 2014
  • HQ Location: Copenhagen, Denmark
  • Twitter: @HeimdalSecurity
    5,086 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    284 employees on LinkedIn®

IBM Verify Privilege

Privileged Access Management (PAM) solution available both on-premises and in the cloud. Discover privileged accounts, vault credentials, delegate access, monitor and record privileged sessions.

Who Is the Company Behind IBM Verify Privilege?

  • Seller: IBM
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • Twitter: @IBMSecurity
    74,660 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM

Iden

Iden is the identity governance (IGA) platform that covers the apps others cannot – SaaS not on enterprise plans, internal tools and legacy systems that lack SCIM or API support. Purpose-built for growing teams that do not want the enterprise bloat or manual tickets. Your SSO serves logins and basic lifecycle management for a fraction of your stack. Iden goes wide and deep and helps you provision users and govern their fine-grained access alongside your SSO. ====== WHY IDEN? • COVERAGE. Iden covers all your SCIM apps by default like other vendors but also has 200+ non-SCIM connectors for the most common SaaS not on enterprise plans. Iden can also build a custom connector in <48 hours for your internal or legacy app (think mainframes/desktop apps). Independent analysis of 721 SaaS apps found 57% support no SCIM at all and 62% put it behind an enterprise plan (read more on scimtax.org) • CONTROL. Fine-grained permissions, deeper than just SSO groups. Time-based access controls for least privilege across the stack. Intent-based, JIT for AI agents too (beta). • COMPLEXITY. Go live in days, not months. No professional services, no dedicated IAM admin and no new headcount needed. Most teams went live with 15 apps in <1hr during onboarding. • COST. Starts $7.50/u/month and goes cheaper with scale. All connectors included. No enterprise-plan upgrades just to unlock provisioning (SCIM tax!) ====== KEY FEATURES • Automated onboarding and birthright provisioning • Clean, compliant offboarding across every connected app, with data backups (supported for 20+ apps) • Self-serve access requests from Slack, Teams, our light-weight ticketing system or also your ITSM • JIT, time-bound access with custom policies and approver workflows • Automated user access reviews (UARs) with multi-stage campaigns and granular scope. • Discover and fix access gaps in real-time with single-click remediation with audit trail, ahead of periodic audits. • Human and non-human identity governance, including service accounts and AI agents, from a single dashboard • Third-party access governance of contractors, vendors with complete lifecycle management • Separation of Duties (SoD) policies enforced at request time • Shadow IT discovery from Google/MS OAuth logs with intelligent scope risks • Shadow AI governance by automated tagging of NHI and owner discovery followed by lifecycle management (as applicable) • Reclaim unused SaaS licenses based on user activity ====== Try Iden for your stack today. Web: https://www.idenhq.com Demo: https://cal.com/team/iden/demo Email: hello@idenhq.com

Who Is the Company Behind Iden?

  • Seller: Iden
  • Company Website:
  • Year Founded: 2024
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    19 employees on LinkedIn®
Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024