Best Penetration Testing Tools - Page 9

How Many Penetration Testing Tools Products Does G2 Track?

Total Products under this Category: 200

Category Stats (Nov 2026)

  • Average Rating: 4.64/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CybaOps (+4.75%) - Among all products in this category, CybaOps recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Penetration Testing Tools Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,900+ Authentic Reviews
  • 200+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

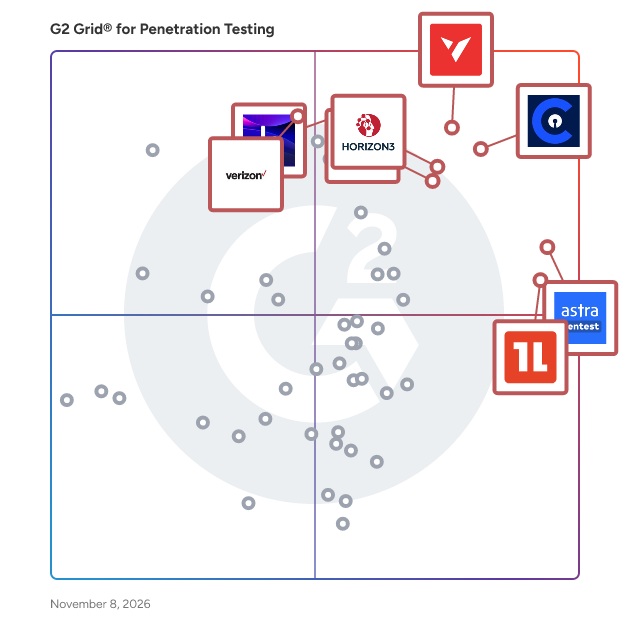
G2 Grid® for Penetration Testing Tools

G2 Grid® for Penetration Testing Tools plotting products by satisfaction and market presence

Highlighted products: Cobalt, vPenTest, Astra Pentest, NodeZero from Horizon3, Oneleet, Pentera, H1 Platform, and Verizon Penetration Testing.

Underlying data: [Grid® JSON](https://www.g2.com/categories/penetration-testing-tools/grids.json?focus%5B%5D=cobalt-io-cobalt&focus%5B%5D=vpentest&focus%5B%5D=astra-pentest&focus%5B%5D=nodezero-from-horizon3&focus%5B%5D=oneleet&focus%5B%5D=pentera&focus%5B%5D=h1-platform&focus%5B%5D=verizon-penetration-testing)

depthfirst

depthfirst is a unified code-to-production security platform. It combines deep understanding of applications and systems with autonomous agents to continuously discover, fix, and prevent security issues, delivering always-on defense. The platform covers three broad areas: - Code Security reviews repositories and pull requests for vulnerabilities, secrets, insecure dependencies, and business-logic flaws. It connects findings to application context so security and engineering teams can focus on the issues that matter and fix them in the code. - Agentic Pentesting uses autonomous agents to attack running applications like a team of elite security researchers. It supports black-, gray-, and white-box testing for new vulnerability discovery, but can also confirm whether code scan findings are exploitable and replay attacks to verify that fixes work. - Dependency Firewall blocks malicious packages before installation to prevent supply chain attacks. It applies a shared security policy at the artifact-repository layer and on managed devices, protecting both people and AI agents. Beyond identifying issues, depthfirst generates fixes and opens pull requests for the engineers responsible for the code, connecting detection, validation, remediation, and retesting in one platform. depthfirst’s in-house research lab develops specialized cybersecurity models, including dfs-large1, and benchmarks AI systems on security tasks. depthfirst works with enterprises such as ServiceNow, government agencies, and innovative AI and fintech companies including Lovable, Supabase, Ripple, Listen Labs, fal, and MoonPay.

Who Is the Company Behind depthfirst?

Dhound

Dhound is a Security-as-a-Service Solution that provides web security monitoring by: - agent-based collection and analysis of security events on your web server; - detecting and alerting about intrusions and suspecious activity; - auditing outgoing traffic and data leakage detection; - tracking events that are important for your online business (logins on websites or admin panel, downloading files, changing account information, etc.)

Who Is the Company Behind Dhound?

Foxhound

Foxhound is the workflow and delivery platform behind Fenko’s penetration testing practice and product. Clients get a single portal to track engagement progress, review findings as we publish them, inspect evidence, and download reports without waiting until the end of the test. Every Fenko pentest engagement runs through Foxhound. There’s no separate fee, no setup, and no plugin to install. When we kick off, your engagement is already live in the portal.

Who Is the Company Behind Foxhound?

  • Seller: Fenko
  • Year Founded: 2025
  • HQ Location: Auckland, NZ
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Gordon VAPT

Gordon Vulnerability Assessment and Penetration Testing (VAPT) combines automated vulnerability scanning with certified analyst-led penetration testing in a single, continuously available service, eliminating the gap between scheduled assessments and ongoing exposure. The service begins with automated discovery and vulnerability scanning across an organization's external and internal attack surfaces, including network infrastructure, web applications, APIs, cloud environments, and endpoints. Discovered vulnerabilities are validated to remove false positives before results are presented, so every finding in the report reflects a confirmed, exploitable issue rather than a raw scanner output. Certified penetration testers then conduct manual exploitation testing against scoped targets, simulating the tactics, techniques, and procedures used in real-world attacks, including privilege escalation, lateral movement, authentication bypass, injection flaws, and business logic vulnerabilities that automated tools cannot detect. Testing covers external network, internal network, web application, API, and cloud infrastructure scopes, configurable per engagement. Each assessment produces two report formats from the same findings: a technical report with full exploit chains, affected assets, CVSS scores, and step-by-step remediation guidance for security and engineering teams; and an executive summary in plain language for leadership and compliance stakeholders, with a risk rating, business impact statement, and remediation priority order. Both are delivered within the agreed SLA, without requiring the customer to reformat or translate findings. Completed assessments map findings to the requirements of SOC 2, ISO 27001, PCI DSS, HIPAA, NIST CSF, and Cyber Essentials. Customers receive a remediation verification retest at no additional cost to confirm fixes before closing the engagement. All scoping, scheduling, reporting, and retest requests are managed through a self-serve portal, with no email-based coordination.

Who Is the Company Behind Gordon VAPT?

  • Seller: Mitigata
  • Year Founded: 2021
  • HQ Location: Bangalore, IN
  • LinkedIn® Page: www.linkedin.com
    106 employees on LinkedIn®
  • Ownership: Private Limited
  • Phone: 7807153087

HostedScan.com

HostedScan provides 24x7 alerts and detection for security vulnerabilities. Industry-standard, open-source, vulnerability scans. Automated alerts when something changes. Manage target list manually or import automatically from providers, such as AWS, DigitalOcean, and Linode, with read-only access. Manage and audit risks with dashboarding and reporting.

Average Rating: 4.3/5.0

Total Reviews: 13

How Do G2 Users Rate HostedScan.com?

  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.4/10)

Who Is the Company Behind HostedScan.com?

  • Seller: HostedScan
  • Year Founded: 2019
  • HQ Location: Seattle, Washington
  • LinkedIn® Page: www.linkedin.com
    4 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 85% Small, 15% Medium

What Are Recent G2 Reviews of HostedScan.com?

ImmuniWeb

ImmuniWeb® AI Platform illuminates your external attack surface and Dark Web exposure for well-informed, risk-based, and DevSecOps-enabled application penetration testing.

Who Is the Company Behind ImmuniWeb?

Impactr

Impactr - The Autonomous Pentest Agent. Security teams don't need more alerts. They need proof. Impactr is an AI-powered Autonomous Penetration Testing Platform that thinks, explores, and validates like an experienced ethical hacker. Unlike traditional vulnerability scanners that generate long lists of potential issues, Impactr autonomously discovers attack paths, verifies vulnerabilities with real exploit evidence, and delivers actionable findings you can trust. Built for modern applications, APIs, networks, cloud environments, and source code, Impactr continuously adapts its approach, chaining vulnerabilities together to uncover real business risk—not just isolated findings. Whether you're securing a fast-moving startup or a global enterprise, Impactr helps you identify exploitable weaknesses earlier, reduce false positives, and accelerate remediation with evidence-backed reporting. Why Impactr? • Autonomous penetration testing • Real exploit verification • Attack path discovery • Evidence-backed reporting • Continuous security validation • CI/CD and DevSecOps ready • Faster, smarter, and scalable security testing Because modern threats require more than automated scanning—they require autonomous thinking. Real Exploits. Verified Live. Reported Instantly.

Who Is the Company Behind Impactr?

Informer

Informer's Attack Surface Management (ASM) and Pentesting platform helps CISOs, CTOs and IT teams map external assets and identify vulnerabilities in real-time so they can be remediated before attackers can exploit them

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Informer?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.4/10)

Who Is the Company Behind Informer?

  • Seller: Informer
  • Year Founded: 2012
  • HQ Location: San Francisco, California, United States
  • LinkedIn® Page: www.linkedin.com
    3,858 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Informer?

Inspectiv

Inspectiv is an all-in-one AppSec testing platform that simplifies the process of discovering, validating, and remediating vulnerabilities. By offering penetration testing, bug bounty programs, dynamic application security testing (DAST), and vulnerability disclosure (VDP) in a single solution, organizations can reduce risk, maintain compliance, and strengthen their security posture. With streamlined management, minimal operational overhead, and predictable pricing, Inspectiv delivers impactful results that make security testing more efficient and effective.

Who Is the Company Behind Inspectiv?

Insurepay

Who Is the Company Behind Insurepay?

  • Seller: InsurePay
  • Year Founded: 2003
  • HQ Location: Nolensville, Tennessee, United States
  • LinkedIn® Page: www.linkedin.com
    58 employees on LinkedIn®
Lauren Worth
LW
Researched and written by Lauren Worth
Updated March 5, 2025