Best Penetration Testing Tools - Page 12

How Many Penetration Testing Tools Products Does G2 Track?

Total Products under this Category: 200

Category Stats (Nov 2026)

  • Average Rating: 4.64/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CybaOps (+4.75%) - Among all products in this category, CybaOps recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Penetration Testing Tools Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,900+ Authentic Reviews
  • 200+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

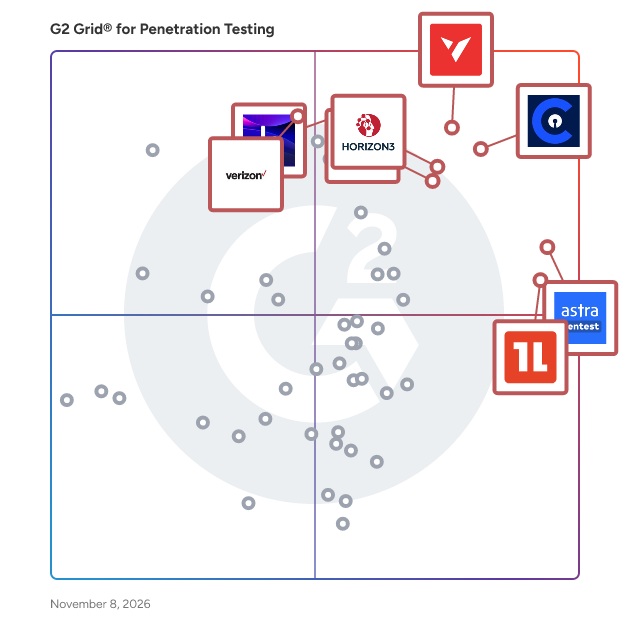
G2 Grid® for Penetration Testing Tools

G2 Grid® for Penetration Testing Tools plotting products by satisfaction and market presence

Highlighted products: Cobalt, vPenTest, Astra Pentest, NodeZero from Horizon3, Oneleet, Pentera, H1 Platform, and Verizon Penetration Testing.

Underlying data: [Grid® JSON](https://www.g2.com/categories/penetration-testing-tools/grids.json?focus%5B%5D=cobalt-io-cobalt&focus%5B%5D=vpentest&focus%5B%5D=astra-pentest&focus%5B%5D=nodezero-from-horizon3&focus%5B%5D=oneleet&focus%5B%5D=pentera&focus%5B%5D=h1-platform&focus%5B%5D=verizon-penetration-testing)

SAINTCloud

SAINT developed SAINTCloud® from the ground up to provide all of the power and capability offered in our fully-integrated vulnerability management solution, SAINT Security Suite, without the need to implement and maintain on-premise infrastructure and software. This means more time spent on reducing risk – less time managing the tools you use.

Average Rating: 4.8/5.0

Total Reviews: 2

Who Is the Company Behind SAINTCloud?

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of SAINTCloud?

SATAN

SATAN is a tool to help systems administrators. It recognizes several common networking-related security problems, and reports the problems without actually exploiting them.

Who Is the Company Behind SATAN?

Scan Search

ScanSearch is an on-demand internet scanner. Instead of querying an indexed snapshot of the internet (Shodan, Censys), you trigger a real, live SYN + service scan of any target — single IPs, CIDRs, country codes or domain lists — and get results in seconds. Built for security researchers, penetration testers, bug-bounty hunters and blue-team defenders who need current data at the moment of the engagement, not weeks-old crawls. Specify the target, the ports (anything from a single port to 1-65535), the modules (open-port discovery, service detection, screenshots, technology stack, CVE matching), and the scan speed (free tier capped at 2 kpps; paid plans from 100 kpps for individual recon up to 10000 kpps for high-throughput country-wide research). Use the web UI or the REST API + official Python SDK. Includes 17 free networking tools (port scanner, SSL checker, subdomain finder, CVE lookup, ASN lookup, ...). Pricing is linear and based on scan speed: from $30/month for individuals, scaling to high-throughput tiers. A free plan is available — no credit card. Crypto checkout supported.

Who Is the Company Behind Scan Search?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

SCYTHE

SCYTHE is an adversary emulation platform (BAS+) catering to the commercial, government, and cybersecurity consulting market. The SCYTHE platform empowers Red, Blue, and Purple teams to swiftly construct and simulate real-world attacks. SCYTHE serves as a robust proactive security tool for scrutinizing detective and preventive controls across multiple communication vectors. Through SCYTHE, with its prepackaged action/behavior logic and threat intelligence, organizations can maintain a continuous evaluation of their risk profile, prioritize vulnerabilities, and take action against threats that matter.

Average Rating: 4.5/5.0

Total Reviews: 1

Who Is the Company Behind SCYTHE?

  • Seller: SCYTHE
  • Year Founded: 2017
  • HQ Location: Columbia, US
  • LinkedIn® Page: www.linkedin.com
    27 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of SCYTHE?

Secqon

SecQon tests your internet-facing assets the way an attacker would, labels every finding by how far it was actually proven, and hands you the OWASP- and SOC 2-mapped report your customer or auditor is asking for.

Who Is the Company Behind Secqon?

  • Seller: Infiqon
  • Year Founded: 2026
  • HQ Location: Noida, IN
  • LinkedIn® Page: www.linkedin.com
    3 employees on LinkedIn®

Secure Schools

The UK’s leading cybersecurity experts serving the education sector.

Who Is the Company Behind Secure Schools?

Securin Offensive Exposure Validation

Securin Validate helps security teams determine which vulnerabilities are actually exploitable in their environment. It runs safe, real-world attack scenarios to confirm which exposures represent proven risk and which are already blocked by existing controls. Unlike traditional point-in-time penetration testing, Securin Validate can run continuously and re-test previously discovered attack paths after patches or configuration changes. This gives teams current proof of exposure instead of a report that becomes outdated soon after delivery. The platform uses a lightweight internal discovery node, called Basecamp, to map reachable assets and services without requiring broad agent deployment or credentialed access. It then applies safe exploitation techniques mapped to MITRE ATT&CK to validate entry points, lateral movement paths, and access to high-value targets. Securin Validate also provides graph-based attack path mapping, showing how an attacker could move through the environment and where controls stop the scenario. It also identifies optimal remediation points, where a single fix breaks multiple attack paths, so teams get the most risk reduction from the least remediation effort. AI-guided validation planning helps teams decide which scenarios to test first based on exploitability and asset context.

Who Is the Company Behind Securin Offensive Exposure Validation?

  • Seller: Securin
  • Year Founded: 2021
  • HQ Location: Albuquerque, New Mexico, United States
  • LinkedIn® Page: www.linkedin.com
    242 employees on LinkedIn®

SecWiz

SecWiz is a software development and cybersecurity platform that combines application building with security services. The platform supports mobile and web app development across iOS, Android, and cross-platform frameworks, offering custom solutions tailored to business needs. With AI and machine learning integration, SecWiz enables intelligent automation alongside API design, microservices architecture, and user-focused UI/UX design. On the security front, SecWiz provides vulnerability assessments, penetration testing, and compliance management for standards like ISO 27001, SOC 2, GDPR, and HIPAA. The risk management tools identify threats, analyze intelligence, and implement mitigation strategies to safeguard assets. SecWiz embeds security throughout the development lifecycle. The four-step framework includes discovery, design, agile development, and continuous improvement to ensure transparent communication and measurable outcomes aligned with business goals.

Who Is the Company Behind SecWiz?

Shinobi

Shinobi is an AI-powered Offensive Security platform that delivers fully autonomous penetration testing for web applications, APIs, mobile apps, and thick clients. It’s the world's first system to supports autonomous testing for mobile applications. Shinobi can detect and chain both syntactic vulnerabilities - such as injection flaws, and semantic vulnerabilities - such as business logic flaws, IDORs, authentication bypasses, and privilege escalations. Built to support enterprise-grade applications, Shinobi handles complex authentication flows including MFA and SSO without custom scripting, integrates natively into CI/CD pipelines, and streams findings in real time so organizations can identify and remediate vulnerabilities continuously, without slowing development velocity.

Who Is the Company Behind Shinobi?

Sn1per Professional

Sn1per Professional is an all-in-one offensive security platform that provides a comprehensive view of your internal and external attack surface and offers an asset risk scoring system to prioritize, reduce, and manage risk. With Sn1per Professional, you can discover the attack surface and continuously monitor it for changes. It integrates with the leading open source and commercial security testing tools for a unified view of your data.

Average Rating: 4.5/5.0

Total Reviews: 1

Who Is the Company Behind Sn1per Professional?

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Sn1per Professional?

SQUR - Autonomous Pentesting

Autonomous pentesting that delivers fast, affordable, and truly actionable results -without the complexity or delays of traditional methods

Who Is the Company Behind SQUR - Autonomous Pentesting?

  • Seller: SQUR
  • Year Founded: 2025
  • HQ Location: Weingarten, DE
  • LinkedIn® Page: www.linkedin.com
    4 employees on LinkedIn®

StaticSpider

Security platform for code, cloud, containers, and web. StaticSpider scans code (secrets, SAST, dependencies, SBOM), containers, and cloud configurations, runs pentest checks and AI code analysis, and adds device and firewall protection with SLAs and reports. Every finding stays pending until a person validates it; nothing is auto-submitted. Free passive website security check at staticspider.com/webscan.

Who Is the Company Behind StaticSpider?

StealthNet

StealthNet is an AI-native penetration testing platform powered by autonomous security agents that execute real exploitation across external infrastructure, APIs, web applications, and human attack surfaces. Unlike traditional vulnerability scanners that generate noisy findings — or manual pentests that are slow and expensive — StealthNet delivers exploit-driven testing at software speed, with compliance-ready reporting for SOC 2, HIPAA, and PCI. Organizations can deploy StealthNet as a recurring platform subscription or leverage hybrid AI + human validation for deeper assessments and audit-ready engagements.

Who Is the Company Behind StealthNet?

Strike Security

Strike's Vulnerability Scanner helps you check any vulnerabilities in your system, specifically designed to obtain Compliance certifications with incredible speed. In just 24 hours, all your domains will be scanned and you will get your Compliance Report (useful for SOC2, ISO 27001, HIPAA, and many other certifications). Get your domains scanned regularly and work to comply with your SLA easily. All the vulnerabilities found will be grouped by criticality and everyone will have clear instructions on fixing it. Get all your vulnerabilities retested easily. Other features: - Recurrent scanning: automatically checks your application while your dev team builds your product. - Subdomain automatic check: the scan will look for vulnerabilities all over your system. - Authenticated scans: better insights on your webpage and also your platform

Who Is the Company Behind Strike Security?

Strobes Agentic Pentesting

Strobes Agentic Pentesting is an AI-agent-native penetration testing and validation platform. Autonomous AI agents run real end-to-end tests across web applications, APIs, network infrastructure, source code, and cloud, then validate every finding with a working proof of concept, full HTTP traces, and reproduction steps. Nothing is reported until exploitation is confirmed, so the false-positive rate on delivered findings is effectively zero. Six specialized AI agents (web app, API, network, code review, cloud, threat intelligence) work in parallel under an AI orchestrator, and assessment context persists across runs so each engagement builds on the last. An 8-phase methodology runs in sandboxed environments with Playwright, sqlmap, Nuclei, and nmap, with out-of-band detection for blind SSRF/XSS and automatic WAF evasion. Test on demand, on a schedule, or continuously. Confirmed findings auto-sync to Jira, GitHub, and Azure DevOps with CI/CD gating. Part of the Strobes CTEM platform. ISO 27001, SOC 2, and CREST certified.

Who Is the Company Behind Strobes Agentic Pentesting?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated March 5, 2025