Best Malware Analysis Tools - Page 3

How Many Malware Analysis Tools Products Does G2 Track?

Total Products under this Category: 55

Category Stats (Sep 2026)

  • Average Rating: 4.51/5 The average rating of products in this category, based on all submitted ratings

Last updated: September 08, 2026

How Does G2 Rank Malware Analysis Tools Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 2,200+ Authentic Reviews
  • 55+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

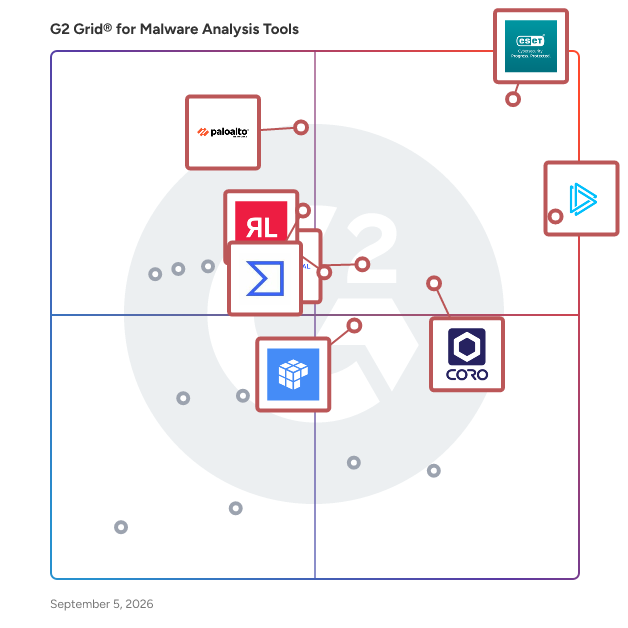
G2 Grid® for Malware Analysis Tools

G2 Grid® for Malware Analysis Tools plotting products by satisfaction and market presence

Highlighted products: ESET PROTECT, ANY.RUN Sandbox, Cloud-Delivered Security Services, Coro Cybersecurity, VirusTotal, Google VirusTotal, ReversingLabs, and Intezer.

Underlying data: [Grid® JSON](https://www.g2.com/categories/malware-analysis-tools/grids.json?focus%5B%5D=eset-protect&focus%5B%5D=any-run-sandbox&focus%5B%5D=cloud-delivered-security-services&focus%5B%5D=coro-cybersecurity&focus%5B%5D=virustotal&focus%5B%5D=google-virustotal&focus%5B%5D=reversinglabs&focus%5B%5D=intezer-intezer)

C-Prot Endpoint Security

With a user-friendly interface, cloud or on-prem based management options and a central control panel, you can easily manage all your endpoint devices (Computer, Mobile Device, Smart TV) from one place.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate C-Prot Endpoint Security?

  • Malware Evaluation: 10.0/10 (Category avg: 9.0/10)
  • Malware Detection: 10.0/10 (Category avg: 9.1/10)
  • File Analysis: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind C-Prot Endpoint Security?

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of C-Prot Endpoint Security?

Domain and IP Intelligence Feeds

Domain and IP Threat Intelligence feeds enable cybersecurity vendors and security operations to make their products and teams faster and more secure. By utilizing machine learning to assess the risk and determine content classifications of hosts, alphaMountain provides real-time threat verdicts for any domain or IP address on the internet. alphaMountain's approach to domain risk is based on three key differentiators: Freshness - real-time domain and IP threat assessments based on first-party algorithms; Fidelity - granularity and context that enable better security outcomes; Factors - contributing rationale that drive all investigations to quick, confident conclusions; By integrating alphaMountain's data into their products, cybersecurity vendors improve the accuracy and performance of their solutions. Security operations teams speed up their investigations through alphaMountain's integrations with leading intelligence platforms including Splunk, SecureX, Maltego, VirusTotal, and more.

Average Rating: 4.7/5.0

Total Reviews: 6

How Do G2 Users Rate Domain and IP Intelligence Feeds?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Domain and IP Intelligence Feeds?

  • Seller: alphaMountain AI
  • Year Founded: 2020
  • HQ Location: Salt Lake City, US
  • Twitter: @alphamountainai
    56 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    9 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Medium, 33% Small

What Do G2 Reviewers Say About Domain and IP Intelligence Feeds?

AI-generated summary from verified user reviews

Pros
  • Users value the high accuracy of Domain and IP Intelligence Feeds, ensuring reliable identification of malicious sites.
  • Users value the responsive alerts that effectively enhance security by quickly identifying and blocking emerging threats.
  • Users value the consistent customer support from Domain and IP Intelligence Feeds, enhancing their overall experience and satisfaction.
  • Users appreciate the ease of use of Domain and IP Intelligence Feeds, finding integration seamless and support helpful.
  • Users appreciate the automation capabilities of the Domain and IP Intelligence Feeds, enhancing security and efficiency in investigations.
Cons
  • Users report issues with false positives, leading to mis-categorizations and missed detections of malicious webpages.
  • Users find the product reasonably expensive, but believe the quality justifies the higher price.
  • Users experience poor detection performance with missed threats and overly generic categorizations of malicious webpages.

What Are Recent G2 Reviews of Domain and IP Intelligence Feeds?

Malzilla

MalZilla is a useful program for use in exploring malicious pages. It allows you to choose your own user agent and referrer, and has the ability to use proxies. It shows you the full source of webpages and all the HTTP headers. It gives you various decoders to try and deobfuscate javascript aswell.

Average Rating: 4.5/5.0

Total Reviews: 1

How Do G2 Users Rate Malzilla?

  • Has the product been a good partner in doing business?: 6.7/10 (Category avg: 8.8/10)
  • Malware Evaluation: 6.7/10 (Category avg: 9.0/10)
  • Malware Detection: 6.7/10 (Category avg: 9.1/10)
  • File Analysis: 8.3/10 (Category avg: 9.0/10)

Who Is the Company Behind Malzilla?

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of Malzilla?

odix Kiosk

The odix Kiosk is a Linux-based hardened workstation dedicated to safely introducing files from removable media. The odix cybersecurity Kiosk has no hard disk and both the operating system and software are SATADOM-based – completely neutralizing the possibility of malicious manipulation. With an encrypted operating system, this solution has the highest resistance against cyber attacks of any kind. The station enables users to plug in any removable media sources, sanitize and ensure that all files are safe to use. odix Kiosk is a perfect solution for secured data exchange from USB flash memory devices to a network (or other devices).

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate odix Kiosk?

  • Malware Evaluation: 8.3/10 (Category avg: 9.0/10)
  • Malware Detection: 10.0/10 (Category avg: 9.1/10)
  • File Analysis: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind odix Kiosk?

  • Seller: odix
  • Year Founded: 2012
  • HQ Location: Rosh Haain, Israel
  • Twitter: @odix
    6 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    18 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of odix Kiosk?

Phishfort Anti-Phishing Solutions

PhishFort offers comprehensive anti-phishing solutions designed to protect brands from online threats such as phishing attacks, impersonation, and brand abuse. Their services encompass real-time detection, swift takedown of malicious content, and continuous monitoring across various digital platforms, ensuring the security of businesses and their customers. Key Features and Functionality: - Domain & Website Protection: PhishFort scans the internet for threats targeting your brand, including fake phishing sites and malware-laden pages, and promptly removes them. - Mobile App Monitoring: The service monitors over 600 app stores to detect and eliminate counterfeit or malicious apps impersonating your brand. - Social Media Content Monitoring: PhishFort identifies and initiates the removal of fraudulent content on major social media platforms that target your brand. - Advanced Detection and Takedowns: Utilizing cutting-edge technology and a team of experienced analysts, PhishFort ensures rapid detection and removal of threats. - Customizable Deployment Packages: The service offers tailored solutions to meet the specific needs of different industries, including finance, healthcare, SaaS, and retail. Primary Value and Problem Solved: PhishFort addresses the growing risk of online brand abuse by providing a multi-layered defense strategy against phishing and impersonation attacks. By safeguarding digital assets, the service helps businesses maintain customer trust, protect revenue, and uphold their brand reputation in an increasingly digital world.

Average Rating: 4.0/5.0

Total Reviews: 1

How Do G2 Users Rate Phishfort Anti-Phishing Solutions?

  • Malware Evaluation: 8.3/10 (Category avg: 9.0/10)
  • Malware Detection: 8.3/10 (Category avg: 9.1/10)
  • File Analysis: 8.3/10 (Category avg: 9.0/10)

Who Is the Company Behind Phishfort Anti-Phishing Solutions?

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of Phishfort Anti-Phishing Solutions?

Re-Sec

Re-Sec solution provides a means preventing cyber threats from entering and spreading within the organization.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Re-Sec?

  • Malware Evaluation: 10.0/10 (Category avg: 9.0/10)
  • Malware Detection: 10.0/10 (Category avg: 9.1/10)
  • File Analysis: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Re-Sec?

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of Re-Sec?

Vortex

Cyberstanc Vortex is designed to enhance the existing frameworks, tools, and techniques for secure data transfer between secure networks. By utilizing Simulation Intelligence and Signature-less detection capabilities, it aims to bridge the gaps and overcome limitations present in current solutions. With its unique "Report, Remove, and Sanitize" feature, Cyberstanc Vortex provides comprehensive protection and ensures the secure transfer of data. One of the key advantages of Cyberstanc Vortex is its exceptional detection accuracy, surpassing traditional anti-virus solutions. By reducing the number of artifacts that need to be sandboxed, it saves valuable time and resources while minimizing the risk of false positives. Through the examination of metadata, file structure, and relationships between files, Cyberstanc Vortex employs simulation intelligence to identify threats effectively. This actionable intelligence provides security teams with detailed information about the nature and behavior of the detected malware, going beyond the simple flagging of files as suspicious, as done by traditional solutions like VirusTotal. Transparency and accountability are paramount for Cyberstanc Vortex. The detection mechanisms are designed and built with a strong emphasis on transparency, ensuring that organizations can trust the accuracy of the results. Cyberstanc Vortex also offers a prototype framework for data sanitization, providing endpoint, network, email, and storage protection. It covers various grey areas that attackers often target, including highly obfuscated and real-world malware techniques such as macro malware, VBA, VBS, PowerShell, DOCx, Calendar files, and more. The platform goes a step further by offering advanced malware simulation of files up to 1GB, providing evidence-based detection and revealing the true nature of the files. While providing robust protection against malware threats, Cyberstanc Vortex maintains a strict no-data acquisition policy, prioritizing user privacy.

Average Rating: 5.0/5.0

Total Reviews: 1

Who Is the Company Behind Vortex?

Who Uses This Product?

  • Company Size: 100% Medium

What Do G2 Reviewers Say About Vortex?

AI-generated summary from verified user reviews

Pros
  • Users are impressed with Vortex's exceptional detection accuracy and its comprehensive protection against threats.
  • Users are impressed with the exceptional detection accuracy and comprehensive protection offered by Vortex.
Cons
  • Users find the price point of Vortex prohibitive, particularly for small to medium-sized businesses and individual users.

What Are Recent G2 Reviews of Vortex?

Deep Instinct Data Security X

Deep Instinct is the only preemptive data security solution that PREVENTS >99% of UNKNOWN and ZERO-DAY threats, including ransomware and AI generated malware before they breach your environment, while providing world-class malware explainability with DIANNA, the DSX Companion. Leveraging the world's only deep learning framework trained for cybersecurity, we prevent threats in <20ms, faster than even the most advanced malware can encrypt. Our streamlined model scales to the needs of the enterprise without introducing operational bottlenecks or vulnerabilities while our lightning-quick scan speeds enable greater throughput than legacy tools can provide. We do it all while maintaining the industry’s lowest false positive rate of <0.1%. After a threat is detected and quarantined, DIANNA, the DSX Companion provides insights and explainability about unknown and zero-day threats in human language to your security teams, augmenting their capabilities and accelerating the investigation and remediation process. DIANNA's unique capabilities save security teams time and money while helping to close vulnerabilities faster and more effectively. Deep Instinct Data Security X (DSX) combines industry-leading static analysis based on the only deep learning framework dedicated to cybersecurity and includes several deployments: * DSX for Applications is a flexible, containerized and highly scalable solution, deployed via API or ICAP, to scan millions of files per day and prevent malicious files from entering storage environments. * DSX for NAS is purpose built for NAS solutions. It scans files at rest or in motion and prevents malicious files from entering your storage. Additionally, the speed of the DSX Brain allows full storage scans, identifying any malicious files that may be waiting to deploy. *DSX for Cloud is purpose built for Cloud storage solutions. It is natively integrated with cloud storage providers to prevent threats before they infiltrate your cloud storage.

Average Rating: 4.3/5.0

Total Reviews: 2

How Do G2 Users Rate Deep Instinct Data Security X?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Deep Instinct Data Security X?

  • Seller: Deep Instinct
  • Year Founded: 2015
  • HQ Location: New York, US
  • Twitter: @DeepInstinctSec
    8,729 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    136 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of Deep Instinct Data Security X?

DOCGUARD Groundbreaking Malware Analysis Platform

DOCGuard is a cutting-edge cybersecurity solution specializing in detecting and analyzing malicious documents. Utilizing advanced structural analysis techniques, DOCGuard identifies threats in Office documents, PDFs, and other file types, providing detailed reports to enhance security measures. Our innovative technology ensures rapid detection with high accuracy, helping organizations protect against evolving cyber threats. Inline SMTP Integration: DOCGuard can be integrated with email systems to analyze incoming and outgoing emails for malicious content. By adding an additional SMTP header with the email's verdict, DOCGuard ensures that only secure emails reach the recipients, while suspicious emails trigger alerts and are blocked if necessary. BCC Integration: DOCGuard can use BCC (Blind Carbon Copy) to analyze emails without interrupting the normal email flow. This allows for continuous monitoring of all emails, providing an additional layer of security by detecting and blocking malicious content before it reaches the intended recipient. SOAR Integration: Security Orchestration, Automation, and Response (SOAR) platforms can leverage DOCGuard's API to validate alerts and enhance incident response. DOCGuard can provide detailed analysis of suspicious files, helping security teams respond more effectively to threats. Incident Response: During digital forensics and incident response (DFIR), DOCGuard can be used to analyze compromised documents and identify indicators of compromise (IOCs). This helps in tracing the source of an attack and understanding the tactics used by threat actors. File Sharing Platforms Integration: DOCGuard can be integrated with file-sharing platforms to ensure that shared documents

Who Is the Company Behind DOCGUARD Groundbreaking Malware Analysis Platform?

Hatching Triage

Triage is Hatching’s new and revolutionary malware sandboxing solution. It leverages a unique architecture, developed with scaling in mind from the start. Triage can scale up to 500.000 analyses per day, an unprecedented number for a sandboxing service.

Who Is the Company Behind Hatching Triage?

  • Seller: Hatching
  • Year Founded: 2015
  • HQ Location: Zaanstad, NL
  • LinkedIn® Page: www.linkedin.com
    6 employees on LinkedIn®

Immunity Debugger

Immunity Debugger is a powerful new way to write exploits, analyze malware, and reverse engineer binary files. It builds on a solid user interface with function graphing, the industry's first heap analysis tool built specifically for heap creation, and a large and well supported Python API for easy extensibility.

Who Is the Company Behind Immunity Debugger?

  • Seller: Immunity
  • Year Founded: 2020
  • HQ Location: Miami, Florida, United States
  • Twitter: @Immunityinc
    6,463 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    402 employees on LinkedIn®

malwareleaks

malwareleaks.com - Cyber ​​Threat Intelligence platform specializing in threat detection and user protection. The main objectives include: - Preventing cyber attacks Early detection and blocking of threats, avoiding phishing campaigns, malware, APT group activities, and botnets. - Minimizing the impact of cyber attacks Reducing the consequences of cyberattacks and preventing new threats. - Protecting the infrastructure Protect critical infrastructure, eliminate ransomware, and prevent data leaks. Our Core Solutions: A web panel for real-time threat detection, with the ability to search for important data among the available information and save it in a convenient form, implemented threat intelligence, search by MITRE ATT&CK® and other functionality for quick threat detection. API integration allows you to interact with the received data quickly. Cyber ​​Threat Intelligence Feed - extracting critical information from the platform and connecting IoCs (identifiers of compromise) to security tools such as Splunk Enterprise, Snort, QRadar, Cloudflare WAF, ELK Stack, and others to protect the infrastructure, block malicious traffic and prevent attacks. This allows for automatic analysis and correlation of security events, anomaly detection, and real-time incident response.

Who Is the Company Behind malwareleaks?

MetaDefender Core

Who Is the Company Behind MetaDefender Core?

  • Seller: OPSWAT
  • Year Founded: 2002
  • HQ Location: Tampa, Florida
  • Twitter: @OPSWAT
    7,257 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,185 employees on LinkedIn®

M&SET

M&SET - The Malware & Social Engineering Toolkit empowers IT staff with advanced digital forensics capabilities to identify threats coming from the most prevalent attack vector today, phishing. Business Email's, Web Applications, Phishing Sites, and Social Media are being used as malware distribution platforms to deliver malware using deep fakes, code injected documents, and compiled malware. Stop malware before it runs server side or on your end points with next generation zero day detection. Now with MITRE ATT&CK integration for behavioral mapping, used during Threat Hunt and Incident Response Scenarios.

Who Is the Company Behind M&SET?

PE File Browser

PE File Browser is a PE explorer that allows you to view the contents of portable executable files. All processor architectures are supported, allowing you to examine ARM executables as well as x86 and x64. As well as displaying the data inside a PE file we also report additional information about the PE file that traditional PE file viewers do not report.

Who Is the Company Behind PE File Browser?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024