Best Intrusion Detection and Prevention Systems (IDPS) - Page 4

How Many Intrusion Detection and Prevention Systems (IDPS) Products Does G2 Track?

Total Products under this Category: 76

Category Stats (Oct 2026)

  • Average Rating: 4.4/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Darktrace / EMAIL (+0.43%) - Among all products in this category, Darktrace / EMAIL recorded the largest rating increase compared to last month

Last updated: October 11, 2026

How Does G2 Rank Intrusion Detection and Prevention Systems (IDPS) Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,700+ Authentic Reviews
  • 76+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

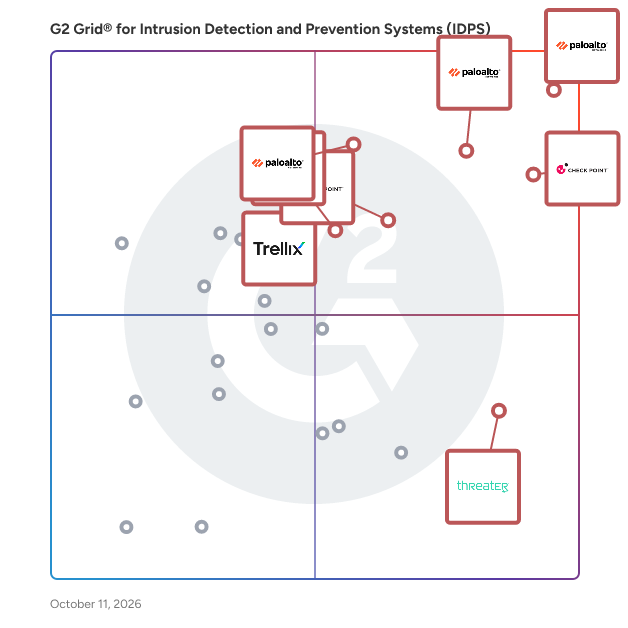
G2 Grid® for Intrusion Detection and Prevention Systems (IDPS)

G2 Grid® for Intrusion Detection and Prevention Systems (IDPS) plotting products by satisfaction and market presence

Highlighted products: Palo Alto Networks Next-Generation Firewalls, Check Point Quantum Intrusion Prevention System (IPS), Palo Alto Networks VM-Series Virtual Firewall, Cloud-Delivered Security Services, Check Point Infinity Platform, Trellix Network Detection and Response (NDR), FortiGate IPS, and threatER.

Underlying data: [Grid® JSON](https://www.g2.com/categories/intrusion-detection-and-prevention-systems-idps/grids.json?focus%5B%5D=palo-alto-networks-next-generation-firewalls&focus%5B%5D=check-point-quantum-intrusion-prevention-system-ips&focus%5B%5D=palo-alto-networks-vm-series-virtual-firewall&focus%5B%5D=cloud-delivered-security-services&focus%5B%5D=check-point-infinity-platform&focus%5B%5D=trellix-network-detection-and-response-ndr&focus%5B%5D=fortigate-ips&focus%5B%5D=threater)

CHESS-P

India's First Secure Hypervisor, Configurable Hardware Enforced Security and Safety Solution, mainly built for mission critical servers, embedded systems, desktops to protect them from Advanced malwares e. g. APT, Rootkit attacks

Who Is the Company Behind CHESS-P?

  • Seller: securweave
  • HQ Location: Hyderabad, IN
  • Twitter: @securweave
    38 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    13 employees on LinkedIn®

Clone Systems VoIP IPS

Clone Systems' VoIP Intrusion Prevention Service (VoIP IPS is a comprehensive security solution designed to protect Voice over IP (VoIP infrastructures from cyber threats. By integrating real-time threat detection and prevention mechanisms, this service ensures the integrity and availability of VoIP communications, safeguarding businesses against potential disruptions and data breaches. Key Features and Functionality: - Real-Time Threat Detection: Continuously monitors VoIP traffic to identify and respond to suspicious activities promptly. - Intrusion Prevention: Actively blocks unauthorized access attempts and mitigates potential attacks before they can impact the system. - Compliance Assurance: Helps organizations meet industry standards and regulatory requirements by maintaining a secure VoIP environment. - Scalability: Adapts to businesses of various sizes, providing tailored protection that grows with organizational needs. Primary Value and Problem Solved: The primary value of Clone Systems' VoIP IPS lies in its ability to secure VoIP networks against evolving cyber threats, ensuring uninterrupted and secure communication channels. By proactively detecting and preventing intrusions, it minimizes the risk of data breaches and service disruptions, thereby protecting sensitive information and maintaining business continuity. This service addresses the critical need for robust VoIP security, allowing organizations to leverage VoIP technology confidently without compromising on security.

Who Is the Company Behind Clone Systems VoIP IPS?

cyber2it

Cyber 2.0 has developed a disruptive cyber-security technology. It is the only system in the world that provides total defense against the spread of cyber attacks within organizational networks. (viruses, ransomware, Trojan, information leakage, browser hijacking, and every new attack). The first computer may be penetrated, but Cyber 2.0 will isolate the attack and block its spreading. Cyber 2.0 puts the system to the test of the best Israeli and International hackers, for a reward of $ 100,000 (The biggest Hackers Challenge). They all failed.

Who Is the Company Behind cyber2it?

  • Seller: Cyber 2.0
  • Year Founded: 2015
  • HQ Location: Rison Letzion, IL
  • LinkedIn® Page: www.linkedin.com
    14 employees on LinkedIn®

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

CYBERSPAN

Who Is the Company Behind CYBERSPAN?

  • Seller: IntelliGenesis
  • Year Founded: 2007
  • HQ Location: Columbia, Maryland, United States
  • LinkedIn® Page: www.linkedin.com
    115 employees on LinkedIn®

DentiGrid

DentiGrid is an enterprise-grade threat intelligence and attack visibility platform designed to help organizations see, understand, and respond to real cyber threats before damage occurs. Unlike traditional security tools that rely on historical logs or third-party feeds, DentiGrid captures live attacker behavior through a distributed global honeypot network and analyzes it in real time using AI-driven threat intelligence. DentiGrid provides organizations with a clear view of who is attacking, how they are attacking, and where the risk is coming from. The platform continuously collects malicious activity data across multiple protocols and regions, transforming raw attack signals into actionable intelligence. Security teams can instantly identify scanning behavior, brute-force attempts, botnet activity, and emerging attack patterns targeting their infrastructure. At the core of DentiGrid is a real-time dashboard that visualizes global attack activity, IP reputation scores, geographic trends, and threat severity. Each malicious IP is enriched with detailed attack metadata, behavioral patterns, and AI-generated risk analysis, enabling faster investigation and informed decision-making. Built-in alerting and webhook integrations allow teams to automate responses and integrate DentiGrid data into existing SIEM, SOC, and security workflows. DentiGrid is designed for startups, SaaS companies, IT service providers, and enterprises that need high-quality threat intelligence without the complexity or cost of traditional enterprise platforms. Its cloud-native architecture ensures fast deployment, minimal maintenance, and scalability as security needs grow. With flexible subscription tiers, organizations can start small and expand as their threat monitoring requirements increase. By focusing on real attacker data instead of assumptions, DentiGrid helps security teams move from reactive defense to proactive threat awareness. The result is improved visibility, reduced attack surface exposure, and faster response to emerging threats — all through a single, intuitive platform. DentiGrid is built by DentiSystems, a cybersecurity company focused on making advanced security intelligence accessible, transparent, and actionable for modern digital businesses.

Who Is the Company Behind DentiGrid?

  • Seller: DentiSystems
  • HQ Location: 101 Kallange Ave, Singapore
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®
  • Phone: +8801308539526

EcoStruxure Security Expert

EcoStruxure Security Expert is a policy-based product that does audit, enforce and report on managed machines with respect to their assigned policies.

Who Is the Company Behind EcoStruxure Security Expert?

  • Seller: Buchi
  • Year Founded: 1939
  • HQ Location: Flawil, CH
  • LinkedIn® Page: www.linkedin.com
    786 employees on LinkedIn®

Ensighten Website Security

Ensighten is a comprehensive website security company, offering next generation client-side protection against data loss, ad injection and intrusion. Through the Ensighten MarSecTM solution, organizations can assess privacy risk and stop unauthorized leakage or theft of data, as well as comply with the CCPA, GDPR and other global data privacy regulations. Threat intelligence underpins our comprehensive security platform with automated analysis specifically focused on client-side attacks, enabling adaptive tuning of rules and configuration. The Ensighten technology gives organizations the ability to bolster their security stance against not only current, but emerging threats. The MarSecTM platform protects some of the largest brands in the world from data leakage whilst ensuring maximum web page performance.

Who Is the Company Behind Ensighten Website Security?

eScan Enterprise EDR (with Neural Intelligence AI/ML Defense)

Your network security is as strong as your least secure endpoint. Even a single endpoint left unsecured will increase your network’s vulnerability. To strengthen your network security, you need to secure each and every endpoint. And only via this way, you can reduce cyberattack risks. A cybercriminal uses following ways to conduct a cyberattack: Launch scripts and executables that download malicious payload or run other malicious programs Run malignant scripts without user’s knowledge in the background Make a program violate its rights and escalate permissions for suspicious activities If unruly behavior is observed across genuine programs, they are assumed malicious as they can get manipulated by malware. In such situations, Boundary Protection Rules can contain all the threats and strengthen your network’s safety. You can use the Safety Check/Audit Mode to analyse how the Boundary Protection Rules (surface attack detection) can improve your network security, if enabled. To ensure your network isn’t jeopardized, always audit events generated by Boundary Protection Rules. This way you can understand how all of your applications are getting affected. Not all genuine applications are developed with maximum security concerns and may appear as if they are executing the same behaviour as malware. By observing the Safety Check Report, you can add security exclusions for genuine applications and apply Boundary Protection Rules to your network, without slowing down endpoint performance. Whenever a boundary protection rule is violated, an alert will be sent to the administrator. You can configure the Alert Settings for multiple recipients, as per your requirements. To ensure maximum protection, you need to deploy a full eScan Enterprise EDR license, which lets you use full capabilities of EDR including Monitoring, Statistics, and workflows available in the eScan Enterprise EDR. The eScan dashboard will display complete EDR activity across your network. You can also download and export the EDR reports to observe actions taken by Boundary Protection Rules.

Who Is the Company Behind eScan Enterprise EDR (with Neural Intelligence AI/ML Defense)?

Exit Point Manager for IBM i

A Key Part of Fortra (the new face of HelpSystems) Powertech is proud to be part of Fortra’s comprehensive cybersecurity portfolio. Fortra simplifies today’s complex cybersecurity landscape by bringing complementary products together to solve problems in innovative ways. These integrated, scalable solutions address the fast-changing challenges you face in safeguarding your organization. With the help of the powerful protection from Exit Point Manager for IBMI i and others, Fortra is your relentless ally, here for you every step of the way throughout your cybersecurity journey.

Who Is the Company Behind Exit Point Manager for IBM i?

  • Seller: Fortra
  • Year Founded: 1982
  • HQ Location: Eden Prairie, Minnesota
  • Twitter: @fortraofficial
    2,773 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,784 employees on LinkedIn®

FortiAIGate

FortiAIGate covers the AI runtime attack surface, protecting LLMs from security threats. Deployed between the app and the model, it manages LLM traffic flows and applies guardrails on the model input and output. With FortiAIGate, you can optimize and secure your AI investments and intellectual property by detecting and preventing model manipulation, prompt injection, excessive consumption, and data leakage. The local, containerized deployment of FortiAIGate offers a lightweight footprint, scalability, and intelligent LLM traffic steering, acting as a proxy between the app and the model to optimize delivery. Output caching offloads duplicate tasks from the model, reducing token consumption and compute costs, while improving the user experience. The solution applies customized guardrails to each LLM endpoint to accurately detect prompt injection, jailbreaking, model poisoning, and attempts to consume excessive resources. Our context-aware DLP engine monitors inbound and outbound traffic to prevent a data breach or model extraction.

Who Is the Company Behind FortiAIGate?

  • Seller: Fortinet
  • Year Founded: 2000
  • HQ Location: Sunnyvale, CA
  • Twitter: @Fortinet
    151,422 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    16,564 employees on LinkedIn®
  • Ownership: NASDAQ: FTNT

Fortinet IPS Rules for AWS Network Firewall

Fortinet Managed IPS Rules for AWS Network Firewall, powered by FortiGuard AI-Powered Security Services, provides AWS customers with advanced, continuously updated intrusion prevention capabilities without requiring additional infrastructure or management overhead. This managed rule service extends Fortinet’s industry-leading threat intelligence and protection directly into AWS Network Firewall environments, helping organizations automatically block exploits, malware, and command-and-control activity at scale. Available on AWS Marketplace. For more information, visit https://vm.fortigate.com/aws/ips-rules.

Who Is the Company Behind Fortinet IPS Rules for AWS Network Firewall?

  • Seller: Fortinet
  • Year Founded: 2000
  • HQ Location: Sunnyvale, CA
  • Twitter: @Fortinet
    151,422 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    16,564 employees on LinkedIn®
  • Ownership: NASDAQ: FTNT

Hawk

Who Is the Company Behind Hawk?

  • Seller: TabMo
  • Year Founded: 2013
  • HQ Location: Paris, FR
  • LinkedIn® Page: www.linkedin.com
    94 employees on LinkedIn®

IBM ZSecure Detection

IBM zSecure Detection is a threat detection and response solution designed specifically for IBM z/OS environments. It helps security teams identify, investigate, and respond to suspicious activity across users, datasets, workloads, network traffic, and cryptographic operations. The solution combines continuous threat monitoring, AI-driven access anomaly detection, network insights, and near real-time security alerting to help organizations detect potentially malicious behavior earlier. It can identify activity such as unusual data access, privilege escalation, suspicious command execution, and unexpected cryptographic activity, while integrating IBM Z security events with enterprise SIEM and security operations workflows. IBM zSecure Detection also supports targeted response and recovery actions, helping organizations reduce threat dwell time, accelerate investigations, contain potential incidents, and strengthen cyber resilience for mission-critical IBM Z workloads.

Who Is the Company Behind IBM ZSecure Detection?

  • Seller: IBM
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • Twitter: @IBMSecurity
    74,660 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM
Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024