Best Intrusion Detection and Prevention Systems (IDPS) - Page 3

How Many Intrusion Detection and Prevention Systems (IDPS) Products Does G2 Track?

Total Products under this Category: 76

Category Stats (Oct 2026)

  • Average Rating: 4.4/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Darktrace / EMAIL (+0.43%) - Among all products in this category, Darktrace / EMAIL recorded the largest rating increase compared to last month

Last updated: October 11, 2026

How Does G2 Rank Intrusion Detection and Prevention Systems (IDPS) Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,700+ Authentic Reviews
  • 76+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

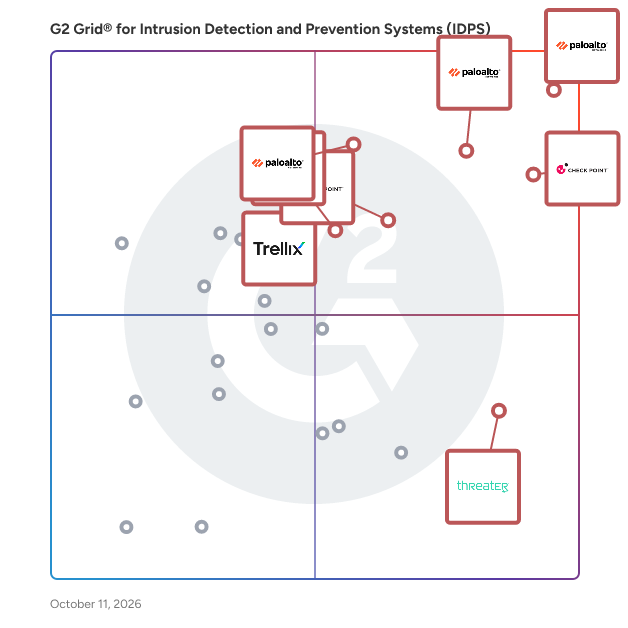
G2 Grid® for Intrusion Detection and Prevention Systems (IDPS)

G2 Grid® for Intrusion Detection and Prevention Systems (IDPS) plotting products by satisfaction and market presence

Highlighted products: Palo Alto Networks Next-Generation Firewalls, Check Point Quantum Intrusion Prevention System (IPS), Palo Alto Networks VM-Series Virtual Firewall, Cloud-Delivered Security Services, Check Point Infinity Platform, Trellix Network Detection and Response (NDR), FortiGate IPS, and threatER.

Underlying data: [Grid® JSON](https://www.g2.com/categories/intrusion-detection-and-prevention-systems-idps/grids.json?focus%5B%5D=palo-alto-networks-next-generation-firewalls&focus%5B%5D=check-point-quantum-intrusion-prevention-system-ips&focus%5B%5D=palo-alto-networks-vm-series-virtual-firewall&focus%5B%5D=cloud-delivered-security-services&focus%5B%5D=check-point-infinity-platform&focus%5B%5D=trellix-network-detection-and-response-ndr&focus%5B%5D=fortigate-ips&focus%5B%5D=threater)

BhaiFi Networks

BhaiFi empowers businesses to forge meaningful connections with their customers through Guest WiFi. By harnessing AI technology, we make network security and compliance effortless, democratizing cybersecurity for businesses of all sizes. Our solutions transform WiFi into a powerful tool for growth - delivering actionable insights, simplifying operations, and allowing you to focus on what truly matters: growing your business and delighting your customers.

Average Rating: 4.2/5.0

Total Reviews: 21

How Do G2 Users Rate BhaiFi Networks?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.0/10)
  • Security hardening: 10.0/10 (Category avg: 8.9/10)
  • Compliance: 10.0/10 (Category avg: 8.8/10)
  • Security Monitoring: 10.0/10 (Category avg: 9.1/10)

Who Is the Company Behind BhaiFi Networks?

  • Seller: BhaiFi
  • Year Founded: 2017
  • HQ Location: Ankit Verma
  • Twitter: @bhaifi
    69 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    24 employees on LinkedIn®
  • Ownership: Ankit Verma

Who Uses This Product?

  • Company Size: 64% Small, 23% Medium

What Are Recent G2 Reviews of BhaiFi Networks?

Dragos Platform

The Dragos Platform is the most effective technology for securing OT environments. Providing automated asset discovery and monitoring capabilities, the Platform delivers asset inventory and visibility across the network. Powered by Dragos OT Cyber Threat Intelligence, the Platform accurately detects threats, providing actionable insights. With a risk-based vulnerability database and risk scoring system, users efficiently prioritize security actions considering operational needs. Expertly crafted OT Response Playbooks streamline investigations in complex operational environments, leveraging insights from the largest ICS/OT practitioner team to effectively respond to adversaries.

Average Rating: 3.8/5.0

Total Reviews: 2

How Do G2 Users Rate Dragos Platform?

  • Has the product been a good partner in doing business?: 6.7/10 (Category avg: 9.0/10)
  • Security hardening: 8.3/10 (Category avg: 8.9/10)
  • Compliance: 8.3/10 (Category avg: 8.8/10)
  • Security Monitoring: 8.3/10 (Category avg: 9.1/10)

Who Is the Company Behind Dragos Platform?

  • Seller: Dragos
  • Year Founded: 2016
  • HQ Location: Hanover, Maryland, United States
  • Twitter: @DragosInc
    26,498 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    687 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Medium, 50% Small

What Are Recent G2 Reviews of Dragos Platform?

Trellix Intrusion Prevention System

McAfee Host Intrusion Prevention for Server boosts server security and lowers costs by reducing the frequency and urgency of patching.

Average Rating: 4.8/5.0

Total Reviews: 2

How Do G2 Users Rate Trellix Intrusion Prevention System?

  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.0/10)
  • Security hardening: 9.2/10 (Category avg: 8.9/10)
  • Compliance: 9.2/10 (Category avg: 8.8/10)
  • Security Monitoring: 9.2/10 (Category avg: 9.1/10)

Who Is the Company Behind Trellix Intrusion Prevention System?

  • Seller: Trellix
  • Year Founded: 2004
  • HQ Location: Plano, TX
  • Twitter: @Trellix
    241,168 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,811 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Small, 50% Medium

What Are Recent G2 Reviews of Trellix Intrusion Prevention System?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

AhnLab AIPS (Advanced IPS)

AhnLab AIPS is the future-driven network intrusion prevention system that detects and blocks advanced network attacks targeting organizations. Why AhnLab AIPS • Intelligence-driven Threat Prevention Backed by our industry-leading threat intelligence, AhnLab AIPS excels in detecting and preventing a broad spectrum of cyber threats that weaponize network, OS, web, and application vulnerabilities, as well as malware and well-known network attacks. • High-Performance Traffic Processing In environments where large-scale traffic processing is needed, AhnLab AIPS delivers fast and precise detection backed by 100G interfaces. The next-gen IPS also performs swift and in-depth analysis of a variety of cyber threats by employing its high-performance engine built on big data processing technology. • Intuitive Data Visualization AhnLab AIPS feeds a wide breadth of information to fuel multi-layered analysis into detected cyber threats. Its cutting-edge ability to visualize analytics in statistics accelerates customers to achieve a greater understanding of context and underlying issues. Key Features • Signature-based Detection & Prevention AhnLab AIPS stands out with its exceptional performance and threat detection & prevention capabilities powered by our high-performance engine and thousands of network attack signatures optimized for blocking the latest network attacks. • Application Control AhnLab AIPS provides precise control over various global applications, thereby effectively blocking application attacks and preventing the leakage of business-critical information. Also, the granular control over application behaviors contributes to a more flexible policy configuration. • Overload Rule Management AhnLab AIPS intelligently identifies and manages rules that could impact product performance. The IPS empowers administrators to pinpoint the causes of overload and evaluate their impact on performance, ensuring smooth operation and business continuity. • Zone Settings Users are allowed to create logically separated security zones within a single appliance. They can categorize these zones by segment, IP range, and VLAN to apply different security policies and controls to each zone.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate AhnLab AIPS (Advanced IPS)?

  • Security Monitoring: 10.0/10 (Category avg: 9.1/10)

Who Is the Company Behind AhnLab AIPS (Advanced IPS)?

  • Seller: AhnLab
  • Year Founded: 1995
  • HQ Location: Seongnam-si, KR
  • Twitter: @AhnLab_SecuInfo
    2,971 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    691 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of AhnLab AIPS (Advanced IPS)?

CA Compliance Event Manager

CA Compliance Event Manager helps you increase your data privacy and simplify regulatory compliance

Average Rating: 4.0/5.0

Total Reviews: 1

Who Is the Company Behind CA Compliance Event Manager?

  • Seller: Broadcom
  • Year Founded: 1991
  • HQ Location: San Jose, CA
  • Twitter: @broadcom
    63,909 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    44,602 employees on LinkedIn®
  • Ownership: NASDAQ: CA

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of CA Compliance Event Manager?

What Are G2 Users Discussing About CA Compliance Event Manager?

Cloud IDS

Cloud IDS Cloud IDS (Cloud Intrusion Detection System) provides cloud-native network threat detection with industry-leading security.

Average Rating: 4.0/5.0

Total Reviews: 1

Who Is the Company Behind Cloud IDS?

  • Seller: Google
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • Twitter: @google
    31,899,995 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

Who Uses This Product?

  • Company Size: 100% Small

What Do G2 Reviewers Say About Cloud IDS?

AI-generated summary from verified user reviews

Pros
  • Users highlight the data management capabilities of Cloud IDS, particularly valuing its AI integration for enhanced functionality.
Cons
  • Users find the complex pricing of Cloud IDS to be a significant barrier to understanding costs effectively.

What Are Recent G2 Reviews of Cloud IDS?

FortiGuard Labs Outbreak Alerts

The FortiGuard team develops effective countermeasures to protect more than 320,000 Fortinet customers around the world. These countermeasures include up-to-the-minute threat intelligence, delivered as a subscription service for Fortinet security products

Average Rating: 4.2/5.0

Total Reviews: 12

How Do G2 Users Rate FortiGuard Labs Outbreak Alerts?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.0/10)

Who Is the Company Behind FortiGuard Labs Outbreak Alerts?

  • Seller: Fortinet
  • Year Founded: 2000
  • HQ Location: Sunnyvale, CA
  • Twitter: @Fortinet
    151,422 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    16,564 employees on LinkedIn®
  • Ownership: NASDAQ: FTNT

Who Uses This Product?

  • Company Size: 69% Medium, 15% Large

What Do G2 Reviewers Say About FortiGuard Labs Outbreak Alerts?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the proactive approach to zero-day malware through quick patch releases for FortiGate devices.
  • Users value the proactive ransomware protection provided by FortiGuard Labs, ensuring timely defenses against evolving threats.
  • Users appreciate the proactive detection of threats provided by FortiGuard Labs Outbreak Alerts, enhancing security measures effectively.
  • Users value the timely software updates that effectively address zero-day malware and enhance security continuously.
Cons
  • Users express concern over the lack of timely updates for firmware exploits and recategorization requests.
  • Users express frustration with the poor customer support, noting delays in addressing firmware exploits and recategorization requests.
  • Users experience poor detection performance as firmware exploits take time to address and recategorization requests go unnoticed.
  • Users report delays in addressing firmware exploits and bugs, impacting the overall effectiveness of FortiGuard Labs Outbreak Alerts.

What Are Recent G2 Reviews of FortiGuard Labs Outbreak Alerts?

Hillstone Cloud Sandbox

Cloud Sandbox delivers a unique, advanced threat detection platform that can emulate the execution environment and analyze all activities related to malicious files, identify advanced threats and collaborate with existing solutions to provide rapid remediation.

Average Rating: 4.0/5.0

Total Reviews: 1

How Do G2 Users Rate Hillstone Cloud Sandbox?

  • Has the product been a good partner in doing business?: 6.7/10 (Category avg: 9.0/10)
  • Security hardening: 8.3/10 (Category avg: 8.9/10)
  • Compliance: 8.3/10 (Category avg: 8.8/10)
  • Security Monitoring: 6.7/10 (Category avg: 9.1/10)

Who Is the Company Behind Hillstone Cloud Sandbox?

  • Seller: Hillstone Networks
  • Year Founded: 2006
  • HQ Location: Santa Clara, US
  • Twitter: @Hillstone_Net
    10,037 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    369 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of Hillstone Cloud Sandbox?

What Are G2 Users Discussing About Hillstone Cloud Sandbox?

NDR by Bricata

Bricata is leading the next generation of advanced network detection and response for the enterprise. By fusing real-time visibility, advanced detection, analysis, forensics, incident response and threat hunting into a single platform, Bricata provides organizations with end-to-end visibility and full context for direct answers and powerful insight to take immediate action.

Average Rating: 4.0/5.0

Total Reviews: 1

How Do G2 Users Rate NDR by Bricata?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind NDR by Bricata?

  • Seller: Bricata
  • Year Founded: 2014
  • HQ Location: Columbia, US
  • LinkedIn® Page: www.linkedin.com
    7 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of NDR by Bricata?

What Are G2 Users Discussing About NDR by Bricata?

Nozomi Networks Platform

Nozomi Networks offers highly accurate, actionable intelligence and protection for integrated cybersecurity at scale. The detailed visibility and in-depth insight provided by Nozomi Networks lets users: • See all the OT, IoT, IT, edge and cloud assets on your networks • Pinpoint the cyber threats and vulnerabilities that matter most • Respond quickly to incidents with forensic analysis tools • Manage asset, security and network data in a single platform • Scale cyber and operational resilience across your entire infrastructure

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Nozomi Networks Platform?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Nozomi Networks Platform?

  • Seller: Nozomi Networks
  • Year Founded: 2013
  • HQ Location: San Francisco, California, United States
  • Twitter: @nozominetworks
    4,238 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    389 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Large

What Do G2 Reviewers Say About Nozomi Networks Platform?

AI-generated summary from verified user reviews

Pros
  • Users highlight the customization features of Nozomi Networks Platform, enhancing their ability to monitor network activities effectively.
  • Users value the effective detection algorithms of Nozomi Networks Platform, which accurately identify intrusions and malicious traffic.
  • Users commend the detection efficiency of Nozomi Networks Platform, effectively identifying intrusions and analyzing traffic patterns.
  • Users value Nozomi's detection algorithms for identifying intrusions and its excellent interface for traffic pattern visualization.
  • Users value the advanced threat detection capabilities of Nozomi Networks, identifying intrusions and malicious traffic effectively.
Cons
  • Users find the Nozomi Networks Platform expensive, yet it aligns with cybersecurity budget constraints against competitors.

What Are Recent G2 Reviews of Nozomi Networks Platform?

AXYVOR

AXYVOR keeps the record of who authorized every security decision — what it rested on, what action followed, and when the reasoning behind it stopped being true. Decision Record Every security decision recorded in AXYVOR carries its authority: the person or AI agent that made it and, for an agent, whether it acted within a granted authority. It preserves the rationale, the alternatives considered, the action that followed, and, when available, the outcome observed afterward. The ledger is append-only and hash-chained. It can be opened exactly as it stood at any point in the past, with information learned later kept out of that historical view. AXYVOR identifies decisions whose supporting reasoning has expired or no longer matches what is being observed. Sealed evidence packs can be independently checked through a public verifier that runs entirely in the browser — no account required, and no need to trust AXYVOR's infrastructure to establish whether the evidence was altered. Exposure Intelligence Every day, AXYVOR measures how the organization appears from the internet using public sources and public-facing measurements only — including certificate transparency, DNS, registration data, TLS and web configuration, email-security records, and public vulnerability and risk intelligence such as CISA KEV, EPSS, and NVD — without authenticated or intrusive access to the organization's systems. It tracks what is new, what disappeared, what changed, and what remains exposed over time. Every finding carries the evidence behind it: what was observed, where, when, and the source or measurement that supports the conclusion. This gives the organization an evidence layer for its external exposure that grows every day, rather than a point-in-time list of alerts. Triage & Prepared Response AXYVOR ingests findings from the security tools an organization connects, correlates them with its own exposure measurements and the assets the organization identifies as critical, and prioritizes them according to business impact rather than technical severity alone. For actionable findings, AXYVOR prepares the recommended response, an estimate of its business impact, a rollback path, and the measurements that should verify success afterward. Execution remains under the organization's control. The Result The result is more than a security log. It is a verifiable record of the security decision itself: what was known, what evidence supported it, who decided, why, what followed, and whether the reasoning still holds. AXYVOR connects exposure, evidence, authority, action and verification into one security record.

Who Is the Company Behind AXYVOR?

BluVector Cortex

As a leader in advanced threat detection, BluVector is empowering security teams to get answers about real threats, allowing businesses and governments to operate with greater confidence that data and systems are protected.

Who Is the Company Behind BluVector Cortex?

  • Seller: BluVector
  • Year Founded: 1994
  • HQ Location: Littleton, Colorado, United States
  • Twitter: @BluVector
    680 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    614 employees on LinkedIn®

Canid

Who Is the Company Behind Canid?

CERNE

The Telesoft CERNE combines a high rate 40Gbps IDS engine with automated record of relevant network traffic for real-time and historical threat investigation. CERNE continuously scans and collects all network packets and only stores traffic associated with an IDS alert, discarding all other traffic, giving an analyst rapid access to critical packets up to 2.4 seconds before an event.

Who Is the Company Behind CERNE?

  • Seller: Telesoft
  • Year Founded: 1989
  • HQ Location: Blandford, GB
  • Twitter: @Telesoft_Tech
    4,338 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    121 employees on LinkedIn®
Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024