Nebulock
Nebulock operates as an AI-driven threat hunting platform.
Who Is the Company Behind Nebulock?
- Seller: Nebulock
- HQ Location: Brookline, US
-
LinkedIn® Page: www.linkedin.com
24 employees on LinkedIn®
Total Products under this Category: 113
Last updated: November 02, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
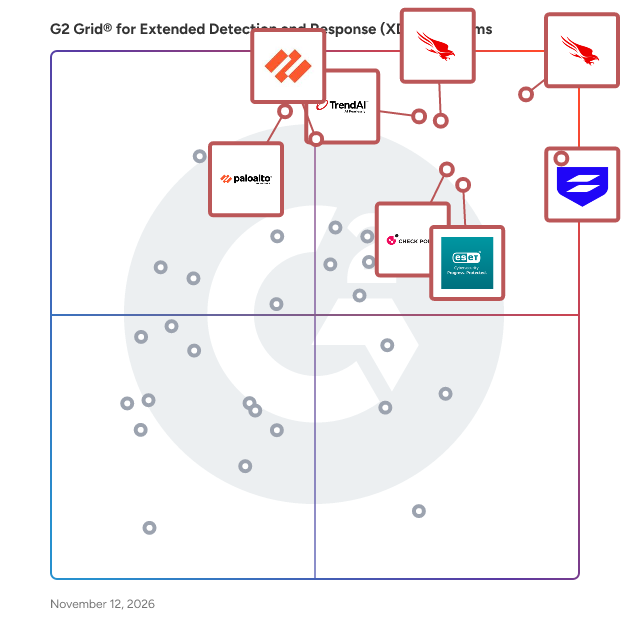
Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Sophos Endpoint, CrowdStrike Falcon Cloud Security, TrendAI Vision One, Check Point Endpoint Security, ESET PROTECT, Palo Alto Cortex XSIAM, and Cortex XDR.
Underlying data: [Grid® JSON](https://www.g2.com/categories/extended-detection-and-response-xdr-platforms/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=sophos-endpoint&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=trendai-vision-one&focus%5B%5D=check-point-endpoint-security&focus%5B%5D=eset-protect&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=palo-alto-networks-cortex-xdr)
Nebulock operates as an AI-driven threat hunting platform.
Nozomi Networks offers highly accurate, actionable intelligence and protection for integrated cybersecurity at scale. The detailed visibility and in-depth insight provided by Nozomi Networks lets users: • See all the OT, IoT, IT, edge and cloud assets on your networks • Pinpoint the cyber threats and vulnerabilities that matter most • Respond quickly to incidents with forensic analysis tools • Manage asset, security and network data in a single platform • Scale cyber and operational resilience across your entire infrastructure
Average Rating: 5.0/5.0
Total Reviews: 1
AI-generated summary from verified user reviews
"Nozomi offers excellent OT IDS"
Rating: 5.0/5.0 stars
— Verified User in Oil & Energy
Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.
Rapid changes in the cyber threat landscape require organizations to uncover hidden risks and threats before they have an impact on the bottom line, operations and reputation. Organizations can no longer rely on perimeter defenses for network security, especially against pernicious ransomware attacks. In addition, many security teams don't have the resources required to effectively monitor security alerts or detect and respond against advanced threats.
OpenText™ Cybersecurity Aviator™ is an advanced AI-driven solution designed to revolutionize threat detection and enhance organizational security postures. By leveraging machine learning models that continuously learn and adapt, it enables rapid deployment of new threat detection models within hours, effectively protecting against both known and emerging cyber threats. Key Features and Functionality: - AI-Powered Threat Detection: Utilizes unsupervised machine learning to identify and classify cyber threats by analyzing vast amounts of security events, uncovering hidden behavior-based patterns. - Rapid Deployment: Facilitates the swift implementation of new threat detection models, ensuring organizations can respond to evolving threats promptly. - Continuous Learning: Employs machine learning models that automatically and continuously learn, enhancing the accuracy and effectiveness of threat detection over time. - Scalability and Flexibility: Offers cloud-based efficiency, allowing organizations to scale their security operations seamlessly without significant infrastructure changes. Primary Value and Problem Solved: OpenText Cybersecurity Aviator addresses the critical need for agile and effective threat detection in an era of rapidly evolving cyber threats. Traditional threshold-driven methods often fall short in identifying sophisticated attacks. By integrating AI and machine learning, Cybersecurity Aviator provides organizations with a proactive defense mechanism that adapts to new threats as they emerge, significantly reducing the time to detect and respond to incidents. This not only enhances the overall security posture but also alleviates the burden on security teams, allowing them to focus on strategic initiatives rather than being overwhelmed by false positives and manual threat analysis.
OpenText Secure Cloud is a comprehensive, cloud-native platform designed to streamline cybersecurity management for Managed Service Providers (MSPs) and Small to Medium-sized Businesses (SMBs). By consolidating account management, license provisioning, security insights, and threat response into a single interface, Secure Cloud simplifies operations, allowing businesses to focus on growth and delivering exceptional services. Key Features and Functionality: - Centralized Management: Manage products, licenses, and billing through a unified platform, enhancing operational efficiency and oversight. - Customizable Bundles: Offer tailored security solutions with flexible, customizable bundles that meet diverse client needs. - API and PSA Integrations: Seamlessly connect with platforms like Kaseya, Autotask, ConnectWise, and HaloPSA to simplify billing and management processes. - Integrated Dashboard: Utilize intuitive tools such as an order history page, customer events calendar, and task alerts to manage tasks, customers, and orders effortlessly. - Customer Relationship Management: Leverage integrated tools like event calendars and renewal alerts to maintain and strengthen client relationships. - Cost Reduction and Margin Enhancement: Automate tasks, unify billing, and implement bundled solutions to deliver greater value to clients while reducing operational costs. Primary Value and Solutions Provided: OpenText Secure Cloud addresses the complexities of cybersecurity management by offering a centralized, user-friendly platform that enhances operational efficiency and scalability. For MSPs, it simplifies service delivery, enabling them to provide comprehensive security solutions with ease. SMBs benefit from robust protection and streamlined operations, allowing them to focus on core business activities without the burden of managing multiple security tools. By integrating various functionalities into a single platform, Secure Cloud reduces overhead, improves service consistency, and supports business growth.
Percept XDR ensures end-to-end security, threat detection and response while allowing enterprises to focus on their core business growth without the fear of compromise. Percept XDR helps to protect against phishing, ransomware, malware, vulnerability exploits, insider threats, web attacks and many more advanced attacks. Percept XDR features SOAR-based automated response in line with the MITRE ATT&CK framework. The reduced number of incidents that require manual intervention allows enterprise IT teams to focus on the core objectives.
Reveelium.ai is an AI-enabled collaborative cybersecurity platform that unifies SIEM/XDR, EASM, SOAR, and Cyber Threat Intelligence (CTI) into a single, modular solution. It helps organizations anticipate, detect, investigate, and respond to cyber threats in real time while automating security operations Reveelium.ai is a scalable, AI-powered cybersecurity platform designed to provide complete visibility and control over an organization's cyber risk. Combining SIEM/XDR, External Attack Surface Management (EASM), Security Orchestration, Automation and Response (SOAR), and Cyber Threat Intelligence (CTI), it centralizes security operations within a single collaborative platform. Built with advanced AI technologies, including Machine Learning, Deep Learning, LLMs, and UEBA, Reveelium.ai enhances threat detection, reduces false positives, prioritizes alerts, and accelerates incident response. Its multi-tenant architecture, customizable detection scenarios, API-driven integrations, and flexible deployment options (on-premises or dedicated SaaS hosted in France) make it an ideal solution for organizations seeking a modern, proactive, and scalable Security Operations Platform.
Rilevera is an AI Detection Engineer platform built for security teams that need to move beyond static, set-it-and-forget-it detection logic. The platform continuously validates, improves, and operationalizes detection rules across SIEM, EDR, and data platforms, ensuring that the rules security teams rely on are actually working at all times. The core problem Rilevera solves is one that most security organizations quietly struggle with: detection drift. Schema changes, missing logs, platform updates, and silent failures erode detection coverage over time, often without anyone knowing. By the time teams discover a rule has broken, coverage gaps have already existed for weeks or months. Rilevera addresses this through four primary capabilities: Continuous Validation monitors detection logic, telemetry dependencies, and schema integrity across platforms in real time. If a rule breaks or data disappears, the team knows immediately rather than discovering it during an incident. Detection Health and Improvement analyzes performance data, false positive trends, logic overlap, and rule quality to surface recommendations and push validated updates back into execution platforms. Coverage Mapping aligns detections and telemetry to the MITRE ATT&CK framework and known threat actors, identifying blind spots and helping teams prioritize where to build new rules. Structured Engineering Workflows bring discipline to the full detection lifecycle, including design, validation, peer review, and controlled deployment, so detection engineering scales with the team rather than against it. The platform essentially acts as an autonomous layer that connects threat intelligence, red team activity, and detection engineering into a unified control plane, allowing teams to translate detection work into measurable risk reduction they can report to leadership. Rilevera is positioned for enterprise security teams, particularly in high-compliance industries like banking, financial services, and insurance, where detection coverage is a direct line to regulatory and operational risk.
Samurai XDR SaaS, developed by global security leader NTT, has access to one of the largest T1 Internet backbones. This access gives Samurai the unique ability to gather intelligence and then detect and identify threats in real-time before they can cause damage. Samurai XDR plays well with others - not hardware vendor specific. Samurai XDR SaaS integrates with all major IT infrastructure and security products through open APIs and cloud connectors. This allows you to leverage your existing investments while future-proofing your business as new technologies emerge. The moment our AI detects malicious activity, you can call our integrated response into action to neutralize the attack. But Samurai XDR doesn’t stop there. It also helps you proactively hunt for risks and improves the overall security posture of your organization. With Samurai XDR SaaS, you get enterprise-grade security capabilities without the need for on-premises infrastructure – enabling businesses of any size to access capabilities that were previously only available to large enterprises.
SEKOIA provides Consulting, Expertise and Innovation in cybersecurity to respond to the challenges of a VUCA world.
ShadowPlex, by Acalvio, is a leading advanced threat protection solution that uses AI-powered deception technology to detect and disrupt APT and AI-driven attacks. Designed to identify stealthy attacker behaviors such as reconnaissance, credential harvesting, and lateral movement early in the attack lifecycle, ShadowPlex ensures high-speed, precise threat detection before breaches occur. The platform employs adaptive deception, continuously evolving to match sophisticated threat tactics and breaking attack chains dynamically. With seamless deployment across IT, cloud, and OT environments, ShadowPlex strengthens defenses without disrupting operations. By mapping detections to MITRE ATT&CK, it prioritizes defense actions based on real-world attacker behavior. This cutting-edge advanced Threat Defense solution provides proactive, preemptive security, helping enterprises detect and neutralize threats before they escalate.
ShieldVision is security software that provides threat detection, investigation, response capabilities, and managed SOC services.
