Cynco
Who Is the Company Behind Cynco?
- Seller: Cynco
- Year Founded: 2024
- HQ Location: Kuala Lumpur, MY
-
LinkedIn® Page: www.linkedin.com
3 employees on LinkedIn®
Total Products under this Category: 113
Last updated: November 02, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
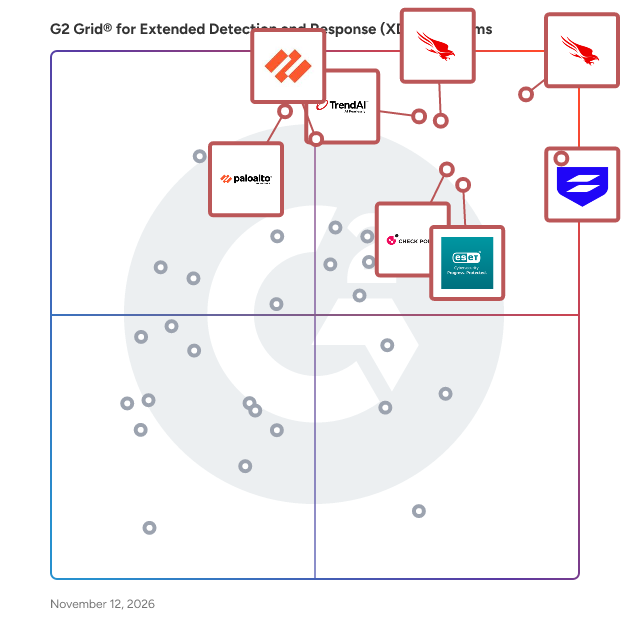
Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Sophos Endpoint, CrowdStrike Falcon Cloud Security, TrendAI Vision One, Check Point Endpoint Security, ESET PROTECT, Palo Alto Cortex XSIAM, and Cortex XDR.
Underlying data: [Grid® JSON](https://www.g2.com/categories/extended-detection-and-response-xdr-platforms/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=sophos-endpoint&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=trendai-vision-one&focus%5B%5D=check-point-endpoint-security&focus%5B%5D=eset-protect&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=palo-alto-networks-cortex-xdr)
Defense.com is an XDR platform that contains everything your organisation needs to detect and respond to cyber threats across all areas of your network, without the enterprise price tag or complexity. Without a solution like Defense.com, you can spend a lot of time and resources manually correlating data from multiple, disparate security tools in order to identify and remediate cyber threats. Defense.com ingests and correlates native and third-party security data from all areas of your environment into a single detection and response platform, helping you to quickly identify threats and prevent breaches. In addition to threat detection and response, the Defense.com platform also helps your organisation strengthen its security posture with built-in vulnerability scanning, endpoint protection, external attack surface monitoring and security awareness training. Managed services Small and medium sized organisations often lack the time or resources to properly monitor their environment, forcing them to settle for just business hours coverage. Defense.com solves this challenge with a 24/7 Managed SIEM service, backed by our in-house SOC analysts and our advanced log monitoring technology. We can take the pressure off your team by monitoring your organisation's environment on your behalf, alerting you to genuine threats and providing detailed remediation advice to help fix issues fast. Why choose Defense.com? Unlike many other providers on the market that operate as MSSPs with third party technology, Defense.com has developed a proprietary SIEM platform that delivers advanced threat detection capabilities and can ingest logs from any system or vendor. This enables organisations to make the most out of their existing security investments, break free from vendor lock-in, and monitor everything in their environment for security threats. We also operate our own in-house SOC team, who provide 24/7 proactive threat detection and log monitoring. Our managed services alleviate the pressure on IT teams by proactively looking for malicious activity in their networks and raising security alerts to their attention, saving them time and ensuring that they only focus on genuine risks. Existing vendors on the market provide complex and expensive solutions that are usually tailored to enterprise organisations with in-house SecOps teams. Defense.com stands out as a more accessible alternative for SMEs in comparison to the current MDR and XDR category leaders.
Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.
Enforcium is business management software built for companies that have outgrown running everything through the founder's memory but haven't yet built formal systems to replace it. It brings goals, KPIs, team structure, and processes into one connected system, instead of spreading them across a task manager, a spreadsheet, and a deck nobody opens after the kickoff meeting. Most operations management software solves one piece of that problem. Enforcium is built to connect all of them. Every goal has a target and a named owner. Every metric can be linked directly to the goal it supports, so when a KPI slips, it's immediately clear which goal is at risk — not something leadership discovers three weeks later in a status meeting. Every process gets documented as a step-by-step SOP with a clear owner, so new hires aren't relying on tribal knowledge to learn how the team actually works. The core of the product is a metrics tree that classifies every KPI as an input, output, or North Star metric — input metrics being the actions a team directly controls, output metrics the results those actions produce, and North Star metrics the one number per function that represents long-term success. That structure makes it clear which numbers a team should actually act on day to day, rather than staring at a dashboard full of figures with no sense of what to do about any of them. Enforcium also includes a built-in task manager and an accountability view that shows exactly who owns what across the company — goals, metrics, and processes alike — so leadership can see where execution is breaking down without chasing down status updates manually. The product is aimed at agencies, IT services and outsourcing firms, SaaS companies, and professional services teams, typically somewhere between 15 and 200 employees — the stage where a company has too many moving parts for informal coordination to work, but isn't yet running the kind of formal operating system that larger organizations depend on. Rather than adding another disconnected tool to an already crowded stack, Enforcium gives growing teams one place to see whether the business is actually on track and who's responsible for keeping it there.
eScan Vision Core XDR delivers government-grade cybersecurity with Neural Intelligence AI/ML Defense through three deployment models: secure on-premises installations for classified environments, scalable cloud SaaS for rapid enterprise deployment, and SOC2-certified cloud solutions for government agencies requiring enhanced compliance. eScan Vision Core XDR is an advanced Extended Detection and Response (XDR) platform that provides real-time visibility, analysis, protection, and remediation across enterprise endpoints. The platform delivers comprehensive threat insights and automated alerts, enabling security teams to conduct faster investigations and implement rapid response measures that minimize attack impact.
Mandiant Advantage is a multi-vendor XDR platform that delivers Mandiant’s transformative expertise and frontline intelligence to security teams of all sizes.
Average Rating: 5.0/5.0
Total Reviews: 1
Rating: 5.0/5.0 stars
— Semih G.
While GoSecure Professional Security Services focuses on finding the problems, GoSecure Titan® Managed Security Services make sure to solve them – making GoSecure your ally to consolidate, evolve & thrive. Our service offering includes: • GoSecure Titan® Managed Extended Detection & Response (MXDR) which offers the best-in-class 15-minute response time from threat detection to mitigate with a solution that identifies, blocks, & reports potential breaches. • GoSecure Titan® Vulnerability Management as a Service (VMaaS) helps defend against the constantly changing threat landscape by continuously identifying critical assets, threats and vulnerabilities and working quickly to remediating threats as they arise allowing businesses to get more value from their security and IT operations. • GoSecure Titan® Managed Security Information and Event Monitoring (SIEM) offers advanced security intelligence, comprehensive incident handling, simplified compliance, scalability, threat intelligence integration, and optimized security operations. • GoSecure Titan® Managed Perimeter Defense (MPD) helps organizations address the challenge of monitoring and managing their firewall infrastructure. Whether a single firewall, or hundreds, GoSecure has the skills and resources to manage any size environment. Operating 24x7x365, the GoSecure Security Operations Center (SOC) provides global coverage to keep your firewalls operating at peak efficiency. • GoSecure Titan® Inbox Detection & Response (IDR) gives every user the ability to test any suspicious email. They can finally stop worrying about missing threats, wasting time wondering what to do, or worrying about “crying wolf” too often. With a simple click, employees now become a united force against phishing. GoSecure Titan® IDR is the perfect solution to remediate the phishing problem. Enhance your organization’s cyber defense capabilities GoSecure Titan® Managed Security Services provides industry-leading response and mitigation speeds, essential in today’s rapidly evolving threat landscape. Our services are designed to keep your business safe and secure, ensuring peace of mind in the face of growing cyber threats.
Average Rating: 3.0/5.0
Total Reviews: 1
Hexnode XDR is an extended detection and response (XDR) software solution designed to help organizations detect, investigate, and respond to security threats across managed endpoints from a centralized platform. It consolidates endpoint telemetry and security signals to provide contextual visibility into potential threats, enabling security and IT teams to take timely and informed action. Hexnode XDR is primarily used by IT administrators and security teams that need greater visibility into endpoint activity and a structured way to investigate and contain security incidents. By correlating endpoint data in real time, the platform helps reduce alert noise and supports faster identification of suspicious behaviour across devices. The solution extends beyond traditional endpoint detection and response (EDR) by providing a more holistic view of security events. Hexnode XDR also supports automated and manual response actions to help contain threats efficiently. Security teams can define response workflows or take direct action from a unified console, reducing investigation time and minimizing the potential impact of security incidents. The platform is designed to integrate smoothly into existing endpoint management workflows, making it suitable for organizations looking to strengthen endpoint security while maintaining operational efficiency. Key Features Include: Real-time Endpoint Visibility: Continuous monitoring of all managed endpoints to ensure total transparency. Advanced Threat Hunting: Proactively search for hidden indicators of compromise (IoCs) across the environment. Contextual Alerting: Intelligent correlation of security events to reduce alert fatigue and prioritize critical incidents. One-Click Remediation: Instantly isolate devices, terminate malicious processes and quarantine suspicious files. Unified Security Console: Manage detection, investigation, and response without switching between multiple platforms. Hexnode UEM Integration: Allows security teams to align threat response with endpoint policies and device controls
Huntsman Security’s Next Gen SIEM is a cyber security analytics product with built-in threat intelligence and behaviour anomaly detection, designed to analyse high volume streams of data in real-time to quickly and accurately detect non-compliant system activity, anomalous behaviour, security issues and cyber threats.
Average Rating: 4.0/5.0
Total Reviews: 1
"Enterprise-wide security management system"
Rating: 4.0/5.0 stars
— Kristian T.
Native Extended Detection and Response (XDR) platform for critical infrastructure protection. Purpose-built platform delivering multi-layered protection for operational technology (OT) environments. • Infrastructure visibility. Track all connected devices and their configurations. Build a network graph and analyze data flows • Threat elimination. Mitigate threats across hosts and networks, with insights into root causes and safe response measures •Risk assessment. Assess vulnerabilities and check security settings changes for hosts, network devices and controllers Kaspersky Industrial CyberSecurity features natively integrated nodes and network security products for protection of modern and legacy OT assets, automation and control systems, without affecting technological process or system availability. • Kaspersky Industrial CyberSecurity for Networks monitors and analyses industrial network traffic to provide full-fledged visibility into industrial assets and communications. By identifying anomalies and intrusions in the OT infrastructure at an early stage, KICS for Networks helps prevent any negative impact on industrial processes. • Kaspersky Industrial CyberSecurity for Nodes is a low-footprint solution that ensures security of each and every Windows and Linux system within today’s diverse industrial environments. It combines traditional endpoint protection with OT-specific controls. KICS for Nodes is also available as a portable, installation-free scanner for sensitive, isolated or legacy machinery and bring-in contractors’ devices.
