RiskQuilt
Who Is the Company Behind RiskQuilt?
- Seller: RiskQuilt
- HQ Location: N/A
-
LinkedIn® Page: www.linkedin.com
1 employees on LinkedIn®
Total Products under this Category: 178
Last updated: September 01, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
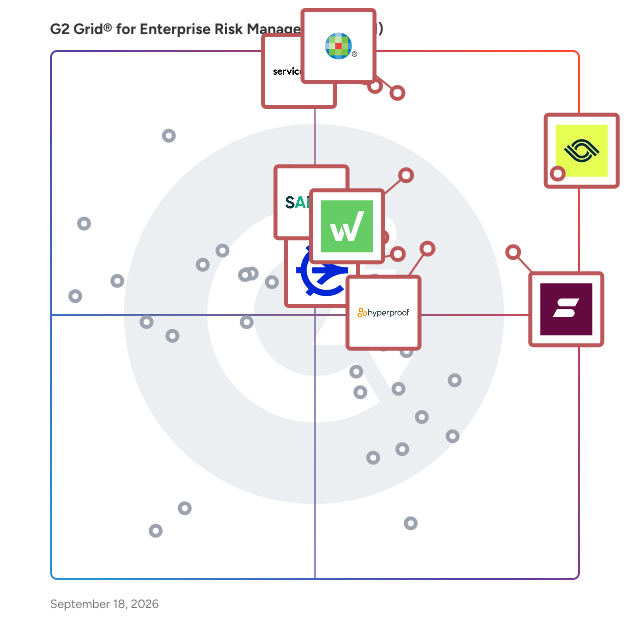
Highlighted products: Optro, TeamMate, ServiceNow Governance, Risk, and Compliance (GRC), Sprinto, Workiva, Hyperproof, LogicGate, and SAI360.
Underlying data: [Grid® JSON](https://www.g2.com/categories/enterprise-risk-management-erm/grids.json?focus%5B%5D=optro&focus%5B%5D=teammate&focus%5B%5D=servicenow-governance-risk-and-compliance-grc&focus%5B%5D=sprinto-inc&focus%5B%5D=workiva-workiva&focus%5B%5D=hyperproof&focus%5B%5D=logicgate&focus%5B%5D=sai360)
Riskware is an integrated AI-powered platform that unifies all your Governance, Risk and Compliance (GRC) functions, while also managing Health, Safety and Environment (HSE), empowering your organisation to holistically manage everything risk.
Rizzqo is asset-first Compliance Execution for regulated organizations. It turns security and regulatory frameworks into concrete work on the assets they affect, assigns that work to the people responsible, and shows ISMS teams and CISOs how compliance is actually implemented across the organization. Most compliance programs are built top-down. Frameworks become controls, controls become policies, and security teams are left trying to find out whether those policies are actually implemented anywhere. A policy is not proof of implementation. Rizzqo adds the execution layer. You model your organization once: the critical services, information and processes you need to protect, the applications, systems, infrastructure and providers they depend on, and who is responsible for each. Controls are translated into requirements that are specific to the type of asset they apply to. When an asset is added or classified, the requirements that apply to it appear automatically and are assigned to its owner. The owner answers each requirement, attaches evidence and confirms the answer. Implementation status, evidence, gaps and risks then roll back up to management. Key capabilities: Asset and dependency model: critical services, information, processes, supporting assets and responsible owners in one connected structure. Frameworks and controls: ISO 27001, ISO 27002, NIS2, DORA, GDPR, EU AI Act, CRA, TISAX, ISO 21434, ISO 27017, MVSP, NIST CSF 2.0 and RL CySec-Rail, plus your own company-specific frameworks and requirements. Asset-specific requirements: applied automatically based on asset category, assigned to responsible owners, answered and evidenced where implementation happens. One requirement can satisfy controls from several frameworks, so the same work is not repeated per framework. Evidence and implementation status: evidence attached to the requirement on the asset, answers confirmed and logged, status calculated from what has actually been answered rather than self-declared. Gaps and risk: open requirements are visible as gaps. Gaps can be documented as risk assessments with inherent, current and residual scoring and a treatment decision, so unfinished work becomes a conscious management decision instead of hidden debt. Tasks: remediation work assigned and tracked, with Jira integration. Management visibility: dashboards showing framework readiness, open gaps and which critical services are exposed by them. Privacy and AI context: PII flows made visible in the dependency model, with processing purpose and legal basis captured on supporting assets. AI assets identified in the same model and assigned an AI risk class. Who it is for: ISMS managers and information security managers who run the program day to day, and CISOs who need a reliable view for management. Strongest fit: regulated mid-sized organizations with several frameworks, responsibility spread across many teams and asset owners, complex asset environments and limited compliance headcount. Rizzqo GmbH is based in Lindau, Germany. The platform is built and hosted in Germany.
RUBiQ provides an agile GRC solution that is flexible to the organization’s current requirements and grows with the organization as requirements change and processes evolve. The solution enables GRC management programs at any level of the organization, whether for departments or enterprise-wide risk management programs. RUBiQ is a solution that can grow and expand with the organization, and adapt as the organization and its environments change. It can be implemented to meet focused risk and control management requirements for organizations needing to address a specific area or implemented as the information and technology architecture core for the breadth of GRC management functions across the organization. RUBiQ offers solutions for Risk Management, Compliance Managemen, EH&S Management, Issue Reporting Incident Management, Issue Reporting Incident Management, Business Continuity Management, Policy & Procedure Management, Audit Management, and Third-Party Management.
Average Rating: 4.0/5.0
Total Reviews: 1
"RubiQ BCM module good for crisis management"
Rating: 4.0/5.0 stars
— Niraj O.
Rukn ERM is a mobile and web enterprise risk platform aligned to the COSO ERM 2017 framework. Risk register, KRIs, risk appetite, controls, incidents, governance, compliance, audits and Monte Carlo quantification — with board-ready reporting, in Arabic and English.
Software de Gestión de Riesgos para Empresas: Identifica, analiza y trata riesgos con el mismo rigor que las grandes organizaciones, sin la complejidad ni el costo de una consultora. Aplicación de normas ISO31000 e ISO27001
SmartFlow Enterprise is the most complete license compliance solution available and includes business analytics, lead generation, customizable reporting, an open API, and CRM integration with Salesforce.
