Top Free Application Shielding Software

How Many Application Shielding Software Products Does G2 Track?

Total Products under this Category: 34

Category Stats (Oct 2026)

  • Average Rating: 4.62/5 (↑0.03 vs Sep 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Promon Shield for Mobile (+9.38%) - Among all products in this category, Promon Shield for Mobile recorded the largest rating increase compared to last month

Last updated: October 07, 2026

How Does G2 Rank Application Shielding Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,100+ Authentic Reviews
  • 34+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

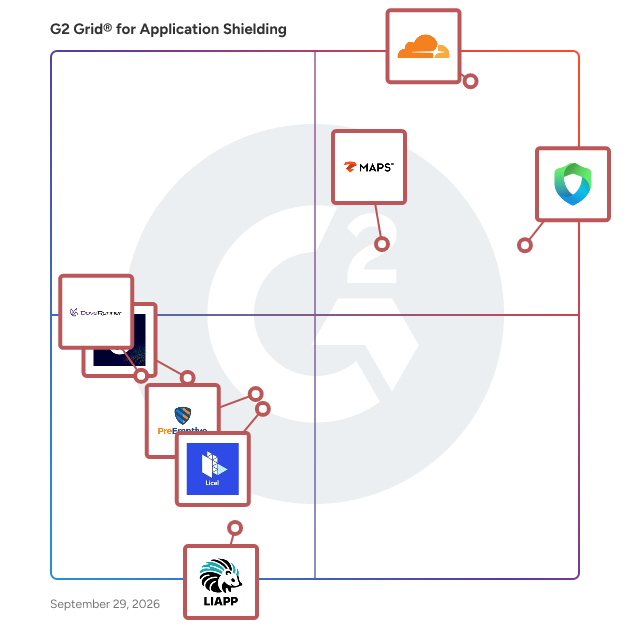
G2 Grid® for Application Shielding Software

G2 Grid® for Application Shielding Software plotting products by satisfaction and market presence

Highlighted products: Cloudflare Application Security and Performance, Appdome, Zimperium Mobile Application Protection Suite (MAPS), PreEmptive, DexProtector, Jscrambler, DoveRunner, and LIAPP.

Underlying data: [Grid® JSON](https://www.g2.com/categories/application-shielding/grids.json?focus%5B%5D=cloudflare-application-security-and-performance&focus%5B%5D=appdome&focus%5B%5D=zimperium-mobile-application-protection-suite-maps&focus%5B%5D=preemptive&focus%5B%5D=dexprotector&focus%5B%5D=jscrambler&focus%5B%5D=doverunner&focus%5B%5D=liapp)

Appdome

Appdome is an agentic platform that protects mobile apps and the mobile business at scale. Trusted by enterprises worldwide, Appdome automates mobile app security, fraud prevention, bot defense, and threat detection and response across Android and iOS applications. Unlike legacy SDK-based approaches that require manual implementation and ongoing maintenance, Appdome uses AI agents to embed protections directly into mobile apps, analyze threats in real time, and continuously adapt defenses without code or complex integration. Organizations use Appdome to protect mobile apps, APIs, identities, accounts, transactions, and users from fraud, bots, malware, account takeover, deepfakes, and other cyber threats. Appdome’s agentic mobile defense platform includes: Identity and reputation protection Fraud and account takeover (ATO) prevention Bot and API defense Mobile app security (RASP and app shielding) DevSecOps and CI/CD integration Threat management and response (including ThreatScope™ Mobile XDR, ThreatEvents™, and Threat Resolution Center™)

Average Rating: 4.8/5.0

Total Reviews: 96

How Do G2 Users Rate Appdome?

  • Ease of Use: 9.2/10 (Category avg: 8.7/10)
  • Quality of Support: 9.6/10 (Category avg: 9.0/10)

Who Is the Company Behind Appdome?

  • Seller: Appdome
  • Company Website:
  • Year Founded: 2012
  • HQ Location: Redwood City, California, United States
  • Twitter: @appdome
    2,107 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    184 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services, Banking
  • Company Size: 48% Large, 34% Medium

What Do G2 Reviewers Say About Appdome?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the excellent customer support from Appdome, highlighting their responsiveness and helpfulness throughout the process.
  • Users value the extensive security features of Appdome, enhancing mobile app protection effectively and efficiently.
  • Users value the ease of use with Appdome, praising its intuitive GUI for securing mobile applications effortlessly.
  • Users value the runtime application protection of Appdome, appreciating its ease and comprehensive security without coding.
  • Users appreciate the ease of implementation with Appdome, enabling fast and efficient integration without coding.
Cons
  • Users note that the licensing costs can be prohibitive, making it challenging for smaller companies to afford Appdome.
  • Users find the complexity of features in Appdome overwhelming, requiring time to understand proper integration and configuration.
  • Users find the initial learning curve challenging due to the extensive features, requiring time to understand configurations.
  • Users face a challenging learning difficulty due to the complexity of configurations and initial integration guidance required.
  • Users often struggle with poor documentation, leading to confusion during integration and configuration of Appdome.

What Are Recent G2 Reviews of Appdome?

PreEmptive

PreEmptive secures apps against IP theft, hacking, and tampering with multi-layered protection for .NET, Android, Java, and JavaScript. PreEmptive protects mobile, web and desktop applications to deliver secure, compliant applications across platforms and devices. PreEmptive expertly balances cost, convenience, & functionality to secure your applications, making them more resistant against AI assisted attacks, data & IP theft, hacking, & tampering. Our quick-to-implement, premium solutions provide multilayered in-app protection: Dotfuscator for .NET, C# & MAUI DashO for Java, Kotlin & Android JSDefender for JavaScript Our multi-layered approach to binary code protection employs obfuscation, encryption, root detection, shielding, & tamper-proofing to defend against exploitation by both humans and machines. PreEmptive offers passive & active defense capabilities, safeguarding trade secrets & intellectual property (IP), reducing piracy & counterfeiting, & preventing tampering of code & sensitive data inspection. Easily integrating into .NET, MAUI, Java, & Android applications, PreEmptive helps you manage application risks and ensure regulatory compliance. PreEmptive protection is easy to implement and use, so your team can secure source code from the very start of development. Meet regulatory standards while protecting sensitive data across finance, healthcare, government, and other high-risk industries. Choose PreEmptive for comprehensive, intelligent app security

Average Rating: 4.6/5.0

Total Reviews: 49

How Do G2 Users Rate PreEmptive?

  • Ease of Use: 8.9/10 (Category avg: 8.7/10)
  • Quality of Support: 9.3/10 (Category avg: 9.0/10)

Who Is the Company Behind PreEmptive?

  • Seller: Sembi
  • Company Website:
  • Year Founded: 2023
  • HQ Location: Austin, US
  • LinkedIn® Page: www.linkedin.com
    114 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 44% Small, 40% Medium

What Are Recent G2 Reviews of PreEmptive?

What Are G2 Users Discussing About PreEmptive?

Jscrambler

Jscrambler is the leader in Client-Side Security for the modern, composable web. As organizations increasingly build digital experiences through third-party software supply chains and AI-powered agents, sensitive data is now created directly in the browser — the point of creation for digital interactions — making it one of the enterprise’s most privileged yet least governed attack surfaces. Jscrambler’s Client-Side Security Platform is powered by a Behavioral Enforcement Core that governs how application code, third-party scripts, and sensitive data behave at runtime. By enforcing software integrity and data governance directly in the browser, the platform ensures sensitive data and AI inputs are controlled according to enterprise policy at the point of creation — before they leave the client environment. Trusted by leading global retailers, airlines, financial services providers, and healthcare organizations, Jscrambler provides the visibility and enforcement organizations need to stop client-side attacks, prevent data leakage, and maintain compliance with regulations including PCI DSS, GDPR, HIPAA, CCPA, and the EU AI Act.

Average Rating: 4.4/5.0

Total Reviews: 31

How Do G2 Users Rate Jscrambler?

  • Ease of Use: 8.7/10 (Category avg: 8.7/10)
  • Quality of Support: 8.8/10 (Category avg: 9.0/10)

Who Is the Company Behind Jscrambler?

  • Seller: Jscrambler
  • Company Website:
  • Year Founded: 2014
  • HQ Location: San Francisco, California
  • Twitter: @Jscrambler
    1,161 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    89 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 35% Medium, 29% Small

What Do G2 Reviewers Say About Jscrambler?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Jscrambler, highlighting its intuitive navigation and user-friendly interface.
  • Users find Jscrambler's automation capabilities beneficial for seamless integration and enhanced security within development workflows.
  • Users commend the rapid and helpful customer support of Jscrambler, enhancing their overall experience significantly.
  • Users value the robust security features of Jscrambler, effectively safeguarding their intellectual property during deployment.
  • Users value the comprehensive overview of Jscrambler, enhancing security and performance while enabling features gradually.
Cons
  • Users experience slow performance with Jscrambler, requiring tuning and noting insufficient documentation for improvement.
  • Users suggest that the dashboard can be improved to display more detailed information from each installation.
  • Users experience a difficult initiation due to a complex setup process requiring substantial understanding of application deployment.
  • Users face challenges with obfuscated pages not working and project file limits in large applications.
  • Users struggle with limited guidance and often face issues when exporting reports, hindering their experience.

What Are Recent G2 Reviews of Jscrambler?

What Are G2 Users Discussing About Jscrambler?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

DoveRunner

DoveRunner, formerly known as AppSealing, is a comprehensive mobile app and content security platform designed to help businesses protect both their mobile applications and premium video content against evolving digital threats. The platform combines advanced mobile app shielding technologies with enterprise-grade video content protection solutions, enabling organizations to secure their digital ecosystem through a unified security approach. DoveRunner offers robust Runtime Application Self-Protection (RASP) capabilities for mobile apps helping businesses safeguard their intellectual property without requiring extensive coding or complex integrations. One of the standout strengths of DoveRunner is its ability to protect applications from tampering, reverse engineering, repackaging, and unauthorized modifications while simultaneously securing premium video content from piracy and illegal distribution. Through advanced security protocols, the platform actively detects and neutralizes threats targeting mobile applications and streaming environments, ensuring the integrity of both the app experience and the content delivery pipeline. DoveRunner’s user-friendly implementation process allows businesses to integrate powerful security capabilities into their existing applications and content workflows with minimal operational complexity. Its no-code and low-code deployment capabilities enable organizations to secure mobile apps and video services quickly, without lengthy development cycles or heavy infrastructure requirements. This combination of ease of use, scalability, and enterprise-grade protection makes DoveRunner an ideal choice for businesses seeking to strengthen both their mobile app security and premium content protection strategies. In summary, DoveRunner provides a unified security platform that addresses the critical challenges faced by modern app-driven and content-centric businesses. By delivering advanced mobile app shielding alongside robust video content protection and anti-piracy solutions, DoveRunner helps organizations defend their applications, protect premium content, preserve revenue streams, and create a safer digital experience for users worldwide.

Average Rating: 4.7/5.0

Total Reviews: 48

How Do G2 Users Rate DoveRunner?

  • Ease of Use: 9.2/10 (Category avg: 8.7/10)
  • Quality of Support: 8.9/10 (Category avg: 9.0/10)

Who Is the Company Behind DoveRunner?

  • Seller: DoveRunner
  • Company Website:
  • Year Founded: 2000
  • HQ Location: San Jose, US
  • Twitter: @doverunner_inc
    12 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    63 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 46% Small, 42% Medium

What Do G2 Reviewers Say About DoveRunner?

AI-generated summary from verified user reviews

Pros
  • Users value the intuitive interface and real-time performance tracking of DoveRunner for efficient data management.
  • Users appreciate the intuitive interface of DoveRunner, finding it efficient for analyzing and managing data seamlessly.
  • Users love the clean, intuitive interface of DoveRunner, enhancing their efficiency in data management and analysis.
Cons
  • Users find that some advanced features have a steep learning curve and lack clear in-app guidance for newbies.

What Are Recent G2 Reviews of DoveRunner?

What Are G2 Users Discussing About DoveRunner?

LIAPP

LIAPP is a specialized mobile application shielding and runtime application self-protection (RASP) solution designed to secure Android and iOS environments from unauthorized access and cyber threats. This security tool allows developers and enterprises to protect their mobile applications by applying robust security layers to the final application binary, ensuring protection against tampering and reverse engineering without requiring changes to the existing source code. The primary function of LIAPP is to maintain the integrity of mobile applications in high-stakes industries, including mobile banking, fintech, and global gaming. By implementing LIAPP, organizations can defend against various attack vectors such as rooting, jailbreaking, debugging, and memory manipulation. This solution is particularly effective for businesses that need to align their mobile services with international security standards and regional financial regulations. In addition to its core shielding capabilities, LOCKIN Company offers supplementary security modules that can be implemented alongside or independently of LIAPP to address specific vulnerabilities: LISS (Screen Protection): A dedicated solution designed to block unauthorized screen captures, screen recording, and remote access attempts to protect visual data integrity. LIKEY (Security Keypad): A specialized virtual keypad that encrypts and secures sensitive user input to prevent data interception from keyloggers and other malicious methods. LIAPP’s deployment model is optimized for rapid integration into the development lifecycle, minimizing the technical burden on engineering teams. This allows organizations to maintain their scheduled release cycles while providing a secure environment for their end-users. The solution provides several key technical advantages: Comprehensive App Shielding: Prevents unauthorized modification and repackaging of the application to ensure the software functions as originally intended. Dynamic Runtime Protection: Actively detects and blocks security threats during the application's execution to prevent data breaches in real-time. Modular Security Expansion: Enables users to enhance their security posture by adding LISS for screen protection or LIKEY for secure data entry based on specific operational needs. Regulatory Compliance Support: Provides the necessary technical infrastructure to assist financial institutions in meeting stringent mobile transaction security and fraud prevention requirements. Through its specialized focus on application integrity, LIAPP assists users in managing the security lifecycle of their mobile products. It offers monitoring capabilities and threat intelligence, allowing stakeholders to identify emerging risks and maintain a resilient mobile presence.

Average Rating: 4.8/5.0

Total Reviews: 20

How Do G2 Users Rate LIAPP?

  • Ease of Use: 9.2/10 (Category avg: 8.7/10)
  • Quality of Support: 9.2/10 (Category avg: 9.0/10)

Who Is the Company Behind LIAPP?

Who Uses This Product?

  • Top Industries: Computer Games
  • Company Size: 60% Medium, 35% Small

What Are Recent G2 Reviews of LIAPP?

What Are G2 Users Discussing About LIAPP?

cside

What is cside? cside is a browser-layer security platform that gives organisations complete visibility and control over the third-party JavaScript running on their websites. It intercepts every script before it reaches the user, captures the full payload, and analyses runtime behaviour in real time. Third-party scripts power modern websites. Analytics, chat, payments, advertising, and session replay tools all inject JavaScript that runs directly in your visitors' browsers. You didn't write that code. You don't control when it changes. And you have no idea what it does at runtime. That is the client-side blind spot. The three problems cside solves 1) Every third-party script is a blind spot. Analytics, chat, payments, ads: you didn't write it, you don't control it, and you have no idea what it does at runtime inside a real browser. 2) PCI DSS 4.0.1 requirements 6.4.3 and 11.6.1 are now enforced. Most companies have no idea how to meet them, and their existing vendors don't cover it. WAFs, CDNs, and tag managers were never built for this problem. 3) AI agents and bots are now targeting high-value web workflows including checkout, login, and form submission in ways that WAFs and CDN-layer tools were never designed to catch. The attack surface has moved into the browser. The tools haven't. What you get with cside 1) Visibility you have never had. Every script on every page, classified, behavioural-profiled, and monitored continuously. Not what a scanner saw on its last crawl. What actually ran in a real user's browser, in real time. 2) Compliance, done. 6.4.3 and 11.6.1 documentation generated automatically. Auditor-ready output without manual effort. QSA-validated. No CSV exports to fill in by hand. 3) Real-time blocking. Malicious or anomalous script behaviour stopped at the browser layer before data leaves the page. Not flagged for review after the fact. Stopped before exfiltration occurs. Why CSPs and crawlers cannot solve this A Content Security Policy tells the browser which domains are allowed to load scripts. It has no visibility into what those scripts execute. A script served from a trusted domain, after being compromised through a supply chain attack, passes every CSP check and still skims card data from your checkout page. Crawlers and scanners have a different problem. Bad actors detect them and serve clean content to the scanner, then flip to malicious for real users. What the scanner saw and what your customers experienced are two different things. WAFs and CDNs operate at the network layer. They cannot see inside the browser. They check what loads, not what executes. cside sits in the delivery path of every script. It captures what scripts actually do in real user sessions. Deployment: One script tag. Under ten minutes. No managed crawl setup, no session tokens, no captcha bypasses required. Pricing: Free tier available to see your script exposure before buying. Business and Enterprise tiers for teams managing compliance, multi-domain environments, and advanced governance. Transparent pricing. No contract required to prove compliance to your QSA before you commit. Frequently asked questions 1) What makes cside different from a Content Security Policy?: A CSP controls which domains scripts can load from. It cannot analyse what those scripts execute at runtime. cside captures the full payload of every script and analyses its behaviour inside real user browsers, giving you the runtime visibility that CSP was never designed to provide. 2) What PCI DSS requirements does cside address?: cside is built specifically around requirements 6.4.3 and 11.6.1 of PCI DSS 4.0.1. It generates the authorised script inventory required by 6.4.3 and provides the ongoing change detection and monitoring required by 11.6.1, with QSA-validated audit-ready output. 3) How is cside different from a WAF or CDN security feature?: WAFs and CDNs operate at the network or server layer and have no visibility into what JavaScript executes inside a user's browser. cside operates at the browser layer. It is a dedicated product for client-side security, not a feature bolted onto an existing network tool. 4) Does cside detect AI agents and bots?: Yes. cside detects AI agents and bots targeting high-value web workflows including checkout, login, and form submission, covering a threat class that network-layer tools were not designed to address.

Average Rating: 4.8/5.0

Total Reviews: 12

How Do G2 Users Rate cside?

  • Ease of Use: 9.2/10 (Category avg: 8.7/10)
  • Quality of Support: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind cside?

  • Seller: cside
  • Year Founded: 2024
  • HQ Location: San Francisco, US
  • Twitter: @csideai
  • LinkedIn® Page: www.linkedin.com
    19 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 83% Small, 17% Medium

What Do G2 Reviewers Say About cside?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the intuitive monitoring of cside, allowing easy oversight of scripts and compliance status.
  • Users appreciate the control and visibility c/side provides over third-party scripts, enhancing security and efficiency.
  • Users praise the advanced threat detection of C/Side, providing unparalleled protection against overlooked cyber threats.
  • Users commend the accuracy of information provided by c/side, experiencing real value and effective detection capabilities.
  • Users value the alert notifications from cside, which help in proactively identifying and addressing issues efficiently.
Cons
  • Users find the difficult initiation challenging, though support assists in eventually mastering the powerful interface.
  • Users face navigation issues that require trial and error, highlighting a need for better guidance and intuitive design.
  • Users find the interface not intuitive, requiring time to adapt to script grouping and display logic.
  • Users find the interface not user-friendly, requiring time and effort to navigate and understand effectively.
  • Users note rough edges and occasional issues with Cside, but quick fixes help mitigate their impact.

What Are Recent G2 Reviews of cside?

Feroot Security

The Feroot AI Platform brings intelligent automation to ensure compliant and secure user experiences across web and mobile applications—eliminating manual processes, reducing human error, and replacing operational overhead with continuous, real-time protection. Instead of spending months manually auditing websites and mobile applications, organizations can achieve security and compliance in as little as 45 seconds. Feroot automates website security and compliance programs to help meet the requirements of PCI DSS 4.0.1, HIPAA (including Rules on the Use of Online Tracking Technologies), CCPA / CPRA, GDPR, CIPA, and more than 50 global laws and industry standards. At the core of the platform are Feroot AI Agents that continuously monitor, detect, and enforce compliance across client-side environments. They identify and stop hidden threats such as Magecart attacks, formjacking, unauthorized tracking, data leakage, and malicious third-party scripts before they can compromise sensitive data. Feroot is purpose-built to protect high-value web assets including payment pages, login forms, healthcare portals, and other sensitive workflows where customer and patient data is most at risk. The unified platform integrates critical web security and compliance capabilities into a single solution, including: • JavaScript behavior analysis • Web compliance scanning • Third-party script monitoring • Consent audit and policy enforcement • Data privacy posture management By combining security monitoring with automated compliance enforcement, Feroot provides complete visibility and control over client-side risk without adding complexity. From Fortune 500 enterprises to healthcare providers, retailers, SaaS platforms, universities, utilities, municipalities, travel companies, gaming platforms, and payment service providers, organizations of all sizes trust Feroot to safeguard sensitive customer data and maintain regulatory compliance in an increasingly complex digital landscape. Feroot AI solutions include: • PaymentGuard AI – Protects payment workflows and PCI-scoped environments • HealthData Shield AI – Secures patient data and healthcare portals • AlphaPrivacy AI – Ensures data privacy compliance and user consent enforcement • CodeGuard AI – Monitors and protects client-side code integrity and behavior Visit https://www.feroot.com for more information.

Average Rating: 4.9/5.0

Total Reviews: 30

How Do G2 Users Rate Feroot Security?

  • Ease of Use: 8.7/10 (Category avg: 8.7/10)
  • Quality of Support: 9.9/10 (Category avg: 9.0/10)

Who Is the Company Behind Feroot Security?

  • Seller: Feroot Security
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Toronto, Ontario, Canada
  • LinkedIn® Page: www.linkedin.com
    53 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 47% Large, 33% Medium

What Do G2 Reviewers Say About Feroot Security?

AI-generated summary from verified user reviews

Pros
  • Users commend Feroot's exceptional customer support, appreciating their quick and accurate responses to inquiries and concerns.
  • Users find Feroot Security to be an easy-to-use solution, facilitating seamless integration and smooth compliance processes.
  • Users commend Feroot Security for its robust support and scalable efficiency, enhancing web security and compliance effortlessly.
  • Users appreciate Feroot's exceptional support and seamless integration, enhancing web security and compliance with minimal effort.
  • Users praise the easy integrations with existing systems, making setup and compliance management a breeze.
Cons
  • Users find the poor interface design challenging, making navigation and setup less intuitive than expected.
  • Users experience a steep learning curve when navigating Feroot Security's complex features and configuration options.
  • Users find the non-intuitive structure of Feroot Security challenging, requiring a learning curve for effective usage.
  • Users find the complex setup process challenging, with a steep learning curve for configuration and navigation.
  • Users find the difficult setup of Feroot Security challenging, impacting initial configuration and policy management.

What Are Recent G2 Reviews of Feroot Security?

Codacy

Codacy is the code quality and security platform for AI-assisted engineering teams. AI is now embedded through the engineering workflow, which has made teams faster, but also adds risk to everything they ship. Codacy helps AI-assisted teams ship high-quality, secure code across the full software development lifecycle, starting in the agent and editor, through pull requests in Git, and into containers and runtime security. At each stage we check for quality issues, security vulnerabilities and AI coding risk introduced into the codebase, and help devs and agent fix them effortlessly. A team's standards become automated guardrails that apply across every IDE, AI coding agent, and Pull Request. More than 250,000 developers rely on Codacy to keep quality and security stable as AI changes how software gets built. Add your repo and get your free scan report in minutes: https://codacy.com

Average Rating: 4.6/5.0

Total Reviews: 31

How Do G2 Users Rate Codacy?

  • Ease of Use: 9.0/10 (Category avg: 8.7/10)
  • Quality of Support: 9.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Codacy?

  • Seller: Codacy
  • Year Founded: 2012
  • HQ Location: Lisbon, Lisboa
  • Twitter: @codacy
    5,002 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    61 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software
  • Company Size: 55% Small, 23% Large

What Do G2 Reviewers Say About Codacy?

AI-generated summary from verified user reviews

Pros
  • Users value the enhanced security features of Codacy, benefiting from integrated automation and insightful vulnerability management.
  • Users appreciate the integrated automation of Codacy, finding it easy to use and helpful for maintaining code quality.
  • Users find the out-of-the-box automation in Codacy to be user-friendly and effective for maintaining code quality.
  • Users value the high code quality provided by Codacy's integrated automation and effective static code analyses.
  • Users value the helpful customer support of Codacy, appreciating their immediate assistance during integration and security management.
Cons
  • Users find Codacy expensive at $19/month, which can be a barrier for smaller organizations.

What Are Recent G2 Reviews of Codacy?

Domdog

Domdog is the most flexible and no-nonsense solution for compliance with 6.4.3 and 11.6.1 requirements of PCI DSS 4.0.1. Every organization has different preferences and constraints regarding what new systems they can integrate into their payment pages. With this in mind, Domdog has been designed to support Remote Scanning, JavaScript Agent, and Content Security Policy. This ensures that no matter what an organization's preferences are, Domdog can help them meet the 6.4.3 and 11.6.1 requirements with the least amount of effort and friction. Domdog offers a range of plans that cover small businesses to large enterprises. While the Business plan focuses on cost-effectiveness and simplified compliance, the Enterprise plan focuses on maximum flexibility and managed onboarding.

Who Is the Company Behind Domdog?

  • Seller: Domdog
  • HQ Location: Delaware, US
  • LinkedIn® Page: linkedin.com
    6 employees on LinkedIn®

Eyeriss

Eyeriss is an API gateway built from the ground up around security. Eyeriss has built-in conditional role-based access control, multiple authentication methods for both clients and backend services, and provides a plethora of metrics for API usage out of the box. It features a split architecture that is built for resiliency, speed, and horizontal scalability. With the defense-in-depth model, security teams and developers alike can be sure their API endpoints are strongly protected from any misuse. Eyeriss is intended to be easy to use for security engineers and developers alike, all while maintaining the capability to handle large traffic and request volumes to ensure availability to backend API services. The powerful WAF features of Eyeriss protects onboarded endpoints from a variety of attacks, greatly lowering the potential for outages and breaches. The on-prem and SaaS Enterprise offering of Eyeriss is ready for any production environment with many build-in integrations for connecting to alerting services, SEIMs, and many more tools to enhance both security teams and developers.

Who Is the Company Behind Eyeriss?

Verimatrix XTD

Verimatrix XTD stands at the forefront of application security, offering unmatched protection for mobile, web desktop and embedded applications in critical industries while streamlining implementation to empower innovation. Verimatrix delivers an amazing cybersecurity experience with XTD; allowing customers to prevent, detect, respond and predict threats to their mobile applications and the devices that connect to their critical infrastructure. We have expanded our detection capabilities to the network, beyond application and device level detections. We can access risk per application to protect the connection to the company critical infra. Verimatrix XTD’s Application Protection Suite includes: - XTD Enterprise Suite - XTD Protect for Mobile (iOS and Android) - XTD Protect for Desktop and Embedded Applications (Windows, MacOS and Linux) - XTD Protect for Native Applications (C/C++) - XTD Key Shield (whitebox cryptography) - XTD Protect for Web Applications - XTD Managed Services

Who Is the Company Behind Verimatrix XTD?

  • Seller: Verimatrix
  • Year Founded: 1995
  • HQ Location: Meyreuil, FR
  • Twitter: @VerimatrixInc
    4,743 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    205 employees on LinkedIn®
Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024