Pelican AI
Who Is the Company Behind Pelican AI?
- Seller: Pelican AI
- HQ Location: N/A
-
LinkedIn® Page: www.linkedin.com
1 employees on LinkedIn®
Total Products under this Category: 304
Last updated: September 05, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
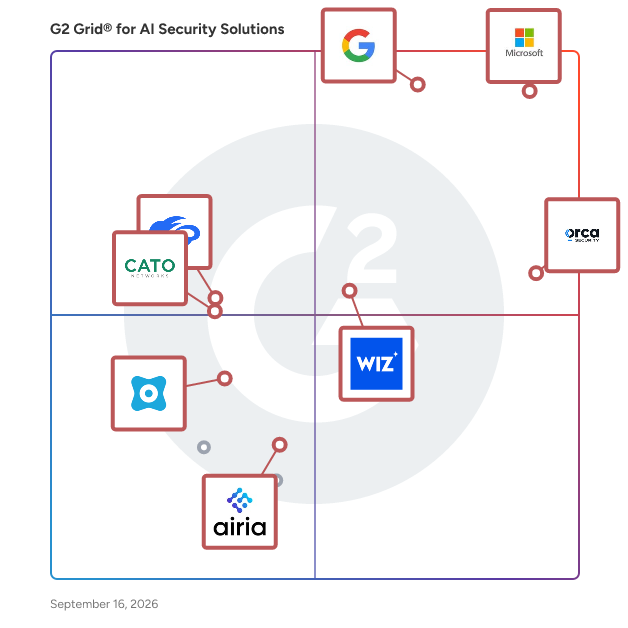
Highlighted products: Microsoft Defender for Cloud, Google Cloud Model Armor, Orca Security, Wiz, Zscaler Internet Access, Cato SASE Cloud, Securiti, and Airia.
Underlying data: [Grid® JSON](https://www.g2.com/categories/ai-security-solutions/grids.json?focus%5B%5D=microsoft-defender-for-cloud&focus%5B%5D=google-cloud-model-armor&focus%5B%5D=orca-security&focus%5B%5D=wiz-wiz&focus%5B%5D=zscaler-internet-access&focus%5B%5D=cato-networks-cato-sase-cloud&focus%5B%5D=securiti&focus%5B%5D=airia)
PlainID is the identity leader built for the AI era. We are the only enterprise Runtime Authorization Platform that controls what every identity - human, non-human, and AI agent - can access, do, and expose. Through centralized policy management and distributed enforcement, PlainID enables Fortune 500 enterprises to achieve zero standing privileges, complete auditability, and policy changes enforced in under 60 seconds.
Plurall AI is an advanced platform designed to detect and prevent deepfake content and fraudulent activities, empowering organizations to safeguard their brand integrity and maintain trust. By leveraging cutting-edge artificial intelligence, Plurall AI offers real-time analysis of images, videos, and audio to identify manipulated media with high accuracy. Key Features and Functionality: - Deepfake Detection: Utilizes AI to analyze media for signs of manipulation, ensuring high precision in identifying deepfake content. - Real-Time Analysis: Provides immediate feedback by detecting deepfakes in under 2 seconds, which is crucial for time-sensitive applications. - High Accuracy and Security: Achieves a 93% accuracy rate, offering reliable and secure detection capabilities. - Comprehensive Media Analysis: Capable of examining various media types, including still images and dynamic video content. - Industry-Specific Applications: Tailored solutions for sectors like social media, banking, and healthcare, where content authenticity is critical. - Layered Security Approach: Integrates multiple detection algorithms to identify sophisticated deepfake techniques. Primary Value and User Solutions: Plurall AI addresses the escalating threat of deepfake content and related fraud by providing organizations with tools to detect and prevent such activities effectively. By implementing Plurall AI, businesses can protect their brand reputation, ensure compliance with evolving regulations, and build trust with their audience. The platform's real-time detection and high accuracy enable swift responses to potential threats, minimizing financial losses and operational disruptions. Additionally, Plurall AI's adaptability to various industries ensures that organizations receive solutions tailored to their specific needs, enhancing overall security and trustworthiness.
PopdockAI is a no-code AI infrastructure platform built by eOne Solutions, an integration company with decades of experience serving 20,000+ businesses around the world. The platform is a unified MCP layer connecting AI assistants (Claude, ChatGPT, Copilot) to all your business systems. Connect to apps like NetSuite, Salesforce, and HubSpot via 100+ pre-built connectors. It offers enterprise-grade security, cross-system data joins, token-optimized filtering, and the ability for AI to take action, all without code. PopdockAI solves AI's "blindness" to business context, replacing months of custom integration work with secure, governed access deployable in hours This lets your team focus on querying data and automating workflows in minutes instead of hours of manual research.
Pretense is an AI security solution designed for enterprise engineering teams to safeguard proprietary code when utilizing AI tools. It functions as an AI firewall that mutates sensitive code identifiers before they reach any large language models (LLMs), ensuring that real identifiers never leave the organization's network. This approach allows developers to leverage AI capabilities without compromising intellectual property. Pretense deploys in 30 seconds and integrates seamlessly with existing AI tools, offering a local-first, open-source solution with no cloud dependency. Key Features and Functionality: - Code Mutation: Deterministically replaces every identifier—such as functions, variables, and classes—with synthetic tokens, allowing LLMs to process functional code without exposing actual identifiers. - Secrets Detection and Blocking: Identifies and blocks API keys, tokens, passwords, and personally identifiable information (PII) before they leave the local environment, covering over 30 major secret formats. - Enterprise-Grade Compliance: Provides a full audit trail of every mutation, ensuring readiness for SOC2, HIPAA, GDPR, and PCI-DSS compliance, with immutable logs for security teams and regulators. - Broad Compatibility: Works with all major AI tools and LLMs, including Claude, Copilot, Cursor, OpenAI, Anthropic, Gemini, and Ollama, as well as various integrated development environments (IDEs). - Rapid Deployment: Installs via a single command, with no dependencies, and operates offline, ensuring that no data leaves the system. Primary Value and Problem Solved: Pretense addresses the critical issue of proprietary code exposure when developers use AI coding tools. Traditional data loss prevention (DLP) solutions often fail to understand code, leaving organizations vulnerable to inadvertent leaks. By mutating code identifiers before they reach AI models, Pretense ensures that sensitive information remains within the organization's control, allowing teams to harness AI's benefits without risking intellectual property. This solution provides real-time insights and analytics, enabling organizations to monitor and control AI interactions with their codebase effectively.
The Prisma AIRS platform secures all apps, agents, models and data from development to deployment. AI Model Security-Enable the safe adoption of third-party AI models by scanning them for vulnerabilities and secure your AI ecosystem against risks such as model tampering, malicious scripts and deserialization attacks. AI Red Teaming-Uncover potential exposure and lurking risks before bad actors do. Perform automated penetration tests on your AI apps and models using our Red Teaming agent that stress tests your AI deployments, learning and adapting like a real attacker. AI Posture Management-Gain comprehensive visibility into your AI ecosystem to prevent excessive permissions, sensitive data exposure, platform misconfigurations, access misconfigurations and more. AI Runtime Security-Protect your LLM-powered AI apps, models and data against runtime threats such as prompt injection, malicious code, toxic content, sensitive data leaks, resource overload, hallucinations and more. AI Agent Security-Secure AI agents — including those built on no-code/low-code platforms — against new agentic threats such as identity impersonation, memory manipulation and tool misuse.
Proofpoint AI Security provides runtime inspection and enforcement for AI applications and agents. The product detects, alerts, and blocks threats across agent-to-tool and agent-to-LLM interactions and evaluates whether agent actions and behavior align with user intent throughout the full execution chain. Deployed at the infrastructure layer via eBPF, coverage is consistent across frameworks, LLM providers, and agent platforms without developer instrumentation.
Protecto is the Data Control Plane for Agentic AI. We help enterprises discover, classify, and protect sensitive and confidential data across AI agents, RAG pipelines, and MCP-enabled workflows. Key capabilities: - Discovery and classification of sensitive and context-based data across data stores and AI workflows, in hours rather than weeks - Context-preserving, format-preserving masking that keeps AI outputs coherent - CBAC (Context-Based Access Control) for context-based sensitive information that traditional DLP tools miss - GPTGuard MCP for policy-aware, protected RAG retrieval - Continuous monitoring for privacy and compliance risk - Simple APIs for integration with existing ETL and AI pipelines - Self-guided onboarding with clear documentation
Protegrity secures the data and knowledge layer AI runs on, binding protection directly to the data itself rather than locking access around it. Its platform tokenizes, encrypts, and masks sensitive data at the field and knowledge-graph level, enforcing policy in real time at the point of a prompt, query, or answer — across AWS, Azure, GCP, and OpenShift, with FIPS-validated, post-quantum-ready cryptography. A Control-Enforce-Verify-Execute framework covers autonomous discovery, natural-language policy, secure query and LLM guardrails, and cryptographic identity for agents and models, packaged for teams from single pipelines to full enterprise estates. Protegrity protects data for 8 of the 15 largest global banks, 2 of the 5 largest U.S. health insurers, 4 of the 10 largest North American retailers, and 3 of the world's largest government agencies. With over 330 employees and 150+ patents, Protegrity is positioned as the security layer beneath AI data platforms, models, and cybersecurity tools.
Average Rating: 4.5/5.0
Total Reviews: 14
Rating: 5.0/5.0 stars
— Péter G.
Rating: 5.0/5.0 stars
— Gaurav S.
Quint is the behavioral security platform for AI agents. As enterprises deploy autonomous coding agents like Claude Code, Cursor, GitHub Copilot, Windsurf, and Devin, security teams have zero visibility into what those agents actually do at runtime. The gap between what an agent claims and what the OS actually sees is where every AI agent breach lives. Existing AI security tools stop at the API gateway. Quint doesn't. A single action is never the signal. The sequence is. Quint intercepts every agent action at the OS level (Endpoint Security framework on macOS, eBPF on Linux), builds a behavioral baseline per agent, scores every action in real time against that baseline, and signs a tamper-proof Ed25519 audit trail for every tool call. One install, every agent, zero code changes. Works with any AI agent running on macOS or Linux. Maps to GDPR, HIPAA, SOC 2, PCI-DSS, EU AI Act, NIST AI RMF, and ISO 42001. Edge-first by design. Raw agent conversations, tool arguments, and file contents never leave the endpoint.
