Best Threat Intelligence Software - Page 12

How Many Threat Intelligence Software Products Does G2 Track?

Total Products under this Category: 222

Category Stats (Sep 2026)

  • Average Rating: 4.59/5 (↑0.01 vs Aug 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Darktrace / EMAIL (+1.92%) - Among all products in this category, Darktrace / EMAIL recorded the largest rating increase compared to last month

Last updated: September 29, 2026

How Does G2 Rank Threat Intelligence Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,700+ Authentic Reviews
  • 222+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

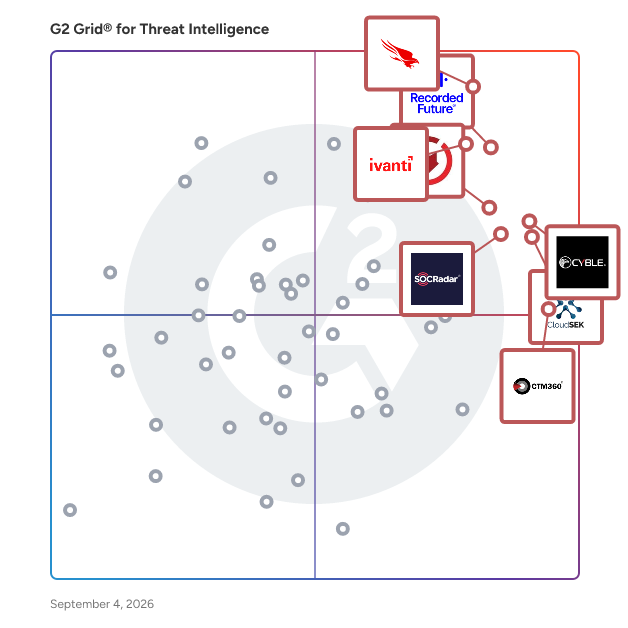
G2 Grid® for Threat Intelligence Software

G2 Grid® for Threat Intelligence Software plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Recorded Future, Ivanti Autonomous Endpoint Management, Cyble, CloudSEK, ZeroFox, SOCRadar Extended Threat Intelligence, and CTM360.

Underlying data: [Grid® JSON](https://www.g2.com/categories/threat-intelligence/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=recorded-future&focus%5B%5D=ivanti-autonomous-endpoint-management&focus%5B%5D=cyble&focus%5B%5D=cloudsek&focus%5B%5D=zerofox&focus%5B%5D=socradar-extended-threat-intelligence&focus%5B%5D=ctm360-ctm360)

Mandiant Threat Detection and Intelligence

Threat Intelligence Get visibility into the latest threats with cyber threat intelligence directly from the frontlines.

Who Is the Company Behind Mandiant Threat Detection and Intelligence?

  • Seller: Google
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • Twitter: @google
    31,899,995 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

Mondego Labs Rhine

Mondego Labs Rhine is a threat intelligence platform built for security teams who can't afford to find out about threats after they've already hit. Rhine surfaces malicious domains, phishing pages, and emerging attack infrastructure as they appear on the open internet. It deploys alongside your current stack with no rip-and-replace and no complex onboarding, going live in hours rather than weeks.

Who Is the Company Behind Mondego Labs Rhine?

Netstate

Netstate is business intelligence software that consolidates company records from government and regulatory sources into unified profiles. The platform covers 300 million entities across 195 countries and provides detailed U.S. business data. Each profile aggregates 16 federal datasets, including Secretary of State registrations, contractor awards, licensing information, loans, patents, trademarks, imports, and employee benefit plans. The system resolves entities across federal, state, and judicial datasets to deliver a complete paper trail in a single search. The software allows browsing by jurisdiction and filtering by 24 industry sectors. For vendor due diligence, the platform displays registration status, liens, and litigation history. Business verification tools compare applications against official records. Lending and underwriting functions access UCC positions, SBA loan history, and litigation records. Every field links directly to its source document.

Who Is the Company Behind Netstate?

OceanCentinell Enterprise

OceanCentinell Enterprise is a maritime cybersecurity and technology monitoring platform designed for organizations responsible for maritime operations, vessels, ports, communications, and related infrastructure. The platform centralizes security visibility through dashboards for asset monitoring, vulnerabilities, threats, incidents, audits, networks, satellite communications, AIS/VTS, and digital radio environments. OceanCentinell Enterprise helps security and operational teams organize cybersecurity information, identify potential risks, track incidents, review security posture, and support compliance workflows from a centralized interface. Its command-center approach provides organizations with a unified view of maritime technology and cybersecurity operations. The platform is designed for maritime organizations seeking improved cybersecurity visibility, risk management, incident tracking, and operational security oversight. Demonstration environments may use synthetic and simulat

Who Is the Company Behind OceanCentinell Enterprise?

Offshark

Offshark is a premier cyber security company dedicated to safeguarding your digital assets in an ever-evolving threat landscape. We provide cutting-edge defense mechanisms and proactive monitoring to ensure your business remains resilient against cyber attacks. With a focus on speed, precision, and reliability, Offshark is the ultimate shield for your digital world.

Who Is the Company Behind Offshark?

Oktoboot

Oktoboot® is a cloud-native Cyber Threat Intelligence (CTI) platform that empowers businesses and organizations to proactively detect, analyze, and respond to cyber threats. By delivering real-time threat insights and actionable intelligence, Oktoboot helps security teams stay ahead of evolving cyber risks and protect their digital assets.

Who Is the Company Behind Oktoboot?

OpenText Core Adversary Signals

OpenText™ Core Adversary Signals is a SaaS-based global signal analytics tool designed to enhance cybersecurity defenses by providing comprehensive visibility into malicious internet traffic. It identifies and analyzes adversarial behaviors, early warning signs, and sophisticated attack paths, enabling organizations to proactively monitor and respond to threats beyond their traditional security perimeters. Key Features and Functionality: - Adversary Signal Analytics: Utilizes advanced analytics to detect and filter malicious internet signals, effectively reducing noise and highlighting targeted attacks. - Threat-Actor Attribution: Tracks threat actors across multiple proxies, uncovering their true origins and motives, thereby providing deeper insights into potential threats. - Cross-Agency Models: Facilitates the validation of threat activities across various divisions within an organization, promoting a unified security approach. - SaaS-Based Deployment: Offers a plug-and-play solution that requires no additional hardware, ensuring quick implementation and seamless integration with existing systems. - Enriched Context: Provides actionable intelligence by leveraging adversary data to offer additional context about threat actors and their activities. - Open Integration: Easily integrates with any Security Information and Event Management (SIEM) or Extended Detection and Response (XDR) systems, enhancing visibility and enabling early threat detection. Primary Value and Problem Solved: OpenText Core Adversary Signals addresses the challenge of limited visibility into external threats by extending monitoring capabilities beyond organizational boundaries. By analyzing global internet traffic, it identifies malicious activities targeting the organization, allowing for early detection and proactive defense measures. This comprehensive approach minimizes disruptions, reduces potential damage, and enhances the overall security posture by providing actionable insights into adversarial behaviors and attack vectors.

Who Is the Company Behind OpenText Core Adversary Signals?

  • Seller: OpenText
  • Year Founded: 1991
  • HQ Location: Waterloo, ON
  • Twitter: @OpenText
    21,565 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    22,835 employees on LinkedIn®
  • Ownership: NASDAQ:OTEX

OSINT360

Who Is the Company Behind OSINT360?

Outseer Global Data Network

The Outseer Global Data Network™ is a collaborative consortium that aggregates and shares high-quality fraud and transaction data from hundreds of financial institutions across over 150 countries. This extensive network enables near real-time sharing of confirmed fraud events and emerging threat patterns, significantly enhancing fraud detection capabilities. By leveraging this collective intelligence, financial institutions can proactively identify and prevent fraudulent activities, safeguarding their customers and assets. Key Features and Functionality: - Comprehensive Data Aggregation: Collects and analyzes data from a vast network of global contributors, encompassing billions of transactions to identify fraud patterns effectively. - Real-Time Fraud Intelligence Sharing: Facilitates near real-time dissemination of fraud-related data among consortium members, ensuring timely updates on emerging threats and tactics. - Advanced Risk Assessment: Utilizes sophisticated analytics and predictive AI models to assess risk, enabling precise identification of fraudulent activities with a low false-positive rate. - Diverse Data Signals: Incorporates various data elements such as device identifiers, IP addresses, geolocation, and behavioral patterns to enhance fraud detection accuracy. Primary Value and Problem Solved: The Outseer Global Data Network addresses the escalating challenge of sophisticated and rapidly evolving fraud schemes by providing a unified platform for data sharing and analysis. By harnessing collective intelligence from a global consortium, it empowers financial institutions to detect and prevent fraud more effectively, reducing losses and enhancing customer trust. This collaborative approach ensures that organizations stay ahead of emerging threats, offering a robust defense against cybercriminal activities.

Who Is the Company Behind Outseer Global Data Network?

  • Seller: Outseer
  • HQ Location: Bedford, US
  • Twitter: @OutseerCo
    123 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    250 employees on LinkedIn®

Parano.ai

Parano.ai is a competitive intelligence platform that automatically tracks changes across your competitors’ websites, pricing pages, product updates, job listings, ads, and reviews. Get real-time alerts, historical change logs, and structured insights without manual research. Built for founders, product, sales, and marketing teams who want to spot moves early, react faster, and turn competitor activity into strategic advantage.

Who Is the Company Behind Parano.ai?

Pillar Security

The Security Stack for AI Teams. Pillar security provides comprehensive AI management and security platform for the entire AI lifecycle, including: 1. MONITORING & VISIBILITY Efficiently manage and audit your AI systems, logging usage, interactions and sessions with full transparency. 2. AI DETECTION & RESPONSE Protect your applications with fast, robust security measures to prevent attacks and maintain user and data integrity. 3. AI EXPOSURE MANAGEMENT Continuously test and improve your AI apps' security to mitigate risks and stay ahead of new threats.

Who Is the Company Behind Pillar Security?

Pure Signal™ Recon

Pure Signal™Recon is a web based Threat Intelligence query platform. It allows Security Analysts access to Team Cymru’s proprietary data called Pure Signal™, enabling them to create searches and filters to discover insights from over 40 datasets. These datasets include NetFlow, PDNS and x509 Certificates among others. Pure Signal™ Recon is designed for highly advanced users, and mostly used for the purpose of Cyber Reconnaissance, Cyber Threat Hunting, Cyber Incident Response, Victimology and Third Party Digital Risks. Pure Signal™ Recon is licensed per user as an annual subscription, with a range of options to suit the budget and requirements of customer needs.

Who Is the Company Behind Pure Signal™ Recon?

  • Seller: Team Cymru
  • Year Founded: 1998
  • HQ Location: Lake Mary, FL
  • Twitter: @teamcymru
    41,148 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    132 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 60% Small, 20% Large

What Do G2 Reviewers Say About Pure Signal™ Recon?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time monitoring capabilities of Pure Signal™ Recon, enhancing their situational awareness and communication analysis.
  • Users highlight the real-time monitoring capability of Pure Signal™ Recon, enhancing situational awareness in communications.
  • Users value the real-time monitoring of wireless signals, enhancing their situational awareness and communication analysis.
Cons
  • Users are concerned about the inadequate security of Pure Signal™ Recon, fearing potential data leaks and hacking risks.
  • Users face information overload from Pure Signal™ Recon, making it challenging to identify critical data efficiently.

Q-Feeds

QFeeds is a real-time threat intelligence platform that empowers organizations to proactively detect and block cyber threats before they impact operations. Designed for seamless integration with SIEMs, and NGFW such as Cisco, Fortinet and Sophos. Q-Feeds delivers curated, actionable data updated every 20 minutes. By reducing malicious traffic and minimizing network strain, Q-Feeds enhances security, boosts performance, and keeps you ahead of evolving threats. • Actionable Intelligence: Gain insights from over 2,500 trusted sources, including phishing, botnets, and dark web data. • Real-Time Updates: Threat data is refreshed every 20 minutes to ensure your defenses stay current. • Fast & Easy Integration: Be up and running in just 5 minutes with our pre-built configurations for major platforms.

Who Is the Company Behind Q-Feeds?

  • Seller: Q-Feeds
  • Year Founded: 2024
  • HQ Location: Hilversum, NL
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

RedCarbon

RedCarbon is a Swiss company specialised in AI-powered cybersecurity. Founded in 2020 by experienced cybersecurity professionals with over two decades of industry expertise, the company focuses on designing and deploying virtual AI Agents to support human teams in managing the increasing volume and complexity of cyber threats. RedCarbon addresses the inefficiencies and limitations of traditional cybersecurity operations by automating the most repetitive and time-intensive activities. Its AI Agents are engineered to act as virtual colleagues, providing round-the-clock support to human analysts, without replacing their strategic value. What It Does RedCarbon offers a modular suite of AI-driven cybersecurity agents capable of autonomously operating across all SOC tiers. These agents are designed to: Autonomous Threat Detection & Analysis Incident Response and Proactive Threat Hunting Seamless Integration with SIEM, EDR, XDR platforms Automated triage, prioritisation and risk scoring Retrospective attack investigation and forensic analysis Threat intelligence monitoring across deep, dark and open web sources All AI Agents operate through a unified dashboard, with full observability and auditability, allowing real-time insights and control. Why It Matters Unlike conventional tools that depend heavily on rule-based systems and manual oversight, RedCarbon’s AI Agents are capable of learning, adapting and responding autonomously, drastically improving the speed and consistency of security operations. With RedCarbon, cybersecurity teams benefit from: Scalability without proportional hiring Significant reduction in response times—from hours to seconds Reduction in alert fatigue and false positives Minimised analyst turnover and operational stress Improved cost efficiency and workload distribution This results in better service quality for Managed SOC providers and greater protection for enterprise environments. For Whom RedCarbon is ideally suited for: Security Operations Centres (SOC/MSOC) Telecommunication providers and MSSPs System integrators seeking AI augmentation for their cybersecurity stack Medium and large enterprises aiming to automate without expanding teams Organizations facing analyst fatigue, burnout, or hiring constraints For further information or to request a demo, please visit: https://www.redcarbon.ai/get-a-demo

Who Is the Company Behind RedCarbon?

Red Sky Alliance CTAC

Wapack Labs is a cyber intelligence operation designed to monitor and report on threats to IT, key personnel and investments in dozens of venues, and make that data available in both human and machine readable formats.

Who Is the Company Behind Red Sky Alliance CTAC?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 22, 2025