Strobes PTaaS
Who Is the Company Behind Strobes PTaaS?
- Seller: Strobes Security Inc
- Year Founded: 2019
- HQ Location: Plano, US
-
LinkedIn® Page: www.linkedin.com
104 employees on LinkedIn®
Total Products under this Category: 200
Last updated: November 01, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
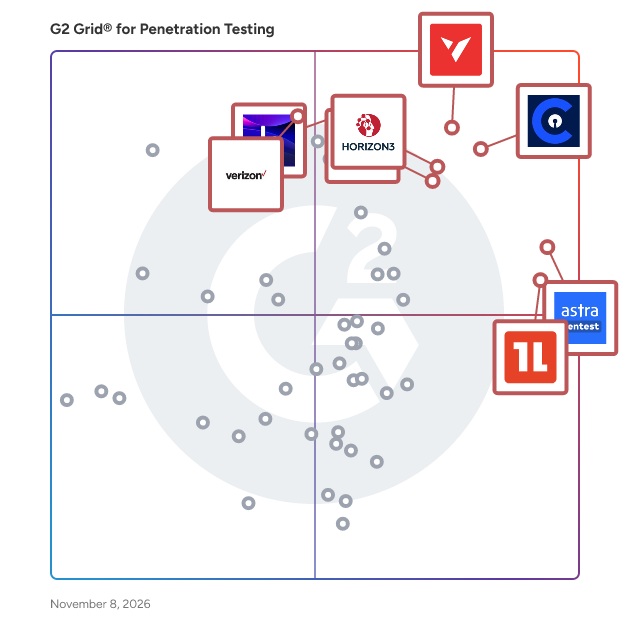
Highlighted products: Cobalt, vPenTest, Astra Pentest, NodeZero from Horizon3, Oneleet, Pentera, H1 Platform, and Verizon Penetration Testing.
Underlying data: [Grid® JSON](https://www.g2.com/categories/penetration-testing-tools/grids.json?focus%5B%5D=cobalt-io-cobalt&focus%5B%5D=vpentest&focus%5B%5D=astra-pentest&focus%5B%5D=nodezero-from-horizon3&focus%5B%5D=oneleet&focus%5B%5D=pentera&focus%5B%5D=h1-platform&focus%5B%5D=verizon-penetration-testing)
SuperPentest is an autonomous AI penetration testing platform for web apps and APIs. AI agents map your attack surface, chain vulnerabilities like a human attacker, and only report findings they can prove with a working exploit, so there are no false positives. First results in 48 hours, continuous retesting, and compliance-ready reports for ISO 27001, SOC 2, NIS2 and DORA. No finding, no fee.
Automated AI-powered penetration testing for real-time vulnerability detection and defense, exclusively available for MSPs, VARs, and Distributors.
Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.
Terra Security is a comprehensive cybersecurity solution designed to protect organizations from a wide range of digital threats. By integrating advanced threat detection, real-time monitoring, and proactive defense mechanisms, Terra Security ensures the safety and integrity of sensitive data and systems. Its user-friendly interface and scalable architecture make it suitable for businesses of all sizes, providing robust protection without compromising performance. Key Features and Functionality: - Advanced Threat Detection: Utilizes machine learning algorithms to identify and neutralize emerging threats before they can cause harm. - Real-Time Monitoring: Offers continuous surveillance of network activities, promptly alerting administrators to any suspicious behavior. - Proactive Defense Mechanisms: Implements automated responses to detected threats, minimizing potential damage and reducing response times. - User-Friendly Interface: Provides an intuitive dashboard that simplifies the management and monitoring of security protocols. - Scalable Architecture: Adapts to the needs of various organizations, from small businesses to large enterprises, ensuring optimal performance regardless of scale. Primary Value and Solutions Provided: Terra Security addresses the critical need for robust cybersecurity in an increasingly digital world. By offering advanced threat detection and real-time monitoring, it empowers organizations to proactively defend against cyberattacks, safeguarding sensitive information and maintaining operational continuity. Its scalable design and user-friendly interface ensure that businesses can implement effective security measures without requiring extensive technical expertise, thereby enhancing overall resilience against digital threats.
TrazTech Inc. provides security and compliance consulting software specializing in SOC 2 Type II certification, ISO 27001 compliance, penetration testing, and fractional CISO leadership. Its four-phase model prepares organizations for audits in under two weeks by streamlining discovery and reducing uncertainty. The platform features a portal for tracking findings, managing evidence, storing documents, monitoring milestones, and executing e-signatures. Penetration testing covers web applications, networks, cloud infrastructure, and server hardening through human-led assessments. AI security tools address prompt injection testing, leakage assessment, and adversarial testing aligned with OWASP LLM Top 10 standards. Fractional CISO services assist with security questionnaires, SOC 2 evidence collection, and board presentations. TrazTech also handles auditor relationships, HIPAA compliance, PCI DSS strategies, incident response, risk assessments, and centralized compliance workflows.
Trickest provides an innovative approach to offensive cybersecurity automation, assets, and vulnerability discovery. The platform combines extensive adversary tactics and techniques with full transparency, hypercustomization, and hyperscalability, making it the go-to platform for offensive security operations. The Trickest platform comes with comprehensive tooling, scripting, managed infrastructure, scaling, ready-to-go solutions, and analytics, serving as a collaborative command center for Offensive Security, Penetration testing, Red teams, Security Analysts, and Security Service providers (MSSPs). What makes us different? Easy customization of logic, inputs, outputs, and integrations, making them adaptable to specific needs and thus producing superior-quality data compared to others. Some of the automation workflows and solutions that our customers deploy and execute: - Attack Surface Discovery - Vulnerability Scanning - Dynamic Application Security Testing (DAST) - Recon/Information Gathering (Passive & Active) - Organization OSINT - CVE scanning - Cloud Scanning - DNS recon & research - Subdomain Enumeration - Subdomain Takeover - Custom Security Automation and Orchestration Main components of the Trickest platform include: Solutions & Analytics - Ready-to-go and transparent solutions for Attack Surface Discovery, Vulnerability Scanning, Dynamic Application Security Testing (DAST), and Open-source intelligence OSINT, offering insight into every step of the process, easy customization, and Analytics on the top. The Builder - Access to 90+ workflow templates, 300+ open-source tools, Bash & Python scripting, CLI for building custom workflows to discover asset, vulnerabilities, scan network & apps, crawl, spider, enumerate, fuzz, bruteforce and much more. Hyperscalability - Whether scanning regional infrastructures with 100s of 1000s of assets or smaller organizational scopes, Trickest supports it all without per-asset costs.
Vantico was born with the belief that security testing must adapt to today’s threat landscape. We are pioneers in the Pentest as a Service (PtaaS) market, combining a SaaS platform with highly skilled experts to change the old way of testing.
Vector is an autonomous pentester. Point it at your web app and our AI agents safely attack it the way a real hacker would, then hand back every weakness they found, proof that each one is exploitable, and the exact fix. It's simple to use, with no security background needed. You get an attacker's view of your app for a small fraction of the price and time. Most software shipped today has holes the people who built it never see. Vector finds them before someone else does.
VirtuProbe Studio is a powerful request manager built for developers, integration engineers, security professionals, and technical teams who need to test, automate, and orchestrate complex workflows across multiple protocols from one place. It lets you chain requests across HTTP, email, LDAP, Kerberos, SMB, and databases, then script the entire flow to reproduce real-world scenarios, validate integrations, troubleshoot systems, and automate multi-step technical processes. Instead of switching between disconnected tools, VirtuProbe Studio brings cross-protocol testing and workflow execution into a single environment, making it easier to build, inspect, repeat, and refine sophisticated request sequences from start to finish.
VORNAC is a platform for continuous security validation. An autonomous AI agent runs penetration tests against production environments using real attack techniques and delivers an audit-ready report with prioritised findings within hours. Tests are triggered via CI/CD webhook, API or on demand and can be repeated as often as needed instead of once a year, so a target system can be tested all year round for roughly the price of one classic pentest. The platform is developed and hosted in Germany with no dependency on US cloud providers. It is built for organisations subject to NIS2, DORA, KRITIS, TISAX, VAIT/BAIT and ISO 27001, such as insurers, financial services, operators of critical infrastructure and industrial companies. VORNAC GmbH is based in Heidelberg and a member of TeleTrusT, the German IT security association.
Vulncure PTaaS (Penetration Testing as a Service) is a cybersecurity platform that helps organizations continuously identify, prioritize, and remediate security vulnerabilities across web applications, APIs, cloud environments, and infrastructure.
Payatu follows a strict methodology when conducting an Application Security Assessment. This method ensures that a structured process is followed and provides the client with the baseline against which the quality of the assessment can be measured. Our methodology takes into consideration the industry-wide projects looking at the most commonly vulnerable areas of the application deployments, considering the OWASP top 10 and Web Application Security Consortium. 1)Extensive audit techniques sweep every corner of your system to discover potential attack surfaces 2)Dual security audit execution approach, i.e. automated and manual security is followed 3)With the invincible combination of industry standards checks and industry best researchers, no leaf is left unturned to find business-critical flaws in your web application. Our Methodology Our methodology takes into consideration the industry-wide projects looking at the most commonly vulnerable areas of the application deployments, considering the OWASP top 10 and Web Application Security Consortium.
Xalgorix is an Apache-2.0 open-source autonomous AI pentesting platform for authorized security testing. Unlike scanners that stop at plausible alerts, Xalgorix uses an AI agent to work through a structured 22-phase methodology and a separate verifier to independently reproduce each candidate finding before it is reported. Teams receive exploit-verified evidence, CVSS scoring, proof-of-concept details, remediation guidance, and branded PDF reports. The self-hosted Go and TypeScript project runs locally, keeps scan data in your infrastructure, and supports OpenAI, Anthropic, Gemini, DeepSeek, Groq, Ollama, MiniMax, and other OpenAI-compatible gateways. It includes a local web dashboard, CLI, Docker image, browser-assisted DAST, source-code review and provision-and-test modes, live telemetry, API and GraphQL testing, authentication and session analysis, injection, SSRF, IDOR/BOLA, file upload, deserialization/RCE, cloud, and WebSocket testing. The public repository is free and open source. The optional hosted Xalgorix service removes setup and adds managed scans, schedules, team workspaces, REST API access, CI gating, webhooks, and reports. A free GitHub App reviews pull-request diffs for security issues. Use Xalgorix only on systems you own or have explicit permission to test.
