Best Incident Response Software for Small Business - Page 2

How Many Incident Response Software Products Does G2 Track?

Total Products under this Category: 110

Category Stats (Nov 2026)

  • Average Rating: 4.48/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Eye Security (+8.08%) - Among all products in this category, Eye Security recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Incident Response Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,600+ Authentic Reviews
  • 110+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

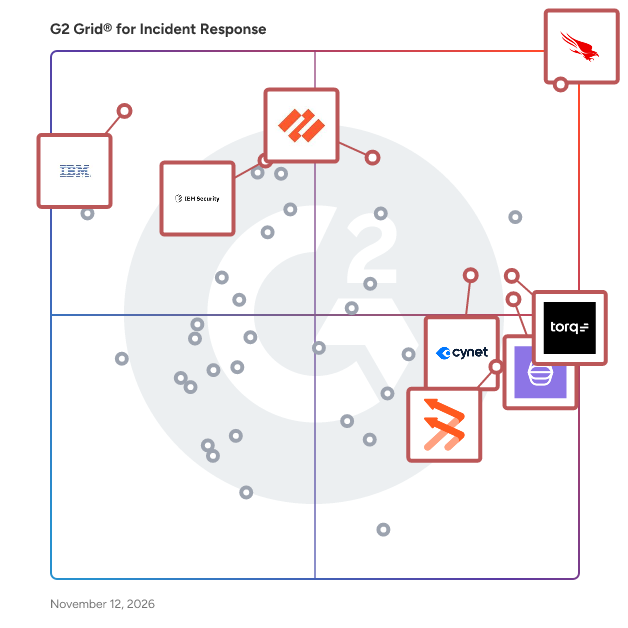
G2 Grid® for Incident Response Software

G2 Grid® for Incident Response Software plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Palo Alto Cortex XSIAM, Tines Stories, Torq AI SOC Platform, UnderDefense MAXI, IBM Concert platform, IBM QRadar SIEM, and Cynet.

Underlying data: [Grid® JSON](https://www.g2.com/categories/incident-response/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=tines-stories&focus%5B%5D=torq-ai-soc-platform&focus%5B%5D=underdefense-maxi&focus%5B%5D=ibm-concert-platform&focus%5B%5D=ibm-ibm-qradar-siem&focus%5B%5D=cynet&segment=small-business)

Blumira Automated Detection & Response

Blumira is an integrated security operations platform built for growing teams and the partners supporting them to gain complete visibility into their environment, identify and address risk faster, and deliver advanced security and compliance. The platform includes: - Managed Detections for automated threat hunting to identify attacks early - AI Investigation with 98.5% accurate, human-in-the-loop triage validated against real cases - Rapid Response with automation and 1-click actions to contain and block threats immediately - One Year of Data Retention with unlimited log ingestion to satisfy compliance requirements - Advanced Reporting and dashboards for forensics and easy investigation - Endpoint & Identity Protection (EDR/ITDR) for real-time remediation across devices and users - 24/7 Security Operations support for critical priority issues

Average Rating: 4.6/5.0

Total Reviews: 122

How Do G2 Users Rate Blumira Automated Detection & Response?

  • Threat Intelligence: 9.1/10 (Category avg: 8.9/10)
  • Quality of Support: 9.5/10 (Category avg: 8.8/10)
  • Incident Case Management: 7.9/10 (Category avg: 8.5/10)
  • Incident Logs: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Blumira Automated Detection & Response?

  • Seller: Blumira
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Ann Arbor, Michigan
  • LinkedIn® Page: www.linkedin.com
    55 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Medium, 36% Small

What Do G2 Reviewers Say About Blumira Automated Detection & Response?

AI-generated summary from verified user reviews

Pros
  • Users commend the ease of use of Blumira, facilitating quick detection and monitoring of security incidents.
  • Users value the outstanding customer support of Blumira, highlighting swift assistance and a seamless onboarding experience.
  • Users appreciate the easy implementation of Blumira Automated Detection & Response, enabling quick and efficient setup processes.
  • Users value the real-time alerting feature of Blumira, enhancing their security awareness and incident management.
  • Users value the real-time alerting of Blumira, as it effectively tracks security events in their MS 365 environment.
Cons
  • Users feel that the limited customization options hinder the product's potential and integration capabilities with other tools.
  • Users find the alert system's customization lacking, highlighting a need for improved log source comparisons and SIEM functionality.
  • Users find the pricing model expensive and inflexible, not meeting their budget or needs effectively.
  • Users find the faulty detection limitations frustrating, especially around custom rules and log visibility.
  • Users find the inefficient alert system lacking essential user details, complicating response strategies and false positive management.

What Are Recent G2 Reviews of Blumira Automated Detection & Response?

What Are G2 Users Discussing About Blumira Automated Detection & Response?

Rapid7 Next-Gen SIEM

Rapid7 InsightIDR is a SaaS SIEM for modern threat detection and response. InsightIDR enables security analysts to work more efficiently and effectively, by unifying diverse data sources, providing early and reliable out of the box detections, and delivering rich visual investigations and automation to expedite response. With a lightweight cloud deployment and intuitive UI and onboarding experience, InsightIDR customers recognize an accelerated return on their investment and start seeing valuable insights from Day 1. With InsightIDR, teams can advance their threat detection and response program without adding headcount.

Average Rating: 4.4/5.0

Total Reviews: 69

How Do G2 Users Rate Rapid7 Next-Gen SIEM?

  • Threat Intelligence: 9.2/10 (Category avg: 8.9/10)
  • Quality of Support: 8.9/10 (Category avg: 8.8/10)
  • Incident Case Management: 8.7/10 (Category avg: 8.5/10)
  • Incident Logs: 9.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Rapid7 Next-Gen SIEM?

  • Seller: Rapid7
  • Year Founded: 2000
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    8,746 employees on LinkedIn®
  • Ownership: NASDAQ:RPD
  • Total Revenue (USD mm): $411

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 67% Medium, 30% Large

What Do G2 Reviewers Say About Rapid7 Next-Gen SIEM?

AI-generated summary from verified user reviews

Pros
  • Users commend the ease of use of Rapid7 Next-Gen SIEM for its intuitive implementation and clear alerts.
  • Users appreciate the easy integrations with third-party tools, enhancing the overall usability of Rapid7 Next-Gen SIEM.
  • Users appreciate the pre-built integrations of Rapid7 Next-Gen SIEM, facilitating easy connections with various third-party tools.
  • Users value the seamless integration of UEBA and deception tools, enhancing threat detection and speeding up investigations.
  • Users appreciate the visibility provided by Rapid7 Next-Gen SIEM, enabling easy log searching and clear alerting.
Cons
  • Users find the limited features of Rapid7 Next-Gen SIEM restrictive, hindering efficient alert creation and setup.
  • Users face challenges with limited alerting capabilities, making it hard to create effective and timely alerts.
  • Users find the limited alert management functionality challenging, particularly in creating and setting up pattern-based alerts.
  • Users find the difficult customization of Rapid7 Next-Gen SIEM hinders their ability to set effective alerts.
  • Users find the difficult setup of Rapid7 Next-Gen SIEM frustrating, especially with creating alerts effectively.

What Are Recent G2 Reviews of Rapid7 Next-Gen SIEM?

What Are G2 Users Discussing About Rapid7 Next-Gen SIEM?

LogRhythm SIEM

Rapidly deploy LogRhythm SIEM, the leading self-hosted SIEM, to secure your organization with powerful detections, synchronized threat intelligence, automated workflows, and achieve faster, more accurate threat detection, investigation, and response (TDIR).

Average Rating: 4.2/5.0

Total Reviews: 137

How Do G2 Users Rate LogRhythm SIEM?

  • Threat Intelligence: 8.7/10 (Category avg: 8.9/10)
  • Quality of Support: 8.5/10 (Category avg: 8.8/10)
  • Incident Case Management: 8.7/10 (Category avg: 8.5/10)
  • Incident Logs: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind LogRhythm SIEM?

  • Seller: Exabeam
  • Year Founded: 2013
  • HQ Location: Broomfield, CO
  • LinkedIn® Page: www.linkedin.com
    785 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Information Security Analyst, Cyber Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 40% Medium, 40% Large

What Are Recent G2 Reviews of LogRhythm SIEM?

What Are G2 Users Discussing About LogRhythm SIEM?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Guardsix

Guardsix is the sovereign security platform for lean European teams, bringing log management and audit-ready compliance to regulated industries, critical national infrastructure operators, and the Managed Security Service Providers (MSSPs) that serve them throughout Europe and beyond. Headquartered in Copenhagen, Denmark, Guardsix delivers sovereign-by-design security for organisations that carry real operational responsibility. The company employs several hundred cyber security specialists and keeps every organisation it serves in full control of their data, deployment, and operations. Guardsix provides a unified Command Centre platform combining: • Security Information and Event Management (SIEM) • Network Detection and Response (NDR) • Security Orchestration, Automation and Response (SOAR) • Fleet for enabling multi-tenant management • Governance for Healthcare internal risk compliance monitoring The platform is built to support European data sovereignty, regulatory compliance and operational control, with predictable node-based pricing and deployment options spanning on-premises, air-gapped, hybrid and cloud environments. Guardsix solutions help organisations: • Simplify audit readiness for regulations such as NIS2, DORA, and GDPR. • Support lean security teams with efficient log management and simplified workflows. • Scale security operations without increased complexity or ingestion-led pricing surprises. • Keep security data under European jurisdiction and control — where it lives, who operates it, and under whose laws. • Deploy on their own terms, on-prem and in infrastructure they control, keeping migration a real option at every renewal. • See clearly across their whole environment, with SIEM, NDR, SOAR, Fleet, and Governance in one sovereign platform rather than a stack of point tools. Guardsix maintains SOC 2 Type II attestation and designs its solutions in accordance with European data protection requirements. With a strong partner-first model, Guardsix works closely with regional MSSPs and service providers, combining sovereign-by-design security technology with European integrity and deployment flexibility.

Average Rating: 4.3/5.0

Total Reviews: 105

How Do G2 Users Rate Guardsix?

  • Threat Intelligence: 8.4/10 (Category avg: 8.9/10)
  • Quality of Support: 9.0/10 (Category avg: 8.8/10)
  • Incident Case Management: 8.3/10 (Category avg: 8.5/10)
  • Incident Logs: 8.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Guardsix?

  • Seller: guardsix
  • Company Website:
  • Year Founded: 2001
  • HQ Location: Copenhagen, Capital Region
  • LinkedIn® Page: linkedin.com
    180 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 44% Medium, 31% Small

What Do G2 Reviewers Say About Guardsix?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Guardsix, highlighting its simple interface and efficient incident management capabilities.
  • Users value the seamless integration and context-centric log management of Logpoint, enhancing efficiency and insights significantly.
  • Users commend the excellent customer support of Logpoint, ensuring quick resolutions and satisfaction throughout their experience.
  • Users highly value the easy integrations of Guardsix, enhancing their overall cybersecurity ecosystem and efficiency.
  • Users commend the efficiency of Logpoint, citing its seamless integration and rapid log normalization as major advantages.
Cons
  • Users find poor interface design frustrating, as it hinders usability and lacks essential features compared to competitors.
  • Users find the UX improvement necessary, citing slow interface and poor log presentation as major issues.
  • Users find the interface complexity challenging at first, but anticipate improvements in future updates.
  • Users find the confusing interface of Guardsix challenging, affecting their overall experience and efficiency.
  • Users note a lack of technical information with Guardsix, making it difficult to properly design and size their systems.

What Are Recent G2 Reviews of Guardsix?

What Are G2 Users Discussing About Guardsix?

SIRP

SIRP is an AI-native Autonomous SOC platform designed to evolve traditional Security Orchestration, Automation, and Response (SOAR) into governed, decision-driven security operations. Unlike legacy SOAR tools that rely on static playbooks and workflow automation, SIRP enables intelligent AI agents to analyze alerts, compute risk, execute response actions, and continuously learn from outcomes within defined policy boundaries. The platform combines contextual reasoning, real-time intelligence, and adaptive learning to reduce manual triage, minimize alert fatigue, and accelerate incident response while maintaining governance, auditability, and control. SIRP supports enterprise SOC teams and MSSPs seeking to operate at machine speed without sacrificing human oversight for high-impact decisions.

Average Rating: 4.7/5.0

Total Reviews: 22

How Do G2 Users Rate SIRP?

  • Threat Intelligence: 9.8/10 (Category avg: 8.9/10)
  • Quality of Support: 9.8/10 (Category avg: 8.8/10)
  • Incident Case Management: 8.8/10 (Category avg: 8.5/10)
  • Incident Logs: 9.5/10 (Category avg: 8.8/10)

Who Is the Company Behind SIRP?

  • Seller: SIRP
  • Year Founded: 2017
  • HQ Location: Bethesda, Maryland
  • LinkedIn® Page: www.linkedin.com
    55 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 41% Small, 37% Medium

What Do G2 Reviewers Say About SIRP?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the comprehensive automation features of SIRP, enhancing their security orchestration and incident management efficiency.
  • Users value the excellent customer support from SIRP, enhancing their overall experience with the product.
  • Users praise SIRP for its ease of use, making security automation and incident management seamless and efficient.
  • Users value the easy integrations offered by SIRP, enhancing their security automation and orchestration experience.
  • Users praise SIRP for its ease of use and excellent support, along with comprehensive security features and integrations.

What Are Recent G2 Reviews of SIRP?

D3 Security

D3 stands at the forefront of AI-powered security, providing real-time, autonomous SOC solutions that help organizations stay ahead of cyber threats. By merging autonomous investigation and triage with AI-guided remediation, D3 is delivering AI-powered, human-led cyber security solutions. Morpheus is D3 Security’s fully autonomous SOC solution that triages, investigates, and responds to every alert, 24/7. Morpheus covers 100% of your alerts — no exceptions — so your team never has to choose between chasing false positives or risking a breach. It triages 95% of alerts in under two minutes, integrating seamlessly with any SIEM, XDR, or security stack. Unlike traditional SOAR platforms, Morpheus doesn’t need endless playbook tuning; it can build response workflows on the fly, specific to your security stack. The result? Zero alert fatigue, fewer missed threats, and a dramatic boost in SOC efficiency, powered by a data privacy-friendly and SecOps-focused AI model.

Average Rating: 4.2/5.0

Total Reviews: 64

How Do G2 Users Rate D3 Security?

  • Threat Intelligence: 9.0/10 (Category avg: 8.9/10)
  • Quality of Support: 9.0/10 (Category avg: 8.8/10)
  • Incident Case Management: 8.9/10 (Category avg: 8.5/10)

Who Is the Company Behind D3 Security?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 49% Large, 41% Medium

What Are Recent G2 Reviews of D3 Security?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated
Reviews & FAQs

Reviews Summary: The Best Incident Response Software for Small-Business Businesses

Thanks to 5136 Incident Response software reviews and associated data from users working for small-sized companies, at G2 we have some of the most definitive data on the best Incident Response software for the smaller space. We have identified 21 individual Incident Response products offering the features, pricing and support that Small-Business companies look for when comparing Incident Response software and solutions. These reviews are generated using the qualitative and quantitative feedback from G2 members working in small-sized companies and who have used these Incident Response software products.

When G2 reviewers submit their Incident Response software reviews, they often provide information on the type of company they work for and what market segment they belong to. We break these different market segments into three distinct groups:

  • Small Business Incident Response Software Reviews (< 50 employees)
  • smaller Incident Response Software Reviews (51-1,000 employees)
  • Enterprise Incident Response Software Reviews (1,001+ employees)

smaller businesses have their own unique requirements when it comes to Incident Response software compared to small or enterprise companies. That is why these individual small-sized company Incident Response software reviews are especially helpful when comparing product set up, ease of use and overall cost.

Below you will find FAQs and review snippets for Incident Response software products that work well in smaller environments. These reviews are written by real G2 users working for these Small-Business companies who have real-world experience with these Incident Response software products.

FAQs About Incident Response Software for Small-Business Businesses

Q. What are the best Incident Response software products for small-sized businesses, according to G2 reviewers?
  • CrowdStrike Falcon Endpoint Protection Platform - 4.7-stars, 30 reviews (11% from smaller reviewers)
  • Tines Stories - 4.6-stars, 45 reviews (28% from smaller reviewers)
  • Palo Alto Cortex XSIAM - 4.5-stars, 14 reviews (27% from smaller reviewers)
  • Torq AI SOC Platform - 4.9-stars, 28 reviews (29% from smaller reviewers)
  • UnderDefense MAXI - 5.0-stars, 15 reviews (45% from smaller reviewers)
Q. What are the least-liked Incident Response software products for professionals at small-sized companies, based on the overall G2 rating?
  • D3 Security - 4.2-stars, 15 reviews (24% from smaller reviewers)
  • SIRP - 4.5-stars, 10 reviews (45% from smaller reviewers)
  • LogRhythm SIEM - 4.2-stars, 17 reviews (18% from smaller reviewers)
  • Guardsix - 4.8-stars, 10 reviews (22% from smaller reviewers)
  • Rapid7 Next-Gen SIEM - 4.3-stars, 12 reviews (19% from smaller reviewers)
Q. What are the highest-rated Incident Response software tool features according to employees at Small-Business companies?
  • Encryption - 5.0-stars
  • Data Security - 5.0-stars
  • Data Visualization - 5.0-stars
Q. What are the features that are rated lowest by employees at Small-Business companies?
  • AI Text Summarization - 3.8-stars
  • AI Text Generation - 3.9-stars
  • System Isolation - 4.1-stars
Q. How many Incident Response software reviews are from users working in smaller companies?

516 out of all Incident Response software reviews on G2 are from users working in Small-Business companies (10%).

Here's What Reviewers Working at smaller Businesses Have to Say About Incident Response Software

What Small-Business Professionals Liked What Small-Business Professionals Disliked

LogRhythm SIEM: “LR SOAR is able to bring detection into action.”

Read Review

Datev: “Pretty much everything. The app to log in is super slow, Datev is complicated and old fashioned, the UX seems like from the 90s, there are no real integrations into other tools.”

Read Review

IBM QRadar SIEM: “Upgraded Technology and Support. SIEM, Digital Forensics, Cloud Security Monitoring and Analysis.”

Read Review

CYREBRO: “The platform still feels immature: some functionalities are limited or not well developed. The integrations with other tools are not as smooth as expected, and the customization of rules or reports is very basic. Sometimes, the analyses are superficial and require manual intervention to obtain real value.”

Read Review

CrowdStrike Falcon Endpoint Protection Platform: “Its strong real-time threat detection and response capabilities. It provides good visibility across endpoints, helps identify suspicious activity and makes it easier to investigate and respond to security incidents from centralized console.”

Read Review

Intezer: “Capping of the free tier. Some GUI issues”

Read Review

Recommendations To Others Problems Solved & Benefits

KnowBe4 PhishER/PhishER Plus: “Talking with a KnowBe4 rep definitely swayed us on the decision. They do a great job of demoing their products.”

Read Review

CrowdStrike Falcon Endpoint Protection Platform: “It helps us detect and respond to endpoint threats quickly by providing centralized visibility, which reduces the time we need to investigate and contain incidents.”

Read Review

Intezer: “Always do a PoC/PoV if one hasn't used it before.”

Read Review

Palo Alto Cortex XSIAM: “Cortex XSIAM is helping us address several challenges around security monitoring, alert fatigue, and incident response.<br><br>One of the biggest benefits for us is automated detection and investigation. XSIAM helps correlate related events and prioritize meaningful threats, reducing the volume of noise our security team needs to manually review. This allows us to focus more time on genuine incidents and threat hunting rather than repetitive alert investigation.”

Read Review

Microsoft Sentinel: “If you're a small team or a big organization, just go for it.”

Read Review

UnderDefense MAXI: “UnderDefense watches for suspicious activity around checkout and payment integrations across the client stores we run, including the ones hosted in completely different environments. Before, an odd pattern on one store could sit there until a client or a payment provider pointed it out. Now we hear about it first, with the relevant context already attached, so we can act on it the same day. It has also changed the conversation with our clients, since we can tell them their store is being watched around the clock and mean it.”

Read Review