Best Identity Threat Detection and Response (ITDR) Software for Small Business

How Many Identity Threat Detection and Response (ITDR) Software Products Does G2 Track?

Total Products under this Category: 73

Category Stats (Oct 2026)

  • Average Rating: 4.57/5 (↓0.01 vs Sep 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Reco (+2.52%) - Among all products in this category, Reco recorded the largest rating increase compared to last month

Last updated: October 08, 2026

How Does G2 Rank Identity Threat Detection and Response (ITDR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,900+ Authentic Reviews
  • 73+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

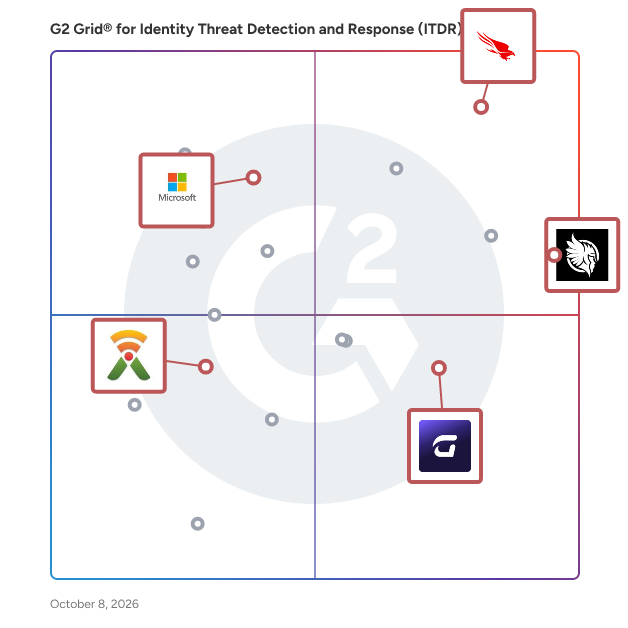
G2 Grid® for Identity Threat Detection and Response (ITDR) Software

G2 Grid® for Identity Threat Detection and Response (ITDR)  Software plotting products by satisfaction and market presence

Highlighted products: Huntress Managed ITDR, CrowdStrike Falcon Endpoint Protection Platform, Guardz, Microsoft Defender for Identity, and SaaS Alerts.

Underlying data: [Grid® JSON](https://www.g2.com/categories/identity-threat-detection-and-response-itdr/grids.json?focus%5B%5D=huntress-managed-itdr&focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=guardz&focus%5B%5D=microsoft-defender-for-identity&focus%5B%5D=saas-alerts&segment=small-business)

Huntress Managed ITDR

Huntress Managed ITDR is a fully managed identity threat detection and response (ITDR) solution that pairs continuous identity monitoring across Microsoft 365 and Google Workspace with a 24/7, human-staffed Security Operations Center (SOC). Built for managed service providers (MSPs) and small to mid-sized businesses (SMBs) with limited in-house identity security expertise, it detects identity-based threats such as credential compromise, privilege escalation, and lateral movement, and pairs automated behavioral analysis with expert analysts who investigate and respond to identity incidents in real time. Huntress Managed ITDR reduces dwell time on compromised accounts through rapid detection and remediation, giving lean IT and security teams enterprise-grade identity protection without the overhead of building an in-house identity security team. Our enterprise-grade solution gives you continuous monitoring for identity-based threats, rapid detection of unauthorized access, location-based and VPN/tunnel/proxy anomalies, and fast response to suspicious activities like rogue applications, shadow workflows, and business email compromise (BEC) scams. By focusing on protecting user credentials and session tokens, Huntress keeps your organization's digital identities safe, even as attackers develop sneakier tactics.

Average Rating: 4.8/5.0

Total Reviews: 117

How Do G2 Users Rate Huntress Managed ITDR?

  • Quality of Support: 9.7/10 (Category avg: 9.1/10)
  • Ease of Use: 9.5/10 (Category avg: 9.0/10)

Who Is the Company Behind Huntress Managed ITDR?

  • Seller: Huntress Labs
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Ellicott City, US
  • Twitter: @HuntressLabs
    40,338 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    978 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 76% Small, 20% Medium

What Do G2 Reviewers Say About Huntress Managed ITDR?

AI-generated summary from verified user reviews

Pros
  • Users value the continuous monitoring of Huntress Managed ITDR, enabling quick detection of threats without additional overhead.
  • Users value the easy integrations of Huntress Managed ITDR, enhancing efficiency and security across multiple platforms.
  • Users value the reliability of Huntress Managed ITDR, ensuring continuous protection and quick detection of threats.
  • Users value the clear visibility and actionable alerts Huntress Managed ITDR provides for identity-based threats.
  • Users praise the rapid and responsive customer support of Huntress Managed ITDR, enhancing overall satisfaction and efficiency.
Cons
  • Users report inadequate detection of failed login attempts, limiting proactive responses to security threats.
  • Users desire greater control and customization in the management console for enhanced functionality and flexibility.
  • Users find the pricing to be high since costs accumulate with each user, impacting overall affordability.
  • Users note occasional false positives triggered by VPN usage or incorrect location data, but overall security is prioritized.
  • Users report an inefficient alert system, lacking crucial details and failing to detect key security threats promptly.

What Are Recent G2 Reviews of Huntress Managed ITDR?

CrowdStrike Falcon Endpoint Protection Platform

Organizations today face a serious challenge: managing numerous security vendors and tools while confronting an ever-evolving threat landscape. Sophisticated adversaries are becoming smarter, faster, and more evasive, launching complex attacks that can strike in minutes or even seconds. Traditional security approaches struggle to keep pace, leaving businesses vulnerable. The CrowdStrike Falcon Platform addresses this by offering a unified, cloud-native solution. It consolidates previously siloed security solutions and incorporates third-party data into a single platform with one efficient and resource-conscious agent, leveraging advanced AI and real-time threat intelligence. This approach simplifies security operations, speeds analyst decision making, and enhances protection to stop the breach, allowing organizations to reduce risk with less complexity and lower costs. CrowdStrike's Falcon Platform includes: - Endpoint Security: Secure the endpoint, stop the breach - Identify Protection: Identity is the front line, defend it - Next-Gen SIEM: The future of SIEM, today - Data Protection: Real-time data protection from endpoint to cloud - Exposure Management: Understand risk to stop breaches - Charlotte AI: Powering the next evolution of the SOC

Average Rating: 4.7/5.0

Total Reviews: 547

How Do G2 Users Rate CrowdStrike Falcon Endpoint Protection Platform?

  • Quality of Support: 9.0/10 (Category avg: 9.1/10)
  • Ease of Use: 9.0/10 (Category avg: 9.0/10)

Who Is the Company Behind CrowdStrike Falcon Endpoint Protection Platform?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • Twitter: @CrowdStrike
    110,809 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Analyst, Security Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 46% Large, 40% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Endpoint Protection Platform?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the lightweight performance and powerful threat detection of CrowdStrike Falcon, enhancing security without slowing down systems.
  • Users commend the effective threat detection capabilities of CrowdStrike Falcon, ensuring robust security without system slowdowns.
  • Users appreciate the ease of use of CrowdStrike Falcon, benefiting from its lightweight impact and efficient incident management.
  • Users appreciate the advanced real-time threat protection of CrowdStrike Falcon, ensuring efficient security without system performance issues.
  • Users praise the exceptional threat detection of CrowdStrike Falcon, noting its effectiveness against both known and unknown threats.
Cons
  • Users find the cost prohibitive for smaller organizations, especially with additional modules increasing overall expenses.
  • Users find the complexity of the user interface and additional costs challenging, complicating their overall experience.
  • Users face a steep learning curve with CrowdStrike’s query language, making transitions from other platforms challenging.
  • Users find the limited features challenging, especially concerning cost and technical accessibility for smaller businesses.
  • Users find that pricing can be a barrier for smaller organizations, complicating access to advanced features.

What Are Recent G2 Reviews of CrowdStrike Falcon Endpoint Protection Platform?

What Are G2 Users Discussing About CrowdStrike Falcon Endpoint Protection Platform?

Guardz

Guardz is a unified cybersecurity platform specifically designed for Managed Service Providers (MSPs). This innovative solution consolidates essential security controls, identity threat detection and response (ITDR), endpoint protection (EDR), email security, user awareness training and phishing simulations, and Managed Detection and Response (MDR) into a single AI-native framework. The platform aims to enhance operational efficiency by streamlining security processes and providing a comprehensive approach to cybersecurity. Targeting MSPs, Guardz addresses the unique challenges these providers face in managing multiple security tools that often operate in silos. By adopting an identity-centric approach, Guardz connects various security vectors, effectively reducing the gaps that can leave organizations vulnerable. This layered and holistic view enables MSPs to respond to user risks in real time, ensuring that security measures are not only reactive but also proactive in safeguarding client environments. Key features of Guardz include its 24/7 AI and human-led Managed Detection and Response (MDR) services. The platform employs agentic AI to triage threats at machine speed, allowing for rapid identification and prioritization of potential security incidents. This automated triage process is complemented by expert analysts who validate findings, mitigate risks, and guide response actions. As a result, MSPs can offer scalable protection to their clients without the need to expand their workforce, making it a cost-effective solution for growing cybersecurity demands. Guardz stands out in the cybersecurity landscape by providing a unified platform that integrates various security functions into one cohesive system. This integration not only simplifies the management of security tools but also enhances the overall effectiveness of security measures. By leveraging AI-driven insights and human expertise, Guardz empowers MSPs to deliver robust cybersecurity solutions that adapt to the evolving threat landscape, ensuring their clients remain protected against emerging risks.

Average Rating: 4.6/5.0

Total Reviews: 125

How Do G2 Users Rate Guardz?

  • Quality of Support: 9.3/10 (Category avg: 9.1/10)
  • Ease of Use: 9.4/10 (Category avg: 9.0/10)

Who Is the Company Behind Guardz?

  • Seller: Guardz
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Tel Aviv, IL
  • Twitter: @GuardzCyber
    114 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    160 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO, Owner
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 77% Small, 18% Medium

What Do G2 Reviewers Say About Guardz?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Guardz, highlighting its organized dashboard and straightforward integration.
  • Users value the robust security of Guardz, ensuring comprehensive protection for their systems and emails effortlessly.
  • Users value the efficient multi-tenant features of Guardz, enhancing operational workflow and client management.
  • Users appreciate the easy setup of Guardz, quickly deploying it for customers in about an hour.
  • Users value the effective threat detection capabilities of Guardz, enhancing overall cybersecurity for their clients.
Cons
  • Users find the limited features of Guardz restrict their workflow and hinder automation capabilities, needing more flexibility.
  • Users face integration issues with Guardz, finding alerts cumbersome and lacking essential API support for smoother operations.
  • Users note a significant lack of features in Guardz, limiting its effectiveness in mixed environments and advanced configurations.
  • Users find limited customization options in Guardz, impacting its adaptability for advanced configurations in mixed environments.
  • Users desire more transparency and clarity regarding the tools and methods used by Guardz for safety.

What Are Recent G2 Reviews of Guardz?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Microsoft Defender for Identity

Microsoft Defender for Identity enables you to integrate Microsoft Defender for Identity with Defender for Endpoint, for an even more complete threat protection solution. While Defender for Identity monitors the traffic on your domain controllers, Defender for Endpoint monitors your endpoints, together providing a single interface from which you can protect your environment.

Average Rating: 4.3/5.0

Total Reviews: 93

How Do G2 Users Rate Microsoft Defender for Identity?

  • Quality of Support: 7.9/10 (Category avg: 9.1/10)
  • Ease of Use: 8.1/10 (Category avg: 9.0/10)

Who Is the Company Behind Microsoft Defender for Identity?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • Twitter: @microsoft
    13,091,739 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 39% Large, 32% Small

What Are Recent G2 Reviews of Microsoft Defender for Identity?

SaaS Alerts

​​SaaS Alerts is a automated cybersecurity platform to detect and automate the remediation of SaaS security threats. The platform provides unified, continuous monitoring of core business SaaS applications to protect against data theft and malicious actors, including Microsoft 365, Google Workspace, Salesforce, Slack, Dropbox, Okta, Duo and more. SaaS Alerts uses machine learning pattern detection to identify breaches, create instant alerts, and lock affected accounts, providing you with valuable time to respond before further damage can occur. It also enables you to terminate dangerous end-user file sharing activities and automate essential security tasks, enhancing efficiency and overall security.

Average Rating: 4.4/5.0

Total Reviews: 32

How Do G2 Users Rate SaaS Alerts?

  • Quality of Support: 9.1/10 (Category avg: 9.1/10)
  • Ease of Use: 8.1/10 (Category avg: 9.0/10)

Who Is the Company Behind SaaS Alerts?

  • Seller: Kaseya
  • Company Website:
  • Year Founded: 2000
  • HQ Location: Miami, FL
  • Twitter: @KaseyaCorp
    17,411 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    5,483 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 88% Small, 13% Medium

What Do G2 Reviewers Say About SaaS Alerts?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time alerts of SaaS Alerts, enhancing security awareness and user activity tracking across platforms.
  • Users appreciate the ease of use of SaaS Alerts, enjoying its intuitive interface and straightforward navigation.
  • Users appreciate the real-time alert notifications from SaaS Alerts, enhancing their confidence in monitoring user activity.
  • Users value the ease of setup and regular innovative features, along with a supportive community for sharing information.
  • Users value the effective reporting of SaaS Alerts, enabling them to identify security gaps efficiently.
Cons
  • Users find the ineffective alerts to be time-consuming, leading to unnecessary investigations into routine activities.
  • Users find the inefficient alert system complicates their workflow, requiring extra time to verify actionable issues.
  • Users experience false positives initially, but report that the system improves with time and learning filters.
  • Users find the inadequate filtering capabilities of SaaS Alerts lead to unnecessary time spent on non-actionable alerts.
  • Users find the inefficient filtering of alerts frustrating, wasting time on identifying real issues versus routine activity.

What Are Recent G2 Reviews of SaaS Alerts?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated