Best Extended Detection and Response (XDR) Platforms - Page 8

How Many Extended Detection and Response (XDR) Platforms Products Does G2 Track?

Total Products under this Category: 113

Category Stats (Nov 2026)

  • Average Rating: 4.55/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Eye Security (+8.95%) - Among all products in this category, Eye Security recorded the largest rating increase compared to last month

Last updated: November 02, 2026

How Does G2 Rank Extended Detection and Response (XDR) Platforms Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,900+ Authentic Reviews
  • 113+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

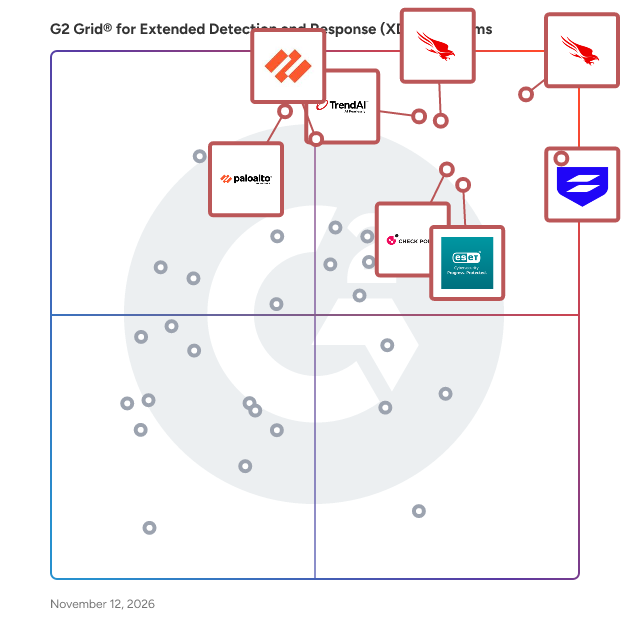
G2 Grid® for Extended Detection and Response (XDR) Platforms

G2 Grid® for Extended Detection and Response (XDR) Platforms plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Sophos Endpoint, CrowdStrike Falcon Cloud Security, TrendAI Vision One, Check Point Endpoint Security, ESET PROTECT, Palo Alto Cortex XSIAM, and Cortex XDR.

Underlying data: [Grid® JSON](https://www.g2.com/categories/extended-detection-and-response-xdr-platforms/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=sophos-endpoint&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=trendai-vision-one&focus%5B%5D=check-point-endpoint-security&focus%5B%5D=eset-protect&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=palo-alto-networks-cortex-xdr)

Spectrum AI-Powered Detection Platform

Detection can’t keep pace with rapidly emerging threats and changing enterprise environments. Spectrum is building the system that finally can.

Who Is the Company Behind Spectrum AI-Powered Detection Platform?

Tehtris XDR

Master the risks and finally tame the unknown with TEHTRIS XDR Platform and its sophisticated technologies for detection and response to security incidents.

Who Is the Company Behind Tehtris XDR?

  • Seller: Tehtris
  • Year Founded: 2010
  • HQ Location: PESSAC, FR
  • LinkedIn® Page: fr.linkedin.com
    181 employees on LinkedIn®

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

ThreatDefence AI SOC Platform

ThreatDefence is an AI SOC platform with a 24x7 managed SOC behind it. It brings your security tools, AI agents and analysts together on one platform, so your team can investigate alerts, coordinate response, hunt for threats and improve detections without replacing the technology you already own. Enterprises, MSPs and MSSPs use it to run security operations with less noise, more clarity and faster response. Cut through alert noise. AI agents investigate every incoming alert. Confirmed benign activity closes under your policies, while suspicious and uncertain findings reach analysts with evidence attached. Understand what happened. The platform connects activity across accounts, endpoints, email, cloud and networks. Agents build timelines, assess the scope and prepare clear verdicts with recommended actions. Contain real threats. Response is coordinated across connected systems. Actions run within your approved limits or wait for an authorized person, with progress tracked in the case. Improve your defenses. Investigation outcomes become proposed detections, targeted exclusions and refined skills. Analyst feedback reduces recurring noise and strengthens future investigations. Stay in control. Choose how far agents can act: recommend only, require approval, or execute authorized actions within defined limits. Every verdict links to its supporting queries and results, and live dashboards track investigation coverage, response times, MTTR, analyst agreement, overrides and incorrect closures. Expertise behind the technology. Our 24x7 SOC brings analysts, threat hunters and incident responders into the same cases as your team, from investigating an uncertain alert to containing a confirmed breach. Services include continuous investigation, proactive threat hunting, and incident response and DFIR. Expand your coverage. Add managed SIEM with detections maintained and tuned by our team, network detection and response, cloud security, attack surface management, identity threat detection, deception, cyber risk management and AI governance on the same platform. Built for MSPs and MSSPs. Run security operations across clients from one partner workspace. Separate tenants keep each client's data, procedures and autonomy settings under control, with optional white-label delivery of the portal, reports and notifications. Founded in 2014 by incident responders and threat hunters, ThreatDefence builds the AI SOC platform and operates the 24x7 SOC behind it. Start with a free trial: managed SIEM and our 24x7 SOC in your own environment, with full service access for four weeks at no cost.

Who Is the Company Behind ThreatDefence AI SOC Platform?

TotalHeal ThreatFusion

TotalHeal ThreatFusion is the Extended Detection & Response (XDR) product of TotalHeal, the security platform made in India by Freaquer Corporation Private Limited. One incident across endpoint, network, identity, email and cloud. It is managed from the TotalHeal console together with the other TotalHeal products, under one account and one bill. TotalHeal is available as a cloud service and for on-premises deployment. Every organisation can start a 30-day free trial from the console.

Who Is the Company Behind TotalHeal ThreatFusion?

Tuskira

Tuskira is a full-stack agentic SecOps platform built to close breach paths before attackers can use them. It connects the security tools you already run and unifies identity, cloud, endpoint, network, exposure, control, and threat-intelligence context into a live Security Context Graph and Digital Twin. That shared context allows Tuskira’s AI agents to model how exposures, identities, workloads, and controls connect, determine which findings and alerts create real production risk, validate whether existing defenses can stop the path, and coordinate the action that closes it. Four specialized agents operate on the same context: - Kairo maps how exposures, identities, workloads, and controls chain into breach paths. - Lattice reduces large volumes of findings to the subset that is exploitable, reachable, and undefended. - Quell determines whether a new zero-day creates a reachable path and recommends the compensating control that can reduce risk while a durable fix is developed. - Iris investigates and validates alerts, determines blast radius, and orchestrates response with an evidence-backed verdict and reasoning chain. Tuskira works across the customer’s existing stack without requiring another centralized log repository. Response is executed through existing security controls under customer-defined approval policies, with human approval where required. Every verdict, approval, and action is auditable. In one global financial-services deployment, Tuskira reduced 12.3 million findings to 0.46% requiring action and cut exposure triage from three weeks to 30 minutes. Security teams use Tuskira for agentic-based continuous threat exposure management (CTEM), vulnerability prioritization, breach-path validation and disruption, alert investigation, and zero-day response, using the tools they already own.

Who Is the Company Behind Tuskira?

XDRShield

XDRShield is an extended detection and response platform built to help organizations improve visibility across endpoints, correlate suspicious activity, and move more efficiently from detection to investigation and response. Designed for modern IT and security teams, XDRShield combines endpoint monitoring, asset and vulnerability context, response workflows, compliance-oriented review, and multi-tenant operational control in one platform. It is especially well-suited for MSPs, MSSPs, and distributed organizations that need stronger workflow ownership, auditability, and operational visibility across customer or business-unit environments.

Who Is the Company Behind XDRShield?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024