Best Dynamic Application Security Testing (DAST) Software - Page 6

How Many Dynamic Application Security Testing (DAST) Software Products Does G2 Track?

Total Products under this Category: 102

Category Stats (Oct 2026)

  • Average Rating: 4.58/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: HCL AppScan (+0.24%) - Among all products in this category, HCL AppScan recorded the largest rating increase compared to last month

Last updated: October 24, 2026

How Does G2 Rank Dynamic Application Security Testing (DAST) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 4,300+ Authentic Reviews
  • 102+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

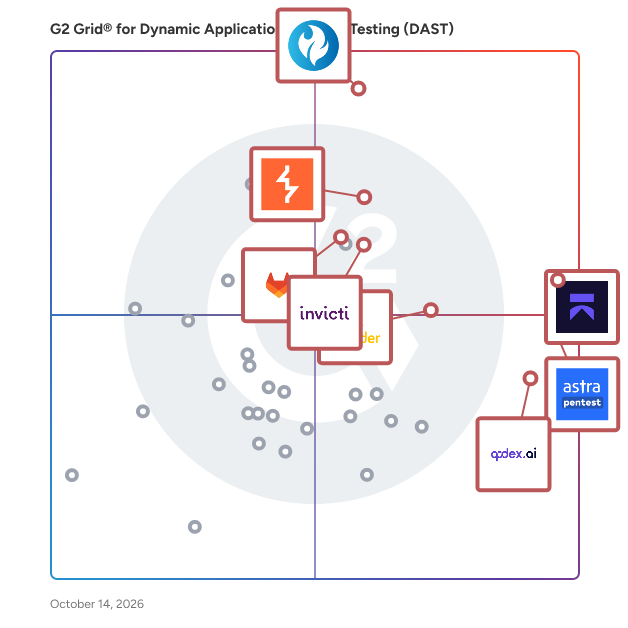
G2 Grid® for Dynamic Application Security Testing (DAST) Software

G2 Grid® for Dynamic Application Security Testing (DAST) Software plotting products by satisfaction and market presence

Highlighted products: HCL AppScan, Aikido Security, Astra Pentest, Burp Suite, Qodex.ai, Intruder, Invicti, and GitLab.

Underlying data: [Grid® JSON](https://www.g2.com/categories/dynamic-application-security-testing-dast/grids.json?focus%5B%5D=hcl-appscan&focus%5B%5D=aikido-security&focus%5B%5D=astra-pentest&focus%5B%5D=burp-suite&focus%5B%5D=qodex-ai&focus%5B%5D=intruder&focus%5B%5D=invicti&focus%5B%5D=gitlab)

Enso Security

Enso Application Security Posture is a platform for AppSec teams to manage their day-to-day work, implement their security strategy into an AppSec organizational program, enforce it and automate it. And all of that in a scalable rapidly changing environment. AppSec teams struggle with prioritization - they may have a vision and concept of how to handle AppSec, but they don’t know where to invest and what actions to take. To keep up with R&D velocity and scale, Enso provides full visibility on the application inventory, focuses the AppSec teams on the most important tasks and insights, and takes a policy-based “call to action” approach so that the AppSec professionals won’t waste their time looking for application changes, prioritizing, or doing manual work.

Who Is the Company Behind Enso Security?

MeshaSec

Product Overview: The Autonomous Evolution of DAST MeshaSec is an autonomous DAST (Dynamic Application Security Testing) tool that scans web applications, APIs, and SPAs behind MFA, SSO, and TOTP authentication — without manual configuration. Built for DevSecOps teams and security engineers who need authenticated coverage with zero false positives. In 2026, security is no longer about just "finding bugs"—it’s about established Protocol Truth. MeshaSec orchestrates the identity handshake natively, treating your complex React/Vue/Angular applications as dynamic state machines rather than static pages. The result? 99.9% noise reduction, 100% authenticated coverage, and deterministic evidence fragments that your developers can act on instantly. Core Value Proposition: Why MeshaSec? 1. Identity-Aware Orchestration (Bypassing the Moat) Legacy scanners bounce off the entrance. MeshaSec natively orchestrates complex identity sessions, including: Enterprise SSO: Microsoft Entra ID (Azure AD), Okta, PingFederate, and Google Workspace. Adaptive MFA: Native TOTP/MFA fulfillment during scan execution. Session Continuity: Protocol-level heartbeats that detect 401/403 errors and silently re-authenticate to maintain continuous discovery. 2. Autonomous Discovery Nodes (Thinking Like an Attacker) Our discovery engine doesn't just crawl links; it understands application states. SPA Mastery: Native navigation of JS-rich environments (React, Vue, etc.). Shadow API Discovery: Uncovering private, undocumented endpoints hidden within client-side state transitions. Deep Business Logic Paths: Mapping every potential user journey to ensure no attack vector is left unverified. 3. Deterministic Protocol Truth (Ending the Triage War) Security teams are drowning in "Possible XSS" alerts. MeshaSec delivers Deterministic Verification: Raw Evidence Fragments: Every finding includes the raw HTTP Request and Response that triggered the flaw. 99.9% Deduplication: We correlate thousands of vectors into a single, irrefutable source of truth. Zero-Guessing Triage: If MeshaSec reports it, it exists. No probability scores—just proof. Technical Specifications & Standards Alignment MeshaSec is engineered to align with global security frameworks, making it the preferred choice for compliance-driven enterprises: OWASP Top 10 Mapping: Every vulnerability is automatically categorized under current OWASP standards. MITRE ATT&CK Integration: Specifically mapped to initial access and credential access techniques. Federal & Global Compliance: Native reporting for NIST 800-53, WASC v2.0, and SOC2 Readiness. Intelligence Isolation: AES-256 encryption-at-rest with total environment separation between scans. Use Cases: Industry Focus FinTech & Banking Secure portals protected by strict MFA and rotating session tokens. MeshaSec fulfills the identity handshake and audits deep behind the boundary without manual intervention. Enterprise SaaS Continuously map and secure multi-tenant dashboards and complex API surfaces that change daily. Our autonomous nodes scale with your deployment frequency About MeshaSec Headquartered in the global technology hub of Bengaluru, India. MeshaSec is committed to engineering the future of autonomous, identity-aware AppSec. We believe that security should be as agile as your code, and as deterministic as your logic. MeshaSec: Precision DAST for the Global Elite

Who Is the Company Behind MeshaSec?

  • Seller: MeshaSec
  • HQ Location: Bengaluru, Karnataka, India
  • LinkedIn® Page: linkedin.com
    1 employees on LinkedIn®

Mobix

Mobix is a SaaS mobile application testing platform that reduces application analysis costs and time, making tests creation and finding vulnerabilities effortless. Mobix's unique characteristics include: - Non-invasive tool, which augments existing SDLC (Software Development Life Cycle) - Automates 90% of the entire test coverage for dynamic and static analysis - No code, plug and play analysis - Automated recording of tests - Machine Learning to automatically adapt auto-tests - Scalable multithread testing, custom scan rules - Compliance to all major mobile security standards

Who Is the Company Behind Mobix?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Nullify

The post-human product security program. Nullify continuously allocates AI capacity toward the highest-impact product security work, maximizing outcomes from every engineer hour and every token spent.

Who Is the Company Behind Nullify?

  • Seller: Nullify
  • Company Website:
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    27 employees on LinkedIn®

Outpost24 Application Security

Dynamic Application Security Testing for DevOps Frequent changes to applications, whether built by in-house DevOps teams or outsourced from commercial suppliers, means risk evaluation must shift towards continuous testing. Our Dynamic Application Security Testing (DAST) solution, provides critical assessments during the SDLC rapidly and efficiently with quick-and-easy configuration assessments. With an accessible REST API, Selenium integration, and automated reporting, Scale is designed to deliver the high-quality vulnerability findings needed to enable each iteration of the SDLC to confidently address issues before they are released to the next phase. 

Who Is the Company Behind Outpost24 Application Security?

Oversecured

Enterprise vulnerability scanner for Android and iOS apps. It offers app owners and developers the ability to secure each new version of a mobile app by integrating Oversecured into the development process.

Who Is the Company Behind Oversecured?

OWASP ZAP

Who Is the Company Behind OWASP ZAP?

  • Seller: OWASP
  • Year Founded: 2001
  • HQ Location: Wakefield, US
  • Twitter: @DependencyTrack
    1,436 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    686 employees on LinkedIn®

Panoptic Scans - Network and Application Vulnerability Scans

Panoptic Scans is a hosted vulnerability scanning platform designed to bolster cybersecurity for businesses by offering automated, comprehensive network and application vulnerability scans. Our platform empowers users to schedule vulnerability scans - daily, weekly, monthly, or annually - to ensure compliance with stringent regulations like SOC 2, HIPAA, ISO 27001, NIST 800-53, CMMC, and GDPR. Leveraging powerful tools such as OpenVAS for network vulnerabilities, OWASP ZAP for application security, and Nmap for port scanning, Panoptic Scans identifies weaknesses like unpatched software, misconfigurations, and open ports that could be exploited by cyber threats. With features like email notifications, detailed scan reports, and a user-friendly API, it simplifies vulnerability management, making it ideal for SaaS companies, security teams, and agile development environments aiming to safeguard sensitive data and maintain robust compliance effortlessly.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Panoptic Scans - Network and Application Vulnerability Scans?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • API / Integrations: 10.0/10 (Category avg: 8.7/10)
  • Detection Rate: 8.3/10 (Category avg: 8.8/10)
  • Test Automation: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Panoptic Scans - Network and Application Vulnerability Scans?

Who Uses This Product?

  • Company Size: 100% Medium

What Do G2 Reviewers Say About Panoptic Scans - Network and Application Vulnerability Scans?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the easy automation of scans with Panoptic Scans, enabling efficient SOC2 Vulnerability scanning and reporting.
  • Users value the automation capabilities of Panoptic Scans, simplifying SOC2 vulnerability scans and enhancing dashboard creation.
  • Users appreciate the easy automation of scans with Panoptic Scans, simplifying SOC2 Vulnerability management and reporting.
  • Users value the dashboard usability of Panoptic Scans, enhancing the ease of managing vulnerability assessments effectively.
  • Users appreciate the ease of use of Panoptic Scans, enabling effortless automation and actionable insights for security assessments.

What Are Recent G2 Reviews of Panoptic Scans - Network and Application Vulnerability Scans?

Proscan

Proscan is a unified application security platform designed to help organizations streamline the management of their security tools. By integrating multiple standalone solutions into a single cohesive experience, Proscan provides comprehensive security visibility across the entire software stack. This platform replaces the complexity of managing various tools for static analysis, dynamic testing, and dependency scanning, allowing teams to focus on building secure applications without the hassle of juggling disparate systems. The platform is particularly beneficial for security teams, developers, and engineering leaders who require a consolidated view of application security risks. Proscan combines nine specialized security scanners, including Static Application Security Testing (SAST), which analyzes source code in over 30 programming languages using advanced detection methods. Dynamic Application Security Testing (DAST) further enhances security by testing live applications, identifying vulnerabilities that may only become apparent during runtime. Additionally, Software Composition Analysis (SCA) evaluates open-source dependencies across 196 package ecosystems, helping organizations detect known vulnerabilities before they can impact production environments. Proscan's capabilities extend beyond code analysis. It includes scanning for hardcoded secrets, misconfigurations in Infrastructure-as-Code, and vulnerabilities in container images. The platform also offers API security testing that validates endpoints against the OWASP API Security Top 10, ensuring robust protection for applications that leverage APIs. For organizations developing AI-powered applications, Proscan features a dedicated AI and LLM security scanner that identifies potential risks associated with prompt injections and other vulnerabilities, utilizing over 4,600 techniques mapped to the OWASP LLM Top 10. Artificial intelligence plays a crucial role in enhancing Proscan's efficiency and accuracy. The platform employs machine-learning algorithms to reduce false positives and prioritize vulnerabilities based on their potential impact. This intelligent approach allows teams to focus on the most critical security issues while providing clear explanations and actionable remediation guidance. Proscan integrates seamlessly into existing development workflows, offering IDE plugins and native CI/CD integrations that ensure security checks are part of the development process without causing disruptions. Compliance readiness is another key feature of Proscan, as it generates audit-ready reports aligned with major security standards, including OWASP Top 10, PCI DSS, HIPAA, and GDPR. This automated evidence collection simplifies the compliance process, providing organizations with the necessary documentation in various formats. Proscan is designed for security teams looking to consolidate fragmented toolchains, developers needing quick feedback, and managed security service providers managing multiple client environments, making it a versatile solution for modern application security challenges.

Who Is the Company Behind Proscan?

ProtoCrawler

ProtoCrawler is an intelligent fuzz testing solution, used to identify security weaknesses and implementation bugs.

Who Is the Company Behind ProtoCrawler?

  • Seller: Cytal
  • Year Founded: 2020
  • HQ Location: Peterborough, GB
  • Twitter: @CyTAL_UK
    36 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    13 employees on LinkedIn®

PT Application Inspector

PT Application Inspector™ (PT AI™) is a comprehensive source code analysis tool that offers protection for web applications of any scale. Its holistic approach combines the advantages of static, dynamic, and interactive analysis to maintain application security throughout every stage of development—from the very first line of code to the go-live.

Average Rating: 5.0/5.0

Total Reviews: 2

How Do G2 Users Rate PT Application Inspector?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind PT Application Inspector?

Who Uses This Product?

  • Company Size: 67% Large, 33% Small

What Are Recent G2 Reviews of PT Application Inspector?

What Are G2 Users Discussing About PT Application Inspector?

Quokka Q-mast

Designed for app development, Q-mast embeds security directly into your workflow to identify security, privacy, and compliance risks before the mobile app is released. With a design tailored for DevSecOps workflows, Q-mast supports continuous, automated security testing that aligns with tools like Jenkins, GitLab, and GitHub. Q-mast capabilities: • Automated scanning in minutes, no source code needed • Analysis of compiled app binary, regardless of in-app or run-time obfuscations • Precise SBOM generation and analysis for vulnerability reporting to specific library version, including embedded libraries • Comprehensive static (SAST), dynamic (DAST), interactive (IAST), and forced-path execution app analysis • Malicious behavior profiling, including app collusion • Checks against privacy & security standards: NIAP, NIST, MASVS

Who Is the Company Behind Quokka Q-mast?

Red Cloud

With prooV Red Cloud, you can assess how technologies will react in the case of a cyberattack before you implement them It is a tailored, cloud-based environment that gives you the flexibility to carry out complex cybersecurity attacks on any type of software you are testing. You can use Red Cloud with the PoC Platform to include red team testing in your initial software testing and evaluation process, or you can use it on its own.

Who Is the Company Behind Red Cloud?

  • Seller: prooV
  • HQ Location: Herzaliya Pituach, IL
  • Twitter: @prooV_inc
    839 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    9 employees on LinkedIn®

SECURITY by HTTPCS

Detect security flaws in your website or web application and avoid being hacked. HTTPCS Security puts Machine Learning at the service of your cyber security to protect your site against hacking and data leaks.

Who Is the Company Behind SECURITY by HTTPCS?

  • Seller: HTTPCS by Ziwit
  • Year Founded: 2011
  • HQ Location: Montpellier, FR
  • Twitter: @httpcs
    2,812 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    27 employees on LinkedIn®
Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024