Best Digital Forensics Software - Page 6

How Many Digital Forensics Software Products Does G2 Track?

Total Products under this Category: 82

Category Stats (Sep 2026)

  • Average Rating: 4.44/5 (↑0.01 vs Aug 2026) The average rating of products in this category, based on all submitted ratings

Last updated: September 26, 2026

How Does G2 Rank Digital Forensics Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,500+ Authentic Reviews
  • 82+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

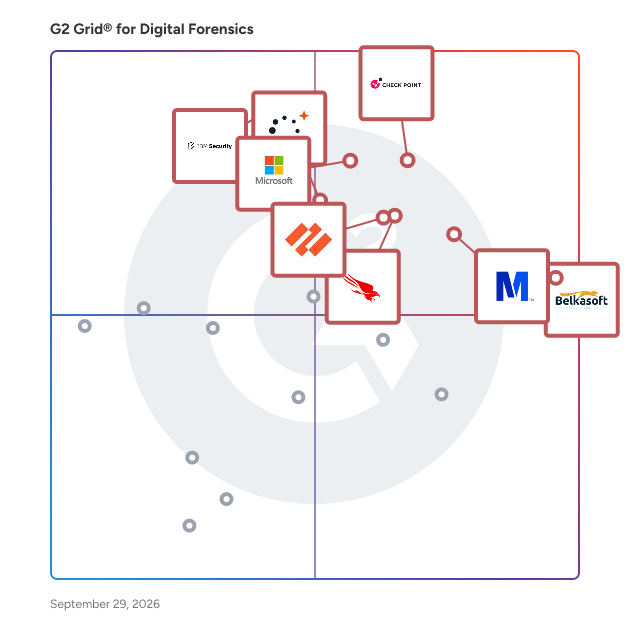
G2 Grid® for Digital Forensics Software

G2 Grid® for Digital Forensics Software plotting products by satisfaction and market presence

Highlighted products: Belkasoft, Check Point Endpoint Security, Magnet Forensics, Microsoft Purview Audit, IBM QRadar SIEM, Falcon Security and IT operations, Palo Alto Cortex XSIAM, and Cellebrite.

Underlying data: [Grid® JSON](https://www.g2.com/categories/digital-forensics/grids.json?focus%5B%5D=belkasoft&focus%5B%5D=check-point-endpoint-security&focus%5B%5D=magnet-forensics-magnet-forensics&focus%5B%5D=microsoft-purview-audit&focus%5B%5D=ibm-ibm-qradar-siem&focus%5B%5D=falcon-security-and-it-operations&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=cellebrite)

Sherlockeye

Sherlockeye is an identity intelligence platform powered by reverse lookup technology. Search across multiple data types including email, phone number, username, domain, and IP address, and get enriched profiles instantly. Available as a web application or via API for fraud prevention and investigations.

Who Is the Company Behind Sherlockeye?

Spellbreaker

Spellbreaker is a deepfake detection platform that identifies AI-generated, manipulated, and synthetic media across video, audio, and images. It's built for organizations where a wrong call on media authenticity carries real consequences — courts and legal teams, insurance claims and SIU units, financial institutions, and enterprise security and trust & safety teams. Unlike single-model detectors that degrade on real-world content, Spellbreaker uses an ensemble of multimodal AI models combined with neuro-symbolic reasoning, cross-referencing signals between modalities to catch inconsistencies in compressed, degraded, or low-quality files — the conditions where deepfakes actually circulate. Every analysis goes beyond a binary real/fake verdict. Spellbreaker generates explainable forensic reports that pinpoint where manipulation occurs and document how each conclusion was reached, giving investigators, claims adjusters, and analysts defensible findings they can present in court, regulatory reviews, or internal investigations. Security and privacy are built into the architecture: files are analyzed statelessly in memory and purged immediately after processing, with no retention. Your systems remain the authoritative record. Key capabilities: Multimodal detection across video, audio, and image files Cross-modal analysis that surfaces multi-layered manipulations single-modality tools miss Explainable forensic reports with traceable reasoning, suitable for legal and investigative use Robust performance on compressed and degraded real-world media Continuously updated detection ensemble to keep pace with new generative techniques Stateless, zero-retention processing for sensitive workflows Flexible deployment: cloud API, analyst web portal, or on-premise/air-gapped for data residency requirements Common use cases: digital evidence verification, insurance claims fraud investigation, threat intelligence and disinformation analysis, executive impersonation investigations, and enterprise incident response.

Who Is the Company Behind Spellbreaker?

Telegram Tracker

StealthMole's Telegram Tracker is a specialized tool designed to detect and investigate cybercriminal activities within Telegram's rapidly expanding ecosystem. By analyzing data from chat logs, groups, and channels, it enables investigators to uncover actionable intelligence on various illicit activities, including illegal trades, financial fraud, and the distribution of stolen credentials.

Who Is the Company Behind Telegram Tracker?

  • Seller: StealthMole
  • HQ Location: Singapore, SG
  • Twitter: @stealthmole_int
    124,833 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    17 employees on LinkedIn®

The 4n6 Analyst Limited

The 4n6 Analyst is Jamaica’s trusted Digital Forensics and Incident Response (DFIR) leader with global expertise spanning Jamaica, Canada, and the United States. We empower organizations to prevent, detect, and respond to cyber threats. Corporate investigations involving Financial Fraud, Embezzlement, Intellectual Property Theft, Business Email Compromise (BEC), Viruses, Intrusions, Hoaxes, Worms, or other malicious code, Insider Threats, Malware, Ransomware Attacks, and Data Breaches.

Who Is the Company Behind The 4n6 Analyst Limited?

TIBCO LogLogic

LogLogic Log Management Intelligence helps unlock value from all this data whether it's generated physically, virtually, on-site, or in the cloud. You can store all your log data in a centralized and secure place, leverage it to attain actionable information, deliver it to a TIBCO or third-party application for analysis, and archive it for future search or forensic investigations.

Who Is the Company Behind TIBCO LogLogic?

Truxton

Truxton is an advanced digital forensics platform designed to automate the analysis of digital media, unify artifact discovery and correlation, and deliver actionable intelligence to investigators across various operational environments. By streamlining forensic processes, Truxton acts as a force multiplier, saving time, manpower, and resources while enhancing collaboration and coordination among investigative teams. Key Features and Functionality: - Intuitive Interface: Truxton offers an easy-to-use, analyst-driven interface that requires minimal training, enabling quick adoption without the need for specialized coding skills. - Investigation Dashboard: Provides a comprehensive overview of each investigation, including case details, assigned investigators, and associated media, along with tools for management, review, and export. - Collaborative Forensics: Supports multiple users working on the same case simultaneously, facilitating workload management and preventing duplication of efforts. - Media Manager: Utilizes a single database repository, allowing loaded media to be used across multiple investigations without the need for repeated ingestion. - Automated Artifact Discovery: Automatically identifies and summarizes key entities such as phone numbers, credit card numbers, passwords, and USB identifiers, reducing noise and focusing on relevant information. - Visualization Tools: Offers powerful visualization capabilities, including timelines and conversation views, to contextualize entities and aid in efficient analysis. - Advanced Querying: Features customizable query filters that allow searches based on various parameters, with the ability to save and reuse queries in future investigations. - Automated Alerts: Enables investigators to set up criteria-based alerts for specific artifacts, ensuring immediate notification when relevant data is identified. - Management Metrics: Provides continuously updated snapshots of lab activities, helping managers monitor data processing, open cases, and resource allocation. Primary Value and Problem Solved: Truxton addresses the challenges of handling large volumes of diverse digital data in forensic investigations. By automating data exploitation, artifact discovery, and reporting, it significantly reduces the time and effort required to process and analyze digital evidence. Its collaborative features enhance teamwork and information sharing, while its scalability ensures adaptability to various operational environments, from field applications to large-scale forensic labs. Ultimately, Truxton empowers investigators to transform raw data into actionable insights more efficiently and effectively.

Who Is the Company Behind Truxton?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024