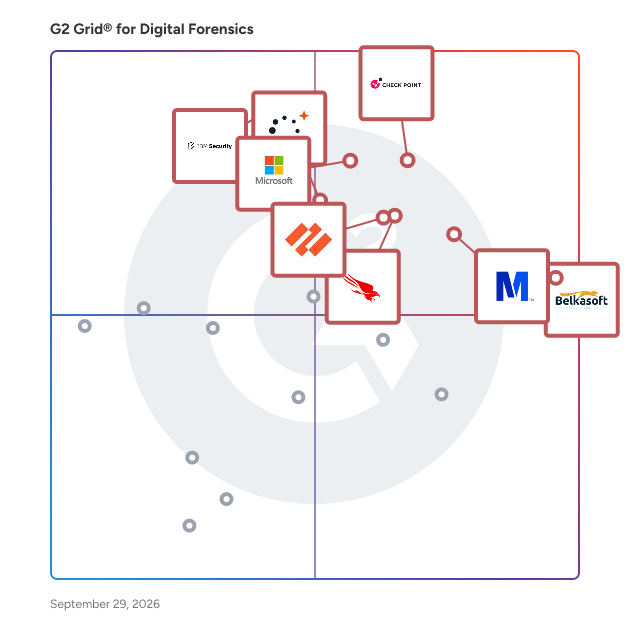
Digital forensics software is used to investigate and examine IT systems after security incidents or for security-related preventive maintenance. These tools help businesses perform in-depth analysis of IT systems to identify the cause of security incidents, outline vulnerabilities, and assist security teams in facilitating incident response processes. These tools aggregate security information from hardware, network logs, and files to present security professionals with a full picture of the likely causes of security incidents. From there, many tools identify the steps necessary to remediate the vulnerability and update policies and configurations to prevent the situation from arising again.
Companies use these tools after security incidents to identify the cause and root out any flaws or bugs that would allow a repeat scenario. They also use these tools to investigate systems, networks, and software to identify risks and remediate them before an incident occurs. Many of the tools in this category align with incident response software; however, those tools do not have the same in-depth investigative functionality and typically focus more on immediate remediation than granular investigation and preventive maintenance.
To qualify for inclusion in the Digital Forensics category, a product must:
- Perform file, internet, email, memory, and hardware security analysis
- Index aggregated security information for analysis
- Outline and/or automate security investigation workflows
- Produce investigative reports outlining security vulnerabilities