ProntoGDPR
Who Is the Company Behind ProntoGDPR?
- Seller: Luna
- Year Founded: 2025
- HQ Location: London, GB
-
LinkedIn® Page: www.linkedin.com
1 employees on LinkedIn®
Total Products under this Category: 244
Last updated: October 26, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
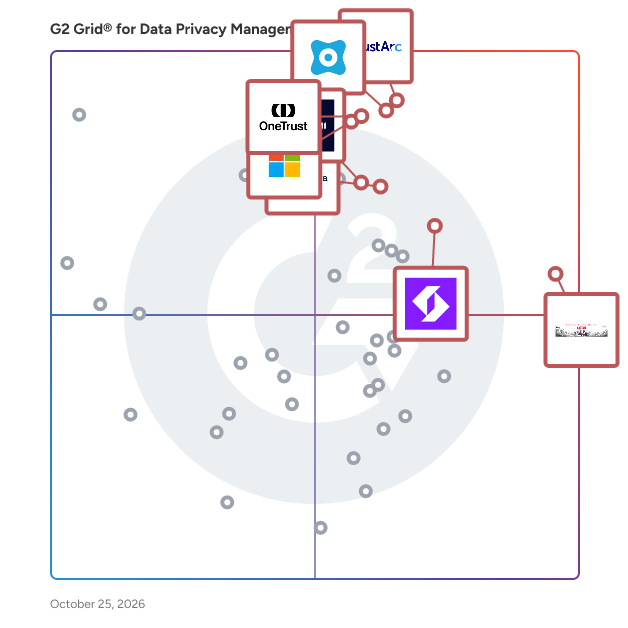
Highlighted products: TrustArc, Captain Compliance, Securiti, OneTrust Privacy Automation, Microsoft Priva, Ketch, Collibra, and Didomi.
Underlying data: [Grid® JSON](https://www.g2.com/categories/data-privacy-management/grids.json?focus%5B%5D=trustarc&focus%5B%5D=captain-compliance&focus%5B%5D=securiti&focus%5B%5D=onetrust-privacy-automation&focus%5B%5D=microsoft-priva&focus%5B%5D=ketch&focus%5B%5D=collibra&focus%5B%5D=didomi)
Protecto is the Data Control Plane for Agentic AI. We help enterprises discover, classify, and protect sensitive and confidential data across AI agents, RAG pipelines, and MCP-enabled workflows. Key capabilities: - Discovery and classification of sensitive and context-based data across data stores and AI workflows, in hours rather than weeks - Context-preserving, format-preserving masking that keeps AI outputs coherent - CBAC (Context-Based Access Control) for context-based sensitive information that traditional DLP tools miss - GPTGuard MCP for policy-aware, protected RAG retrieval - Continuous monitoring for privacy and compliance risk - Simple APIs for integration with existing ETL and AI pipelines - Self-guided onboarding with clear documentation
Proteus GRCyber is a risk management solution (IRMS), with GRC and cybersecurity combined into one unified risk framework.
Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.
Proteus NextGen Data Privacy software provides DPOs, Privacy teams and Legal teams with the data privacy management tools required to manage GDPR compliance, CCPA compliance or other data privacy compliance programme, comprehensively and effectively. Ranked #1 data privacy software platform by users in SoftwareReviews’ 2020 Privacy Program Management Data Quadrant, Proteus® NextGen Data Privacy™ brings together cyber security, data privacy, risk management and legal teams with the business leaders to provide a cohesive approach to managing compliance against GDPR, CCPA and a host of other data privacy regulations. Designed for enterprise organisations using current, secure technologies, Proteus NextGen is often regarded as the most highly configurable and comprehensive data privacy software on the market. Covering Privacy Impact Assessments, DPIAs, Transfer Impact Assessments, data mapping, reporting (eg Records of Processing Activity reports), Subject Access Request management, breach notification, vendor management, risk assessment and even automated SCC generation to help with Schrems II compliance, plus other features you would and would not expect. With training and consultancy available to get you up and running quickly, we aim for ultimate customer satisfaction. Proteus® NextGen Data Privacy™ is available in three versions: Proteus NextGen Express for fast, single site audits; Proteus NextGen Enterprise for even the biggest and most complex of organisations; and Proteus NextGen Schrems II, a standalone vendor management capability that maps and risk assesses international transfers and then, where required, automates the production and implementation of the SCCs required as supplementary measures. Schrems II comes as part of the Enterprise version but may be licensed separately by organisations who already have a data privacy system in place but are finding it inadequate to meet the new requirements introduced by the CJEU Schrems II ruling (see here for implications of this ruling). To read more about how our data privacy management software can help you, visit our website www.proteuscyber.com where you can also book a demo. We look forward to speaking with you soon.
QueryPie is a leading all-in-one access governance platform founded in Silicon Valley, helping teams manage and secure access to databases, servers, Kubernetes, and internal web apps — now with powerful AI agent support. Used by top organizations like Kakao, Shinhan, Toss, MUSINSA, HYBE, and Yanolja, QueryPie is fully compliant with global security standards (ISMS, PCI-DSS, GDPR) and trusted by over 130 enterprises. With the launch of the QueryPie Community Edition — a free, self-hosted version available to anyone for one year — startups and SMEs can now access enterprise-grade infrastructure security to stay compliant and productive without the overhead. 🚀 Now Available: QueryPie Community Edition Deploy unified access control for your infrastructure — completely free up to 5 active users. From SQL masking and SSH auditing to Kubernetes RBAC and web app activity logging, everything is included in our self-hosted Community Edition, with no sales call required. ✅ SQL query-level masking & approval ✅ Command-level SSH session control with live replay ✅ Kubernetes API-level access policies ✅ User behavior recording on web apps ✅ Centralized audit logs & enforcement 📘 Setup guide: https://www.querypie.com/resources/learn/documentation/querypie-install-guide 🤖 New: QueryPie AI Hub is Now Public Build and run LLM-powered agents with MCP (Model Context Protocol) — connect external SaaS tools and your own internal systems, all from a single interface. - Smart Tool Discovery powered by RAG - Edge Tunnel for secure internal tool connection (no firewall changes needed) - Custom MCP Server support (SSE-based) - Optional governance layer to control and audit agent behavior 🎯 Try it today: https://app.querypie.com/login 📺 See how it collaboratively works: Watch the demo at https://youtu.be/GdWEW45rJPA Need a unified layer to manage access and securely scale your AI workflows? QueryPie brings it all together — with enterprise-grade control and developer-ready tools.
Average Rating: 4.0/5.0
Total Reviews: 1
AI-generated summary from verified user reviews
"Secure and Centralized Data Access Solution"
Rating: 4.0/5.0 stars
— Falaque F.
RecordPoint provides unified data governance for highly regulated organizations, enabling trust at scale so enterprise data can be used confidently, defensibly, and in compliance with regulatory obligations. RecordPoint delivers end-to-end governance of structured and unstructured data across legacy systems, modern applications, and AI pipelines. Organizations gain visibility and continuous control over where information resides, how it is managed, and how it is retained and disposed. Policies are enforced in place and in the background, helping teams maintain compliance without disrupting business operations or requiring data migration. The platform supports core governance use cases, including information management, data inventory, data categorization, and retention and disposition. Policy-based automation reduces reliance on manual processes and end-user decision-making, helping organizations apply consistent controls as data volumes grow. RecordPoint supports government agencies and regulated enterprises globally, helping them modernize governance programs, reduce risk, and strengthen defensibility. This enables organizations to safely scale AI initiatives and capture competitive advantage, rather than remaining constrained by complexity, disruption, and compliance risk.
Average Rating: 4.3/5.0
Total Reviews: 2
Rating: 4.0/5.0 stars
— Santosh R.
"Management Portals for managers"
Rating: 4.5/5.0 stars
— Alfaizkhan P.
RedactifyAI is a cloud-based, AI-powered document redaction platform that helps law firms, legal departments, and compliance teams permanently remove sensitive information from PDFs, Word documents, and scanned images. Using advanced Named Entity Recognition (NER) technology, RedactifyAI automatically detects and redacts 25+ types of personally identifiable information (PII) — including Social Security numbers, emails, phone numbers, addresses, and financial data — delivering faster, more accurate redaction compared to manual methods. Built specifically for legal professionals, RedactifyAI addresses the critical challenges associated with traditional redaction techniques. It eliminates the risks of incomplete redaction often encountered with manual methods like black box overlays or basic PDF markup tools, which can leave sensitive data recoverable. RedactifyAI performs true permanent text removal, ensuring redacted content cannot be reversed, copied, or extracted. RedactifyAI solves two fundamental problems in document redaction. First, it replaces time-consuming manual review with AI-powered detection that identifies sensitive data in seconds, not hours. Second, it ensures complete data protection by removing not just visible content but also hidden metadata, preventing inadvertent data leaks that manual processes frequently miss. Key features of RedactifyAI include: - AI-powered PII detection using Named Entity Recognition for automatic identification of 25+ sensitive data types - Permanent, irreversible text removal that truly deletes underlying data, unlike surface-level black box overlays - OCR technology for redacting scanned documents and image-based PDFs - Native Clio Manage integration for seamless legal workflow automation - Multi-format support for PDFs, Word documents (.docx), and scanned images - Side-by-side comparison view to review original and redacted documents - Version control and comprehensive audit trails for compliance documentation - Team collaboration with role-based access and multi-seat workspaces - Batch processing for high-volume document redaction - Complete metadata removal to prevent hidden data exposure - Custom data retention policies for regulatory compliance RedactifyAI offers significant advantages over traditional redaction methods: 1. Speed and Efficiency: AI-powered detection reduces redaction time by up to 90% compared to manual review, enabling legal teams to process large document sets in minutes rather than hours. 2. Enhanced Security: Unlike PDF markup software or black box methods that can be reversed or seen through, RedactifyAI provides permanent, irreversible redaction of sensitive information with full metadata removal. 3. Compliance and Auditability: The platform generates detailed audit trails of all redaction activity, creating a clear compliance record — a crucial feature for organizations subject to FOIA, HIPAA, GDPR, and other regulatory requirements. 4. Accessibility: As a browser-based SaaS solution, RedactifyAI can be accessed from any device with an internet connection, requiring no software installation or IT setup. 5. Legal Workflow Integration: Native Clio Manage integration allows legal professionals to redact documents directly within their existing case management workflow, eliminating manual file transfers. Organizations using RedactifyAI can efficiently manage document redaction at scale while maintaining confidentiality and ensuring compliance with data privacy regulations. Whether redacting a single PDF for court filing or processing bulk discovery documents, RedactifyAI provides an intuitive interface that simplifies the entire redaction workflow. With plans starting at $0/month for individuals and scaling to enterprise, RedactifyAI serves solo practitioners, mid-size firms, and large legal departments alike.
Redacto is the India's first AI-agentic privacy, security and third-party risk technology platform built for fast-growing BFSI and Health tech teams. It auto-maps data flows, orchestrates consent, and interrogates vendor evidence, resolving 1,000+ compliance checks in minutes. CISOs & DPOs gain real-time, revenue-saving insight, letting growth accelerate without ever outrunning critical governance or trust.
Every B2B SaaS that uses Stripe, AWS, OpenAI, Microsoft 365 or similar is expected, under GDPR Article 28(2), to publish a current list of those subprocessors and notify customers before the list changes. Almost nobody keeps it current, because the upstream providers change their own lists without telling anyone. Registora closes that loop end to end: - Hosts your public subprocessor register on your subdomain or custom domain. - Monitors the published subprocessor pages of major providers daily and amends your register the moment one changes. - Auto-drafts the GDPR Article 28(2) customer notification email when a change is detected. - Generates a Data Processing Addendum (DPA) and supports e-signature. There is also a free audit at registora.com/check that lists the third parties a site loads. A DORA tier produces a starter EBA Register-of-Information template for EU financial entities. Free tier hosts up to five subprocessors.
Rowpa is UK-built GDPR software for small businesses that have no legal team and no DPO, and that get asked for compliance documents by their customers. Enter your website. Rowpa scans it for the tools, trackers and scripts it recognises, classifies your business, and drafts your Article 30 record of processing activities, with a legal basis, a retention period and a vendor against every activity. Where it is unsure it says so and flags it, rather than guessing quietly. You review and approve everything before it goes anywhere. Then it answers the ask. When a customer wants your GDPR documents, Rowpa assembles a supplier pack addressed to them: how you handle data, sub-processors, international transfers, AI tools in use, security measures, breach and complaints procedures, policies and a named signatory, shared as a link you can revoke or as a PDF. When a buyer sends a security questionnaire spreadsheet, Rowpa drafts every row it can evidence from your record and your security profile, shows the source beside each answer, marks the rows only you can answer, and writes your approved answers back into their own file in their own layout. It also keeps the record alive: a privacy policy generated from your ROPA and flagged when the record moves on without it, a vendor DPA library covering 400+ tools with sub-processor lists and transfer mechanisms checked at the source, a data subject request workflow with AI-drafted responses, a public Trust Center URL for the prospect who checks before asking, a DPIA tool, a breach response planner, and weekly monitoring of ICO guidance and vendor changes. Built for UK and EU small businesses: SaaS startups facing enterprise procurement, e-commerce and app developers, recruitment firms, accountants, solicitors, MSPs, and marketing and web agencies managing client compliance. Hosted in the EU (Frankfurt). No model training on customer data. Row-level tenant isolation. Passwordless sign-in. Cyber Essentials certified by IASME. ICO registration ZC134108. UK GDPR and EU GDPR in one tool, with interface and pricing in English, German, French, Polish and Spanish. Rowpa is not a consent management platform and does not serve a cookie banner. It is not SOC 2 or ISO 27001 automation. It is not legal advice and is not a substitute for a Data Protection Officer where one is legally required. It is the working tool that produces what you are asked for.
Safe Privacy Mask is a Chrome extension that detects and replaces sensitive information in input fields before data is sent to external services. The extension identifies emails, phone numbers, API keys, tokens, IP addresses, credit card numbers, and region-specific IDs, replacing them with customizable tokens directly in the input field. Detection and masking occur locally on the device, ensuring no personal data is sent to external servers. The extension supports AI chat platforms like ChatGPT, Claude, Gemini, and Copilot, and works with any web form via manual field registration. Users can create unlimited custom replacement rules using word matching or regular expressions, with options for case sensitivity and whole-word matching. Masking can occur in real time, upon pasting, or before sending. No account creation, ads, or tracking is required, and settings are stored locally. Advanced features include checksum validation for credit card numbers and timeout protection for rules.
Savira is an Australian privacy compliance platform and consent management platform (CMP) built for small and medium businesses. It helps you manage your website privacy obligations under the Privacy Act 1988 and the Australian Privacy Principles (APPs), without needing a lawyer, a developer or a dedicated privacy officer. Most consent management and cookie consent tools are built for global enterprises and the GDPR. Savira is built for Australian businesses and Australian privacy law, with setup, pricing and support designed for smaller teams. Cookie consent banner Savira adds a cookie consent banner to your website that gives visitors a clear choice about cookies and tracking. Tracking scripts, such as analytics and advertising pixels, are held back until the visitor agrees. Consent records and compliance logs Every consent choice is logged in your Savira dashboard. You keep a dated record of consent to refer to if a customer asks, or if the Office of the Australian Information Commissioner (OAIC) makes an enquiry. Privacy policy generator Savira creates an Australian privacy policy based on the APPs and publishes it to your website, so your privacy notice stays in one place and is easy to keep up to date. Free website privacy scan Scan your website free to see which cookies and trackers it uses, whether your consent banner and privacy policy are in place, and where you have gaps against the Australian Privacy Principles. WordPress cookie consent plugin Install the Savira WordPress plugin and you are set up in about 10 minutes. Savira adds your privacy policy, switches on your cookie banner and starts recording consent, with no coding required. Australian data hosting and security Customer data is hosted on AWS in Sydney, Australia. Identifiable end-user data is encrypted at rest, and access to decrypted data is controlled and logged. Who uses Savira Savira is privacy compliance software for Australian businesses that collect personal information through their website. That includes health and allied health clinics, medical practices, real estate agencies, pharmacies, accounting and law firms, retailers, and the digital and marketing agencies that manage their websites. Why it matters Australian privacy law applies to how websites collect personal information, including through cookies, tracking pixels and online forms. The OAIC has found that tracking pixels can collect personal information, and health information is sensitive information that needs extra care. Savira gives you a practical way to manage website consent, privacy notices and consent records in one place.
The Enterprise Platform for Consent, Privacy and Data Quality Governance. Sentinel Insights provides continuous visibility into whether consent and privacy requirements are actually being followed across digital data. And, we ensure marketers leverage clean, consented, and high quality data. Unlike periodic scans, we detect risk using real visitor data in real time and provide defensible evidence to support identification, remediation, and executive oversight.
