AI-Generated Results
Finding matches…
Technological advancements and evolving work habits are expanding the modern attack surface. Adversaries are using AI to rapidly scan and breach networks, making it critical for organizations to identify and mitigate vulnerabilities before they can be exploited.
The Unisys Attack Surface Discovery solution scans your modern attack surface, analyzes the results, and reports on insights augmented with risk quantification in business context. Your IT resources can focus on what matters most to your business while gaining visibility into unknown assets, exposure discovery, and contextual threat intelligence.
Not seeing what you're looking for?
Dive deeper into "AITalk" on G2 AI

Gordon Attack Surface Monitoring continuously discovers and monitors all internet-facing assets associated with an organization, including domains, subdomains, IP addresses, cloud resources, APIs, and third-party integrations, without requiring a pre-configured asset inventory.
The platform scans from an external perspective using DNS records, certificate transparency logs, WHOIS data, and passive reconnaissance to identify known and unknown assets, including shadow IT and inherited infrastructure. Each discovered asset is assessed for misconfigurations, exposed services, outdated software, and known vulnerabilities, then assigned a risk score based on severity and exploitability.
Users receive continuous alerts when new assets appear, configurations change, or new vulnerabilities are detected. Findings include remediation guidance and a map to common compliance frameworks, including NIST CSF, ISO 27001, PCI DSS, and SOC 2. The platform requires only a domain or email address to begin scanning and deploys without agents or connectors.

Mandiant Attack Surface Management is a cybersecurity solution designed to provide organizations with a comprehensive view of their external digital footprint. By continuously discovering and analyzing internet-facing assets—including cloud resources, applications, and services—ASM identifies vulnerabilities, misconfigurations, and exposures. This proactive approach enables security teams to understand their attack surface from an adversary's perspective, allowing them to prioritize and remediate risks effectively.
Key Features:
- Continuous and Automated External Asset Discovery: ASM continuously identifies and monitors internet-facing assets across dynamic environments, ensuring up-to-date visibility.
- Infrastructure Integrations: The solution supports integrations with cloud and DNS providers, enhancing asset visibility and management.
- Intelligence-Informed Active and Passive Checks: Utilizing frontline intelligence, ASM performs both active and passive assessments to validate asset susceptibility to exploitation.
- Customizable Scans: Organizations can schedule daily, weekly, or on-demand scans to meet specific security requirements.
- Outcome-Based Asset Discovery: ASM allows for tailored asset discovery workflows based on specific outcomes or use cases, enhancing operational efficiency.
- Integration Support: The platform is compatible with various Security Information and Event Management , Security Orchestration, Automation, and Response , and ticketing systems, facilitating streamlined remediation processes.
Primary Value and Problem Solved:
In today's rapidly evolving IT landscape, organizations face challenges in maintaining visibility over their expanding digital environments, which include cloud services, SaaS applications, and remote work infrastructures. This expansion often leads to unknown or unmanaged assets, increasing the risk of cyber threats. Mandiant ASM addresses this challenge by providing continuous, automated discovery and analysis of external assets, enabling organizations to:
- Enhance Security Posture: By identifying vulnerabilities before they can be exploited, ASM helps organizations strengthen their defenses.
- Mitigate Risks: The solution reduces the attack surface by alerting teams to exposed assets, allowing for timely remediation.
- Achieve Comprehensive Visibility: ASM offers a detailed inventory of applications and services within the external ecosystem, ensuring no asset goes unnoticed.
By operationalizing threat intelligence and providing actionable insights, Mandiant ASM empowers organizations to proactively manage their attack surface, thereby reducing the likelihood of security breaches and ensuring a robust cybersecurity posture.
On your way to the top, you need a comprehensive understanding of the latest threats targeting your business and how much risk to remediate, retain or transfer via a cyber risk insurance policy. We understand the tactics, techniques and procedures used by attackers to bypass defenses and we will help you quantify your cyber risk, prevent and mitigate it. Here’s how we will help your organization:
– We’ll secure your remote and onsite workforce –
– Prevent risks and attacks as they happen with our managed detection and response service –
– Identify ongoing vulnerabilities, penetration testing, email security, employee training, advanced any analysis and incident response –
– Quantifying your cyber risk and insurance need –
PT Telecom Attack Discovery is designed to provide security monitoring, up-to-the-minute detection of anomalous activity, and protection of the signaling network perimeter.
We are passionate about cybersecurity and proud to make the Internet safer. We aim to propose a comprehensive threat intelligence solution accessible to all cybersecurity professionals and design a platform with one of the best user experiences.Our services include:
Platform-API-Data Feeds.

IONIX is the attack surface management solution that uses Connective Intelligence to shine a spotlight on exploitable risks across your real attack surface and its digital supply chain. Only IONIX discovers and monitors every internet-facing asset and connection, delivers laser focus into the most important risks to your business, and provides the tools to rapidly remediate exploitable threats and reduce attack surface risk. Global leaders including Infosys, Warner Music Group, The Telegraph, and E. ON depend on IONIX’s machine learning-powered discovery engine, contextual risk assessment and prioritization, and end-to-end remediation workflow to go on the offensive in managing their complex and ever-changing attack surfaces.
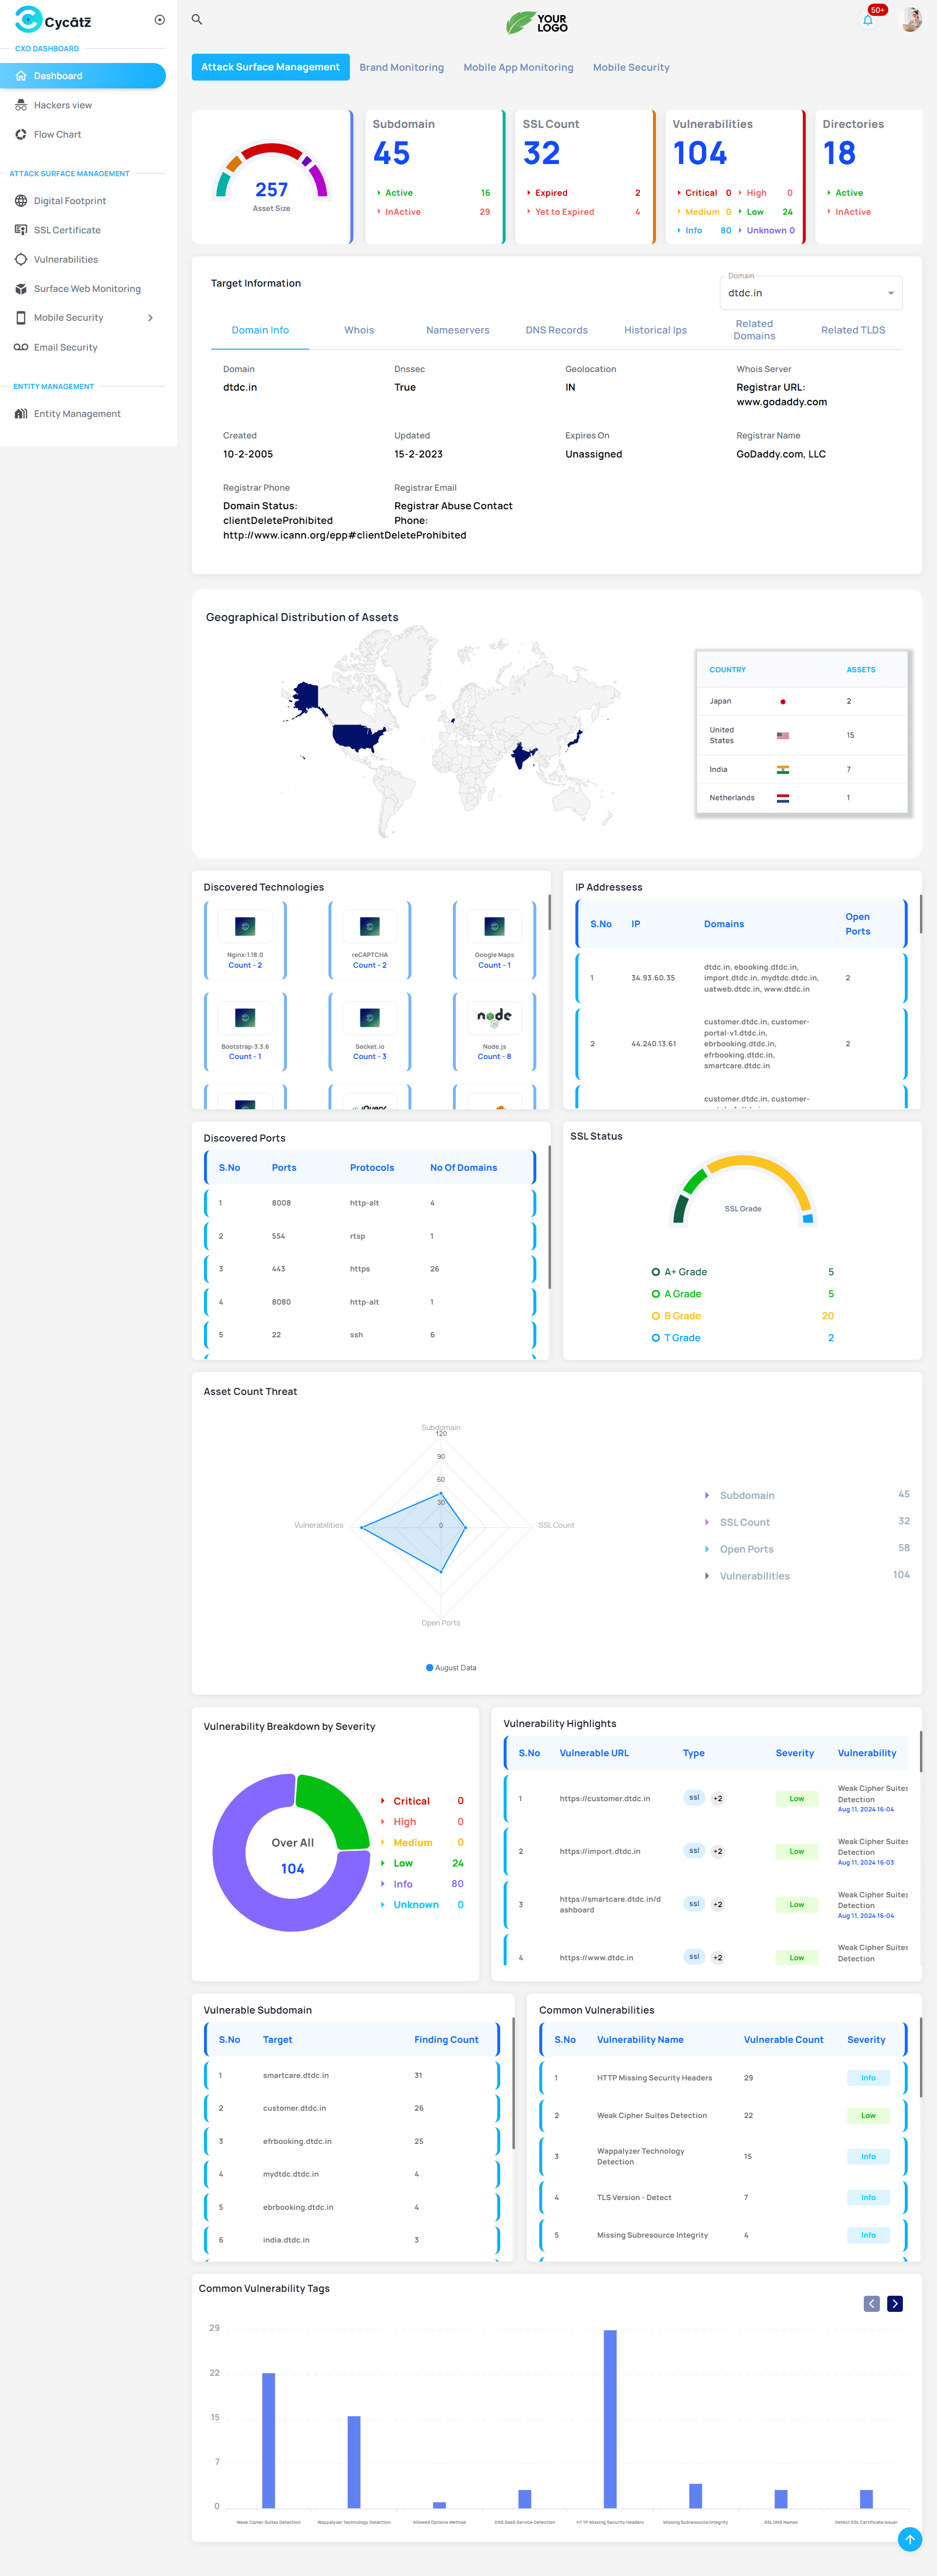
"External App. Vulnerabilities External Asset Vulnerabilites SSL Certificate & Lookalike Domain Monitoring Digital Foot print &
Vulnerabilities Attack path Analysis with Mitre Attack Threat Feed &
Threat Intelligence
Fake App Mobile Detection
Email Security
Incident Management Integration with all the tools"
"Dark web Monitoring Surface Web Monitoring
Brand Monitoring,
Threat Feed & Threat Intelligence
Fake App Mobile Detection"

Kaduu helps you understand when, where and how stolen or accidentally leaked information in dark web markets, forums, botnet logs, IRC, social media and other sources is exposed. Kaduu’s alerting service can also detect threats before they turn into incidents. Kaduu offers AI-driven dark web analysis, real-time threat alerts and pre-Attack threat indicators. Setup in minutes you will receive instant access to real-time reporting including:
- Infrastructure exposure: IOT, Git, AWS, Bitbucket & more
- People exposure: Social media monitoring
- Ransomware exposure: leak & credential monitoring
- Attack prevention: domain and certificate monitoring
Quest Identity Defense (previously known as Security Guardian) is an AI-powered, hybrid Active Directory security solution that continuously identifies identity risk, blocks unauthorized changes to critical Tier 0 assets, and instantly contains attacks before they spread.
With clear visibility and observability across human and non-human identities, organizations can investigate, respond, and remediate threats with simplicity and speed.

Host4Geeks offers SSD-powered shared web hosting solutions designed to provide fast, reliable, and affordable services for individuals and businesses. With a focus on performance and security, their hosting plans cater to a wide range of website requirements, ensuring optimal uptime and user experience.
Key Features and Functionality:
- Enterprise-Grade Servers: Utilization of the latest SSD drives and branded hardware from Supermicro and Dell, housed in top-tier data centers across multiple global locations.
- Free Domain Name: Customers opting for the Business SSD Web Hosting Plan on a 1, 2, or 3-year term receive a complimentary .com or .in domain for the duration of their hosting service.
- Free SSL Certificates: All hosting plans include free SSL certificates, enhancing website security and trustworthiness.
- LiteSpeed Web Server: Integration of LiteSpeed Web Server technology ensures faster load times and improved performance.
- DDoS Protection: Comprehensive DDoS protection safeguards websites against malicious attacks, ensuring uninterrupted service.
- CloudFlare CDN Integration: Incorporation of CloudFlare Content Delivery Network (CDN) enhances website speed and security by distributing content across multiple servers worldwide.
- 24/7 Customer Support: Round-the-clock support is available to assist with any technical issues or inquiries.
Primary Value and Solutions Provided:
Host4Geeks' shared hosting services address the need for dependable and high-performing web hosting at competitive prices. By offering features like SSD storage, robust security measures, and global data center locations, they ensure websites operate efficiently with minimal downtime. The inclusion of free domain names and SSL certificates adds value, reducing additional costs for users. Their commitment to customer support ensures that clients receive timely assistance, making Host4Geeks a comprehensive solution for hosting needs.

Spot by NetApp is a comprehensive cloud operations platform designed to automate and optimize cloud infrastructure management across various environments, including AWS, Azure, and Google Cloud. By leveraging advanced analytics and machine learning, Spot enables organizations to enhance application performance, ensure high availability, and achieve significant cost reductions. The platform offers a suite of solutions that address cloud cost management, Kubernetes infrastructure optimization, and cloud commitment management, providing full visibility and automation to maximize efficiency and scalability.
Key Features and Functionality:
- Automated Infrastructure Management: Spot automates the provisioning, scaling, and optimization of cloud resources, ensuring applications receive the necessary resources without over-provisioning.
- Kubernetes Optimization: With solutions like Spot Ocean, the platform continuously analyzes container resource requirements, optimizing Kubernetes infrastructure for performance and cost-efficiency.
- Cloud Cost Management: Spot provides tools such as Cost Intelligence and Billing Engine to deliver actionable insights, comprehensive billing reports, and intelligent cost allocation, enabling effective cloud financial management.
- Cloud Commitment Management: The platform includes Spot Eco, which automates the management of Reserved Instances and Savings Plans, optimizing cloud commitments for maximum savings and flexibility.
- Continuous Security: Spot Security offers continuous assessment and analysis of cloud security posture, helping organizations identify misconfigurations, reduce potential attack surfaces, and ensure compliance.
Primary Value and Problem Solved:
Spot by NetApp addresses the challenges of managing complex cloud infrastructures by providing automated solutions that optimize resource utilization, enhance application performance, and reduce operational costs. By integrating cloud cost management, infrastructure optimization, and security into a unified platform, Spot empowers organizations to focus on innovation and business growth while maintaining control over their cloud environments. This holistic approach ensures that businesses can scale efficiently, maintain high availability, and achieve substantial cost savings without compromising on performance or security.

Our autonomous PreCrime™ platform predicts, blocks, and preempts malicious campaigns before they impact your business. This evolutionary learning technology is constantly improving anomaly
identification, while reducing false positives to 0.05%, enabling organizations to stop attacks in minutes.
PreCrime Intelligence is our predictive attack intelligence solution. Our behavioral AI goes beyond reactive blocklists to equip your team with the most extensive dataset of future malicious infrastructure, better arming your security stack to deny malicious traffic in near real-time before they launch attacks.

NuovoTeam is a Team Communication solution-focused towards field force and frontline employees. It enables organizations to provide team communication and collaboration software to non-desk employees. NuovoTeam brings the power of instant messaging, VoIP Calling and group chats to facilitate team communication within a secure environment.
Modern teams and a perimeter-less workforce need a trusted, secure tool to communicate and collaborate with ease. NuovoTeam facilitates team communication within a secure environment, enables teams to share business documents and files and paves the way for group communication without compromising data security.
Features:
Two-way Encrypted messaging :
Communicate with your remote team members with a secure messaging app. Send and receive messages, get the message read status and flag important messages for future reference. Allow or block message text copy, delete, edit and forward actions.
VoIP calling & Voice notes:
Keep in touch with your perimeter-less workforce. Call your team members over a VoIP call. Record and send voice messages to your contacts
Restrict usage to approved users only:
Add users to the NuovoTeam dashboard with email and invite users to the NuovoTeam app. Employees can start communicating with the pre-populated contact list only. This prevents the usage of the application for personal or non-business purposes.
Broadcast messages:
Broadcast messages and updates to select users in the organization. Add users to a broadcast channel and send messages to all the users in the channel.
Exchange images & files:
Don't let lack of business resources hamper employee productivity. Simplify collaboration by sharing images and add appropriate captions. Exchange PDF files, word documents and text files with Oneteam messenger.
Group Communication simplified with NuovoTeam Channels
Make way for improved team communication with group chats using NuovoTeam Channels.
Public Channel:
Create an organization-wide channel and invite users to group communication. Users can subscribe or unsubscribe from the channel anytime.
Closed Channel:
Create a team-specific channel for enabling group chats within a team. Users are auto-subscribed to the channel and cannot unsubscribe.
Limited Public Channel:
Create an open channel for specific users in your organization. Users can subscribe and unsubscribe anytime.
LMNTRIX provides a fully managed 24x7x365 Managed Detection & Response platform. The LMNTRIX multi-vector fully managed platform includes advanced network and endpoint threat detection, deceptions everywhere, analytics, full fidelity forensics, automated threat hunting on both the network and endpoints, and real-time threat intelligence technology, combined with deep/dark web monitoring which scales for small, medium, enterprise, cloud or SCADA/Industrial environments.
We Prevent, Detect, Investigate, Validate, Contain and Remediate security incidents. The LMNTRIX platform/service includes full incident validation and remote incident response activities without the need for an incident-response-specific retainer; such activities may include malware analysis,
identifying IOCs, automated and human-powered threat hunting, granular threat
containment at endpoint level and specific guidance on remediation.
The outcomes we deliver clients are fully validated incidents aligned to the kill chain and Mitre ATT&CK framework. No dumb alerts. These outcomes contain detailed investigative actions and recommendations that your organization follows to protect against the unknown, insider threat and malicious attacker.

Kaspersky Security for Microsoft Office 365 is an advanced, all-in-one threat protection solution designed to safeguard Microsoft Office 365's communication and collaboration services. It enhances the default security controls of Office 365 by addressing known, unknown, and advanced threats through the use of advanced heuristics, machine learning, and other next-generation technologies. This comprehensive protection covers Microsoft Exchange Online, OneDrive, SharePoint Online, and Teams, ensuring that cloud-oriented enterprises are shielded from ransomware, malicious attachments, spam, phishing, Business Email Compromise , and other cyber threats.
Key Features and Functionality:
- Comprehensive Threat Protection: Utilizes advanced heuristics, machine learning, and next-generation technologies to detect and prevent ransomware, malicious attachments, spam, phishing, BEC, and unknown threats across Microsoft Exchange Online, OneDrive, SharePoint Online, and Teams.
- Phishing and BEC Prevention: Employs a combination of SPF, DKIM, and DMARC email validation methods, along with sandboxing and machine learning, to filter out phishing attempts and BEC attacks before they reach users.
- Advanced Threat Detection: Combines signature-based protection, heuristic and behavioral analysis to immediately detect advanced threats in all Office 365 applications.
- Data Compliance and Visibility: Provides continuous auditing of cloud data, utilizing preset templates to identify confidential and sensitive information, ensuring data integrity and compliance readiness.
- Seamless Integration: Offers straightforward licensing without vendor lock-in, allowing businesses to scale without incurring exponential costs.
Primary Value and User Solutions:
Kaspersky Security for Microsoft Office 365 addresses the security gaps in Microsoft's default controls by providing robust protection against a wide range of cyber threats. It ensures that enterprises can safely utilize Office 365's communication and collaboration tools without the risk of data breaches, malware infections, or compliance violations. By integrating seamlessly with existing Office 365 services, it offers a cost-effective and scalable solution that enhances overall cybersecurity posture, allowing businesses to operate with confidence in their cloud environments.

CrowdStrike, a global cybersecurity leader, has redefined modern security with one of the world’s most advanced cloud-native platforms for protecting critical areas of enterprise risk – endpoints and cloud workloads, identity and data. Powered by the CrowdStrike Security Cloud, the CrowdStrike Falcon® platform leverages real-time indicators of attack, threat intelligence, evolving adversary tradecraft and enriched telemetry from across the enterprise to deliver hyper-accurate detections, automated protection and remediation, elite threat hunting and prioritized observability of vulnerabilities.
Reposify is an External Attack Surface Management platform that delivers autonomous, 24/7 discovery of exposed internet assets and shadow IT risks so they can be eliminated before attackers exploit them. No installation is required.
Your attack surface is the sum of every attack vector that can be used to breach your perimeter defenses. In other words, it is the total quantity of information you are exposing to the outside world. Typically, the larger the attack surface, the more opportunities hackers will have to find a weak link which they can then exploit to breach your network. Professional hackers typically follow the cyber kill chain when attacking a target, and surveying the target's attack surface is normally the very first step in this process; what is known as advanced reconnaissance. Reducing the attack surface can minimize risk further down the cyber kill chain, preventing attacks before they even occur by eliminating potential attack vectors as early as possible. The cyber kill chain is a method of categorizing and tracking the various stages of a cyberattack from the early reconnaissance stages to the exfiltration of data. Quantum Armor aims at monitoring, managing and reducing your attack surface.

Remote workers often unwittingly put their organizations at risk by visiting phishing sites or downloading malware. Harmony Browse is a modern web security solution that offers the strongest protections against web-based attacks without compromising workers productivity.