Best Vendor Security and Privacy Assessment Software - Page 7

How Many Vendor Security and Privacy Assessment Software Products Does G2 Track?

Total Products under this Category: 142

Category Stats (Sep 2026)

  • Average Rating: 4.56/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Whistic (+0.31%) - Among all products in this category, Whistic recorded the largest rating increase compared to last month

Last updated: September 29, 2026

How Does G2 Rank Vendor Security and Privacy Assessment Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 16,300+ Authentic Reviews
  • 142+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

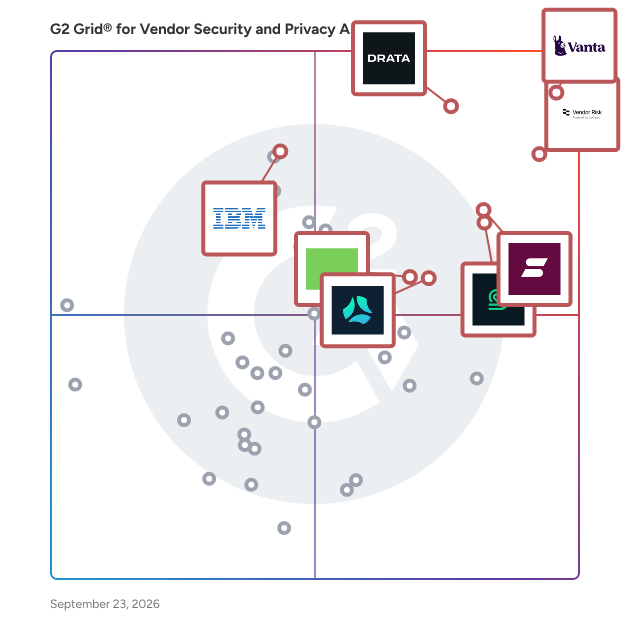
G2 Grid® for Vendor Security and Privacy Assessment Software

G2 Grid® for Vendor Security and Privacy Assessment Software plotting products by satisfaction and market presence

Highlighted products: Vanta, UpGuard Vendor Risk, Drata, Sprinto, Secureframe, Scrut Automation, IBM OpenPages, and Thoropass.

Underlying data: [Grid® JSON](https://www.g2.com/categories/vendor-security-and-privacy-assessment/grids.json?focus%5B%5D=vanta&focus%5B%5D=upguard-vendor-risk&focus%5B%5D=drata&focus%5B%5D=sprinto-inc&focus%5B%5D=secureframe&focus%5B%5D=scrut-automation&focus%5B%5D=ibm-openpages&focus%5B%5D=thoropass)

Avertro

CyberHQ® from Avertro is the Resilience Command Platform that directs your defense. We translate technical signals into quantifiable, governance-ready intelligence, empowering you to validate cyber effectiveness, prove defensible resilience, and optimize security-per-dollar with absolute confidence.

Who Is the Company Behind Avertro?

  • Seller: Avertro
  • Year Founded: 2019
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    17 employees on LinkedIn®

Azanzi TPRM

Azanzi TPRM is a Third-Party Risk Management platform that our customers use to manage cyber security and ESG compliance in the supply chain

Who Is the Company Behind Azanzi TPRM?

Bayonet

Bayonet is a first-of-its-kind sales prospecting tool designed specifically for Sales professionals selling cybersecurity products and services. Effectively, a lead-generation platform, Bayonet features hundreds of thousands of qualified leads — compromised companies around the world with active vulnerabilities that can be converted into customers. Bayonet accelerate sales prospecting by: - Finding customers that need your solutions in seconds. - Filtering prospects to match your qualification criteria. - Enriching prospects with unprecedented vulnerability data. - Providing prospects their Supply Chain risk reports.

Who Is the Company Behind Bayonet?

Censinet

Censinet delivers the healthcare industry’s leading risk intelligence platform, designed specifically to help organizations understand and manage systemic risk across their digital and third-party ecosystems. Powered by the RiskOps™ platform, Censinet provides enterprise-wide visibility into how risk moves across vendors, products, technologies, and critical clinical and operational functions. By operationalizing industry frameworks such as the Health Sector Coordinating Council’s Sector Mapping and Risk Toolkit (SMART), Censinet helps healthcare organizations identify concentration risk, understand operational dependencies, and prioritize mitigation efforts that strengthen resilience and support recovery when disruption occurs. The platform also supports AI governance by providing insight into vendor and product AI usage, while leveraging AI-powered automation to streamline assessments and risk operations across the healthcare ecosystem. Learn more at censinet.com.

Who Is the Company Behind Censinet?

  • Seller: Censinet
  • Year Founded: 2017
  • HQ Location: Boston, US
  • LinkedIn® Page: www.linkedin.com
    43 employees on LinkedIn®

Complyrim Vendor Triage

Vendor Triage is an AWS-native SaaS platform for third-party risk management. It automates vendor security assessments and generates audit-ready reports — accelerating vendor evaluation from the industry-typical 2 to 3 weeks down to 2 to 3 days through intelligent workflows, multi-stakeholder routing, and evidence validation. The questionnaire: 78 industry-standard questions across 8 security domains — information security policy, access management, encryption and key management, network security, vulnerability management, incident response, business continuity, and third-party / subprocessor risk. Questions map to SOC 2, ISO 27001, NIST CSF, HIPAA, GDPR, and PCI DSS controls. Why completion rates beat the industry: Vendor Triage achieves an 85%+ questionnaire completion rate by routing each section to the appropriate stakeholder at the vendor — security questions to the CISO or security lead, privacy questions to the DPO, technical questions to engineering. Single-recipient questionnaires from competitors typically stall on a single overworked contact and complete at 50-60%. Evidence validation: vendors upload SOC 2 reports, ISO certificates, penetration test reports, insurance certificates, and policy documents directly into the platform. Vendor Triage performs automated verification — expiry date checks, scope validation, cross-reference matching against questionnaire responses. Evidence and answers combine into an audit-ready PDF. Risk scoring: intelligent classification by contract value, data sensitivity, and operational criticality. Critical vendors (those handling regulated data or core operations) trigger expanded due diligence; low-risk vendors complete the standard assessment. Risk scores roll up into the executive summary auditors reach for first. What you get: audit-ready PDF with executive summary, full questionnaire, evidence references, risk score, and prioritized remediation roadmap for any vendor that fails any control. Supports SOC 2, ISO 27001, NIST CSF, HIPAA, GDPR, and PCI DSS framework alignment. Who uses Vendor Triage: vendor risk managers, TPRM leads, procurement teams, legal teams, and CISOs at any organization managing 10 or more vendors with compliance requirements. Particularly valuable for FinTech, HealthTech, B2B SaaS, and government contractors that need vendor assessments on file before audit time. What it replaces: spreadsheet-based vendor assessment processes, single-recipient SurveyMonkey-style questionnaires, and enterprise GRC TPRM modules at $50,000-plus per year. Vendor Triage is purpose-built for the mid-market 100-1,000 employee company that's outgrown spreadsheets but can't justify enterprise GRC pricing. Pricing description (500 chars max) Subscription on AWS Marketplace from $49/month for low-volume teams to $999/month for high-volume vendor risk programs.

Who Is the Company Behind Complyrim Vendor Triage?

Cyberator

Cyberator is an innovative governance, risk and compliance (IT GRC) solution, that can take a 360 degree view of your cybersecurity program in areas such as people, process and technology utilization and provide quantifiable maturity scores on your entire program, along with a comprehensive remediation plan to address the identified gaps. Our solution helps you address the following pain points: • How can I quickly leverage the best security framework and align it to my organization's objective to build my roadmap? • Am I compliant with the latest data privacy and security regulations? • Do I have the right plan, processes and technologies in place to mitigate and lower the identified risk? • Am I prioritizing and focusing my limited security resources and budget on the areas where they can do the most good? • How can I efficiently manage potential risks arising from third-party vendor relationships?

Who Is the Company Behind Cyberator?

  • Seller: Zartech
  • Year Founded: 2016
  • HQ Location: Dallas, US
  • Twitter: @ZartechInc
    44 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    54 employees on LinkedIn®

Cybernark

Cybernark helps organizations comply with ISO27001 by providing automated supplier onboarding, security assessments, CIA risk scoring, document and evidence management, continuous monitoring and audit-ready reporting. The platform enables secure vendor-supplier communication and gives organizations full visibility into supply-chain cyber risks without relying on spreadsheets or excel.

Who Is the Company Behind Cybernark?

CyberRank

Who Is the Company Behind CyberRank?

  • Seller: IISRI
  • Year Founded: 2016
  • HQ Location: Auckland, NZ
  • LinkedIn® Page: www.linkedin.com
    6 employees on LinkedIn®

CyberVadis

Mitigate third-party cyber risks. With confidence. CyberVadis is a trusted solution for mitigating third-party cyber risks. We combine the speed of automation with the reliability of a team of information security experts, providing evidence-based assessments. Our comprehensive, scalable and managed solution enables you to effectively reduce risks across your entire supply chain. - Manage all third parties on a single platform - Collect and monitor automated risk insights - Have all critical suppliers assessed by analysts based on evidence - Drive improvements & share recommendations

Who Is the Company Behind CyberVadis?

CYRAPID AI

CYRAPID AI, a research-based & risk-managed GENERATIVE AI Platform for Cyber, enables accelerated cyber risk and TPRM assessments with more accuracy and at 65% less cost while guaranteeing human-level quality.

Who Is the Company Behind CYRAPID AI?

Ethira

Ethira is a supply chain security and TPRM platform for high-trust organizations: financial services, healthcare, critical infrastructure, and other sectors where a vendor compromise becomes your incident. It continuously discovers every vendor, subprocessor, internal system, and AI agent touching your estate, including the shadow IT and shadow AI that never went through procurement, then monitors how each one actually interacts with your systems and data at runtime. When a third party is breached, impact analysis traces the blast radius from that vendor through services and data stores down to the specific datasets and fields exposed, in minutes rather than weeks. Findings carry owners, evidence, and data reach, and trigger automated response through Slack, API, and existing security tooling. The same live inventory produces DORA Registers of Information, GDPR Article 30 records, and audit evidence as a byproduct.

Who Is the Company Behind Ethira?

  • Seller: Ethira
  • Year Founded: 2025
  • HQ Location: Stockholm, SE
  • LinkedIn® Page: www.linkedin.com
    18 employees on LinkedIn®

Fortify CSRM

Fortify 1's CSRM, simplifies how businesses demonstrate holistic cybersecurity risk management from front-line technical defenses to non-technical requirements such as governance and oversight.

Who Is the Company Behind Fortify CSRM?

  • Seller: Fortify1
  • Year Founded: 2016
  • HQ Location: Denver, US
  • LinkedIn® Page: www.linkedin.com
    4 employees on LinkedIn®

Galink

Galink replaces manual vendor cyber risk assessments with AI. Galink is built with a single mission: save Cybersecurity and GRC teams over 1 million hours by eliminating manual vendor risk work, something only AI can achieve. Vendor cyber risk management has become increasingly complex, time-consuming, and analyst-dependent. Galink transforms this model by embedding AI at the core of the entire vendor risk lifecycle. Galink offers two AI operating modes, allowing organizations to adopt AI at their own pace: • AI-Assisted Mode The AI supports security and GRC teams by generating risk analyses, recommendations, findings, and remediation actions, while humans remain in control of final decisions. • Autonomous AI Mode The AI operates as a virtual analyst, fully performing vendor assessments, reviewing evidence and documents, identifying risks, and proposing remediation actions, dramatically reducing human effort. Across both modes, Galink enables teams to: • Automatically detect and prioritize vendor cyber risks • Tier suppliers based on criticality and exposure • Run questionnaires and AI-driven evidence reviews • Share structured remediation action plans with vendors • Continuously monitor vendor risk with live insights and alerts Unlike traditional VRM tools that digitize manual processes, Galink replaces them. By shifting analyst work to AI, organizations can finally scale vendor risk management without increasing headcount. Galink is trusted by CISOs, Cybersecurity teams, Risk and Compliance leaders who need clarity, speed, and measurable time savings — especially in regulated environments (ISO 27001, DORA, and beyond). Outcome: fewer manual tasks, faster decisions, and thousands of hours returned to cyber and GRC teams.

Who Is the Company Behind Galink?

GORICO

Solving the compliance and certification challenge is only the first step. GoRICO empowers organizations to understand, attain and sustain true security.

Who Is the Company Behind GORICO?

  • Seller: Accorian
  • Year Founded: 2019
  • HQ Location: East Brunswick, New Jersey, United States
  • LinkedIn® Page: www.linkedin.com
    146 employees on LinkedIn®

Guardiso

Guardiso is a governance, risk and compliance (GRC) platform built in Europe, covering international frameworks and national law in one place. One control catalogue spans every framework a company is subject to, among them ISO 27001, GDPR, NIS 2, DORA, TISAX, SOC 2, ISO 27701, ISO 22301, ISO 42001 and the EU AI Act. A control satisfied for one standard counts towards the others, so the same work is not repeated for every audit. We use Guardiso ourselves and we are ISO 27001 certified. The platform holds the parts an auditor asks to see. Policies carry versions, approvals and acknowledgements by named people. The risk register links every risk to the controls that treat it. The evidence register stores each item with a timestamp and a hash, so its integrity can be shown later. There is an internal audit programme with checklists for each framework, an incident register with regulatory reporting, supplier assessments with security questionnaires, GDPR registers, business continuity and employee training. Evidence is gathered from the systems a company already runs. Guardiso connects to Microsoft 365, Microsoft Entra, Google Workspace, AWS, Azure, Google Cloud, GitHub, GitLab, Okta, Jira, Slack and Snyk, checks their security settings every day and files each result against the relevant control. Evidence packs for an auditor are exported in DOCX, PDF and XLSX. The Guardiso Assistant drafts policies and procedures from answers about the organisation, proposes a risk assessment and answers security questionnaires sent by business partners. A person reviews and approves everything before it is used. National law sits beside the international frameworks. Where a country implements a directive in its own act, that act is covered as a framework of its own. The first one is the Polish cybersecurity act implementing NIS 2: the product determines whether it applies to an organisation, which statutory duties follow and which requirements must be met. The interface, the policy text and the documents an auditor receives are multilingual, and further European languages are being added. The company has provided compliance consulting since 2018. The Guardiso platform launched in 2026. Data is stored in the European Union.

Who Is the Company Behind Guardiso?

  • Seller: Guardiso
  • Year Founded: 2018
  • HQ Location: Poznan, Poland
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®
Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024