Best Vendor Security and Privacy Assessment Software - Page 10

How Many Vendor Security and Privacy Assessment Software Products Does G2 Track?

Total Products under this Category: 140

Category Stats (Sep 2026)

  • Average Rating: 4.56/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Skypher (+0.29%) - Among all products in this category, Skypher recorded the largest rating increase compared to last month

Last updated: September 15, 2026

How Does G2 Rank Vendor Security and Privacy Assessment Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 16,100+ Authentic Reviews
  • 140+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

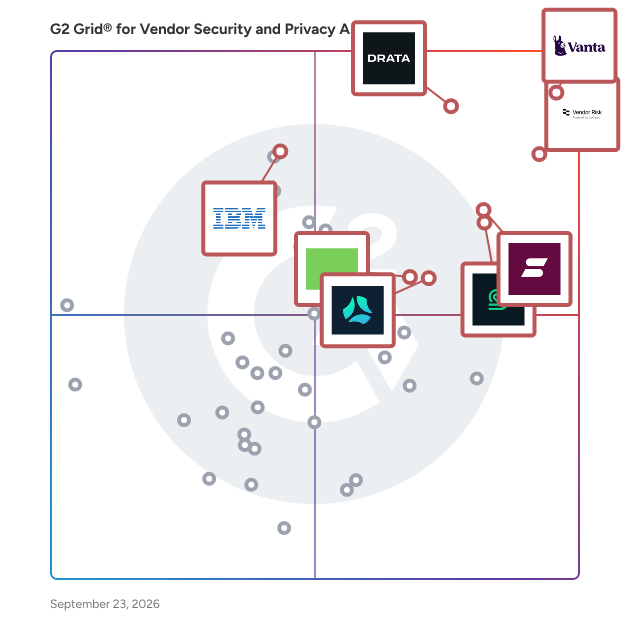
G2 Grid® for Vendor Security and Privacy Assessment Software

G2 Grid® for Vendor Security and Privacy Assessment Software plotting products by satisfaction and market presence

Highlighted products: Vanta, UpGuard Vendor Risk, Drata, Sprinto, Secureframe, Scrut Automation, IBM OpenPages, and Thoropass.

Underlying data: [Grid® JSON](https://www.g2.com/categories/vendor-security-and-privacy-assessment/grids.json?focus%5B%5D=vanta&focus%5B%5D=upguard-vendor-risk&focus%5B%5D=drata&focus%5B%5D=sprinto-inc&focus%5B%5D=secureframe&focus%5B%5D=scrut-automation&focus%5B%5D=ibm-openpages&focus%5B%5D=thoropass)

VendorReview.com

VendorReview.com positions itself as a streamlined solution for the vendor review process. The platform is designed to assist teams in efficiently determining vendor risk scores and providing comprehensive evidence to auditors. It emphasizes the ease of making informed and precise decisions, thereby enhancing the role of its users within their respective organizations.

Who Is the Company Behind VendorReview.com?

Vendor Risk Management Maturity Model (VRMMM)

The Vendor Risk Management Maturity Model (VRMMM is a comprehensive framework designed to help organizations assess and enhance their third-party risk management programs. By evaluating existing practices against industry benchmarks and best practices, the VRMMM enables organizations to identify areas for improvement, allocate resources effectively, and establish a baseline for program maturity. This model is particularly beneficial for organizations aiming to adapt their risk management strategies based on factors such as industry type, organizational size, and risk tolerance. Key Features and Functionality: - Program Governance: Establishes a risk management governance model with defined objectives, board reporting, and oversight, including considerations for ESG and codes of conduct. - Policies, Standards, and Procedures: Develops comprehensive policies for vendor risk management, including risk categorization, due diligence standards, and lifecycle management. - Contracts Management: Provides guidelines for contract provisions, relationship management, and procedures for vendor termination or exit. - Vendor Risk Assessment Process: Implements processes for pre-outsourcing risk evaluation, vendor risk tiering, ongoing assessments, and process automation. - Skills and Expertise: Defines roles and responsibilities, staffing levels, training programs, and qualifications necessary for effective risk management. - Communication and Information Sharing: Facilitates integration of vendor risk programs, reporting mechanisms, and communication protocols. - Tools, Measurement, and Analysis: Utilizes workflow management, risk scoring tools, financial analysis, and automation to monitor vendor risks. - Monitoring and Review: Establishes procedures for tracking contract provisions, monitoring service level agreements, and conducting continuous monitoring programs. Primary Value and Problem Solved: The VRMMM addresses the critical need for organizations to manage and mitigate risks associated with third-party vendors. By providing a structured approach to evaluate and improve vendor risk management programs, the VRMMM helps organizations make informed decisions regarding resource allocation and vendor-related risks. It enables the establishment of a maturity baseline, identification of high-value components, and tracking of program progress over time. Ultimately, the VRMMM empowers organizations to enhance their risk management capabilities, ensuring robust governance and compliance in their third-party relationships.

Who Is the Company Behind Vendor Risk Management Maturity Model (VRMMM)?

VendorSafe

VendorSafe automates security questionnaire responses for vendors and suppliers. It analyzes your company profile, maps answers to common frameworks (SIG Lite, CAIQ, SOC 2), and generates Word, PDF, and Excel exports ready to submit. Free tier available — no credit card required. Built by cybersecurity consultants who review vendor security assessments daily.

Who Is the Company Behind VendorSafe?

Venpo

Vendor legal documents change constantly, and almost no one reads the diff. Venpo tracks the Terms of Service, Privacy Policies, Data Processing Agreements, and subprocessor lists of the SaaS vendors you rely on, detects every change, and tells you what it actually means - in plain English, with a clear verdict on whether it matters. Built for lean teams that own vendor due diligence without a dedicated GRC function. Instead of quarterly manual reviews or finding out about a new subprocessor from a customer's security questionnaire, you get an alert the day it happens: what changed and why it matters. Venpo replaces manual ToS re-reading, ad-hoc diff checking, and "we'll catch it at renewal" as a vendor monitoring strategy.

Who Is the Company Behind Venpo?

  • Seller: Venpo
  • Year Founded: 2023
  • HQ Location: Miami, US
  • LinkedIn® Page: www.linkedin.com
    2 employees on LinkedIn®

ZeroRisk

ZeroRisk is a Done-for-You vendor risk and compliance platform for mid-market regulated firms in the EU, UK and US. Most compliance tools give you a dashboard and leave the work to you. ZeroRisk runs the work itself: an agent assesses each vendor clause by clause against the frameworks you're held to, gathers the evidence, and produces a verdict your team reviews and signs. Vendors are re-checked continuously, so the record stays current between audits rather than going stale the day after you finish. The same evidence base powers internal certification readiness, so you're not maintaining two separate programs. Scope your ISMS, upload what you already have, and the platform tells you what's missing and what still needs an owner. Covers ISO 27001:2022, SOC 2, GDPR, NIS2, DORA and the Cyber Resilience Act. Includes a vendor library of 10,000+ pre-monitored suppliers, an asset register, access reviews, a risk register, and audit-ready evidence packs you can hand straight to an assessor. Pricing is published, from $149/month. No sales call required to find out what it costs.

Who Is the Company Behind ZeroRisk?

  • Seller: ZeroRisk
  • Year Founded: 2025
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    2 employees on LinkedIn®
Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024