Best Managed Detection and Response (MDR) Software - Page 7

How Many Managed Detection and Response (MDR) Software Products Does G2 Track?

Total Products under this Category: 144

Category Stats (Sep 2026)

  • Average Rating: 4.48/5 (↑0.03 vs Aug 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Proficio (+77.78%) - Among all products in this category, Proficio recorded the largest rating increase compared to last month

Last updated: September 15, 2026

How Does G2 Rank Managed Detection and Response (MDR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 8,800+ Authentic Reviews
  • 144+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

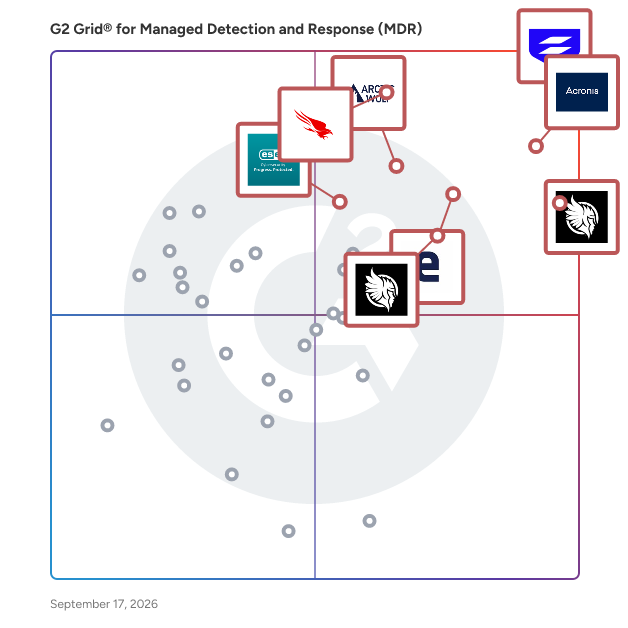
G2 Grid® for Managed Detection and Response (MDR) Software

G2 Grid® for Managed Detection and Response (MDR)  Software plotting products by satisfaction and market presence

Highlighted products: Sophos MDR, Acronis Cyber Protect Cloud, Huntress Managed EDR, CrowdStrike Falcon Endpoint Protection Platform, eSentire, Arctic Wolf, Huntress Managed ITDR, and ESET PROTECT.

Underlying data: [Grid® JSON](https://www.g2.com/categories/managed-detection-and-response-mdr/grids.json?focus%5B%5D=sophos-mdr&focus%5B%5D=acronis-cyber-protect-cloud&focus%5B%5D=huntress-managed-edr&focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=esentire&focus%5B%5D=arctic-wolf&focus%5B%5D=huntress-managed-itdr&focus%5B%5D=eset-protect)

Cybool

Cybool is a Next-Gen GRC platform that unifies risk management, policy governance, and compliance tracking into a single, intelligence-driven solution. The platform transforms raw security data into actionable insights, enabling organizations to maintain continuous compliance across frameworks such as NIS2, ISO 27001, SOC 2, and HIPAA. At its core, Cybool provides a centralized compliance tracker that consolidates progress across multiple regulatory frameworks in real-time. Security teams gain immediate visibility into control status, open risks, and overall compliance posture through a unified dashboard. This eliminates the fragmented view that traditional GRC tools typically offer. The platform features comprehensive policy management capabilities, supporting the entire lifecycle from drafting and distribution to review and employee acknowledgment. Organizations can maintain complete, auditable evidence of policy awareness and acceptance, satisfying regulatory requirements for documentation and training verification. Cybool automates evidence collection from cloud infrastructure, IT systems, and HR platforms. This reduces manual effort, minimizes human error, and ensures audit evidence remains current and readily accessible for both internal reviews and external audits. A distinctive element of the platform is its gamified remediation workflow. Tasks are automatically assigned to appropriate owners with clear deadlines and progress tracking. Leaderboards and scoring mechanisms increase engagement across teams, shorten remediation cycles, and improve accountability for security-related activities. The platform ingests proprietary threat intelligence, including infostealer logs and security feeds, normalizing and correlating this data to enhance risk assessments and incident response. This intelligence-led approach ensures compliance programs reflect current threat realities rather than static checklist assessments. Additional capabilities include cyber insurance gap analysis, which compares policy terms against security posture to identify coverage blind spots, and a tamper-resistant critical incident log for comprehensive event documentation and response tracking.

Who Is the Company Behind Cybool?

  • Seller: Cybool
  • Year Founded: 2020
  • HQ Location: Tel Aviv, IL
  • LinkedIn® Page: www.linkedin.com
    2 employees on LinkedIn®

Cybriant MDR

With MDR from Cybriant, our security analysts monitor your endpoints 24/7 and filter out false positives. You’ll receive the alerts when relevant threats are detected along with advice and insight from our cyber security team to help you mitigate and respond to the threat.

Who Is the Company Behind Cybriant MDR?

  • Seller: Cybriant
  • Year Founded: 2015
  • HQ Location: Alpharetta, GA
  • Twitter: @CybriantMSSP
    791 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    33 employees on LinkedIn®

Cyderes Managed Detection Response

Cyderes MDR helps organizations detect, investigate, and respond to threats using the technologies they already trust, while reducing the conditions that allow incidents to recur. Unlike traditional MDR services that operate within the limits of monitored tools or escalate alerts without sufficient context, Cyderes MDR is powered by Meridian. Meridian creates a continuously updated understanding of identities, assets, access, and risk across the environment by integrating signals from the broader ecosystem of security and operational tools, including systems beyond those actively monitored by MDR. This shared understanding helps prioritize threats based on identity relationships, blast radius, and environmental impact rather than isolated alerts or static severity. The result is faster response, stronger prioritization, and action that extends beyond containment to strengthen identity, exposure, and broader security programs over time.

Who Is the Company Behind Cyderes Managed Detection Response?

  • Seller: Cyderes
  • Year Founded: 2003
  • HQ Location: Kansas City, MO
  • Twitter: @Cyderes
    11,836 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    897 employees on LinkedIn®

Cythera

Managed Detection & Response

Who Is the Company Behind Cythera?

  • Seller: Cythera
  • Year Founded: 2023
  • HQ Location: Wellington, NZ
  • LinkedIn® Page: www.linkedin.com
    103 employees on LinkedIn®

Daylight AI-Powered MDR

Daylight is a security services company delivering Managed Agentic Security Services (MASS) for SecOps, including MDR, threat hunting, incident response, and more, through a fundamentally different architecture than traditional security services providers. Daylight's architecture combines an agentic platform that runs the full cycle from detection to response with security experts from IR and threat hunting backgrounds. The platform integrates deeply across your environment - cloud, identity, SaaS, endpoints - and collects identity and business context to investigate alerts the way a senior analyst would. It continuously learns your environment to make better decisions over time. Security experts validate decisions, feed insights into the platform, optimize detections, and take over in case of an incident. The result: security teams move from firefighting mode to strategic work that improves their security posture.

Who Is the Company Behind Daylight AI-Powered MDR?

Endpoint Defense Management 360 (EDM360)

Reveald’s Endpoint Defense Management 360° (EDM360°) subscription service is a comprehensive offering that includes continuous management and optimization of endpoint security technology that reduces the attack surface of commonly targeted systems inside and outside of the Client IT business environment. The platform as associated services are designed to reduce risk at the endpoint by maintaining operational security, maximum defensive posture, and agent health. Reveald includes continuous management and support through our Service Delivery team, including Client Success Management, evaluation, management, optimization, defensive hardening, performance reporting, and managed technology support.

Who Is the Company Behind Endpoint Defense Management 360 (EDM360)?

  • Seller: Reveald, Inc
  • Year Founded: 2015
  • HQ Location: New York, New Mexico, United States
  • Twitter: @RevealdCyber
    328 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    40 employees on LinkedIn®

enhanced.io

enhanced.io is a channel-only Open XDR SOCaaS built exclusively for MSPs, with 400+ integrations across endpoint, network, cloud, identity and IoT/OT. The service gives MSPs a full security operations center without the cost of building one. A 24/7 SOC team monitors, detects, investigates, and responds to threats across every client environment. A named Fractional Security Director works openly alongside the MSP, joining client calls and quarterly business reviews. enhanced.io replaces MDR and SOCaaS providers and integrates with the partner's existing stack. There is no rip and replace. MSPs keep the client relationship. enhanced.io never sells direct to end clients. The service is particularly well suited to MSPs serving regulated industries like healthcare, legal, and financial services, and IoT/OT-heavy sectors like manufacturing, building management, retail, and education. It is also applicable to clients of any size and shape. Coverage is worldwide.

Who Is the Company Behind enhanced.io?

  • Seller: enhanced.io
  • Year Founded: 2019
  • HQ Location: Edinburgh, United Kingdom
  • LinkedIn® Page: www.linkedin.com
    10 employees on LinkedIn®

Flarehawk

Flarehawk is a managed detection and response platform built exclusively for Cloudflare customers, delivering real-time threat visibility across HTTP traffic, WAF bypass attempts, Zero Trust identities, and admin activity—all the blind spots Cloudflare alone doesn't monitor. With ML-powered detection, analyst-verified alerts, and one-click mitigation, your team gets actionable security without building a SOC. Deploy in minutes with a single API token, retain logs for up to 5 years for compliance, and let our Aegis AI co-pilot translate complex incidents into plain-language insights. Starting at $299/month, Flarehawk gives lean teams and MSSPs enterprise-grade Cloudflare security monitoring—24/7 protection, zero headcount required.

Who Is the Company Behind Flarehawk?

Gordon

Gordon is an AI-powered cyber resilience platform built by Mitigata for regulated enterprises. It replaces multiple point solutions with one unified console covering SOC, VAPT, GRC, phishing simulation, third-party risk, brand monitoring, and cyber insurance. 𝗖𝗼𝗿𝗲 𝗰𝗮𝗽𝗮𝗯𝗶𝗹𝗶𝘁𝗶𝗲𝘀 𝗜𝗱𝗲𝗻𝘁𝗶𝗳𝘆 Discover and map all cyber assets across domains, IPs, subdomains, and mobile apps. Score employee cyber risk (0–100) using real behavior like phishing clicks, credential reuse, and unusual access patterns. Integrates with HRMS tools like Darwinbox, Keka, and SAP SuccessFactors. 𝗔𝘀𝘀𝗲𝘀𝘀 Continuous VAPT by CERT-In empanelled testers across web, API, cloud (AWS, Azure, GCP), network, and mobile. Third-party risk scoring using 200+ signals. Compliance mapped to RBI, SEBI, DPDP Act 2023, IRDAI, and CERT-In. Quantifies financial impact using FAIR methodology. 𝗠𝗶𝘁𝗶𝗴𝗮𝘁𝗲 Automated phishing simulations with multilingual templates. Risk-based microlearning and gamified training. Integrated cyber insurance from leading providers with posture-linked pricing, reducing premiums by up to 40%. 𝗠𝗼𝗻𝗶𝘁𝗼𝗿 24/7 SOC with AI-driven alert triage to reduce false positives. Full attack chain visibility mapped to MITRE ATT&CK. Automated CERT-In reporting within 6 hours. Continuous brand monitoring across dark web, domains, and social platforms with takedown support. 𝗪𝗵𝘆 𝗚𝗼𝗿𝗱𝗼𝗻 Gordon AI powers the platform with executive summaries, prioritised actions, anomaly alerts, and ready-to-share board reports. Built for BFSI, fintech, healthcare, SaaS, and manufacturing. Deploys in hours, not months. Starts at $1,787/month with a 15-day free trial.

Who Is the Company Behind Gordon?

  • Seller: Mitigata
  • Year Founded: 2021
  • HQ Location: Bangalore, IN
  • LinkedIn® Page: www.linkedin.com
    106 employees on LinkedIn®
  • Ownership: Private Limited
  • Phone: 7807153087

Gordon SOC Monitoring

Gordon SOC Monitoring provides continuous, 24/7 security monitoring of an organization's endpoints, network traffic, cloud environments, and identity systems, combining automated threat detection with human analyst review and response. The service ingests log and telemetry data from existing tools, including Microsoft 365, Google Workspace, firewalls, EDR agents, and cloud platforms, without requiring replacement of the customer's current security stack. Ingested data is correlated against threat intelligence feeds and behavioral baselines to identify anomalies, lateral movement, privilege escalation, and indicators of compromise. Automated triage filters out noise before escalating validated incidents to analysts, reducing the volume of alerts requiring human review. When a confirmed threat is identified, Gordon analysts investigate, document the incident's scope, and notify the designated customer contact with a plain-language summary of what happened, which systems are affected, and the recommended immediate containment steps. For customers who opt in to active response, analysts can execute containment actions, such as isolating endpoints or blocking accounts, directly, without requiring the customer to act first. Each customer receives a monthly report showing detected threats, response timelines, open risks, and trend data over the previous period. Reports are formatted for both technical and non-technical stakeholders, including IT managers and executives without a security background. Findings are mapped to SOC 2, NIST CSF, ISO 27001, HIPAA, and PCI DSS control requirements to support audit and compliance reporting. Gordon SOC Monitoring deploys without on-site hardware and integrates with existing environments via API connectors and log forwarding. Initial onboarding is completed without manual asset list uploads. The service auto-discovers monitored assets from the connected directory and cloud sources.

Who Is the Company Behind Gordon SOC Monitoring?

  • Seller: Mitigata
  • Year Founded: 2021
  • HQ Location: Bangalore, IN
  • LinkedIn® Page: www.linkedin.com
    106 employees on LinkedIn®
  • Ownership: Private Limited
  • Phone: 7807153087
Lauren Worth
LW
Researched and written by Lauren Worth
Updated July 23, 2025