Best Enterprise Exposure Management Platforms

How Many Exposure Management Platforms Products Does G2 Track?

Total Products under this Category: 79

Category Stats (Nov 2026)

  • Average Rating: 4.67/5 (↓0.02 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Topscan (+0.59%) - Among all products in this category, Topscan recorded the largest rating increase compared to last month

Last updated: November 12, 2026

How Does G2 Rank Exposure Management Platforms Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,800+ Authentic Reviews
  • 79+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

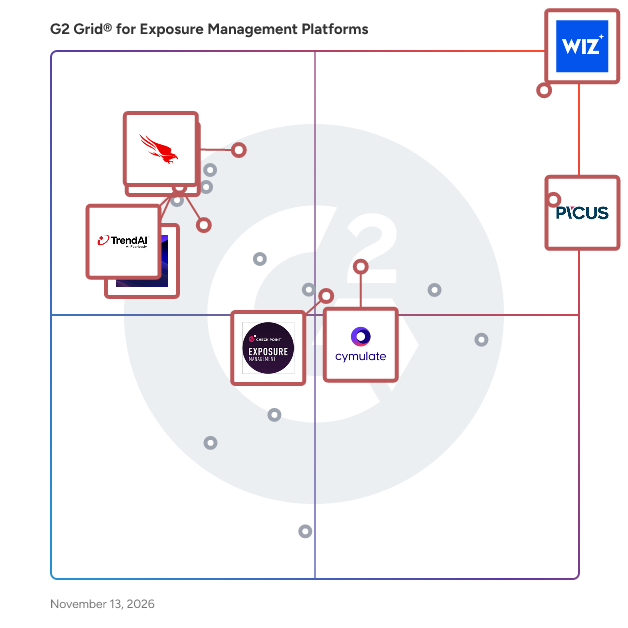
G2 Grid® for Exposure Management Platforms

G2 Grid® for Exposure Management Platforms plotting products by satisfaction and market presence

Highlighted products: Wiz, Picus Security, CrowdStrike Falcon Cloud Security, TrendAI Vision One, H1 Platform, Check Point Exposure Management, Cymulate, and Darktrace / HYBRID NETWORK.

Underlying data: [Grid® JSON](https://www.g2.com/categories/exposure-management-platforms/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=picus-security&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=trendai-vision-one&focus%5B%5D=h1-platform&focus%5B%5D=check-point-exposure-management&focus%5B%5D=cymulate&focus%5B%5D=darktrace-hybrid-network&segment=enterprise)

Wiz

Wiz transforms cloud security for customers – including more than 50% of the Fortune 100 – by enabling a new operating model. With Wiz, organizations can democratize security across the development lifecycle, empowering them to build fast and securely. Its Cloud Native Application Protection Platform (CNAPP) consolidates CSPM, KSPM, CWPP, Vulnerability management, IaC scanning, CIEM, DSPM into a single platform. Wiz drives visibility, risk prioritization, and business agility. Protecting Your Cloud Environments Requires a Unified, Cloud Native Platform. Wiz connects to every cloud environment, scans every layer, and covers every aspect of your cloud security - including elements that normally require installing agents. Its comprehensive approach has all of these cloud security solutions built in. Hundreds of organizations worldwide, including 50 percent of the Fortune 100, to rapidly identify and remove critical risks in cloud environments. Its customers include Salesforce, Slack, Mars, BMW, Avery Dennison, Priceline, Cushman & Wakefield, DocuSign, Plaid, and Agoda, among others. Wiz is backed by Sequoia, Index Ventures, Insight Partners, Salesforce, Blackstone, Advent, Greenoaks, Lightspeed and Aglaé. Visit https://www.wiz.io for more information.

Average Rating: 4.7/5.0

Total Reviews: 929

Who Is the Company Behind Wiz?

  • Seller: Google
  • Company Website:
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

Who Uses This Product?

  • Who Uses This: Security Engineer, CISO
  • Top Industries: Financial Services, Computer Software
  • Company Size: 54% Large, 37% Medium

What Do G2 Reviewers Say About Wiz?

AI-generated summary from verified user reviews

Pros
  • Users praise the user-friendly capabilities of Wiz, highlighting excellent service and reporting improvements.
  • Users value the enhanced security features of Wiz, benefiting from improved visibility and innovation in cloud security.
  • Users find Wiz to be incredibly easy to use, with a friendly interface and great support enhancing the experience.
  • Users value the enhanced visibility from Wiz, enabling efficient data security management and quick access to essential resources.
  • Users find the setup of Wiz to be easy and fast, enhancing their overall experience with its intuitive interface.
Cons
  • Users indicate that improvement is needed in reporting, alert tuning, and AI-related features for Wiz.
  • Users desire more features and consistency in Wiz to improve experience and enhance AI-related security capabilities.
  • Users find the learning curve steep, struggling with navigation and overwhelming popups in Wiz's interface.
  • Users highlight the need for improvements in reporting and additional capabilities in AI security and alert tuning.
  • Users find the complexity of the platform can be overwhelming, requiring significant effort to navigate and manage effectively.

What Are Recent G2 Reviews of Wiz?

Picus Security

Picus Security helps organizations continuously validate which exposures attackers can exploit, how far they can reach, and whether security controls can prevent or detect their attacks. The Picus Platform brings together Exposure Validation, Autonomous Penetration Testing, and Breach and Attack Simulation (BAS) in one coordinated program. Each validation method answers a different security question while sharing evidence across assets, exposures, identities, controls, and threats. Exposure Validation determines whether exposures are exploitable across affected assets, helping security teams prioritize remediation based on validated exploitability rather than vulnerability severity alone. Autonomous Penetration Testing chains real exploits from initial access through privilege escalation and lateral movement to uncover exploitable vulnerabilities and validate attack paths to critical assets. Breach and Attack Simulation safely runs real attacker techniques against live security controls to show whether attacks are prevented, detected, or missed. Instead of creating separate findings and priorities for each testing method, Picus uses a shared findings model that is deduplicated, evidence-backed, and asset-aware. This gives security teams shared context and a prioritized backlog for remediation and revalidation. Numi AI and Picus Swarm add an agentic layer across the platform. Specialist agents support discovery, exploitation, validation, mobilization, and reporting workflows. Organizations can run workflows on demand, under human supervision, or autonomously, with decision gates and audit trails that keep teams in control. Picus helps security teams move from scheduled security testing toward change-driven validation, so emerging vulnerabilities, new attack campaigns, security control changes, and infrastructure changes can trigger the right validation method. Teams can use the resulting evidence to prioritize proven risk, remediate or mitigate findings, and revalidate fixes.

Average Rating: 4.8/5.0

Total Reviews: 228

Who Is the Company Behind Picus Security?

  • Seller: Picus Security
  • Company Website:
  • Year Founded: 2013
  • HQ Location: San Francisco, California
  • LinkedIn® Page: www.linkedin.com
    317 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Cyber Security Specialist, Cyber Security Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 39% Large, 37% Medium

What Do G2 Reviewers Say About Picus Security?

AI-generated summary from verified user reviews

Pros
  • Users commend Picus Security for its deep integration and continuous threat simulation, enhancing proactive cybersecurity measures effectively.
  • Users find the intuitive and user-friendly interface of Picus Security enhances their overall security validation experience.
  • Users commend Continuous Validation in Picus Security, enhancing threat detection and security posture across infrastructure effortlessly.
  • Users value the actionable insights from Picus Security, enhancing proactive defense against evolving threats effectively.
  • Users value the seamless integration of Picus Security with existing tools, enhancing threat simulation and proactive defense strategies.
Cons
  • Users note the need for enhanced reporting customizability, particularly for management and compliance framework clarity.
  • Users face integration issues with Picus Security, making setup and navigation complex and time-consuming for teams.
  • Users find the steep learning curve of Picus Security challenging initially, particularly for those new to security validation.
  • Users find the complex setup of Picus Security to be time-consuming, especially in larger environments.
  • Users note the limited customization options, wishing for enhanced flexibility in reporting and simulation parameters.

What Are Recent G2 Reviews of Picus Security?

What Are G2 Users Discussing About Picus Security?

CrowdStrike Falcon Cloud Security

Crowdstrike Falcon Cloud Security is the only CNAPP to stop breaches in the cloud Built for today’s hybrid and multi-cloud environments, Falcon Cloud Security protects the entire cloud attack surface - from code to runtime - by combining continuous agentless visibility with real-time detection and response. At runtime, Falcon Cloud Security delivers best-in-class cloud workload protection and real-time cloud detection and response (CDR) to stop active threats across hybrid environments. Integrated with the CrowdStrike Falcon platform, it correlates signals across endpoint, identity, and cloud to detect sophisticated cross-domain attacks that point solutions miss—enabling teams to respond faster and stop breaches in progress. To reduce risk before attacks occur, Falcon Cloud Security also delivers agentless-driven posture management that proactively shrinks the cloud attack surface. Unlike typical solutions, Crowdstrike enriches cloud risk detections with adversary intelligence and graph-based context, enabling security teams to prioritize exploitable exposures and prevent breaches before they happen. Customers using Falcon Cloud Security consistently see measurable results: 89% faster cloud detection and response 100x reduction in false positives by prioritizing exploitable, business-critical risk 83% reduction in cloud security licenses due to elimination of redundant tools

Average Rating: 4.5/5.0

Total Reviews: 249

Who Is the Company Behind CrowdStrike Falcon Cloud Security?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Who Uses This: Analyst
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 52% Large, 31% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their protection in cloud environments.
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their cloud security management significantly.
  • Users value the real-time detection efficiency of CrowdStrike Falcon Cloud Security for enhanced cloud threat management.
  • Users value the real-time vulnerability detection of CrowdStrike Falcon Cloud Security, enhancing proactive risk management and security.
  • Users appreciate the ease of use of CrowdStrike Falcon Cloud Security, making it a top choice for cloud cybersecurity.
Cons
  • Users find CrowdStrike Falcon Cloud Security to be expensive, particularly challenging for small businesses with budget constraints.
  • Users face issues with alert fatigue and response lag, calling for improved prioritization and better support resources.
  • Users experience alert fatigue and desire improved response times and better training resources for CrowdStrike Falcon.
  • Users find the feature complexity of CrowdStrike Falcon Cloud Security can overwhelm new users and necessitate a learning curve.
  • Users report a challenging learning curve with CrowdStrike Falcon, especially for those unfamiliar with similar tools.

What Are Recent G2 Reviews of CrowdStrike Falcon Cloud Security?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

TrendAI Vision One

TrendAI Vision One is a cloud-native security operations platform, serving cloud, hybrid, and on-premises environments. It combines ASM and XDR in a single console to effectively manage cyber risk across your organization. The platform provides powerful risk insights, earlier threat detection, and automated risk and threat response options. Utilize the platform’s predictive machine learning and advanced security analytics for a broader perspective and advanced context. TrendAI Vision One integrates with its own expansive protection platform portfolio and industry-leading global threat intelligence, in addition to a broad ecosystem of purpose-built and API-driven third-party integrations.

Average Rating: 4.7/5.0

Total Reviews: 248

Who Is the Company Behind TrendAI Vision One?

  • Seller: TrendAI
  • Company Website:
  • Year Founded: 1988
  • HQ Location: Tokyo
  • LinkedIn® Page: www.linkedin.com
    7,996 employees on LinkedIn®
  • Ownership: OTCMKTS:TMICY

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 52% Large, 34% Medium

What Do G2 Reviewers Say About TrendAI Vision One?

AI-generated summary from verified user reviews

Pros
  • Users value the unified visibility of TrendAI Vision One, enhancing security operations and reducing alert fatigue effectively.
  • Users commend the unified visibility of TrendAI Vision One, enhancing security operations through effective threat detection and response.
  • Users appreciate the ease of use of TrendAI Vision One, enjoying its intuitive dashboard and seamless navigation.
  • Users appreciate the unified visibility of TrendAI Vision One, enhancing security operations across multiple platforms seamlessly.
  • Users value the powerful threat detection capabilities of TrendAI Vision One, enhancing security response and visibility.
Cons
  • Users find the complex interface of TrendAI Vision One overwhelming, affecting navigation and usability significantly.
  • Users report integration issues with TrendAI Vision One, leading to complexities with setup and third-party tools.
  • Users report a challenging learning curve with TrendAI Vision One, making onboarding difficult for new teams.
  • Users note the high cost of TrendAI Vision One compared to similar products, impacting overall value perception.
  • Users note the limited features of TrendAI Vision One, especially in reporting and dynamic dashboard capabilities.

What Are Recent G2 Reviews of TrendAI Vision One?

What Are G2 Users Discussing About TrendAI Vision One?

H1 Platform

HackerOne is a global leader in Continuous Threat Exposure Management (CTEM) and the only solution provider that pairs the simultaneous trust of the Fortune 500 and the world's largest community of security researchers to secure the AI-native enterprise. The H1 Platform unites agentic AI solutions with security researchers ingenuity to continuously discover, validate, prioritize, and remediate exposures across code, cloud, and AI systems. Through solutions like bug bounty, vulnerability disclosure, agentic pentesting, AI red teaming, and code security, HackerOne delivers measurable, continuous reduction of cyber risk for enterprises. Industry leaders, including Anthropic, Crypto.com, General Motors, Goldman Sachs, Lufthansa, Uber, UK Ministry of Defence, and the U.S. Department of Defense, trust HackerOne to safeguard their digital ecosystems. HackerOne was recognized in Gartner’s Emerging Tech Impact Radar: AI Cybersecurity Ecosystem report for its leadership in AI Security Testing.

Average Rating: 4.5/5.0

Total Reviews: 107

Who Is the Company Behind H1 Platform?

  • Seller: HackerOne
  • Company Website:
  • Year Founded: 2012
  • HQ Location: San Francisco, California
  • LinkedIn® Page: www.linkedin.com
    7,090 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 47% Large, 34% Medium

What Do G2 Reviewers Say About H1 Platform?

AI-generated summary from verified user reviews

Pros
  • Users highlight the ease of use of H1 Platform, making it simple to manage and track bounty programs effectively.
  • Users highlight the helpful customer service of HackerOne, ensuring effective assistance and smooth platform navigation.
  • Users value the seamless collaboration facilitated by H1 Platform, enhancing communication with security researchers and team members.
  • Users value the enhanced security protection of H1 Platform, facilitating proactive vulnerability management and team collaboration.
  • Users value the exceptional customer support of H1 Platform, enhancing their overall experience and program management.
Cons
  • Users find the complexity issues in triaging and credentials management to be a challenge, impacting overall efficiency.
  • Users note the expensive pricing of H1 Platform, which may challenge smaller organizations despite its value.
  • Users face time management challenges with inconsistent triage speed and quality, impacting overall efficiency on the H1 Platform.
  • Users experience poor customer support with long ticket resolutions and unresolved queries impacting their overall satisfaction.
  • Users find the poor interface design of H1 Platform confusing and difficult to navigate, often missing reports.

What Are Recent G2 Reviews of H1 Platform?

What Are G2 Users Discussing About H1 Platform?

Check Point Exposure Management

Exposure Management is changing how organizations react to vulnerabilities that put them in risk. Attackers exploit exposed assets, leaked credentials, and misconfigurations within hours using sophisticated AI attack tools. Meanwhile, security teams are left sorting through dashboards, alerts, and disconnected tools. For a limited time only, we are providing an Agentic Exposure Validation Scan at no cost. The scan delivers proven, evidence-backed findings your team can act on immediately. Request scan here - https://checkpoint.cyberint.com/limited-time-offer-aev-scan Check Point Exposure Management closes that gap by combining billions of external intelligence signals into a Unified Intelligence Fabric. The platform continuously identifies, validates, prioritizes, and safely remediates the exposures attackers are most likely to exploit. With Cyber Asset Attack Surface Management (CAASM), security teams gain a real-time inventory across cloud, SaaS, on-premises infrastructure, endpoints, and identities through 150+ agentless integrations. Unlike traditional vulnerability management, Check Point prioritizes exposures based on real-world exploitability, active threat intelligence, business context, and existing security controls, eliminating duplicate alerts and reducing remediation noise. It does so while maintaining business continuity. Safe-by-design remediation then validates every action before enforcement, enabling capabilities such as virtual patching, IPS activation, configuration hardening, and policy enforcement without disrupting business operations. Organizations using the platform achieve a 93% true positive rate on alerts, 12-hour average takedown MTTR, and 504 safe remediations per organization every month. Built around Gartner's Continuous Threat Exposure Management (CTEM) framework, Check Point helps organizations move from visibility to measurable risk reduction. Gartner predicts organizations adopting CTEM with mobilization will experience 50% fewer successful cyberattacks by 2028. Ready to see Exposure Management in action? Get a 15-minute demo: https://l.cyberint.com/exposure-management-demo

Average Rating: 4.6/5.0

Total Reviews: 198

Who Is the Company Behind Check Point Exposure Management?

Who Uses This Product?

  • Who Uses This: Cyber Security Analyst, Security Threat Analyst
  • Top Industries: Banking, Financial Services
  • Company Size: 66% Large, 21% Medium

What Do G2 Reviewers Say About Check Point Exposure Management?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Check Point Exposure Management, enabling quick data requests and straightforward setup.
  • Users value the fidelity of alerts and expert analysts, enhancing threat detection and remediation efficiency.
  • Users value the fidelity of alerts and experienced analysts, enabling timely remediation and proactive threat identification.
  • Users value the fidelity of alerts and expert remediation support from Check Point Exposure Management for proactive threat management.
  • Users value the quick and responsive customer support from Cyberint, enhancing their confidence in threat intelligence services.
Cons
  • Users experience inefficient alerts, facing repetitive notifications and high alert noise that complicates management efforts.
  • Users encounter false positives with Check Point Exposure Management, leading to confusion and redundant alerts in their experience.
  • Users report an inefficient alert system that generates excessive notifications, impacting overall usability and user experience.
  • Users notice integration issues with Check Point Exposure Management, limiting third-party tool compatibility and overall usability.
  • Users express concerns about the limited features of Check Point Exposure Management, particularly regarding alert tuning and integrations.

What Are Recent G2 Reviews of Check Point Exposure Management?

What Are G2 Users Discussing About Check Point Exposure Management?

Cymulate

Designed for security teams to continuously validate threats and build exposure-informed defenses, the Cymulate Platform combines advanced attack simulation with an agentic cyber defense engineering control plane to continuously prove, prioritize and adapt security controls for the latest threats. With a daily feed of threat intelligence and a comprehensive attack library, Cymulate is a SaaS offering that applies AI to tailor offensive testing to the environment while integrating with security stack to push updates for immediate prevention and detection. Core use cases include threat validation, control validation & tuning, detection engineering, and vulnerability validation and prioritization.

Average Rating: 4.9/5.0

Total Reviews: 177

Who Is the Company Behind Cymulate?

  • Seller: Cymulate
  • Company Website:
  • Year Founded: 2016
  • HQ Location: Holon, Israel
  • LinkedIn® Page: www.linkedin.com
    214 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Analyst, Cyber Security Engineer
  • Top Industries: Financial Services, Banking
  • Company Size: 56% Large, 42% Medium

What Do G2 Reviewers Say About Cymulate?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the intuitive and user-friendly design of Cymulate, enhancing accessibility for organizations of all sizes.
  • Users value the effective continuous security validation offered by Cymulate, enhancing their overall security posture.
  • Users appreciate Cymulate's effective vulnerability identification, enabling actionable insights and continuous threat assessment with ease.
  • Users value Cymulate's extensive customization options, benefiting from dynamic dashboards and a large threat library.
  • Users appreciate the helpful and friendly customer support of Cymulate, enhancing their overall experience and effectiveness.
Cons
  • Users note that dynamic reporting and integration stability need improvement for better execution and overall experience.
  • Users note that integration issues hinder Cymulate's effectiveness and call for enhanced compatibility with existing systems.
  • Users find reporting issues time consuming, with delays and a lack of critical data affecting efficiency.
  • Users note that advanced features can be complex to configure, making the initial setup time-consuming for newcomers.
  • Users find the inefficient alert system challenging, affecting real-time notifications and making assessments cumbersome to manage.

What Are Recent G2 Reviews of Cymulate?

Darktrace / HYBRID NETWORK

Darktrace / HYBRID NETWORK uses Adaptive AI to continuously learn behavior across your infrastructure, combining NDR, CDR, OT security, ITDR, exposure management, attack path modelling and forensic investigations into a single solution. - Unify visibility - Detect and contain known, novel and insider threats - AI-led triage and investigations - Increase resilience Named a Leader in the 2025 and 2026 Gartner® Magic Quadrant™ for NDR and the only Visionary in the 2025 Gartner® Magic Quadrant™ for CPS.

Average Rating: 4.4/5.0

Total Reviews: 48

Who Is the Company Behind Darktrace / HYBRID NETWORK?

  • Seller: Darktrace
  • Year Founded: 2013
  • HQ Location: Cambridgeshire, England
  • LinkedIn® Page: www.linkedin.com
    2,597 employees on LinkedIn®
  • Ownership: LON: DARK

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 61% Medium, 29% Large

What Do G2 Reviewers Say About Darktrace / HYBRID NETWORK?

AI-generated summary from verified user reviews

Pros
  • Users value the robust monitoring capabilities of Darktrace, enhancing visibility and confidence in network security.
  • Users appreciate the self-learning AI technology of Darktrace, enhancing security with real-time monitoring and automated responses.
  • Users commend the rapid and accurate threat detection of Darktrace, ensuring confidence and effective protection from cyber threats.
  • Users appreciate the responsive customer support of Darktrace, enhancing their learning and experience with the platform.
  • Users commend the autonomous AI capabilities of Darktrace for its proactive and effective threat detection and response.
Cons
  • Users face a significant initial learning curve with Darktrace, requiring extensive time investment for proper tuning and validation.
  • Users find Darktrace / HYBRID NETWORK to be expensive, especially for smaller organizations with limited security budgets.
  • Users often face alert issues during the learning phase, needing significant time and effort to manage false positives.
  • Users report that the complex setup of Darktrace requires significant engineering skills and ongoing management efforts.
  • Some users experience false positives, necessitating IT intervention to restore services and improve detection capabilities.

What Are Recent G2 Reviews of Darktrace / HYBRID NETWORK?

What Are G2 Users Discussing About Darktrace / HYBRID NETWORK?

CTM360

CTM360 is a consolidated external security platform that integrates External Attack Surface Management, Digital Risk Protection, Cyber Threat Intelligence, Brand Protection & Anti-phishing, Surface, Deep, & Dark Web Monitoring, Security Ratings, Third-party risk Management, and fully managed unlimited Takedowns. As a pioneer and innovator in preemptive security, CTM360 operates as an external CTEM technology platform outside an organization’s perimeter. Seamless and turn-key, CTM360 requires no configurations, installations or inputs from the end-user, with all data pre-populated and specific to your organization. All aspects are managed by CTM360.

Average Rating: 4.6/5.0

Total Reviews: 174

Who Is the Company Behind CTM360?

  • Seller: CTM360
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Manama, BH
  • LinkedIn® Page: www.linkedin.com
    136 employees on LinkedIn®
  • Phone: +97377360360

Who Uses This Product?

  • Top Industries: Banking, Financial Services
  • Company Size: 37% Medium, 37% Large

What Do G2 Reviewers Say About CTM360?

AI-generated summary from verified user reviews

Pros
  • Users value the responsive and reliable customer support of CTM360, enhancing their overall experience and satisfaction.
  • Users appreciate the ease of use of CTM360, finding its dashboard intuitive for all users, including executives.
  • Users value the seamless onboarding and efficient takedowns, appreciating CTM360's customer-centric approach and ease of use.
  • Users value the strong monitoring and efficient case handling, enhancing their cyber risk visibility and response capabilities.
  • Users value the high detection efficiency of CTM360, appreciating the minimal false positives and quick impersonation detection.
Cons
  • Users find CTM360 has limited features, lacking capabilities found on the web portal and needing additional tools for security.
  • Users face integration issues with CTM360, as it struggles to seamlessly connect with existing security infrastructures.
  • Users note a lack of features in CTM360, indicating a need for improvements and additional tools for better functionality.
  • Users are frustrated by the lack of integration with existing security tools, hindering effective automated security management.
  • Users note a significant lack of integrations with existing security infrastructure, limiting automated security workflows.

What Are Recent G2 Reviews of CTM360?

Pentera

Pentera is the category leader for Automated Security Validation, allowing every organization to test with ease the integrity of all cybersecurity layers, unfolding true, current security exposures at any moment, at any scale. Thousands of security professionals and service providers around the world use Pentera to guide remediation and close security gaps before they are exploited. Its customers include Casey's General Stores, Emeria, LuLu International Exchange, IP Telecom PT, BrewDog, City National Bank, Schmitz Cargobull, and MBC Group. Pentera is backed by leading investors such as K1 Investment Management, Insight Partners, Blackstone, Evolution Equity Partners, and AWZ. Visit https://pentera.io for more information.

Average Rating: 4.6/5.0

Total Reviews: 195

Who Is the Company Behind Pentera?

  • Seller: Pentera
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    460 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Government Administration, Computer & Network Security
  • Company Size: 52% Large, 34% Medium

What Do G2 Reviewers Say About Pentera?

AI-generated summary from verified user reviews

Pros
  • Users love the user-friendly UI of Pentera, which simplifies penetration testing and enhances overall efficiency.
  • Users value the effective vulnerability identification and remediation suggestions, enhancing their overall security posture.
  • Users appreciate the fully automated features of Pentera, noting its quick implementation and user-friendly interface.
  • Users value the responsive customer support of Pentera, enhancing overall satisfaction and efficiency in vulnerability management.
  • Users value the realistic testing capabilities of Pentera, enhancing company network security and response effectiveness.
Cons
  • Users find the reporting inadequate, lacking detail for enterprise-scale insights and missing multilingual support.
  • Users are disappointed with the lack of a robust RBAC system for effective user access control in Pentera.
  • Users desire improvements in handling false positives, but overall satisfaction remains high with current functionalities.
  • Users note that reporting lacks robustness, especially for enterprise-level insights and multilingual support.
  • Users express concerns about the missing features, such as insufficient vulnerabilities, limited RBAC, and lack of translation.

What Are Recent G2 Reviews of Pentera?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated