Best Dynamic Application Security Testing (DAST) Software - Page 5

How Many Dynamic Application Security Testing (DAST) Software Products Does G2 Track?

Total Products under this Category: 102

Category Stats (Oct 2026)

  • Average Rating: 4.58/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: HCL AppScan (+0.24%) - Among all products in this category, HCL AppScan recorded the largest rating increase compared to last month

Last updated: October 24, 2026

How Does G2 Rank Dynamic Application Security Testing (DAST) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 4,300+ Authentic Reviews
  • 102+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

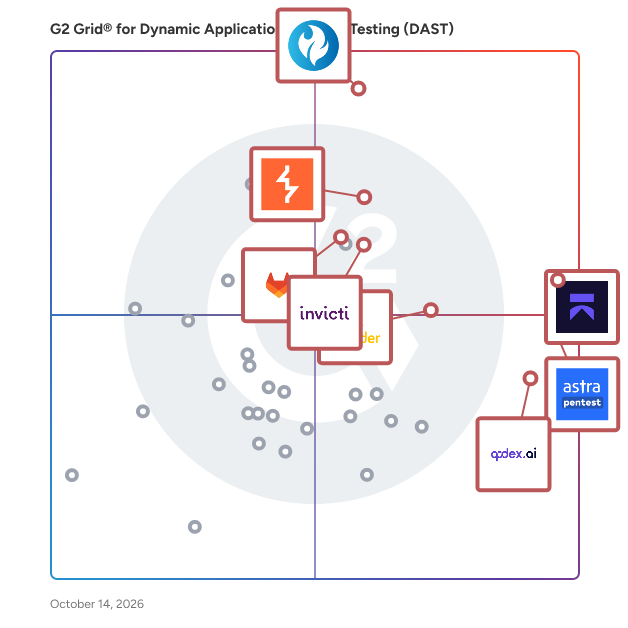
G2 Grid® for Dynamic Application Security Testing (DAST) Software

G2 Grid® for Dynamic Application Security Testing (DAST) Software plotting products by satisfaction and market presence

Highlighted products: HCL AppScan, Aikido Security, Astra Pentest, Burp Suite, Qodex.ai, Intruder, Invicti, and GitLab.

Underlying data: [Grid® JSON](https://www.g2.com/categories/dynamic-application-security-testing-dast/grids.json?focus%5B%5D=hcl-appscan&focus%5B%5D=aikido-security&focus%5B%5D=astra-pentest&focus%5B%5D=burp-suite&focus%5B%5D=qodex-ai&focus%5B%5D=intruder&focus%5B%5D=invicti&focus%5B%5D=gitlab)

esChecker MAST (SAST, DAST & IAST)

esChecker combines many years of penetration testing experience with a unique dynamic engine simulating attack techniques, such as reverse-engineering or code tampering. No source code is needed, only the app binary (Android apk or iOS ipa). esChecker provides immediate feedback about the way your app reacts against many hacking techniques. You can now spare your pentest budget for in-depth vulnerability analyses.

Average Rating: 4.3/5.0

Total Reviews: 2

Who Is the Company Behind esChecker MAST (SAST, DAST & IAST)?

  • Seller: eShard
  • Year Founded: 2015
  • HQ Location: Pessac, FR
  • LinkedIn® Page: www.linkedin.com
    47 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of esChecker MAST (SAST, DAST & IAST)?

Fluid Attacks

Implement Fluid Attacks' comprehensive, AI-powered solution into your SDLC and develop secure software without delays. As an all-in-one solution, Fluid Attacks accurately finds and helps you remediate vulnerabilities throughout the SDLC and ensures secure software development. The solution integrates its AI, automated tool, and team of pentesters to perform SAST, SCA, DAST, CSPM, SCR, PtaaS and RE to help you improve your security posture. This way, Fluid Attacks delivers accurate knowledge of the security status of your application. This means security goes alongside innovation without hindering your speed. Fluid Attacks provides you with expert knowledge about vulnerabilities and support options that enable you to remediate the security issues in your application.

Average Rating: 4.5/5.0

Total Reviews: 1

How Do G2 Users Rate Fluid Attacks?

  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.2/10)
  • API / Integrations: 10.0/10 (Category avg: 8.7/10)
  • Test Automation: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Fluid Attacks?

  • Seller: Fluid Attacks
  • Year Founded: 2001
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    181 employees on LinkedIn®
  • Phone: +14154042154

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Fluid Attacks?

HackZero

HackZero is a security and compliance platform in the same category as Vanta, Drata and Secureframe, with the two things they leave you to buy separately already in the package: a real, continuous penetration test, and an independent CPA who issues the attestation. The usual path to SOC 2 Type 2 is three vendors. A compliance platform for the paperwork, a separate firm for the pentest, and an auditor at the end, wired together by you. HackZero runs all three as one motion. The platform collects and maps your evidence to the SOC 2 Trust Services Criteria itself, so you do not need Vanta, Drata or Secureframe alongside it. If you already run one, our pentest report drops straight in as evidence there. The penetration test is not a separate purchase: we test your live app continuously with AI agents, and hackers in the loop confirm every finding actually exploits, with each one pre-mapped to the control it satisfies. The same evidence is formatted for HIPAA, PCI DSS 4.0 and ISO 27001:2022 when you need those. We do not sell the audit. An independent AICPA-member CPA issues the SOC 2 opinion and you pay them directly, which is what keeps the attestation independent and keeps us out of the audit-mill category. A first SOC 2 Type 2 lands around $6,000 all-in, against the $30,000 to $45,000 a separate platform, pentest and auditor cost. Our pricing is public, our benchmark results are public, and our vulnerability research is public and credited, including a critical RCE in velocity.js (CVSS 9.8) and a Function-constructor escape in JSONPath-Plus, so our claim of real security depth is one you can verify.

Average Rating: 4.8/5.0

Total Reviews: 2

How Do G2 Users Rate HackZero?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind HackZero?

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of HackZero?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Nexora Cyber

Nexora is an automated Dynamic Application Security Testing platform designed to help you find web vulnerabilities before they become real incidents. You scan your web applications and APIs continuously. Nexora identifies security risks based on OWASP Top 10, assigns clear risk scores, and shows you what needs to be fixed first.

Average Rating: 4.5/5.0

Total Reviews: 1

How Do G2 Users Rate Nexora Cyber?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Test Automation: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Nexora Cyber?

Who Uses This Product?

  • Company Size: 100% Small

What Do G2 Reviewers Say About Nexora Cyber?

AI-generated summary from verified user reviews

Pros
  • Users find the easy setup of Nexora Cyber ideal for teams managing web apps without extensive resources.

What Are Recent G2 Reviews of Nexora Cyber?

ProjectDiscovery

ProjectDiscovery is the team behind Nuclei, httpx, and subfinder, open-source tools used by more than 100,000 security professionals. Ten billion scans later, we know the difference between a finding and an exploit. Neo puts that toolkit in the hands of AI agents that test like an attacker, including behind login, and prove each finding with a working payload, reproduction steps, and a fix written for your code. It covers attack surface discovery, web app testing, PR-level security reviews, and regression testing that confirms your fixes held.

Average Rating: 5.0/5.0

Total Reviews: 4

How Do G2 Users Rate ProjectDiscovery?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • API / Integrations: 10.0/10 (Category avg: 8.7/10)
  • Detection Rate: 10.0/10 (Category avg: 8.8/10)
  • Test Automation: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind ProjectDiscovery?

  • Seller: ProjectDiscovery
  • Company Website:
  • Year Founded: 2020
  • HQ Location: San Francisco, US
  • Twitter: @pdiscoveryio
    41,738 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    50 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 75% Large, 25% Medium

What Do G2 Reviewers Say About ProjectDiscovery?

AI-generated summary from verified user reviews

Pros
  • Users commend the excellent customer support from ProjectDiscovery, ensuring swift assistance and attentiveness to feedback.
  • Users find ProjectDiscovery's platform remarkably easy to use, enabling quick integration and immediate value in vulnerability management.
  • Users find the onboarding process incredibly simple, enabling quick integration and immediate value in vulnerability management.
  • Users value the accuracy of results from ProjectDiscovery, which enhances threat detection and overall security posture.
  • Users value the seamless cloud integration of ProjectDiscovery, enhancing vulnerability management and asset discovery effortlessly.
Cons
  • Users feel the dashboard issues limit functionality, especially for complex security ecosystems needing broader feature sets.
  • Users express concerns about inadequate analytics in ProjectDiscovery, limiting insights within complex security environments.
  • Users note integration issues with ProjectDiscovery, especially within complex security environments, limiting its overall effectiveness.
  • Users note the limited features of ProjectDiscovery, particularly compared to larger enterprise solutions, impacting overall utility.
  • Users feel the limited features of ProjectDiscovery may not meet the needs of complex security environments.

What Are Recent G2 Reviews of ProjectDiscovery?

SAMI

Assisted by AI, SAMI (Security Automated by Machine Intelligence) simplifies cyber related financial and operational risk management. Demonstrably reducing risk, saving cost, enhancing ROI, streamlining process and increasing revenue for our customers.

Average Rating: 5.0/5.0

Total Reviews: 1

Who Is the Company Behind SAMI?

  • Seller: Autnhive
  • Year Founded: 2018
  • HQ Location: Oakville, CA
  • LinkedIn® Page: www.linkedin.com
    37 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of SAMI?

SmartScanner

SmartScanner is an AI-powered web vulnerability scanner designed to enhance the security of websites and applications. It offers features such as comprehensive vulnerability detection, support for various technologies, and a user-friendly interface that automates dynamic application security testing (DAST). Targeting a wide range of clients needing web security, SmartScanner provides detailed reports and flexible pricing options, making it a budget-friendly choice for organizations of all sizes. With its adaptive intelligence, it ensures optimal results tailored to the unique characteristics of each website.

Average Rating: 5.0/5.0

Total Reviews: 1

Who Is the Company Behind SmartScanner?

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of SmartScanner?

VulnSign

VulnSign is help to organizations enhance their cybersecurity posture and protect their web applications from potential threats. Our intuitive, user-friendly platform allows users to quickly and easily scan their web applications for vulnerabilities that could be exploited by cybercriminals. VulnSign is designed to easy to use, yet powerful enough to identify potential vulnerabilities in your web-based systems. Our team of security experts is constantly working to improve and update our DAST application, ensuring that it stays at the forefront of the cybersecurity industry.

Average Rating: 5.0/5.0

Total Reviews: 1

Who Is the Company Behind VulnSign?

  • Seller: VulnSign
  • Year Founded: 2022
  • HQ Location: West Hollywood, US
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of VulnSign?

Appvigil

Appvigil is a completely automated Mobile Reputation Protection Suite for Mobile Apps.Powered by patent pending technology, Appvigil employs intensive static, dynamic & stringent network analysis.

Who Is the Company Behind Appvigil?

  • Seller: Appvigil
  • HQ Location: Seattle, US
  • Twitter: @appvigil_co
    438 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

ArgosX

ArgosX independently checks what your AI app builder missed. It finds the security flaws in apps built with Lovable, Bolt, Replit, v0 or a custom stack, proves how each one happens, and gives you a fix you can paste straight back into your builder. A free scan checks what any visitor can already reach: leaked AI and service keys in your pages and JavaScript bundles, a database readable while logged out, missing security headers, cookies and TLS issues, accessibility, SEO and broken links. Paid scans sign in with a test account and use your app like a customer, testing each role you give them, which is where most real problems hide, such as one user being able to load another user's records. Every report rolls security, functionality, UX, accessibility and performance into one VibeScore with worst-first findings, reproduction steps and a shareable trust card. The Human-Verified tier adds a person on the team for UX and edge cases. ArgosX never enters real payment details or moves real money in your app.

Who Is the Company Behind ArgosX?

Bugsmirror MASST (Mobile Application Security Suite & Tools)

Bugsmirror Mobile Application Security Suite & Tools (MASST) is designed specifically for your business, providing scalable, end-to-end security for your mobile app. From detection to protection, MASST ensures your app is safeguarded against evolving security threats. With MASST, you can focus on growing your business, knowing your app is fully protected at every stage.

Who Is the Company Behind Bugsmirror MASST (Mobile Application Security Suite & Tools)?

CloneGuard

CloneGuard by Clone Systems is a security testing and compliance platform for merchants, MSPs, payment providers and growing businesses. Clone Systems has delivered managed security since 1998 and has been a PCI SSC Approved Scanning Vendor (ASV) since 2007. What CloneGuard includes: - PCI ASV Scanning: quarterly external ASV scans, free rescans until you pass, and a downloadable Attestation of Compliance. Buy online and scan the same day. - Vulnerability Scanning: external, internal, agent-based and authenticated web application scanning, all managed in one portal. - Automated Penetration Testing: buy online and launch the same day. Safe exploit validation, internal and external coverage, MITRE ATT&CK mapped findings and audit-ready reports. - Managed Penetration Testing: engineer-led, remote testing of web applications, APIs, cloud (AWS, Azure, GCP), internal networks and Active Directory, external networks, mobile apps and wireless, plus red team and source code review. Every engagement includes a hand-written report and a free remediation retest. - Managed Security: 24/7 US-based SOC, SIEM and endpoint protection, intrusion prevention and AI-assisted alert triage. - CloneGuard AI Assistant: AI-guided remediation for every finding. - White-Label Program: resell PCI ASV scanning under your own brand, with optional add-on modules. Reports support PCI DSS 4.0.1, HIPAA, SOC 2, ISO 27001, FedRAMP and cyber insurance requirements.

Who Is the Company Behind CloneGuard?

  • Seller: Clone Systems
  • Year Founded: 1998
  • HQ Location: Philadelphia, US
  • Twitter: @CloneSystemsInc
  • LinkedIn® Page: www.linkedin.com
    20 employees on LinkedIn®

Conviso

The Conviso Platform is a complete Application Security Posture Management (ASPM) solution that centralizes visibility, correlation, and prioritization of vulnerabilities across the software development lifecycle. It integrates with your existing SAST, DAST, SCA, IaC, and CI/CD tools, automates triage, and provides a unified view of risk — helping security and development teams work together to reduce complexity and strengthen AppSec maturity.

Who Is the Company Behind Conviso?

depthfirst

depthfirst is an AI-native security platform offering continuous cyber defense. It reasons through code, infrastructure, and business logic to understand how systems work and build a threat model. That context helps depthfirst find and verify vulnerabilities, prioritize what is exploitable, block malicious dependencies, and help teams remediate security issues. The platform covers three broad areas: Code Security reviews repositories and pull requests for vulnerabilities, secrets, insecure dependencies, and business-logic flaws. It connects findings to application context so security and engineering teams can focus on the issues that matter and fix them in the code. Agentic Pentesting uses autonomous agents to attack running applications like a team of elite security researchers. It supports black-, gray-, and white-box testing for new vulnerability discovery, but can also confirm whether code scan findings are exploitable and replay attacks to verify that fixes work. Dependency Firewall blocks malicious packages before installation to prevent supply chain attacks. It applies a shared security policy at the artifact-repository layer and on managed devices, protecting both people and AI agents. depthfirst routes each task to the best-suited AI model to optimize performance and cost. It also includes dfs-large1, depthfirst’s own frontier cybersecurity model, which performs comparably to frontier general-purpose models on vulnerability detection tasks at a fraction of the cost. depthfirst works with enterprises such as ServiceNow, government agencies, and innovative AI and fintech companies including Lovable, Supabase, Ripple, Listen Labs, fal, and MoonPay.

Who Is the Company Behind depthfirst?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024