Top Free Dynamic Application Security Testing (DAST) Software - Page 3

How Many Dynamic Application Security Testing (DAST) Software Products Does G2 Track?

Total Products under this Category: 100

Category Stats (Oct 2026)

  • Average Rating: 4.58/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Astra Pentest (+0.28%) - Among all products in this category, Astra Pentest recorded the largest rating increase compared to last month

Last updated: October 14, 2026

How Does G2 Rank Dynamic Application Security Testing (DAST) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 4,300+ Authentic Reviews
  • 100+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

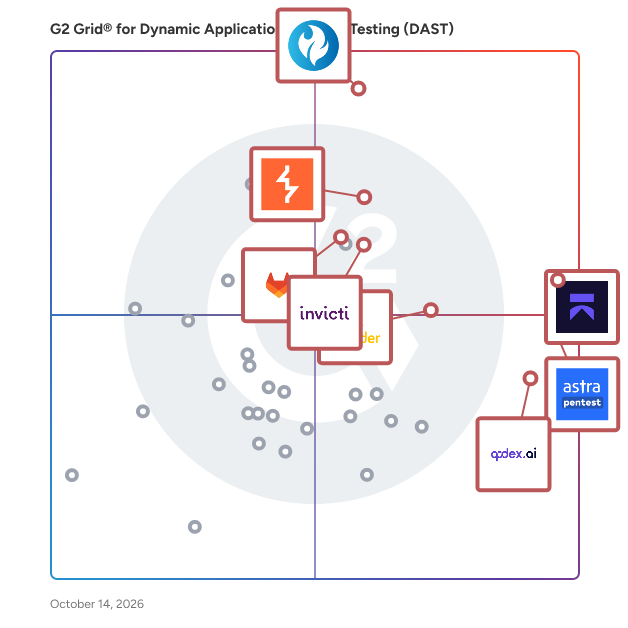
G2 Grid® for Dynamic Application Security Testing (DAST) Software

G2 Grid® for Dynamic Application Security Testing (DAST) Software plotting products by satisfaction and market presence

Highlighted products: HCL AppScan, Aikido Security, Astra Pentest, Burp Suite, Qodex.ai, Intruder, Invicti, and GitLab.

Underlying data: [Grid® JSON](https://www.g2.com/categories/dynamic-application-security-testing-dast/grids.json?focus%5B%5D=hcl-appscan&focus%5B%5D=aikido-security&focus%5B%5D=astra-pentest&focus%5B%5D=burp-suite&focus%5B%5D=qodex-ai&focus%5B%5D=intruder&focus%5B%5D=invicti&focus%5B%5D=gitlab)

OX Security

OX rewires your security program for the Mythos Age: the era where AI writes the code, chains the exploits, and moves faster than human-built defenses can track. OX is an AI Native Application Protection Platform (AINAPP) unifying security from Prompt to Runtime. It moves your control surface upstream to the prompt, preventing and governing risk at the source instead of chasing it downstream in runtime. OX Mind and OX AI Context Lake connect AI-user governance, code security, cloud and runtime enforcement, and agentic pentesting into one system that shares context across the entire Agentic Development Lifecycle (ADLC), replacing fragmented point tools with a single platform. The platform runs on four connected pillars: OX VibeSec: Prevents unsafe AI decisions at the point of creation and governs every AI user in the organization, not just developers using coding assistants. Full visibility into which agents, MCPs, skills, and packages run, with what permissions, against what data. OX Code: Separates exploitable risk from theoretical noise using evidence from your actual deployment, threat model, and threat intelligence. OX Cloud: Prevents misconfigurations and enforces runtime boundaries that code and agents cannot cross, watching what actually runs in production. OX Agentic Pentester: Continuously simulates adversarial agent behavior to prove exploit paths back to their exact source, feeding what it finds back into OX VibeSec to sharpen governance. OX connects to your existing stack and traces every finding back to its origin (the prompt, the AI user, or the endpoint that created it), then fixes issues at the source rather than flagging them after the fact. For new deployments, OX consolidates governance, code security, cloud enforcement, and pentesting into one platform. For existing stacks, OX layers governance on top and makes current tools smarter through continuous learning, so the same issue never gets created twice. Visit https://ox.security for more information.

Average Rating: 4.8/5.0

Total Reviews: 51

How Do G2 Users Rate OX Security?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.2/10)

Who Is the Company Behind OX Security?

Who Uses This Product?

  • Who Uses This: Security Engineer
  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 63% Medium, 25% Large

What Do G2 Reviewers Say About OX Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the intuitive dashboard of OX Security, enhancing issue management and streamlining security processes effectively.
  • Users find OX Security highly user-friendly, benefiting from an intuitive dashboard and responsive support for seamless operations.
  • Users value the responsive and professional customer support of OX Security, enhancing their overall experience and efficiency.
  • Users value the seamless integration support from OX Security, enhancing their workflow with fast and user-friendly solutions.
  • Users appreciate the comprehensive security capabilities of OX Security, ensuring a streamlined and effective security management experience.
Cons
  • Users report integration issues with OX Security's limited documentation and insufficient support for various tools.
  • Users note some missing features in OX Security, which can affect its overall usability and integration capabilities.
  • Users find the complexity of OX Security daunting, with inadequate documentation and a steep learning curve for new users.
  • Users find OX Security's inadequate reporting limits their ability to effectively showcase security progress to management.
  • Users find the limited cloud integration with certain tools frustrating, impacting overall connectivity and functionality.

What Are Recent G2 Reviews of OX Security?

Cyber Chief

Cyber Chief is a vulnerability scanner & issue management tool that helps you ship software with zero known security vulnerabilities. It gives your software team the power to find and fix thousands of vulnerabilities in your web applications and cloud infrastructure. With its one-click vulnerability scanning and smart vulnerability management features, Cyber Chief will help your software team secure their applications abs infrastructure, even if there is zero application security qualifications or experience on the team. Cyber Chief is cloud-based and has military-grade security controls so that your security secrets are kept safe.

Average Rating: 4.5/5.0

Total Reviews: 7

How Do G2 Users Rate Cyber Chief?

  • Has the product been a good partner in doing business?: 7.8/10 (Category avg: 9.2/10)
  • Detection Rate: 8.3/10 (Category avg: 8.8/10)
  • Test Automation: 6.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Cyber Chief?

  • Seller: Audacix
  • Year Founded: 2015
  • HQ Location: Melbourne, Victoria
  • LinkedIn® Page: www.linkedin.com
    14 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 43% Medium, 43% Small

What Do G2 Reviewers Say About Cyber Chief?

AI-generated summary from verified user reviews

Pros
  • Users value the automated scanning capabilities of Cyber Chief, streamlining security testing across all platforms effectively.
  • Users appreciate the responsive customer support of Cyber Chief, which ensures thorough assistance throughout their security journey.
  • Users appreciate the comprehensive cybersecurity solutions of Cyber Chief, ensuring thorough testing and support in one platform.
  • Users praise Cyber Chief for its comprehensive vulnerability detection, streamlining security testing within a single, user-friendly platform.
  • Users appreciate the vulnerability identification capability of Cyber Chief, enhancing security and collaboration across platforms.

What Are Recent G2 Reviews of Cyber Chief?

What Are G2 Users Discussing About Cyber Chief?

ZeroThreat

ZeroThreat Inc. is an AI-driven cybersecurity innovator dedicated to transforming how modern enterprises protect their web applications and APIs through its advanced platform. We empower organizations, from fast-growing startups to global enterprises, to stay ahead of evolving threats by delivering continuous, attacker-style penetration testing at the speed of modern development. Our mission is to eliminate the noise and complexity of traditional application security. By pioneering an Agentic AI engine and automated penetration testing platform, ZeroThreat.ai enables security teams to automate complex manual processes, reducing manual pentesting effort by 90% while achieving a 99.9% accuracy rate. It doesn't just scan for vulnerabilities. It validates real-world attack paths and provides audit-ready evidence, ensuring that organizations in highly regulated sectors such as Fintech, Healthcare, and Government can scale securely and maintain compliance. ZeroThreat.ai bridges the gap between developers and security teams by providing proof-based findings and actionable remediation guidance. We are committed to restoring developer trust through non-destructive, intelligent validation that focuses exclusively on exploitable risks, allowing businesses to ship software up to 10x faster without compromising security.

Average Rating: 4.8/5.0

Total Reviews: 10

How Do G2 Users Rate ZeroThreat?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • API / Integrations: 10.0/10 (Category avg: 8.7/10)
  • Detection Rate: 8.3/10 (Category avg: 8.8/10)
  • Test Automation: 5.0/10 (Category avg: 8.8/10)

Who Is the Company Behind ZeroThreat?

Who Uses This Product?

  • Company Size: 50% Large, 30% Medium

What Do G2 Reviewers Say About ZeroThreat?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of ZeroThreat, enjoying smooth integration and a user-friendly interface for security management.
  • Users value the real-time vulnerability detection of ZeroThreat, enhancing security without disrupting workflow and reducing false positives.
  • Users commend the accuracy of results from ZeroThreat, significantly reducing false positives and enhancing security efficiency.
  • Users appreciate the setup ease of ZeroThreat, enabling quick integration into existing workflows without complications.
  • Users appreciate the easy setup of ZeroThreat, allowing quick integration and immediate security scanning in their workflow.
Cons
  • Users find the inefficient filtering in ZeroThreat's reporting section makes locating specific results unnecessarily time-consuming.
  • Users experience integration issues with ZeroThreat, finding it challenging to connect with DevOps tools and proprietary software.
  • Users feel that the limited integrations with other tools hinder a more seamless experience with ZeroThreat.
  • Users report slow performance in ZeroThreat, with lagging features and longer loading times affecting productivity.
  • Users note that the UX improvement in ZeroThreat is needed for better navigation, filtering, and faster loading times.

What Are Recent G2 Reviews of ZeroThreat?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Siemba

Siemba is an AI-driven Continuous Threat Exposure Management (CTEM) platform that helps enterprises, government agencies, and growing organizations discover, prioritize, and fix critical vulnerabilities across their entire attack surface. Security teams use Siemba to build and mature CTEM programs without requiring deep hacking expertise or constant human intervention. The platform brings together four integrated capabilities on a single unified interface: Penetration Testing as a Service (PTaaS) for expert-led manual pen testing on demand; GenPT for AI-native Dynamic Application Security Testing (DAST) that simulates real-world attack techniques against web applications and APIs; GenVA for AI-driven vulnerability assessment that continuously scans and scores risks across your environment; and EASM for External Attack Surface Management that maps and monitors all external-facing assets, including shadow IT and exposed infrastructure. Together these capabilities deliver actionable intelligence across the full CTEM lifecycle, from asset discovery and attack surface mapping through to risk prioritization, validation, and remediation guidance. Security leaders gain the visibility, speed, and scalability needed to run continuous offensive security programs and generate strategic insights that maximize Return on Mitigation. Siemba is trusted by enterprises, global systems integrators, and government agencies looking to consolidate their offensive security tooling, reduce exposure windows, and demonstrate measurable security improvement over time.

Average Rating: 4.7/5.0

Total Reviews: 5

How Do G2 Users Rate Siemba?

  • API / Integrations: 10.0/10 (Category avg: 8.7/10)

Who Is the Company Behind Siemba?

  • Seller: Siemba
  • Year Founded: 2018
  • HQ Location: Alpharetta, US
  • LinkedIn® Page: www.linkedin.com
    38 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 60% Small, 40% Medium

What Are Recent G2 Reviews of Siemba?

Semgrep

Semgrep is a modern static analysis (SAST), software composition analysis (SCA), and secrets detection platform designed for both developers and security teams. It combines fast, deterministic analysis with context-aware AI that triages findings like a senior security engineer. The AI Assistant helps reduce false positives, prioritize meaningful results, and offers clear remediation guidance. Its “Memories” feature learns from past decisions to further reduce triage noise over time. Semgrep also supports deep analysis of transitive dependencies, not just direct ones, helping teams surface and address hidden risks in their supply chain. It integrates well into modern development workflows and is easy to customize across environments.

Average Rating: 4.6/5.0

Total Reviews: 56

How Do G2 Users Rate Semgrep?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)

Who Is the Company Behind Semgrep?

  • Seller: Semgrep
  • Year Founded: 2017
  • HQ Location: San Francisco, US
  • Twitter: @semgrep
    4,433 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    265 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 45% Large, 43% Medium

What Do G2 Reviewers Say About Semgrep?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Semgrep, enabled by its intuitive syntax and smooth integration with CI/CD.
  • Users appreciate the flexibility and speed of Semgrep in enforcing coding standards and catching vulnerabilities effectively.
  • Users appreciate the effective vulnerability detection of Semgrep, facilitating quick identification and resolution of security issues.
  • Users appreciate the scanning efficiency of Semgrep, benefiting from rapid scans and streamlined CI/CD integration.
  • Users value Semgrep for its effective security vulnerability detection, enabling quick resolutions without hindering development speed.
Cons
  • Users find Semgrep not user-friendly due to a steep learning curve and complex initial setup requirements.
  • Users find the limited features of Semgrep restrict its usability and complicate effective vulnerability management.
  • Users find the difficult learning curve for Semgrep daunting, especially for creating advanced rules and setups.
  • Users express concerns about the lack of guidance in creating custom rules, complicating effective use of Semgrep.
  • Users note a steep learning curve for Semgrep's rule syntax, making it challenging for newcomers to master.

What Are Recent G2 Reviews of Semgrep?

Crashtest Security

Crashtest Security is a SaaS-based security vulnerability scanner allowing agile development teams to ensure continuous security before every release. Our state-of-the-art dynamic application security testing (DAST) solution integrates seamlessly with your dev environment and protects multi-page and JavaScript apps, as well as microservices and APIs. Set up Crashtest Security Suite in minutes, get advanced crawling options, and automate your security. Whether you want to see vulnerabilities within the OWASP Top 10 or you want to go for deep scans, Crashtest Security is here to help you stay on top of your security and protect your code and customers.

Average Rating: 5.0/5.0

Total Reviews: 2

How Do G2 Users Rate Crashtest Security?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • API / Integrations: 10.0/10 (Category avg: 8.7/10)
  • Test Automation: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Crashtest Security?

Who Uses This Product?

  • Company Size: 50% Medium, 50% Small

What Are Recent G2 Reviews of Crashtest Security?

esChecker MAST (SAST, DAST & IAST)

esChecker combines many years of penetration testing experience with a unique dynamic engine simulating attack techniques, such as reverse-engineering or code tampering. No source code is needed, only the app binary (Android apk or iOS ipa). esChecker provides immediate feedback about the way your app reacts against many hacking techniques. You can now spare your pentest budget for in-depth vulnerability analyses.

Average Rating: 4.3/5.0

Total Reviews: 2

Who Is the Company Behind esChecker MAST (SAST, DAST & IAST)?

  • Seller: eShard
  • Year Founded: 2015
  • HQ Location: Pessac, FR
  • LinkedIn® Page: www.linkedin.com
    47 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of esChecker MAST (SAST, DAST & IAST)?

Bugsmirror MASST (Mobile Application Security Suite & Tools)

Bugsmirror Mobile Application Security Suite & Tools (MASST) is designed specifically for your business, providing scalable, end-to-end security for your mobile app. From detection to protection, MASST ensures your app is safeguarded against evolving security threats. With MASST, you can focus on growing your business, knowing your app is fully protected at every stage.

Who Is the Company Behind Bugsmirror MASST (Mobile Application Security Suite & Tools)?

Oversecured

Enterprise vulnerability scanner for Android and iOS apps. It offers app owners and developers the ability to secure each new version of a mobile app by integrating Oversecured into the development process.

Who Is the Company Behind Oversecured?

Panoptic Scans - Network and Application Vulnerability Scans

Panoptic Scans is a hosted vulnerability scanning platform designed to bolster cybersecurity for businesses by offering automated, comprehensive network and application vulnerability scans. Our platform empowers users to schedule vulnerability scans - daily, weekly, monthly, or annually - to ensure compliance with stringent regulations like SOC 2, HIPAA, ISO 27001, NIST 800-53, CMMC, and GDPR. Leveraging powerful tools such as OpenVAS for network vulnerabilities, OWASP ZAP for application security, and Nmap for port scanning, Panoptic Scans identifies weaknesses like unpatched software, misconfigurations, and open ports that could be exploited by cyber threats. With features like email notifications, detailed scan reports, and a user-friendly API, it simplifies vulnerability management, making it ideal for SaaS companies, security teams, and agile development environments aiming to safeguard sensitive data and maintain robust compliance effortlessly.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Panoptic Scans - Network and Application Vulnerability Scans?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • API / Integrations: 10.0/10 (Category avg: 8.7/10)
  • Detection Rate: 8.3/10 (Category avg: 8.8/10)
  • Test Automation: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Panoptic Scans - Network and Application Vulnerability Scans?

Who Uses This Product?

  • Company Size: 100% Medium

What Do G2 Reviewers Say About Panoptic Scans - Network and Application Vulnerability Scans?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the easy automation of scans with Panoptic Scans, enabling efficient SOC2 Vulnerability scanning and reporting.
  • Users value the automation capabilities of Panoptic Scans, simplifying SOC2 vulnerability scans and enhancing dashboard creation.
  • Users appreciate the easy automation of scans with Panoptic Scans, simplifying SOC2 Vulnerability management and reporting.
  • Users value the dashboard usability of Panoptic Scans, enhancing the ease of managing vulnerability assessments effectively.
  • Users appreciate the ease of use of Panoptic Scans, enabling effortless automation and actionable insights for security assessments.

What Are Recent G2 Reviews of Panoptic Scans - Network and Application Vulnerability Scans?

Proscan

Proscan is a unified application security platform designed to help organizations streamline the management of their security tools. By integrating multiple standalone solutions into a single cohesive experience, Proscan provides comprehensive security visibility across the entire software stack. This platform replaces the complexity of managing various tools for static analysis, dynamic testing, and dependency scanning, allowing teams to focus on building secure applications without the hassle of juggling disparate systems. The platform is particularly beneficial for security teams, developers, and engineering leaders who require a consolidated view of application security risks. Proscan combines nine specialized security scanners, including Static Application Security Testing (SAST), which analyzes source code in over 30 programming languages using advanced detection methods. Dynamic Application Security Testing (DAST) further enhances security by testing live applications, identifying vulnerabilities that may only become apparent during runtime. Additionally, Software Composition Analysis (SCA) evaluates open-source dependencies across 196 package ecosystems, helping organizations detect known vulnerabilities before they can impact production environments. Proscan's capabilities extend beyond code analysis. It includes scanning for hardcoded secrets, misconfigurations in Infrastructure-as-Code, and vulnerabilities in container images. The platform also offers API security testing that validates endpoints against the OWASP API Security Top 10, ensuring robust protection for applications that leverage APIs. For organizations developing AI-powered applications, Proscan features a dedicated AI and LLM security scanner that identifies potential risks associated with prompt injections and other vulnerabilities, utilizing over 4,600 techniques mapped to the OWASP LLM Top 10. Artificial intelligence plays a crucial role in enhancing Proscan's efficiency and accuracy. The platform employs machine-learning algorithms to reduce false positives and prioritize vulnerabilities based on their potential impact. This intelligent approach allows teams to focus on the most critical security issues while providing clear explanations and actionable remediation guidance. Proscan integrates seamlessly into existing development workflows, offering IDE plugins and native CI/CD integrations that ensure security checks are part of the development process without causing disruptions. Compliance readiness is another key feature of Proscan, as it generates audit-ready reports aligned with major security standards, including OWASP Top 10, PCI DSS, HIPAA, and GDPR. This automated evidence collection simplifies the compliance process, providing organizations with the necessary documentation in various formats. Proscan is designed for security teams looking to consolidate fragmented toolchains, developers needing quick feedback, and managed security service providers managing multiple client environments, making it a versatile solution for modern application security challenges.

Who Is the Company Behind Proscan?

PT Application Inspector

PT Application Inspector™ (PT AI™) is a comprehensive source code analysis tool that offers protection for web applications of any scale. Its holistic approach combines the advantages of static, dynamic, and interactive analysis to maintain application security throughout every stage of development—from the very first line of code to the go-live.

Average Rating: 5.0/5.0

Total Reviews: 2

How Do G2 Users Rate PT Application Inspector?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind PT Application Inspector?

Who Uses This Product?

  • Company Size: 67% Large, 33% Small

What Are Recent G2 Reviews of PT Application Inspector?

What Are G2 Users Discussing About PT Application Inspector?

Sn1per Professional

Sn1per Professional is an all-in-one offensive security platform that provides a comprehensive view of your internal and external attack surface and offers an asset risk scoring system to prioritize, reduce, and manage risk. With Sn1per Professional, you can discover the attack surface and continuously monitor it for changes. It integrates with the leading open source and commercial security testing tools for a unified view of your data.

Average Rating: 4.5/5.0

Total Reviews: 1

Who Is the Company Behind Sn1per Professional?

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Sn1per Professional?

Topscan

Topscan is a continuous security monitoring platform for the DevOps engineer or CTO who owns security among other things. It covers the whole delivery pipeline in one subscription — static analysis in your code, dynamic scanning of live applications and infrastructure, and continuous monitoring of everything you expose to the internet — instead of three separate vendors for SAST, DAST and attack surface management. Perimeter. External infrastructure scanning reports open ports, service versions and known server vulnerabilities matched against CVE databases, with unlimited scheduled rescans. Asset discovery maps the subdomains and hosts you forgot about — the Grafana, the Sentry, the staging box nobody remembers deploying — and new hosts arrive with a review prompt: you confirm ownership before anything is scanned. Attack surface monitoring keeps every exposed service inventoried, and certificate watch catches TLS/SSL expiry weeks early instead of on the Friday night it happens. Applications and code. Web application scanning runs OWASP-class checks against live apps: SQL injection, XSS, exposed admin panels, default credentials, missing headers. Static application security testing covers three kinds of risk in one scan — vulnerable code patterns, committed secrets and keys, and known CVEs in dependencies (software composition analysis) — on every commit, pointing at the exact file and line. Pipeline and cloud. A CI/CD webhook gives you a unique event link to call from the last step of your deploy script: no API keys, no agent, nothing installed on your servers. AWS connects with keys you issue to discover EC2 and Route 53 resources, which are added to monitoring and rescanned when they change. Workflow. Findings are deduplicated and carry severity in your context, CVSS, a first-seen date and an SLA clock with overdue flags. Snooze what you accept, mark false positives and they stop resurfacing, and work through a large backlog in triage mode. Informational findings stay out of the feed and never touch your score. One security score tracks the whole estate over time — the number you show yourself, your CEO or an auditor. Alerts reach the team in Slack or Microsoft Teams and turn into Jira tickets; chat and tracker routing starts on the Advanced plan. Audit and compliance. Auditors ask for evidence of regular scanning and an inventory of what is exposed: scan history with downloadable reports and an exportable asset inventory answer both, which is what most teams use Topscan for ahead of SOC 2, ISO 27001 or a customer security review. Auditor seats are free and read-only, and users are unlimited on every plan. Pricing starts at $129 per month and is published on the site — no demo call required to see it — with a 14-day free trial of the full plan and no credit card. Add a domain and the first map of your perimeter arrives in five to ten minutes.

Average Rating: 4.9/5.0

Total Reviews: 5

Who Is the Company Behind Topscan?

  • Seller: Topscan
  • Year Founded: 2024
  • HQ Location: Dubai, AE
  • LinkedIn® Page: www.linkedin.com
    5 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 80% Small, 20% Medium

What Are Recent G2 Reviews of Topscan?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024