Best Attack Surface Management Software for Small Business - Page 2

How Many Attack Surface Management Software Products Does G2 Track?

Total Products under this Category: 196

Category Stats (Nov 2026)

  • Average Rating: 4.59/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: ThreatConnect Risk Quantifier (+1.46%) - Among all products in this category, ThreatConnect Risk Quantifier recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Attack Surface Management Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,100+ Authentic Reviews
  • 196+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

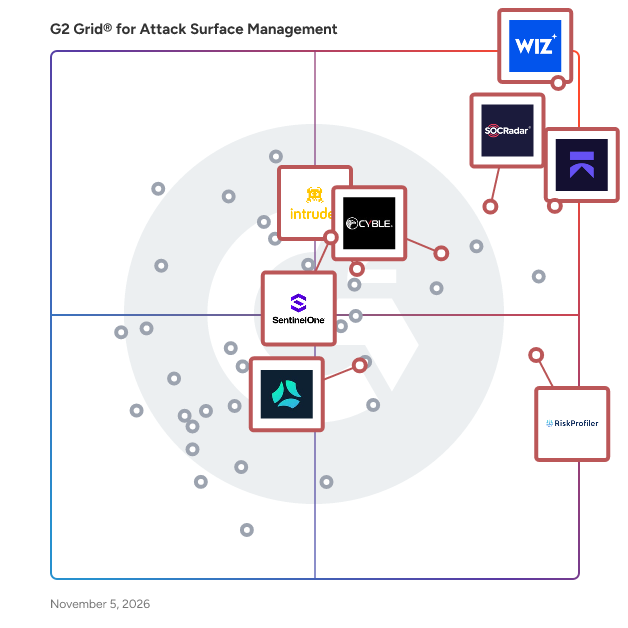
G2 Grid® for Attack Surface Management Software

G2 Grid® for  Attack Surface Management Software plotting products by satisfaction and market presence

Highlighted products: Aikido Security, Wiz, Intruder, RiskProfiler - External Threat Exposure Management, Cyble, SentinelOne Singularity Cloud Security, SOCRadar Extended Threat Intelligence, and Scrut Automation.

Underlying data: [Grid® JSON](https://www.g2.com/categories/attack-surface-management/grids.json?focus%5B%5D=aikido-security&focus%5B%5D=wiz-wiz&focus%5B%5D=intruder&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=cyble&focus%5B%5D=sentinelone-singularity-cloud-security&focus%5B%5D=socradar-extended-threat-intelligence&focus%5B%5D=scrut-automation&segment=small-business)

Check Point Exposure Management

Exposure Management is changing how organizations react to vulnerabilities that put them in risk. Attackers exploit exposed assets, leaked credentials, and misconfigurations within hours using sophisticated AI attack tools. Meanwhile, security teams are left sorting through dashboards, alerts, and disconnected tools. For a limited time only, we are providing an Agentic Exposure Validation Scan at no cost. It delivers proven, evidence-backed findings your team can act on immediately. Request scan here - https://checkpoint.cyberint.com/limited-time-offer-aev-scan Check Point Exposure Management closes that gap by combining billions of external intelligence signals into a Unified Intelligence Fabric. The platform continuously identifies, validates, prioritizes, and safely remediates the exposures attackers are most likely to exploit. With Cyber Asset Attack Surface Management (CAASM), security teams gain a real-time inventory across cloud, SaaS, on-premises infrastructure, endpoints, and identities through 150+ agentless integrations. Unlike traditional vulnerability management, Check Point prioritizes exposures based on real-world exploitability, active threat intelligence, business context, and existing security controls, eliminating duplicate alerts and reducing remediation noise. It does so while maintaining business continuity. Safe-by-design remediation then validates every action before enforcement, enabling capabilities such as virtual patching, IPS activation, configuration hardening, and policy enforcement without disrupting business operations. Organizations using the platform achieve a 93% true positive rate on alerts, 12-hour average takedown MTTR, and 504 safe remediations per organization every month. Built around Gartner's Continuous Threat Exposure Management (CTEM) framework, Check Point helps organizations move from visibility to measurable risk reduction. Gartner predicts organizations adopting CTEM with mobilization will experience 50% fewer successful cyberattacks by 2028. Ready to see Exposure Management in action? Get a 15-minute demo: https://l.cyberint.com/exposure-management-demo

Average Rating: 4.6/5.0

Total Reviews: 198

How Do G2 Users Rate Check Point Exposure Management?

  • Vulnerability Intelligence: 8.8/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 8.7/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.3/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.1/10 (Category avg: 9.0/10)

Who Is the Company Behind Check Point Exposure Management?

Who Uses This Product?

  • Who Uses This: Cyber Security Analyst, Security Threat Analyst
  • Top Industries: Banking, Financial Services
  • Company Size: 66% Large, 21% Medium

What Do G2 Reviewers Say About Check Point Exposure Management?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Check Point Exposure Management, enjoying its intuitive interface for threat detection.
  • Users value the comprehensive threat intelligence from Cyberint, enhancing detection and response to potential threats effectively.
  • Users commend the enhanced threat detection capabilities of Check Point Exposure Management, improving situational awareness and response efficiency.
  • Users value the comprehensive intelligence feeds of Check Point Exposure Management, enhancing threat detection and situational awareness.
  • Users value the responsive and proactive customer support from Cyberint, enhancing their overall threat management experience.
Cons
  • Users face challenges with inefficient alerts due to false positives, complicating the verification process for analysts.
  • Users experience false positives that necessitate additional validation time, complicating the overall alert management process.
  • Users find the inefficient alert system complicates handling excessive alerts and delays threat intel on compromised accounts.
  • Users note integration issues with Check Point Exposure Management, particularly regarding centralizing alerts and connecting security tools.
  • Users note the limited features of Check Point Exposure Management, specifically regarding alert tuning and user account restrictions.

What Are Recent G2 Reviews of Check Point Exposure Management?

What Are G2 Users Discussing About Check Point Exposure Management?

CloudSEK

CloudSEK is a contextual AI company that predicts Cyber Threats. We combine the power of Cyber Crime monitoring, Brand Monitoring, Attack Surface monitoring, and Supply Chain intelligence to give context to our customers’ digital risks.

Average Rating: 4.8/5.0

Total Reviews: 137

How Do G2 Users Rate CloudSEK?

  • Vulnerability Intelligence: 9.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.6/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.4/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.6/10 (Category avg: 9.0/10)

Who Is the Company Behind CloudSEK?

  • Seller: CloudSEK
  • Year Founded: 2015
  • HQ Location: Singapore, SG
  • Twitter: @cloudsek
    2,417 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    247 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Analyst, Analyst
  • Top Industries: Financial Services, Airlines/Aviation
  • Company Size: 53% Large, 31% Medium

What Do G2 Reviewers Say About CloudSEK?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of CloudSEK, noting its smooth functions and intuitive dashboard for seamless monitoring.
  • Users value the continuous monitoring and real-time alerts provided by CloudSEK for effective brand oversight.
  • Users praise the responsive customer support of CloudSEK, which effectively resolves issues quickly and efficiently.
  • Users praise CloudSEK's excellent coverage and AI-driven threat intelligence, enhancing cybersecurity and providing invaluable insights.
  • Users value the real-time visibility into external threats offered by CloudSEK, enhancing proactive risk management.
Cons
  • Users are frustrated by the high rate of false positives in alerts for credential breaches and domain impersonation.
  • Users experience inefficient alerts from CloudSEK, often overwhelming them with false positives and complicating threat prioritization.
  • Users experience dashboard issues with false positives, cluttered layouts, and a need for further customization and basic features.
  • Users experience inefficient alert systems, struggling with false positives and difficulty in managing genuine threats effectively.
  • Users find the complex UI of CloudSEK overwhelming, making it challenging to interpret key information effectively.

What Are Recent G2 Reviews of CloudSEK?

Halo Security

Halo Security is an External Attack Surface Management (EASM) platform that helps organizations discover, monitor, and secure their external digital footprint against cyber threats. The solution enables security teams to view their infrastructure from an attacker's perspective, providing continuous visibility into vulnerabilities, exposed assets, and potential security risks across web applications, cloud resources, and third-party services. Halo Security was founded in 2013 and is headquartered in the United States. With a team of experienced security professionals, the company has assisted thousands of organizations in strengthening their security posture. Their fully US-based operations have earned the trust of organizations across various industries seeking to protect their digital assets from evolving cyber threats. The platform combines automated discovery with expert analysis to deliver comprehensive attack surface monitoring, vulnerability detection, and technology identification. Key features include continuous asset discovery that automatically identifies unknown digital resources, real-time alerts for newly discovered vulnerabilities delivered via integrations with dozens of tools, technology fingerprinting to detect potential vulnerabilities in third-party services, and subdomain takeover protection that identifies dangerous DNS misconfigurations before attackers can exploit them. Halo Security empowers organizations to eliminate blind spots in their attack surface, prioritize remediation efforts based on real risk, and secure their external-facing assets against increasingly sophisticated cyber threats. The solution solves critical challenges for security teams by providing visibility into forgotten or unknown assets, detecting vulnerabilities in third-party platforms, and alerting teams to changes that introduce security risks. Whether managing a growing digital footprint or meeting compliance requirements, Halo Security provides the visibility and tools needed to maintain a strong security posture in today's complex threat landscape.

Average Rating: 4.5/5.0

Total Reviews: 56

How Do G2 Users Rate Halo Security?

  • Vulnerability Intelligence: 8.5/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.4/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.3/10 (Category avg: 8.7/10)
  • Ease of Admin: 8.4/10 (Category avg: 9.0/10)

Who Is the Company Behind Halo Security?

  • Seller: Halo Security
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Miami Beach, US
  • Twitter: @halohackers
    84 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    33 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Retail
  • Company Size: 54% Medium, 23% Large

What Do G2 Reviewers Say About Halo Security?

AI-generated summary from verified user reviews

Pros
  • Users praise the ease of use of Halo Security, noting its simplicity and seamless integration for effective protection.
  • Users value the easy integrations of Halo Security, seamlessly enhancing their security workflows and overall efficiency.
  • Users commend Halo Security for its comprehensive attack surface visibility and seamless integration, enhancing overall security management.
  • Users value the real-time notifications from Halo Security, enabling proactive management of potential security risks effectively.
  • Users highlight Halo Security's strong security capabilities, appreciating its seamless integration and actionable insights for robust protection.
Cons
  • Users find it difficult to navigate the Halo Security portal, leading to occasional frustration in locating functions.
  • Users find the complex UI challenging, especially with the organization and display of menus post-update.
  • Users find the complexity of the setup for multiple scan targets to be cumbersome and inefficient.
  • Users find the complex setup of Halo Security frustrating, noting it requires too many steps for multiple scan targets.
  • Users dislike the dashboard navigation issues in Halo Security, finding the new console cumbersome and uncomfortable to use.

What Are Recent G2 Reviews of Halo Security?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Criminal IP

Criminal IP is a cyber threat intelligence solution that provides decision-ready threat intelligence, and attack surface management solutions to security teams worldwide. By continuously scanning the global internet, Criminal IP aggregates and contextualizes threat signals across IPs, domains, URLs, and attack infrastructure, covering malicious indicators, known vulnerabilities, exposed assets, and attacker behavior. Criminal IP's mission is to give organizations real visibility into their cyber landscape and accelerate threat detection and response by delivering the intelligence needed to outsmart attackers.

Average Rating: 4.6/5.0

Total Reviews: 21

How Do G2 Users Rate Criminal IP?

  • Ease of Admin: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Criminal IP?

  • Seller: Criminal IP
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Las Vegas, US
  • LinkedIn® Page: www.linkedin.com
    29 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 84% Small, 12% Medium

What Do G2 Reviewers Say About Criminal IP?

AI-generated summary from verified user reviews

Pros
  • Users value the automation capabilities of Criminal IP, enabling efficient visualization and management of security data.
  • Users appreciate the ease of use of Criminal IP, enjoying its intuitive navigation and quick setup for complex data.
  • Users appreciate the intuitive design and powerful toolkit of Criminal IP, making complex security data easy to manage.
  • Users commend the quick response time of Criminal IP, enabling efficient real-time visualization and action on threats.
  • Users appreciate the seamless setup of Criminal IP, enabling quick and effortless integration into their systems.
Cons
  • Users find the difficult learning curve frustrating, especially when mastering advanced search filters and navigating the interface.
  • Users experience a steep learning curve for advanced search filters, highlighting the need for improved onboarding resources.
  • Users experience slow loading issues with Criminal IP's web interface, causing minor delays in accessing live data.

What Are Recent G2 Reviews of Criminal IP?

Heimdal

Accommodate all your cybersecurity needs under one convenient roof with the Heimdal® Unified Cybersecurity Platform. Our cybersecurity solutions can be used as standalone products or integrated into one another as part of a cohesive and unified XDR platform. Whether you’re a reseller, distributor, MSSP, or an organization committed to bolstering your online security, we provide an array of cutting-edge products to make your mission smoother. Heimdal® is a fast-growing cybersecurity company focused on continuous technological innovation. Since its establishment in 2014 in Copenhagen, based on the winning idea of CTF World Champions, Heimdal has experienced spectacular growth by proactively building products that anticipate threatscape trends. The company offers a multi-layeredand unified security suite that combines threat prevention, patch and asset management, endpoint rights management, antivirus and mail security which together secure customers against cyberattacks and keep critical information and intellectual property safe. Heimdal has been recognized as a thought leader in the industry and has won multiple international awards both for its solutions and for its educational content creation. The Heimdal line of products currently consists of 10 products and 2 services. The former category encompasses DNS Security for Endpoints & Network, Patch & Asset Management, Privileged Access Management, Application Control, Next-Gen Endpoint Antivirus, Ransomware Encryption Protection, Email Security, Email Fraud Prevention, and Remote Desktop. The latter is represented by Endpoint Detection & Response, as well as eXtended Detection & Response, or EDR and XDR for short. Currently, Heimdal’s cybersecurity solutions are deployed in more than 45 countries and supported regionally from offices in 15+ countries, by 175+ highly qualified specialists. Heimdal is ISAE 3000 certified and secures more than 2 million endpoints for over 10,000 companies. The company supports its partners without concessions on the basis of predictability and scalability. The common goal is to create a sustainable ecosystem and a strategic partnership.

Average Rating: 4.4/5.0

Total Reviews: 84

How Do G2 Users Rate Heimdal?

  • Ease of Admin: 8.2/10 (Category avg: 9.0/10)

Who Is the Company Behind Heimdal?

  • Seller: Heimdal®
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Copenhagen, Denmark
  • Twitter: @HeimdalSecurity
    5,086 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    284 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Computer & Network Security, Construction
  • Company Size: 56% Medium, 29% Small

What Do G2 Reviewers Say About Heimdal?

AI-generated summary from verified user reviews

Pros
  • Users praise the easy setup of Heimdal, appreciating its straightforward installation and quick integration with their systems.
  • Users find that file transfer with Heimdal is seamless and reliable, enhancing overall productivity and ease of use.
  • Users commend Heimdal for its exceptional issue resolution support, providing quick and professional solutions exceeding expectations.
  • Users value the reliable patch management of Heimdal, delivering consistent performance without issues during monthly updates.
  • Users value the reliable security and user-friendly interface of Heimdal, enhancing overall satisfaction and support.
Cons
  • Users find the complex interface of Heimdal difficult to navigate, complicating their overall experience and functionality.
  • Users find the admin portal complex and illogical, making navigation frustrating and cumbersome for essential tasks.
  • Users find the customer support lacking during initial setup, which causes issues with product deployment and upgrades.
  • Users find the poor interface design of Heimdal difficult to navigate, complicating essential tasks and access.
  • Users experience restart issues with Heimdal, feeling unprotected after scans until the software is rebooted.

What Are Recent G2 Reviews of Heimdal?

Notus

Notus's primary focus is to overcome cyber asset visibility by integrating with a wide range of data sources, providing security teams with comprehensive, continuous, unified, and up-to-date visibility of their cyber assets. This proactive approach reveals potential gaps and facilitates the identification of devices, software, services, and configurations.

Average Rating: 4.9/5.0

Total Reviews: 34

How Do G2 Users Rate Notus?

  • Vulnerability Intelligence: 9.2/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.9/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.6/10 (Category avg: 8.7/10)
  • Ease of Admin: 8.5/10 (Category avg: 9.0/10)

Who Is the Company Behind Notus?

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 44% Small, 41% Medium

What Do G2 Reviewers Say About Notus?

AI-generated summary from verified user reviews

Pros
  • Users find Notus to provide significant time savings through automated reporting and vulnerability management processes.
  • Users value the automation capabilities of Notus, enhancing efficiency in vulnerability management and reporting.
  • Users highlight the vulnerability scanning speed and accuracy of Notus, enhancing their asset management experience significantly.
  • Users commend Notus for its responsive customer support, providing quick solutions to problems when needed.
  • Users benefit from the efficiency improvement of Notus, as it simplifies simultaneous data analysis from multiple sources.
Cons
  • Users find the update delays to be frustrating, impacting their overall experience with Notus.

What Are Recent G2 Reviews of Notus?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated