TrueCode
TrueCode is a static application security testing solution.
Who Is the Company Behind TrueCode?
- Seller: SiteLock
- Year Founded: 2008
- HQ Location: Scottsdale, AZ
-
LinkedIn® Page: www.linkedin.com
90 employees on LinkedIn®
Total Products under this Category: 144
Last updated: November 01, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
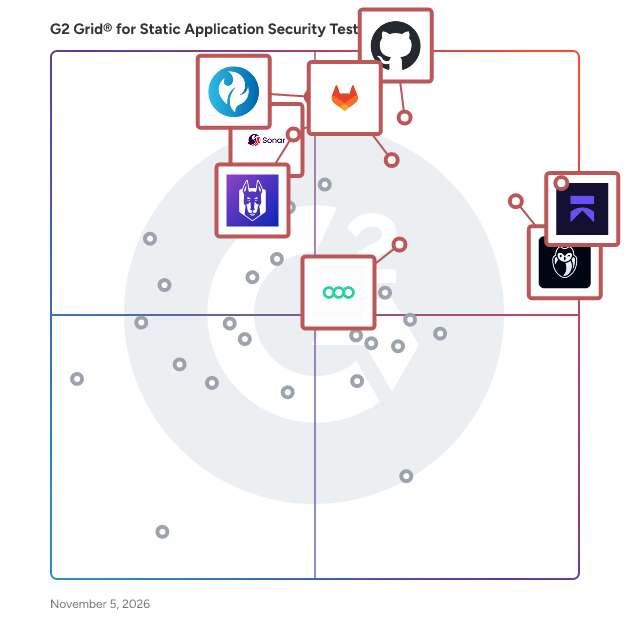
Highlighted products: Aikido Security, GitGuardian, GitHub, GitLab, SonarQube, HCL AppScan, Snyk, and Semgrep.
Underlying data: [Grid® JSON](https://www.g2.com/categories/static-application-security-testing-sast/grids.json?focus%5B%5D=aikido-security&focus%5B%5D=gitguardian&focus%5B%5D=github&focus%5B%5D=gitlab&focus%5B%5D=sonarqube&focus%5B%5D=hcl-appscan&focus%5B%5D=snyk&focus%5B%5D=semgrep)
TrueCode is a static application security testing solution.
TruStacks is a software delivery engine that offers standardized, efficient DevOps workflows to help teams ship products faster and more frequently.
Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.
VulnSign is help to organizations enhance their cybersecurity posture and protect their web applications from potential threats. Our intuitive, user-friendly platform allows users to quickly and easily scan their web applications for vulnerabilities that could be exploited by cybercriminals. VulnSign is designed to easy to use, yet powerful enough to identify potential vulnerabilities in your web-based systems. Our team of security experts is constantly working to improve and update our DAST application, ensuring that it stays at the forefront of the cybersecurity industry.
Average Rating: 5.0/5.0
Total Reviews: 1
"VulnSign's DAST and the Art of Finding Vulnerabilities!"
Rating: 5.0/5.0 stars
— Levi Y.
AppSec Testing(AST) - Whatever your motivation, a proactive security push or a compliance compulsion, our AST service can help keep your application secure against external threats. Security Automation - Secure your agile Software Development Life Cycle(SDLC) without compromising on quality or time. AppSec Training - Our numerous/variegated training offerings help product teams gain the security understanding necessary to keep their deployments secure. Orchestron - Make Application Security efficient with one of the most integral parts of a modern DevSecOps toolchain - An AVC engine. Threat PlayBook - A (relatively) Unopinionated framework that faciliates Threat Modeling as Code married with Application Security Automation on a single Fabric. Perform Iterative Threat Modeling in an Agile Environment with Threat Playbook.
Xygeni: AI-Native ASPM for the Software Supply Chain Xygeni is an AI-native ASPM (Application Security Posture Management) platform that unifies native and third-party security findings into one prioritized view. Its own detection engines cover SAST, SCA, DAST, Secrets, IaC, Container, CI/CD, and Build Security, and it also ingests results from tools like Snyk, Veracode, and Checkmarx so teams don't have to abandon what they've already invested in. Every finding, regardless of source, gets scored by exploitability, reachability, and business impact through Xygeni's Dynamic Funnels, which is what drives its reported 90% cut in alert noise. Two AI systems sit underneath the platform. CoreAI acts as a correlation and reporting layer for security leaders, turning scattered findings into a single risk narrative. DevAI works earlier, inside the developer's IDE and AI coding assistants, catching problems in both human-written and AI-generated code and proposing fixes before a pull request is even opened. On the supply chain side, Xygeni's MEW engine (Malware Early Warning) is built to catch malicious open-source packages the moment they hit a public registry, ahead of when a formal malware signature would normally exist. Shield takes that enforcement to the developer's own machine, blocking unauthorized package downloads at the OS level before they reach disk. Xygeni also runs a dedicated Code Quality engine across ten languages, ranking maintainability and complexity issues alongside security findings in the same console, so a team can see when the messiest file is also the riskiest one. The platform connects to GitHub, GitLab, Bitbucket, Jenkins, and Azure DevOps, and deploys as SaaS, on-premises, or fully air-gapped. Xygeni was named Hot Company in ASPM and in GenAI Application Security at the 2026 Global InfoSec Awards.
Average Rating: 4.6/5.0
Total Reviews: 4
AI-generated summary from verified user reviews
"Revolutionized Our Security Workflow with Unified, AI-Driven Efficiency"
Rating: 5.0/5.0 stars
— Yerassyl K.
"The essential tool for proactive security and confident development"
Rating: 4.5/5.0 stars
— Marcos C.
YAGAAN is a french startup established in 2017 and located in the Brittany Cyber Valley. In the SAST landscape, the YAG-Suite offers unique features to auditors and developers that only machine learning can bring on top of static analysis : - Smart detection of vulnerabilities - Automated qualification and hierarchization of the warnings raised by SAST, based on their likeliness to be true positives and their criticallity (individual CVSS score) - Advanced diagnostics of the detected vulnerabilities to help users understand their causes - Remediation support with recommended vulnerability fix - Code mining queries to help auditors and experts to accelerate further manual investigations The Scanner is available in saas access or on premise to be integrated in CI/CD Request your free saas trial at https://yagaan.com/en/
An advanced interactive application security tool identifying vulnerabilities in both self-developed code and open-source dependencies. Seamlessly integrate into CI/CD and can be applied in both application development phase and application deployment phase.
Continuous security delivery fabric for modern enterprise infrastructure.
