Revealer Keylogger
Who Is the Company Behind Revealer Keylogger?
- Seller: Logixoft
- HQ Location: N/A
-
LinkedIn® Page: www.linkedin.com
1 employees on LinkedIn®
Total Products under this Category: 54
Last updated: October 07, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
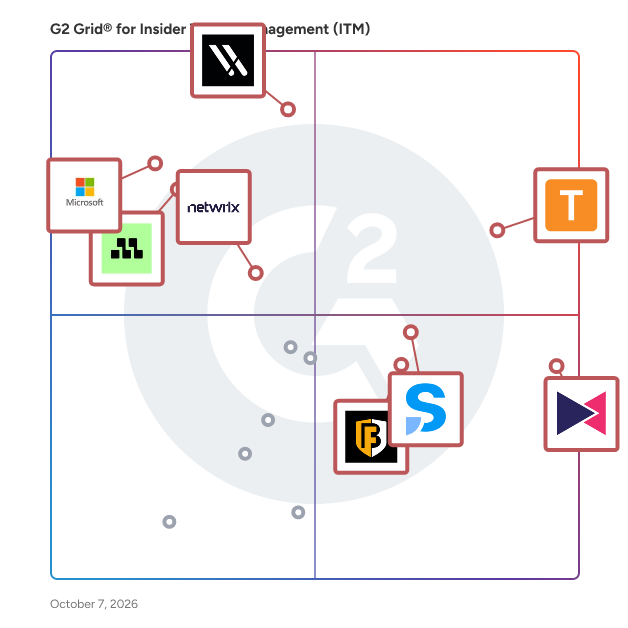
Highlighted products: Teramind, Varonis Data Security Platform, DataPatrol, Safetica, BlackFog, Incydr, Microsoft Purview Insider Risk Management, and Netwrix Auditor.
Underlying data: [Grid® JSON](https://www.g2.com/categories/insider-threat-management-itm/grids.json?focus%5B%5D=teramind&focus%5B%5D=varonis-data-security-platform&focus%5B%5D=datapatrol&focus%5B%5D=safetica&focus%5B%5D=blackfog&focus%5B%5D=incydr&focus%5B%5D=microsoft-purview-insider-risk-management&focus%5B%5D=netwrix-auditor)
Fully automated security marketplace to help digital businesses protect against cyber threats and data loss. Companies are now highly dependent on their digital environment for critical business functions like file sharing, collaboration, code management, and customer relationship. An emerging challenge for these companies is how to stay secure while continue and grow their digital business as they: 1) Have no understanding of how to protect against attacks. 2) Don’t have the personnel to address IT security. 3) Have failed to act following a cybersecurity incident. In our SaaS Security portfolio, you can find the following features 1) Proactive Threats Protection - Based on cloud-native security controls, proactively take action to mitigate risks before they evolve to breach. Revoke permissions, limit sharing & manage incident response. 2) Ongoing Backups - Prevent from losing mission-critical data and metadata with automated backups and rapid recovery. 3) Prevent Human Erros - Empowers employees with the knowledge and skills to stay cyber secure at work and home by automating communications and simulate cyberthreats. 4) Stay Compliant - Simplifying the complex, time-consuming, and tedious process of becoming SOC2, PCI, or ISO 27001 compliant. Saasment easily integrates with all your cloud applications seamlessly.
Average Rating: 5.0/5.0
Total Reviews: 1
"Easy to use, perfect for small IT teams. Highly recommended."
Rating: 5.0/5.0 stars
— Verified User in Computer Software
Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.
SearchInform Risk Monitor is an internal threat mitigation and insider risk protection solution, that controls the maximum quantity of information channels as well as featuring built-in analytical tools. The system conducts a real-time analysis, identifying every ongoing event within a network and mitigating insider risk. The software saves the data it obtains and allows users to restore details, enabling retrospective investigation and providing access to the archive. The system operates on two levels. It keeps track of the data leaving the network while at the same time monitors employee activities on computers. SearchInform Risk Monitor keeps an eye on the company’s assets 24/7 even if the employees are outside the office (field work, WFH or while on the business trip) but using corporate devices. SearchInform Risk Monitor aids companies in building a risk management program and a solid insider threat management process, helping to foresee any prospective internal corporate risks in advance via: · Immunization to the consequences of data leakage · Exposing fraud schemes (sabotage, embezzlement, theft, waste, and kickbacks) · Safeguarding the company against personnel risks and predicting employee behavior patterns · Solving regulatory compliance issues · Helping to increase staff productivity · Team loyalty management
ShadowSight, an innovative Australian solution which redefines the approach to managing insider threats by integrating advanced SEIM and user behaviour analytics to meticulously analyse and understand the context behind employee activities. Unlike traditional systems, which overwhelm with false alerts, ShadowSight’s detection rules are adjusted in near real-time to adapt to evolving business risks. Its unique attributes include eliminating the need for ongoing professional services, simplifying the application of custom rules for enhanced monitoring, and offering a user-friendly interface that streamlines the filtering of benign activities. With an integrated workflow for seamless business integration and centralisation of staff activity logs into a single pane of glass, ShadowSight not only surpasses current DLP tools but also reduces current SIEM costs. ShadowSight recognises that most risky behaviours are not malicious, focusing on intent to improve compliance and visibility of insider risks. ShadowSight stands out as a cost-effective, precise, and adaptable platform, offering unparalleled protection against insider threats while ensuring seamless business operations.
All-in-One Solution for Insider Threat Management and Employee Monitoring. Staffcop is a groundbreaking solution that integrates Insider Threat Management with robust employee monitoring and remote administration features. Positioned at the intersection of security and performance, Staffcop offers a comprehensive set of functions to protect company data and oversee employee activities. Utilizing UAM, UEBA modules, OLAP technology, and pre-built or custom dashboards, Staffcop aids enterprises, SMBs, and government entities in reducing information security risks and enhancing workforce efficiency on Windows, Linux, and macOS platforms.
Average Rating: 4.3/5.0
Total Reviews: 3
AI-generated summary from verified user reviews
"Positive beginning in case of initial employee monitoring"
Rating: 4.0/5.0 stars
— Cadete d.
"Comprehensive Monitoring with Advanced Security Features"
Rating: 5.0/5.0 stars
— Bhavin G.
TrackerDetect brings a whole new way of protecting your applications against Insider threats. Powered by our unique patent-pending clustering engine, driven by activity flow analytics, TrackerIQ automatically, swiftly, and accurately detects and responds to every insider threat on any enterprise application, without having to create rules, build data models, or clean outliers IT'S TIME FOR A NEW WAY TO PROTECT.
Trua-CE™ goes beyond initial and periodic background checks by offering continuous and automated background screening that is alert-driven and exception-based. The solution offers role-specific criteria and packages, while delivering employee privacy by design. It's highly secure with a blockchain, encrypted data vault, and ISO Security Standard 27001 certified. Trua-CE's patented, full-spectrum enterprise insider threat and trust screening solution offers the following key benefits: Real-Time Risk Identification, Enhanced Security and Safety, Improved Compliance, Increased Efficiency, Proactive Risk Management, Better Decision-Making, and Cost Savings
UpGuard User Risk is an AI-powered human risk management solution that empowers security teams to gain clear visibility into human risk, enable safe AI adoption, and drive a security-first culture. As part of the UpGuard Cyber Risk Posture Management (CRPM) platform, it integrates seamlessly with Breach Risk and Vendor Risk to provide a unified defense against modern cyber threats. As organizations scale, the workforce remains one of the most targeted attack vectors. Traditional security awareness training often falls short, leaving teams vulnerable to shadow AI, compromised credentials, and over-privileged access. User Risk solves this by combining continuous human risk monitoring, contextual guidance, and policy governance into a single, automated platform. Key Capabilities: • Continuous Human Risk Monitoring: Illuminate risks hiding in plain sight. Security starts with visibility. User Risk transforms fragmented identity, behavior, and threat signals into a clear, unified view of human risk that’s always up to date. Get constant visibility into everything from unauthorized AI usage to compromised credentials. • Contextual Guidance: Nudge users to stay safe. Build a sustainable security culture by helping employees self-remediate in the moment. Educational prompts trigger employees to act when risky behavior is detected, and automated follow-up scans confirm that the right action was taken. • Shadow AI Detection: Shine a light on shadow AI. Prevent critical data leakage by identifying exactly which AI tools your workforce is using and when. Use granular threat detection to create smart policies that enable safe AI usage, instead of blocking access to AI across the board. • Actionable Prioritization: Surface the risks that matter most. User Risk automatically scores and ranks risks into a prioritized action plan for quick, precise decision-making. Understand exactly which teams and individuals require immediate attention and see the exact steps required to secure them. By translating fragmented identity, behavior, and threat signals into a clear view of human risk, UpGuard User RIsk enables security leaders to pinpoint vulnerabilities, build a sustainable security culture, and confidently manage workforce risk.
