Ransomware Susceptibility
Who Is the Company Behind Ransomware Susceptibility?
- Seller: Risk Cognizance
- Year Founded: 2023
- HQ Location: New York, US
-
LinkedIn® Page: www.linkedin.com
16 employees on LinkedIn®
Last updated: November 18, 2026
Total Products under this Category: 81
Last updated: November 17, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
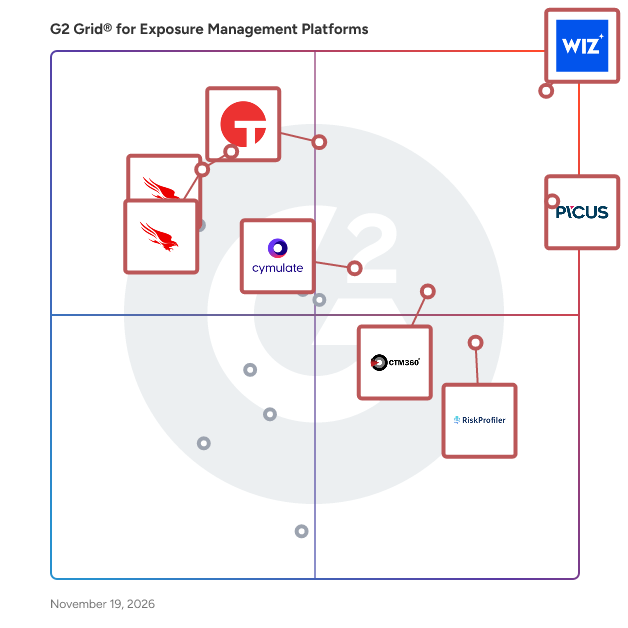
Highlighted products: Wiz, Picus Security, Tanium, CTM360, RiskProfiler - External Threat Exposure Management, Cymulate, CrowdStrike Falcon Cloud Security, and CrowdStrike Falcon Exposure Management.
Underlying data: [Grid® JSON](https://www.g2.com/categories/exposure-management-platforms/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=picus-security&focus%5B%5D=tanium&focus%5B%5D=ctm360-ctm360&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=cymulate&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=crowdstrike-falcon-exposure-management)
With Red Sift ASM (Attack Surface Management), you can continuously discover, inventory and manage your business’s critical external-facing and cloud assets. With Red Sift ASM, you: 1) Get complete visibility with a view into your entire attack surface – including assets you didn't know existed; 2) Remediate configuration risks before bad actors can take advantage; 3) Reduce premiums by solving problems before they are visible to your cyber insurer.
Average Rating: 4.0/5.0
Total Reviews: 1
AI-generated summary from verified user reviews
Rating: 4.0/5.0 stars
— Verified User in Information Technology and Services
Resilience is a cyber risk management platform that helps organizations identify vulnerabilities across their applications, networks, and cloud services, quantify the financial impact of those vulnerabilities, and prioritize remediation based on expected dollar loss. The platform integrates real-time threat intelligence, security posture data, and insurance claims data to produce risk models that use machine learning to rank vulnerabilities by their likelihood of causing financial harm. The platform is built on the Threatonomics Risk Graph, a proprietary AI-powered engine that ingests security control data from an organization's existing tools (EDR, SIEM, vulnerability scanners, cloud security), enriches it with live threat intelligence and aggregated loss data from Resilience's insurance portfolio, and outputs financially quantified risk assessments. These assessments express cyber risk in dollar terms rather than abstract severity scores. Resilience is available in two packages: Resilience Edge is designed for individual enterprises. It includes continuous security posture assessment, a financially prioritized Cyber Action Plan with projected ROI for each remediation, breach and attack simulation powered by AttackIQ, vendor risk reports, and board-ready reporting with peer benchmarks. The Risk Operations Center provides ongoing monitoring of threat activity, delivering expert-validated alerts on industry-specific threats, active ransomware campaigns, and vulnerabilities under active exploitation. Resilience Arc is designed for multi-entity organizations such as holding companies, private equity portfolios, and multinationals. It includes everything in Edge plus automated risk assessments across every subsidiary and business unit, a portfolio-level dashboard that stack-ranks entities by financial risk exposure, and centralized monitoring across all entities from a single interface. Resilience also provides integrated cyber insurance, connecting risk quantification directly to coverage decisions. The platform's risk models are trained and continuously validated against actual insurance claims outcomes from Resilience's underwriting portfolio, creating a feedback loop between security controls and real-world loss data. Primary users include CISOs and security leaders (for vulnerability prioritization and security investment planning), CFOs and boards (for financial visibility into cyber exposure), and risk managers (for balancing security investment against insurance coverage). The platform serves mid-market and enterprise organizations across manufacturing, financial services, healthcare, technology, construction, energy, transportation, and the public sector. Resilience serves 800+ enterprise clients, including more than 10% of US-based companies with revenue over $1 billion. The platform is recognized in Gartner's Hype Cycle for Cyber Risk Management. The company is headquartered in San Francisco and backed by over $200M in venture funding.
Average Rating: 4.5/5.0
Total Reviews: 1
AI-generated summary from verified user reviews
"Resilience - The name itself says all"
Rating: 4.5/5.0 stars
— Siddharth Ranjan S.
Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.
runZero provides a single source of truth for exposure management across your total attack surface. Without requiring agents, authentication, or appliances, runZero delivers the most complete and accurate visibility into every asset and exposure across internal, external, IT, OT, IoT, mobile, and cloud environments — including uncovering unknown and unmanageable devices and broad classes of exposures that evade traditional tools. Founded in 2018 by HD Moore, runZero is trusted by more than 500 companies and 30,000 users worldwide to mitigate risks faster, meet compliance requirements, and improve overall security.
Average Rating: 4.0/5.0
Total Reviews: 1
Rating: 4.0/5.0 stars
— Christian F.
Securin Exposure brings vulnerability and exposure data from existing security tools into a single normalized, deduplicated view, giving security teams one place to understand risk across internal infrastructure, cloud environments, applications, and other assets. Rather than replacing scanners, it works across the existing security stack to turn fragmented findings into a prioritized remediation workflow. Exposure prioritizes vulnerabilities using more than severity scores. It combines asset criticality and business context with Securin's vulnerability and threat intelligence, including exploit availability, active exploitation, ransomware associations, and threat-actor activity. This helps teams distinguish the exposures attackers are most likely to use from the much larger exposure backlog and focus remediation where it can reduce the most risk. Security teams can organize assets by business importance, track exposure age and remediation progress, and use role-based dashboards and reporting to give analysts, engineers, executives, and auditors the information relevant to their roles. Securin VERA, the platform's embedded AI reasoning agent, correlates assets, exposures, and live threat intelligence to answer questions about vulnerabilities, identify affected assets, surface priority exposures, and generate remediation-ready context. Exposure also connects prioritization directly to remediation. Through integrations with ticketing and security tools, teams can move prioritized exposures into existing operational workflows, track them through closure, and measure how exposure changes over time. The result is a scanner-neutral approach to Unified Vulnerability Management that helps organizations move from collecting vulnerability findings to making defensible remediation decisions and demonstrating measurable risk reduction.
The Sevco Exposure Assessment Platform (EAP) breaks down siloed tech tools to provide a system of record to support security programs. With Cyber Asset Attack Surface Management (CAASM) as the inventory foundation, Sevco has evolved to include vulnerability assessment, vulnerability prioritization, and threat intelligence—becoming a true EAP that provides comprehensive data on devices, identities, applications, users and vulnerabilities. Power your exposure management and CTEM programs with the Sevco Exposure Assessment Platform and discover, prioritize, and resolve risks at scale.
Teisoft Exposure Platform™ is a Continuous Threat Exposure Management (CTEM) solution designed to help organizations continuously identify, validate, prioritize, and remediate risks across their external attack surface. Unlike traditional External Attack Surface Management (EASM) platforms that charge based on the number of discovered assets, Teisoft enables organizations to maintain an unlimited inventory of internet-facing assets while operating under predictable, assessment-based pricing. What Makes Teisoft Different -Unlimited Asset Repository: Maintain visibility across unlimited domains, IPs, cloud resources, web applications, APIs, and external infrastructure without worrying about asset-based licensing costs. -Dynamic Assessment Rotation: Each subscription includes a monthly pool of assessments that can be allocated dynamically across assets based on business priorities and risk exposure. Continuously assess critical assets while rotating coverage across lower-priority infrastructure to maximize security ROI. CTEM-Powered Exposure Management Teisoft supports the full CTEM lifecycle by: -Discovering and inventorying external assets -Identifying vulnerabilities, misconfigurations, exposed services, and threat exposures -Validating exploitability through automation and expert review -Prioritizing findings based on business impact and risk context -Tracking remediation efforts and measuring risk reduction over time Human-Verified Security Findings When automated evidence is insufficient, Teisoft's offensive security specialists perform expert-led validation and authorized penetration testing to confirm real-world exploitability, helping security teams eliminate false positives and focus on actionable threats. Benefits: -Unlimited asset visibility -Predictable security spending -Reduced false positives -Faster remediation cycles -Continuous risk reduction -Improved compliance and audit readiness Teisoft combines automated exposure management with human-led offensive security expertise, helping organizations continuously reduce their attack surface while maximizing the value of every security assessment.
TENET is a risk intelligence platform purpose-built for the Microsoft ecosystem to deliver unified visibility and proactive risk assessment across Azure and M365. It serves as a single source of truth for identifying, prioritizing, and mitigating cloud risk at scale—enabling organizations to shift from reactive firefighting to continuous, intelligence-driven security operations. Key Features: - Attack surface management: Identify risky entry points, misconfigurations, and third-party exposures. Visualize attack paths, map findings to MITRE ATT&CK, prioritize remediation, and manage incidents from a unified cloud risk view. - Anomaly detection: Detect issues early with real-time analysis of cloud workloads, identities, and applications, helping teams identify abnormal behaviour and mitigate risks before they become incidents. - Compliance readiness: Simplify audits with continuous compliance monitoring, guided remediation, and risk-prioritized insights. Reduce costs and manual effort while shrinking audit preparation from weeks to hours. - Microsoft 365: Gain visibility into external sharing, device risk, license utilization, and Copilot agents. Understand how identities, configurations, and data exposures combine to create risk across your cloud environment. - Access governance: Monitor human and non-human identities, analyze effective permissions across Entra ID and RBAC, and maintain clear visibility into who can access resources across your cloud estate. - AI monitoring: Discover and inventory AI models, agents, and cognitive services. Continuously monitor performance, reliability, and security posture while identifying AI-specific risks and prioritizing remediation. - Intelligent insights: Investigate and resolve issues faster with BriteAI. Transform live data into actionable insights, identify root causes through natural language queries, and receive precise remediation guidance. Core Value: TENET eliminates blind spots and reduces mean time to remediation (MTTR) through end-to-end Microsoft cloud visibility and guided remediation. It lowers compliance and audit overhead, enables teams to proactively identify and mitigate risks before they escalate, and scales security operations efficiently with AI-powered insights and autonomous remediation with full context via the TENET MCP server. For more information, visit www.aesonsolutions.com.
Nipper OmniSight: preemptive exposure assessment for complex networks Nipper OmniSight is Titania’s preemptive exposure assessment solution, providing enterprise-scale, regular, and repeatable configuration assessment that validates segmentation and least-privilege access (core Zero Trust controls), exposes unintended access paths, and helps reduce exposure across complex networks. What problem does Nipper OmniSight solve? AI is shrinking the time defenders have to act. The firewalls, routers, and switches that decide whether an incident stays contained are governed by configurations that broad platforms infer rather than validate. A temporary migration rule stays in place. A broad rule overrides a restrictive one. A segmentation boundary looks right in theory but fails in practice. Nipper OmniSight validates those configurations directly, from the inside out, so you can prove your network is configured as intended. Proof, not inference. How does it work? Nipper OmniSight validates firewall, router, switch, and wireless access point configurations directly, with expanding SD-WAN and software-defined network (SDN) coverage. It models what each device permits and traces how misconfigurations combine into access paths to critical assets. Findings are ranked by exploitability and impact, so teams fix what matters first. Deployed on-premises or in a virtual private cloud (VPC), Nipper OmniSight works without agents, live-network scanning, or cloud dependency, so even sensitive and air-gapped networks can be assessed safely. It complements outside-in vulnerability scanning with deterministic, reproducible findings. Who is it for? Security operations: find and prioritize exposure, and prove segmentation and least-privilege access hold. Network operations: validate change before it is deployed and identify drift through assessment, before it causes an outage. Audit and assurance: framework-mapped, defensible evidence, with audit prep time cut by up to 80%. Deployment options Standalone: scheduled, repeatable assessments for up to 200 devices, without needing a configuration management database (CMDB). Integrated: adds CMDB or configuration-storage ingestion and security information and event management (SIEM) workflow integrations to automate assessment across distributed environments. Continuous: regular, repeatable assessment at enterprise scale, covering up to 250,000 devices within 24 hours. It helps teams identify configuration changes through assessment, validate Zero Trust segmentation, and help constrain unauthorized lateral movement as networks change. Trusted where the stakes are highest 1000+ organizations trust Nipper solutions, including 30+ US federal agencies and 100+ critical infrastructure providers across 43 countries.
Trend Micro's Cyber Risk Exposure Management (CREM is a comprehensive solution designed to enhance an organization's cybersecurity posture by providing continuous visibility, assessment, and mitigation of cyber risks. By integrating advanced technologies such as AI and machine learning, CREM enables businesses to proactively identify vulnerabilities, prioritize remediation efforts, and predict potential threats before they materialize. This proactive approach ensures that organizations can effectively manage their attack surface, reduce exposure to cyber threats, and maintain compliance with industry standards. Key Features and Functionality: - Continuous Asset Discovery: CREM offers real-time discovery of all cyber assets, including cloud services, devices, and APIs, ensuring comprehensive visibility across the entire digital environment. - Risk Assessment and Prioritization: Utilizing intelligent, context-driven risk scoring, CREM evaluates assets based on factors such as criticality, threat activity, and business impact, allowing organizations to focus on mitigating the most significant risks first. - Predictive Threat Analysis: By mapping discovered risks to critical assets and visualizing potential attack paths, CREM anticipates where adversaries might strike, enabling proactive defense measures. - Automated Remediation: The platform accelerates threat response through AI-driven recommendations and automated security playbooks, reducing the mean time to respond (MTTR and allowing security teams to concentrate on strategic initiatives. - Compliance Management: CREM streamlines compliance processes by mapping security efforts to global standards such as NIST and GDPR, generating audit-ready reports, and automating routine compliance tasks. Primary Value and Problem Solved: CREM addresses the critical challenge of managing and mitigating cyber risks in an increasingly complex digital landscape. By providing continuous, real-time insights into an organization's attack surface, it enables proactive identification and remediation of vulnerabilities, thereby reducing the likelihood of security breaches. The integration of AI and machine learning enhances decision-making processes, allowing for efficient resource allocation and improved operational efficiency. Ultimately, CREM empowers organizations to build resilience against cyber threats, maintain regulatory compliance, and protect their digital assets effectively.
Trickest provides an innovative approach to offensive cybersecurity automation, assets, and vulnerability discovery. The platform combines extensive adversary tactics and techniques with full transparency, hypercustomization, and hyperscalability, making it the go-to platform for offensive security operations. The Trickest platform comes with comprehensive tooling, scripting, managed infrastructure, scaling, ready-to-go solutions, and analytics, serving as a collaborative command center for Offensive Security, Penetration testing, Red teams, Security Analysts, and Security Service providers (MSSPs). What makes us different? Easy customization of logic, inputs, outputs, and integrations, making them adaptable to specific needs and thus producing superior-quality data compared to others. Some of the automation workflows and solutions that our customers deploy and execute: - Attack Surface Discovery - Vulnerability Scanning - Dynamic Application Security Testing (DAST) - Recon/Information Gathering (Passive & Active) - Organization OSINT - CVE scanning - Cloud Scanning - DNS recon & research - Subdomain Enumeration - Subdomain Takeover - Custom Security Automation and Orchestration Main components of the Trickest platform include: Solutions & Analytics - Ready-to-go and transparent solutions for Attack Surface Discovery, Vulnerability Scanning, Dynamic Application Security Testing (DAST), and Open-source intelligence OSINT, offering insight into every step of the process, easy customization, and Analytics on the top. The Builder - Access to 90+ workflow templates, 300+ open-source tools, Bash & Python scripting, CLI for building custom workflows to discover asset, vulnerabilities, scan network & apps, crawl, spider, enumerate, fuzz, bruteforce and much more. Hyperscalability - Whether scanning regional infrastructures with 100s of 1000s of assets or smaller organizational scopes, Trickest supports it all without per-asset costs.
Full-cycle exposure management combining native automated testing, human expertise, risk-based prioritization, remediation tracking, and validation in one platform.
"All-in-One Exposure Management Platform with Strong Continuous Audit Readiness"
Rating: 5.0/5.0 stars
— Verified User in Computer & Network Security
