Best AI SOC Agents - Page 3

How Many AI SOC Agents Products Does G2 Track?

Total Products under this Category: 54

Category Stats (Oct 2026)

  • Average Rating: 4.64/5 (↓0.01 vs Sep 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Hunto AI (+1.58%) - Among all products in this category, Hunto AI recorded the largest rating increase compared to last month

Last updated: October 07, 2026

How Does G2 Rank AI SOC Agents Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,100+ Authentic Reviews
  • 54+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

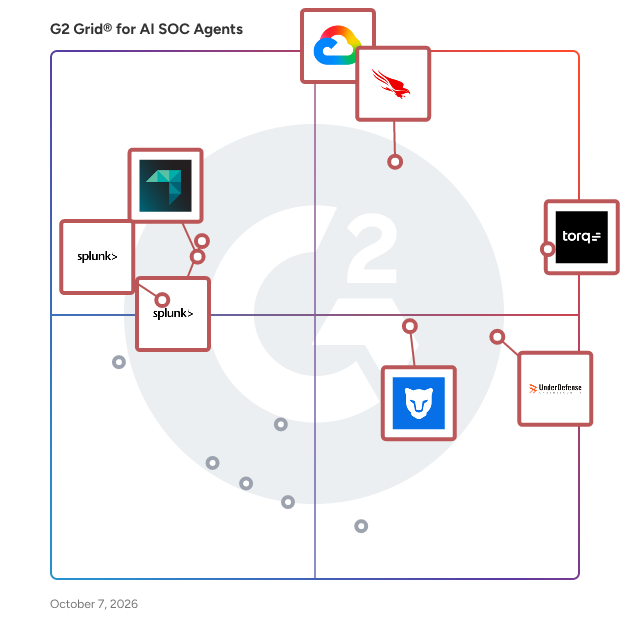
G2 Grid® for AI SOC Agents

G2 Grid® for AI SOC Agents plotting products by satisfaction and market presence

Highlighted products: Google Security Operations, Torq AI SOC Platform, CrowdStrike Charlotte AI, UnderDefense MAXI, Panther, Splunk Enterprise Security, ReliaQuest GreyMatter, and Splunk SOAR (Security Orchestration, Automation and Response).

Underlying data: [Grid® JSON](https://www.g2.com/categories/ai-soc-agents/grids.json?focus%5B%5D=google-security-operations&focus%5B%5D=torq-ai-soc-platform&focus%5B%5D=crowdstrike-charlotte-ai&focus%5B%5D=underdefense-maxi&focus%5B%5D=panther&focus%5B%5D=splunk-enterprise-security&focus%5B%5D=reliaquest-greymatter&focus%5B%5D=splunk-soar-security-orchestration-automation-and-response)

Arcanna.AI

Arcanna.AI is an AI Platform focused on augmenting human decisions in the SOC, agnostic to the tools and processes utilized by the analyst team. Reduce the risk of human error and increase efficiency in decision-making Your data. Your models. Your network. Your tools. Your processes. Empowering SOC Analysts with Superior Decisions; Seamless Integration; Data Privacy And Security

Who Is the Company Behind Arcanna.AI?

  • Seller: Arcanna.AI
  • Year Founded: 2019
  • HQ Location: New York, US
  • Twitter: @ArcannaAi
    82 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    24 employees on LinkedIn®

Artemis Security

The AI-Native Protection Platform Powering Modern Security Operations Traditional SIEMs weren’t built for AI-driven threats. Artemis closes that gap by dramatically reducing MTTD and MTTR, stopping attacks before they can cause adverse impact.

Who Is the Company Behind Artemis Security?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Bricklayer.ai

Bricklayer AI is an innovative cybersecurity platform that integrates autonomous AI agents with human experts to enhance the efficiency and effectiveness of Security Operations Centers (SOCs). By automating repetitive Tier 1 tasks, such as 24/7 monitoring and alert triage, Bricklayer AI allows human analysts to focus on more complex threats, thereby reducing operational costs and improving response times.

Who Is the Company Behind Bricklayer.ai?

Crogl

Crogl is an advanced AI-driven solution designed to enhance Security Operations Centers (SOCs) by automating alert triage, investigation, and threat hunting processes. Operating autonomously, it requires no coding or pre-written playbooks, ensuring seamless integration into both on-premises and cloud environments.

Who Is the Company Behind Crogl?

  • Seller: Crogl
  • Year Founded: 2023
  • HQ Location: N/A
  • LinkedIn® Page: www.linkedin.com
    27 employees on LinkedIn®

Culmintate

AI SOC Analyst that autonomously investigates all alerts across connected systems, without playbooks or coding, producing decision‑ready reports that enhance investigation speed and accuracy

Who Is the Company Behind Culmintate?

  • Seller: Culminate
  • Year Founded: 2023
  • HQ Location: Palo Alto, California
  • LinkedIn® Page: www.linkedin.com
    19 employees on LinkedIn®

Darktrace / SECURE AI

Darktrace / SECURE AI applies behavioral security to help organizations safely adopt AI across their business. Powered by Darktrace Adaptive AI, it learns how prompts, users, agents, and AI systems normally operate within the context of each organization, helping security teams identify misuse, misconfiguration, policy violations, and unexpected behavior that traditional, rule-based controls may miss. Darktrace / SECURE AI gives organizations the visibility, behavioral understanding, governance, and ability to act needed to manage AI risk across four key areas: - Shadow AI Management: Discover unsanctioned or unexpected AI activity, distinguish misuse of approved tools from genuinely unapproved services, and guide users toward sanctioned alternatives. - AI Prompt Analysis: Monitor prompts, sessions, and responses across supported enterprise AI services and agent-building environments to identify sensitive data exposure, attempted jailbreaks, possible prompt injection, and other risky activity. - AI Agent Identities and Actions: Understand which human and non-human identities are associated with AI activity, what agents can access, how they connect to other systems, and whether their behavior remains aligned with their intended purpose. - AI Agent Development Risk Management: Identify excessive permissions, misconfigurations, and anomalous development activity across supported low-code and high-code AI development environments. Policy Manager provides a governance layer across these capabilities by mapping an organization’s own AI policies against real prompt activity. This helps teams investigate potential misalignment, track policy effectiveness over time, and manage AI adoption based on how AI is actually being used. Darktrace / SECURE AI helps organizations move beyond simply observing AI activity to understanding behavior, managing risk, and governing AI adoption with confidence

Who Is the Company Behind Darktrace / SECURE AI?

  • Seller: Darktrace
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Cambridgeshire, England
  • Twitter: @Darktrace
    18,177 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,597 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

Dropzone AI

Dropzone Al offers a pre-trained Al SOC analyst that autonomously handles Tier 1 alert triage and investigation for every alert. It replicates the investigative process and techniques of expert analysts, augmenting SOCs with unlimited cognitive automation to handle time-consuming and tedious SecOps tasks. Dropzone AI was founded in 2023 and is based in Seattle, WA. The company's customers include forward-thinking security organizations such as UiPath, Zapier, and CBTS.

Who Is the Company Behind Dropzone AI?

  • Seller: Dropzone AI
  • Year Founded: 2023
  • HQ Location: Seattle, US
  • Twitter: @DropzoneAI
    326 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    11 employees on LinkedIn®

Gladius Securitas

Gladius Securitas is an AI Algorithmic Response Platform that eliminates alert fatigue through continuous, machine-speed remediation. We execute autonomous Purple Teaming to validate and close exploitable attack paths across cloud, API, and human/machine identities.

Who Is the Company Behind Gladius Securitas?

Gym Management Automation

Gym Management Automation is cloud-based software that streamlines fitness facility operations with digital tools and automated workflows. It includes an admin dashboard for managers, a member app for Android/iOS, and a trainer app for fitness professionals. The admin dashboard centralizes member profiles, staff coordination, revenue tracking, and analytics. The member app lets users view plans, record attendance, access diet/workout plans, and track progress. The trainer app helps professionals manage client profiles, create plans, and monitor progress. Billing is automated via integrated payment gateways supporting UPI, cards, and net banking. Features include renewal reminders, subscription management, and real-time analytics. Operating on cloud infrastructure, it provides access to administrative functions and member services from anywhere, accommodating diverse fitness business models without scaling limits.

Who Is the Company Behind Gym Management Automation?

Imperum

Imperum is an Autonomous SecOps & Investigation Platform powered by Agentic AI, built for enterprise SOCs, MSSPs, and MDR providers. Security teams today face the same operational pressure: too many alerts, too many disconnected tools, too much manual investigation, and not enough analyst capacity. Imperum helps SOC teams reduce alert fatigue, accelerate investigations, and move from fragmented signals to validated action. The platform connects to the security tools an organization already uses, including SIEM, EDR/XDR, identity, email, cloud, network, threat intelligence, ITSM, and endpoint systems. It brings alerts, evidence, cases, automation, forensics, reporting, and response workflows into one governed SecOps operating layer. At the center of Imperum is Autonomous SOC, the AI-driven intelligence layer of the platform. Imperum’s AI agents can triage alerts, collect evidence, enrich indicators, correlate related activity, prioritize cases, recommend next steps, and support response workflows. Analysts stay in control of critical actions, with approvals, audit trails, and case records preserved throughout the process. Imperum is designed to solve common SOC challenges: Alert fatigue SOC teams often receive more alerts than they can investigate manually. Imperum helps reduce repetitive triage work by using AI-driven alert qualification, contextual enrichment, and prioritization. Slow investigations Investigations often require analysts to jump between many tools to gather evidence. Imperum brings relevant context into a structured investigation workflow, helping teams move faster from alert to finding. Tool switching Security data is usually spread across SIEM, EDR, XDR, NDR, identity, email, cloud, and threat intelligence tools. Imperum connects these systems and turns their data into a unified investigation and case workflow. Inconsistent case handling Different analysts and shifts may investigate similar incidents in different ways. Imperum supports repeatable triage, case management, evidence collection, reporting, and approval workflows. Limited analyst capacity Senior SOC expertise is scarce, and junior analysts often need support to handle complex investigations. Imperum’s AI agents help complete repeatable investigation steps and surface relevant evidence so analysts can focus on higher-value decisions. Hard-to-prove SOC outcomes SOC leaders need visibility into what was investigated, what was decided, what action was taken, and why. Imperum maintains case records, audit trails, performance dashboards, and reporting workflows to support operational visibility and accountability. MSSP and MDR scaling challenges Managed security providers need to deliver consistent service quality across many customer environments. Imperum supports multi-tenant operations, tenant isolation, customer-specific workflows, and scalable service delivery. Imperum includes capabilities for: * Autonomous alert triage * AI-driven investigation * Case management and prioritization * Threat enrichment * Endpoint investigation and forensics * Visual playbook automation * AI agents and AI Assistant * Agentic AI Studio for custom agent workflows * MCP Gateway for governed tool access * Connector marketplace and integrations * Reporting, auditability, and operational dashboards * Multi-tenant MSSP/MDR operations * Cloud, on-premises, hybrid, and air-gapped deployment models Unlike basic automation tools that depend mainly on static playbooks, Imperum uses AI agents that work with operational context, evidence, historical activity, entity relationships, and approved workflows. This allows security teams to investigate more alerts without giving up control over sensitive response actions. Imperum is built for security teams that need more SOC capacity, faster investigation, better case prioritization, and stronger operational control. From alert noise to validated action, Imperum helps teams bring evidence, context, verdict, action, and auditability into one SecOps workflow.

Who Is the Company Behind Imperum?

  • Seller: Imperum
  • Year Founded: 2021
  • HQ Location: Amsterdam
  • LinkedIn® Page: www.linkedin.com
    35 employees on LinkedIn®
Opsei

Opsei is an Agentic AI that unifies your AI Chatbot, AI Receptionist, CRM, customer service, and business workflows into one system.

Who Is the Company Behind Opsei?

  • Seller: Wodely
  • Year Founded: 2014
  • HQ Location: Sydney, AU
  • LinkedIn® Page: www.linkedin.com
    5 employees on LinkedIn®

Port0

Who Is the Company Behind Port0?

  • Seller: Port0
  • Year Founded: 2025
  • HQ Location: N/A
  • LinkedIn® Page: www.linkedin.com
    12 employees on LinkedIn®

Prisma AIRS

The Prisma AIRS platform secures all apps, agents, models and data from development to deployment. AI Model Security-Enable the safe adoption of third-party AI models by scanning them for vulnerabilities and secure your AI ecosystem against risks such as model tampering, malicious scripts and deserialization attacks. AI Red Teaming-Uncover potential exposure and lurking risks before bad actors do. Perform automated penetration tests on your AI apps and models using our Red Teaming agent that stress tests your AI deployments, learning and adapting like a real attacker. AI Posture Management-Gain comprehensive visibility into your AI ecosystem to prevent excessive permissions, sensitive data exposure, platform misconfigurations, access misconfigurations and more. AI Runtime Security-Protect your LLM-powered AI apps, models and data against runtime threats such as prompt injection, malicious code, toxic content, sensitive data leaks, resource overload, hallucinations and more. AI Agent Security-Secure AI agents — including those built on no-code/low-code platforms — against new agentic threats such as identity impersonation, memory manipulation and tool misuse.

Who Is the Company Behind Prisma AIRS?

  • Seller: Palo Alto Networks
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Prophet Security

Powered by Agentic AI, Prophet Security’s AI SOC Platform enhances SecOps productivity and lowers risks by autonomously triaging, investigating, and responding to every alert or security event. Prophet AI eliminates the manual, repetitive work that slows down security operations. Analysts stay focused on high-value decisions and threat response, while the platform handles the heavy lifting. What makes Prophet AI different? Coverage: Prophet Security provides comprehensive coverage across all of your security alerts, including custom detections. Prophet AI is data agnostic, which means it can investigate and respond to alerts regardless of whether the data is in the SIEM, native security tool, cloud storage, or a data lake like they're in your native security tool (EDR, IDP) or in the SIEM Depth of Investigation: Speed adds little value if the investigation is superficial. Prophet AI replicates the investigative process of an expert analyst, asking the same probing questions a human would to make a determination. It goes beyond simple summarization to conduct a rigorous forensic examination of every alert. Accuracy: Prophet AI is designed for measurable precision. It allows you to establish a baseline for accuracy by comparing its output against your team's historical analysis. Crucially, the system demonstrates calibration by identifying when it is uncertain, flagging ambiguous cases for human review rather than guessing at a definitive answer. Transparency and Explainability: Consequential decisions require clear reasoning. Prophet AI demonstrates exactly how it reached a conclusion through step-by-step logic, cited evidence, and a replayable investigation timeline. These explanations serve as a contract for accountability, allowing auditors and senior analysts to validate the work instantly. Adaptability: Static models degrade over time, but Prophet AI functions as a learning system. It actively incorporates analyst feedback; when a human corrects a verdict or adds context, the model updates its approach for future alerts. This "human-on-the-loop" dynamic builds trust and ensures the system aligns more closely with your organizational policies and nuance over time. Security and privacy: Sensitive data is never used to train or fine-tune LLMs, preventing leakage and ensuring security. Single tenant architecture ensures an extra layer of security.

Who Is the Company Behind Prophet Security?

  • Seller: Prophet Security
  • Company Website:
  • Year Founded: 2024
  • HQ Location: Atherton, California, United States
  • LinkedIn® Page: www.linkedin.com
    41 employees on LinkedIn®
Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated April 9, 2026