Pulse Security AI
Who Is the Company Behind Pulse Security AI?
- Seller: Pulse Security AI
- Year Founded: 2025
- HQ Location: Los Altos, US
-
LinkedIn® Page: www.linkedin.com
16 employees on LinkedIn®
Total Products under this Category: 99
Last updated: September 26, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
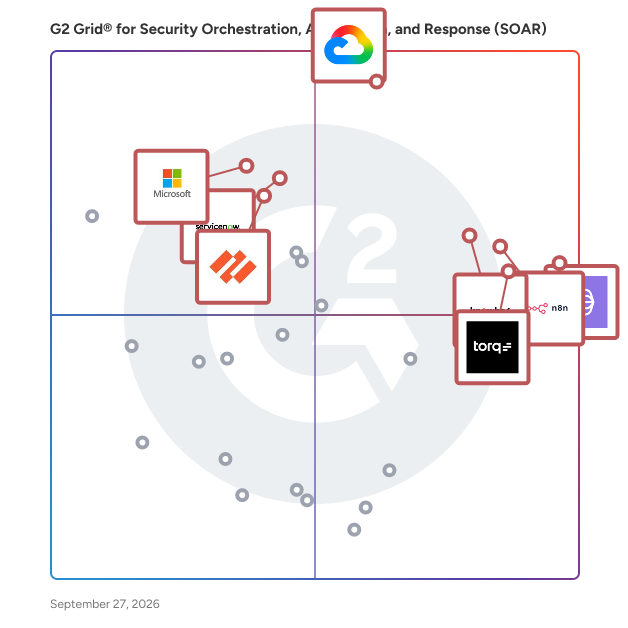
Highlighted products: Google Security Operations, Tines Stories, n8n, Torq AI SOC Platform, KnowBe4 PhishER/PhishER Plus, ServiceNow Security Operations, Microsoft Sentinel, and Palo Alto Cortex XSIAM.
Underlying data: [Grid® JSON](https://www.g2.com/categories/security-orchestration-automation-and-response-soar/grids.json?focus%5B%5D=google-security-operations&focus%5B%5D=tines-stories&focus%5B%5D=n8n&focus%5B%5D=torq-ai-soc-platform&focus%5B%5D=knowbe4-phisher-phisher-plus&focus%5B%5D=servicenow-security-operations&focus%5B%5D=microsoft-sentinel&focus%5B%5D=palo-alto-cortex-xsiam)
Revelstoke radically simplifies security orchestration, automation and response (SOAR), so security teams can work faster, smarter and more effectively. With a low-code, drag-and-drop interface, dozens of built-in integrations, incredible visibility into performance metrics, and robust reporting capabilities, Revelstoke empowers analysts to stop threats fast, and gives security leaders a clear picture on the business impact of security operations.
Agentic AI video monitoring for RAD devices and third-party camera systems. Verify incidents, trigger deterrence, and orchestrate response from detection to resolution. ⤷ 2026 SIA New Product Showcase Winner – Commercial Monitoring Solutions: Inside Immix ⤷ 2025 SIA New Product Showcase Winner – Threat Detection and Response ⤷ 2025 SIA Judges’ Choice Winner – SARA (Speaking Autonomous Responsive Agent)
SecPortal is an AI-native security orchestration platform that automates vulnerability remediation, incident response, penetration testing workflows, and compliance management. It uses AI to analyze security findings, generate remediation actions, and orchestrate workflows from detection to resolution. Security teams use SecPortal to centralize operations, automate remediation, and accelerate security workflows with intelligent automation.
Securaa (SOAR + TIP + CSAM) Securaa is a Comprehensive No Code Security Automation Platform that blends intelligence, risk-based asset management, vulnerability insights, automation and incident response into a single platform enabling SOC’s to reduce cybersecurity response time significantly and increase throughput manifolds. Securaa provides a single pane of glass to get alerts from various sources such as SIEM, EPP, NDR, EDR, UBA, CSP, as well as configuration issues and vulnerabilities. Securaa works as the primary technology for SOC teams to automate day to day investigation, triage, enrich and response activities. Key Features : Securaa is a cutting-edge SOAR platform designed to enhance security operations through automation and contextual intelligence. Its No-Code Build Your Integrations (BYI) enables unlimited integrations across security and infrastructure products within hours, offering unparalleled flexibility. With over 1,000 automated tasks and playbooks, Securaa orchestrates and responds to security alerts efficiently, enabling rapid deployment and configuration in just days—no programming skills required. Securaa’s proprietary Threat Intelligence Platform (TIP) enriches incident analysis with data from 20+ open-source and commercial feeds, while Cybersecurity Asset Management (CSAM) provides internal organizational context by converging asset repositories, vulnerability scanners, and exploit data. This unique combination ensures comprehensive situational awareness, including risk scoring and proactive coverage gap identification. The platform offers real-time dashboards, customizable via a No-Code framework, delivering actionable insights and boosting productivity. Its native multi-tenancy supports MSPs with a single console to manage multiple engagements seamlessly. Securaa’s features, such as risk scoring, asset exploration, playbooks, and case management, have helped clients automate L1 tasks, reduce alert response time by 95%, and enhance analyst productivity by 300%. It’s a game-changer for agile, efficient, and risk-oriented security operations.
Security Flow is a hybrid Security Orchestration, Automation, and Response solution designed to empower security analysts by automating time-consuming tasks without the need for coding expertise. By integrating diverse security and IT tools, Security Flow enhances operational efficiency, reduces alert fatigue, and enables teams to focus on high-value activities. Key Features and Functionality: - Visual Interface: Offers an intuitive, flow-based environment that allows users to create and manage automation workflows seamlessly. - Extensive Plugin Library: Provides a wide range of plugins to integrate with various security and IT products, facilitating comprehensive automation capabilities. - Broadcast Event Mechanism: Utilizes broadcast actions to decouple workflows from plugins, enabling flexible and efficient event handling across multiple scenarios. - Extensibility: Allows power users to execute Python and JavaScript scripts, offering the flexibility to extend functionality and integrate with custom or less common services. - Professional Services Support: Includes professional service hours with licenses to assist in implementation and customization, ensuring optimal value from existing and future software installations. Primary Value and Problem Solved: Security Flow addresses the challenges of alert fatigue and staffing shortages in security operations by automating routine and complex incident management tasks. This automation decreases the window of vulnerability, ensures repeatable responses, and maintains comprehensive action tracking. By leveraging Security Flow, organizations can fully utilize their existing security and IT portfolios, achieving faster return on investment and enhanced overall performance.
SEKOIA provides Consulting, Expertise and Innovation in cybersecurity to respond to the challenges of a VUCA world.
SentinelOne Purple AI is an advanced AI cybersecurity analyst designed to enhance security operations by automating and accelerating threat detection, investigation, and response. By integrating generative AI, Purple AI empowers security teams to manage complex threats more efficiently, reducing response times and improving overall security posture. Key Features and Functionality: - Automated Threat Detection: Utilizes AI-driven analysis to identify and assess potential security threats in real-time. - Accelerated Incident Investigation: Streamlines the investigation process by providing comprehensive insights and context for detected threats. - Enhanced Response Capabilities: Facilitates rapid and informed decision-making to mitigate risks effectively. - Integration with SentinelOne Platform: Seamlessly works within the SentinelOne ecosystem, ensuring cohesive security management. Primary Value and User Benefits: Purple AI addresses the challenges of modern cybersecurity by automating routine tasks, allowing security teams to focus on strategic initiatives. It reduces the time and effort required for threat detection and response, thereby minimizing potential damage from cyber incidents. By leveraging generative AI, Purple AI enhances the efficiency and effectiveness of security operations, providing organizations with a robust defense against evolving cyber threats.
Average Rating: 4.8/5.0
Total Reviews: 2
"Super-Fast Threat Detection with Actionable Alerts and Insights"
Rating: 5.0/5.0 stars
— Verified User in Legal Services
"SentinelOne Purple AI Makes Security Investigations Faster and Clearer"
Rating: 4.5/5.0 stars
— Verified User in Information Technology and Services
Defines organizational security posture. Determines type, level, volume of sources. Collects, collates, correlates and analyzes telemetry data. Overlays cyber threat intelligence. Derives actionable cyber security intelligence. Cyber security incident response & remediation.
Average Rating: 4.5/5.0
Total Reviews: 1
"Essential EDR Tool To Secure Your Valuable Assets"
Rating: 4.5/5.0 stars
— Wai Yan P.
Shield Sphere by Raptas is an advanced cybersecurity platform that unifies SIEM, SOAR, IOC, threat intelligence, and compliance automation into a single intelligent command center. Designed to replace 5–15 fragmented tools, it delivers real-time threat detection, automated incident response, and continuous compliance monitoring. With role-based dashboards for CXOs, CISOs, and SOC teams, Shield Sphere provides clarity across operations, risk, and governance. Features include AI-powered query builder, dark web monitoring, multi-framework compliance automation, and board-ready reporting. Deployed in hours, Shield Sphere reduces costs by 50% while enhancing visibility, resilience, and executive confidence in enterprise-wide security operations.
Sola is a self serve cybersecurity platform that enables teams to build, deploy, and manage custom security solutions without heavy engineering overhead. It allows organizations to address a wide range of security use cases through flexible, app based workflows, making security faster to implement and easier to scale.
