Sam For Compliance
EXPERTS IN STANDARDS COMPLIANCE AND CYBERSECURITY
Who Is the Company Behind Sam For Compliance?
- Seller: Sam For Compliance
- HQ Location: N/A
-
LinkedIn® Page: www.linkedin.com
1 employees on LinkedIn®
Total Products under this Category: 212
Last updated: September 01, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
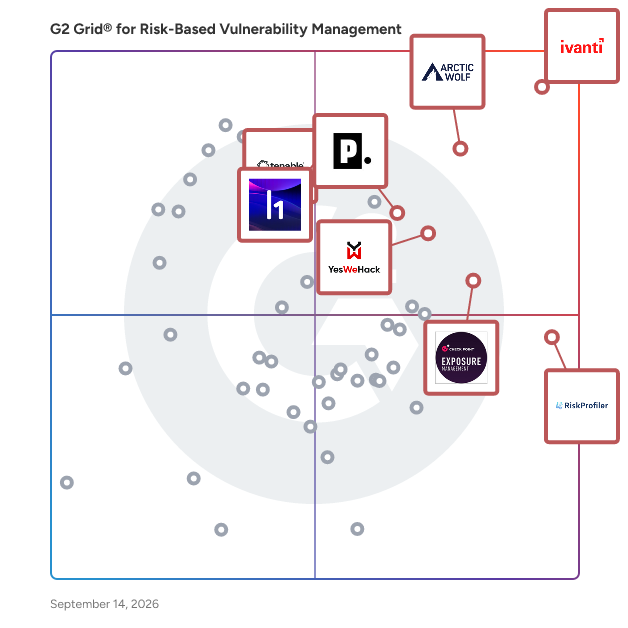
Highlighted products: Ivanti Neurons for Unified Endpoint Management, Arctic Wolf, Tenable Vulnerability Management, RiskProfiler - External Threat Exposure Management, YesWeHack, Pentera, Check Point Exposure Management, and H1 Platform.
Underlying data: [Grid® JSON](https://www.g2.com/categories/risk-based-vulnerability-management/grids.json?focus%5B%5D=ivanti-neurons-for-unified-endpoint-management&focus%5B%5D=arctic-wolf&focus%5B%5D=tenable-vulnerability-management&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=yeswehack&focus%5B%5D=pentera&focus%5B%5D=check-point-exposure-management&focus%5B%5D=h1-platform)
EXPERTS IN STANDARDS COMPLIANCE AND CYBERSECURITY
Your OPERATIONAL TECHNOLOGY (OT) NETWORK and associated IT network is your castle, protecting your business operations. Whilst traditional Security Information and Event Management (SIEM) solutions provide intelligence on castle occupant activities, the Sapien Vulnerability Management, Threat Management and managed Security Operations Centre offerings provide you with a continuous assessment of your castle’s battlement weaknesses and defensive readiness, as well as actionable intelligence on any threat to your network
Scan Ninja is a vulnerability management and compliance automation platform that ingests security scan data, prioritizes remediation based on risk and exploitability, and generates audit‑ready evidence for frameworks such as SOC 2 and PCI DSS. It integrates with native and third‑party scanners, tracks remediation through closure, and produces time‑stamped compliance artifacts and executive reporting.
SCYTHE is an adversary emulation platform (BAS+) catering to the commercial, government, and cybersecurity consulting market. The SCYTHE platform empowers Red, Blue, and Purple teams to swiftly construct and simulate real-world attacks. SCYTHE serves as a robust proactive security tool for scrutinizing detective and preventive controls across multiple communication vectors. Through SCYTHE, with its prepackaged action/behavior logic and threat intelligence, organizations can maintain a continuous evaluation of their risk profile, prioritize vulnerabilities, and take action against threats that matter.
Average Rating: 4.5/5.0
Total Reviews: 1
"Purple Teaming for the People"
Rating: 4.5/5.0 stars
— Verified User in Banking
Seconize enables enterprises to manage their cyber risks through its continuous predictive risk intelligence technology Seconize DeRisk Center is an automated and continuous IT risk and compliance management SaaS product that proactively identifies weak points in the enterprise IT infrastructure, prioritizes the risks based on the impact so that optimal investments can be made to minimize exposure.
Securin Exposure brings vulnerability and exposure data from existing security tools into a single normalized, deduplicated view, giving security teams one place to understand risk across internal infrastructure, cloud environments, applications, and other assets. Rather than replacing scanners, it works across the existing security stack to turn fragmented findings into a prioritized remediation workflow. Exposure prioritizes vulnerabilities using more than severity scores. It combines asset criticality and business context with Securin's vulnerability and threat intelligence, including exploit availability, active exploitation, ransomware associations, and threat-actor activity. This helps teams distinguish the exposures attackers are most likely to use from the much larger exposure backlog and focus remediation where it can reduce the most risk. Security teams can organize assets by business importance, track exposure age and remediation progress, and use role-based dashboards and reporting to give analysts, engineers, executives, and auditors the information relevant to their roles. Securin VERA, the platform's embedded AI reasoning agent, correlates assets, exposures, and live threat intelligence to answer questions about vulnerabilities, identify affected assets, surface priority exposures, and generate remediation-ready context. Exposure also connects prioritization directly to remediation. Through integrations with ticketing and security tools, teams can move prioritized exposures into existing operational workflows, track them through closure, and measure how exposure changes over time. The result is a scanner-neutral approach to Unified Vulnerability Management that helps organizations move from collecting vulnerability findings to making defensible remediation decisions and demonstrating measurable risk reduction.
Vulnerability Management allows you to discover vulnerabilities in your network easily. It advises solving these weak spots and securing your environment without installing agents. Goodbye, vulnerabilities, and Shadow IT! Security is a continuous process. Our Vulnerability Management enables you to log your actions to solve vulnerabilities. It will also show when vulnerabilities were found or solved. An audit trail helps you in your next audit or when an incident occurs.
SentinelOne's Singularity Vulnerability Management is an advanced solution designed to identify, assess, and remediate vulnerabilities across enterprise environments. By integrating seamlessly with SentinelOne's Singularity platform, it offers real-time visibility into potential security weaknesses, enabling organizations to proactively address threats before they can be exploited. Key Features and Functionality: - Comprehensive Vulnerability Assessment: Conducts thorough scans to detect vulnerabilities in applications and operating systems. - Real-Time Monitoring: Provides continuous surveillance to identify and alert on emerging threats. - Automated Remediation: Offers tools to automatically patch or mitigate identified vulnerabilities, reducing manual intervention. - Integration with Singularity Platform: Ensures cohesive operation with SentinelOne's broader security ecosystem for unified threat management. Primary Value and Problem Solved: Singularity Vulnerability Management empowers organizations to proactively manage and mitigate security vulnerabilities, reducing the risk of breaches and ensuring compliance with industry standards. By automating the detection and remediation processes, it minimizes the window of exposure to potential exploits, thereby enhancing the overall security posture of the enterprise.
Siemba is an AI-driven Continuous Threat Exposure Management (CTEM) platform that helps enterprises, government agencies, and growing organizations discover, prioritize, and fix critical vulnerabilities across their entire attack surface. Security teams use Siemba to build and mature CTEM programs without requiring deep hacking expertise or constant human intervention. The platform brings together four integrated capabilities on a single unified interface: Penetration Testing as a Service (PTaaS) for expert-led manual pen testing on demand; GenPT for AI-native Dynamic Application Security Testing (DAST) that simulates real-world attack techniques against web applications and APIs; GenVA for AI-driven vulnerability assessment that continuously scans and scores risks across your environment; and EASM for External Attack Surface Management that maps and monitors all external-facing assets, including shadow IT and exposed infrastructure. Together these capabilities deliver actionable intelligence across the full CTEM lifecycle, from asset discovery and attack surface mapping through to risk prioritization, validation, and remediation guidance. Security leaders gain the visibility, speed, and scalability needed to run continuous offensive security programs and generate strategic insights that maximize Return on Mitigation. Siemba is trusted by enterprises, global systems integrators, and government agencies looking to consolidate their offensive security tooling, reduce exposure windows, and demonstrate measurable security improvement over time.
Average Rating: 4.7/5.0
Total Reviews: 5
"Great end to end tool for visibility and alerts for small teams"
Rating: 4.5/5.0 stars
— Mevin B.
"Powerful All-in-One Solution for Lean Teams"
Rating: 5.0/5.0 stars
— Arun C.
Silobreaker is a technology company that builds solutions that unify data, contextual analysis, and human expertise to deliver decision-grade intelligence when and where it matters most. Continually refined for both leadership and analysts operating across business resilience, enterprise security, threat, and risk disciplines, the Silobreaker intelligence layer uses a proprietary search and entity database to automate the production of intelligence across cyber, geopolitical, and physical domains. Using Silobreaker's priority intelligence requirements (PIR)-driven workflows, agentic automation, MCP-enabled integrations, and executive-ready reporting, governments and global enterprises can anticipate threats, protect assets and people, accelerate decision-making, and steer through uncertainty with confidence.
Average Rating: 4.3/5.0
Total Reviews: 2
Rating: 4.0/5.0 stars
— Lalith K.
"Good DWM dark web monitoring tool"
Rating: 4.5/5.0 stars
— Aman P.
Software Vulnerability Manager allows you to identify, prioritize and remediate software vulnerabilities rapidly to dramatically reduce risk to your organization. Gain visibility over software vulnerabilities affecting your environment, and automate patch management tasks to accelerate your ability to respond to vulnerabilities. Enjoy security advisories covering more third-party software than any solution on the market, and prioritize and patch quickly leveraging the power of threat intelligence coupled with the largest third-party patch catalog on the market.
Average Rating: 4.5/5.0
Total Reviews: 2
AI-generated summary from verified user reviews
"SVM Offers a Novel Approach to 3rd Party Patch Management and Vulnerability Research"
Rating: 4.0/5.0 stars
— Verified User in Higher Education
"Powerful Solution for Proactive Vulnerability Management"
Rating: 5.0/5.0 stars
— Vladimirs P.
SecOps deserve better than raw cloud telemetry. Most tools patch over noise, ignoring the state of your cloud. We fix the root cause. Stream turns raw cloud telemetry into a stateful real-time model, powering risk-based detection and response.
Our team of TechGuardians are highly educated and certified professionals who have utilized their extensive IT security experience to support both Fortune 500 businesses and multiple governmental agencies. We take a unique approach to protecting your critical infrastructure.
