Best Attack Surface Management Software - Page 12

How Many Attack Surface Management Software Products Does G2 Track?

Total Products under this Category: 189

Category Stats (Sep 2026)

  • Average Rating: 4.6/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Hunto AI (+2.02%) - Among all products in this category, Hunto AI recorded the largest rating increase compared to last month

Last updated: September 26, 2026

How Does G2 Rank Attack Surface Management Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,900+ Authentic Reviews
  • 189+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

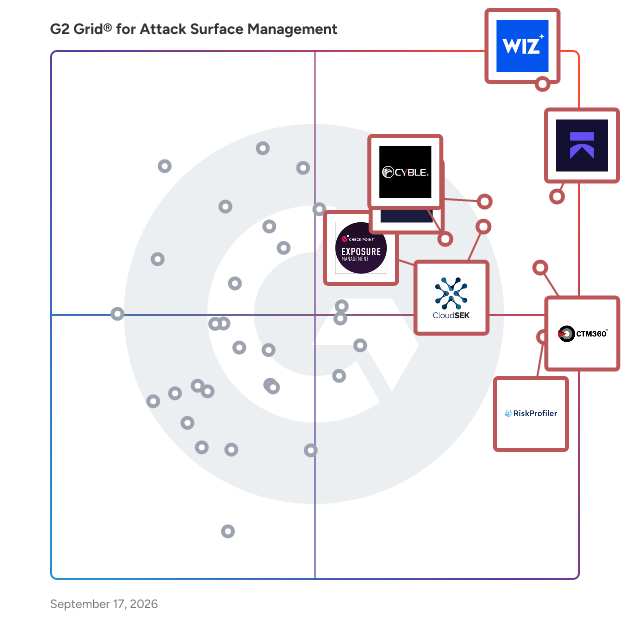
G2 Grid® for Attack Surface Management Software

G2 Grid® for  Attack Surface Management Software plotting products by satisfaction and market presence

Highlighted products: Wiz, Aikido Security, SOCRadar Extended Threat Intelligence, CTM360, CloudSEK, Cyble, RiskProfiler - External Threat Exposure Management, and Check Point Exposure Management.

Underlying data: [Grid® JSON](https://www.g2.com/categories/attack-surface-management/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=aikido-security&focus%5B%5D=socradar-extended-threat-intelligence&focus%5B%5D=ctm360-ctm360&focus%5B%5D=cloudsek&focus%5B%5D=cyble&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=check-point-exposure-management)

RiskXchange

RiskXchange provides continuous data-driven insights that help improve your cybersecurity rating and prevent security breaches. If you are looking to strengthen your cybersecurity rating and programme to prevent attacks and protect your data, then RiskXchange can help you!

Who Is the Company Behind RiskXchange?

RootVector Core

Offensive Security Intelligence. Designed for a Secure Tomorrow.

Who Is the Company Behind RootVector Core?

runZero

runZero provides a single source of truth for exposure management across your total attack surface. Without requiring agents, authentication, or appliances, runZero delivers the most complete and accurate visibility into every asset and exposure across internal, external, IT, OT, IoT, mobile, and cloud environments — including uncovering unknown and unmanageable devices and broad classes of exposures that evade traditional tools. Founded in 2018 by HD Moore, runZero is trusted by more than 500 companies and 30,000 users worldwide to mitigate risks faster, meet compliance requirements, and improve overall security.

Average Rating: 4.0/5.0

Total Reviews: 1

Who Is the Company Behind runZero?

  • Seller: runZero
  • Year Founded: 2018
  • HQ Location: Austin, US
  • Twitter: @runZeroInc
    2,443 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    84 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of runZero?

Ryft Security

See what attackers see. Ryft continuously discovers everything your organization has exposed to the internet, forgotten subdomains, misconfigured cloud buckets, abandoned admin panels, tests them for real vulnerabilities, and uses AI to validate which findings are actually actionable. External attack surface management, built for modern teams.

Who Is the Company Behind Ryft Security?

Securin External Attack Surface Management

Securin Surface is Securin’s External Attack Surface Management (EASM) solution that helps organizations discover, monitor, and prioritize internet-facing assets. It gives security teams complete visibility across domains, subdomains, IPs, cloud assets, and exposed services to complement and enhance internal CMDBs and security inventories. Through continuous outside-in discovery, Securin Surface identifies both known and unknown assets by analyzing DNS, certificate transparency, WHOIS, BGP data, and various other intelligence sources. Discovery is passive-first by default, with optional active probing for service-level visibility on owned assets, and requires no agents or credentials. It helps security teams uncover shadow IT, abandoned infrastructure, forgotten development systems, expired certificates, and assets introduced through mergers and acquisitions. To prioritize risk, Securin Surface enriches exposures with weaponization intelligence and ranks them based on active exploitation, public exploit code, ransomware association, and threat-actor activity. It also monitors deep and dark web sources for breached credentials tied to an organization’s domains and internet-facing assets, then maps those credentials back to the assets they could unlock. Every exposure routes into Securin Exposure with attribution, priority, and ownership pre-populated, so external risk enters the same remediation workflow as internal risk. Common use cases include shadow IT discovery, merger and acquisition due diligence, subsidiary and brand monitoring, external compliance validation, and continuous audit evidence collection. For security teams that need a clearer view of external exposure, Securin Surface combines discovery, attribution, exposure assessment, and credential monitoring in a single workflow.

Who Is the Company Behind Securin External Attack Surface Management?

  • Seller: Securin
  • Year Founded: 2021
  • HQ Location: Albuquerque, New Mexico, United States
  • Twitter: @Securin_io
  • LinkedIn® Page: www.linkedin.com
    242 employees on LinkedIn®

Sn1per Professional

Sn1per Professional is an all-in-one offensive security platform that provides a comprehensive view of your internal and external attack surface and offers an asset risk scoring system to prioritize, reduce, and manage risk. With Sn1per Professional, you can discover the attack surface and continuously monitor it for changes. It integrates with the leading open source and commercial security testing tools for a unified view of your data.

Average Rating: 4.5/5.0

Total Reviews: 1

Who Is the Company Behind Sn1per Professional?

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Sn1per Professional?

stacksciences

StackSciences provides a SaaS platform to centralize your #devops environment risk analysis, policy compliance and runtime enforcement. On a single view, you can measure your attack surface, view what you expose and prioritize your next actions to make your multi-cloud infrastructure more secure.

Who Is the Company Behind stacksciences?

SurveilX

Surveil-X helps businesses identify and understand their public-facing cybersecurity risks without installing software, writing code, or providing internal system access. Simply enter a company domain, and Surveil-X scans the security signals visible from the outside. Including website vulnerabilities, SSL and HTTPS issues, DNS configuration, email security protections such as SPF, DKIM, and DMARC, and potential credential exposure. The findings are grouped by severity and translated into clear, plain-language explanations with recommended next steps. Within minutes, businesses receive a professional, client-ready cyber risk report that can be used to prioritise security improvements, prepare for procurement reviews, answer client security questions, or demonstrate their external security posture to partners and investors. Surveil-X is designed for founders, SaaS teams, digital agencies, IT consultants, MSPs, and service providers that need fast security clarity before investing in a deeper penetration test or technical audit.

Who Is the Company Behind SurveilX?

swordeye

In late 2018, it developed the first product that provides one-time digital asset issuance, called SwordEye Recon. In this process, it served dozens of customers until 2020. Thanks to the feedback received from customers, it started to develop a new product that constantly monitors digital assets, gives alarms when necessary, and automatically discovers all sub-products and services connected to the domain. With the investment it received in the first quarter of 2020, it developed the SwordEye Attack Surface Monitoring product and started to offer a product that gives a risk letter grade with a unique risk score algorithm that explains the importance of the attack surface and offers solutions.

Who Is the Company Behind swordeye?

  • Seller: SwordSec
  • Year Founded: 2018
  • HQ Location: Ankara, TR
  • LinkedIn® Page: www.linkedin.com
    11 employees on LinkedIn®

Theatmate

Unified Attack Surface Management Built for MSPs ThreatMate empowers MSPs with a single platform to monitor, manage, and secure every attack surface—external, internal, and cloud—all from one powerful dashboard. Find and fix security exposures before adversaries do

Who Is the Company Behind Theatmate?

ThreatPort Security

ThreatPort is an External Attack Surface Management (EASM) and Cyber Threat Intelligence (CTI) platform built for security-conscious organizations that need continuous visibility into their digital exposure. ThreatPort automatically maps and monitors your organization's attack surface — including subdomains, open ports, SSL/TLS configurations, DNS security posture, web application vulnerabilities, and CVE/KEV matches — and delivers real-time alerts when new risks emerge. Attack Surface Management ThreatPort continuously scans your domain infrastructure to identify exposed assets before attackers do. From subdomain enumeration and open port detection to certificate expiry monitoring and misconfigured security headers, every layer of your external footprint is analyzed and scored. Threat Intelligence Stay ahead of emerging threats with integrated feeds from leading intelligence sources including VirusTotal, Shodan, AbuseIPDB, AlienVault OTX, URLhaus, MalwareBazaar, ThreatFox, and CISA's Known Exploited Vulnerabilities (KEV) catalog. ThreatPort correlates these feeds against your specific assets to surface only the threats that matter to your organization. AI-Powered Penetration Testing ThreatPort includes an autonomous AI pentest agent that performs real-world attack simulations against your web infrastructure — including endpoint discovery, vulnerability scanning with Nuclei, Nmap-based port analysis, and web security checks — all within a consent-gated, non-destructive framework. Remediation & Reporting Security findings are automatically prioritized by severity and mapped to actionable remediation steps. Shareable reports and PDF exports allow security teams to communicate risk to stakeholders without manual effort. Who Uses ThreatPort ThreatPort is designed for IT security teams, managed security service providers (MSSPs), and security-aware businesses that need enterprise-grade threat visibility without the complexity or cost of traditional EASM platforms. Whether you're conducting a security audit, preparing for a compliance review, or building a proactive security monitoring program, ThreatPort gives you the continuous intelligence you need to stay protected.

Who Is the Company Behind ThreatPort Security?

ThreatScope

ThreatScope is an external attack surface management platform built specifically for mid-market companies ($50M–$500M revenue). Unlike enterprise tools that cost six figures and require dedicated analysts, ThreatScope gives lean security teams continuous visibility into their internet-facing attack surface — with AI-powered findings anyone can understand. What it does: Discovers all internet-facing assets (subdomains, IPs, services, certificates) Continuously monitors for vulnerabilities and misconfigurations Cross-references findings with CISA's Known Exploited Vulnerabilities (KEV) catalog Maps threats to MITRE ATT&CK techniques Generates plain-English findings with step-by-step remediation Produces executive, technical, and compliance (NIST CSF) PDF reports What makes it different: Built for mid-market, not enterprise — simple pricing, no complexity AI-powered analysis explains findings in plain English Agentless — no software to install, no network access needed Threat intelligence from 6+ sources (CISA KEV, NVD, MITRE ATT&CK, OTX, Abuse.ch, GitHub Advisories) Includes attack surface discovery (subdomain enumeration, DNS, HTTP probing) Scheduled scans with email alerts for critical findings Pricing: Starting at $500/month (Starter: 5 domains, 10 IPs)

Who Is the Company Behind ThreatScope?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated April 10, 2026