Tenable
648 reviews
- 10 profiles
- 21 categories
Average star rating
4.5
#1 in 2 categories
Grid® leader
Serving customers since
Tenable Solutions
Discover ready-made solutions that bring related products, reviews, and resources together in one place.
Featured Products
Tenable Reviews

AF
Verified User in Food Production
Small-Business (50 or fewer emp.)Unified Exposure View That Makes Executive Risk Reporting Easy
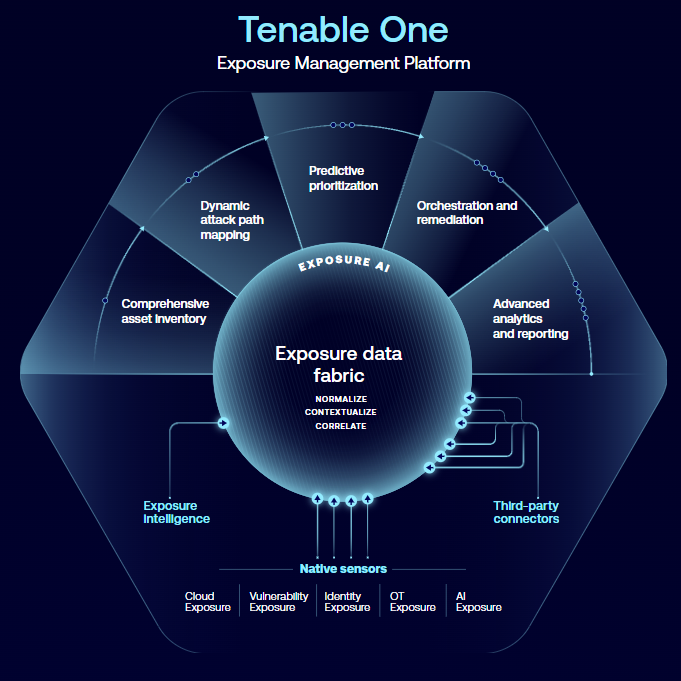
It brings vulnerability, cloud, identity, and OT exposure into a single view, which makes it much easier to explain overall risk to executives. The third-party connectors are a big plus: ingesting data from tools like CrowdStrike and Claroty xDome lets us enrich the asset inventory and build exposure views and dashboards that reflect the client’s real environment, not just Tenable’s own data.
AF
Verified User in Food Production
Small-Business (50 or fewer emp.)Excellent Scan Accuracy, Strong Plugin Coverage, and a Powerful API for Automation
Its plugin coverage and scan accuracy are excellent, and VPR makes prioritization much more realistic than relying on CVSS alone. The API is also a big strength: we’ve automated bulk creation of compliance scans and built custom reporting from exports, which saves us a lot of time when managing multiple clients at scale.
AC
Verified User in Computer & Network Security
Small-Business (50 or fewer emp.)Agentless AD & Entra ID Risk Visibility with Clear, Actionable Remediation
It gives clear, continuous visibility into Active Directory and Entra ID risk without installing agents on domain controllers. The Indicators of Exposure come with plain explanations and concrete remediation steps, which makes it easy to hand findings straight to AD admins. The Indicators of Attack add real-time detection of things like DCSync and Kerberoasting, and it fits well alongside the rest of the Tenable platform.
About
What is Tenable?
Tenable, the Exposure Management company, empowers organizations to understand and reduce cyber risk.
Details
Ownership
NASDAQ: TENB
Website
www.tenable.com