Best Attack Surface Management Software - Page 13

How Many Attack Surface Management Software Products Does G2 Track?

Total Products under this Category: 195

Category Stats (Oct 2026)

  • Average Rating: 4.59/5 (↓0.01 vs Sep 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: ThreatConnect Risk Quantifier (+1.46%) - Among all products in this category, ThreatConnect Risk Quantifier recorded the largest rating increase compared to last month

Last updated: October 26, 2026

How Does G2 Rank Attack Surface Management Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,100+ Authentic Reviews
  • 195+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

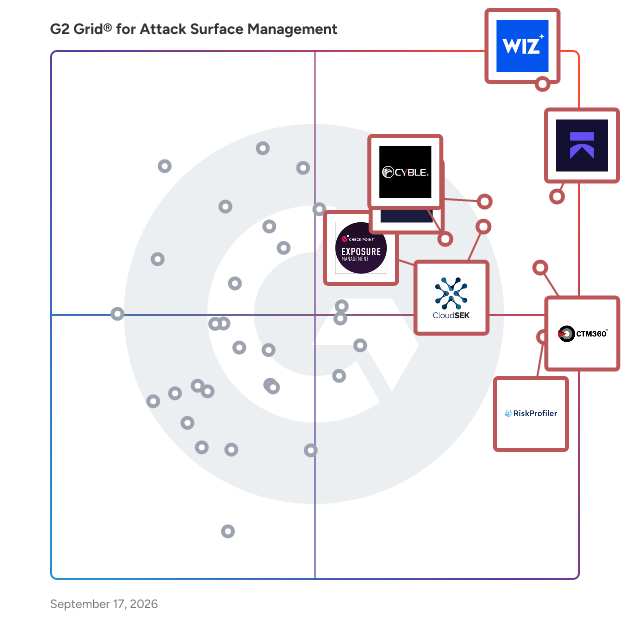
G2 Grid® for Attack Surface Management Software

G2 Grid® for  Attack Surface Management Software plotting products by satisfaction and market presence

Highlighted products: Wiz, Aikido Security, SOCRadar Extended Threat Intelligence, CTM360, CloudSEK, Cyble, RiskProfiler - External Threat Exposure Management, and Check Point Exposure Management.

Underlying data: [Grid® JSON](https://www.g2.com/categories/attack-surface-management/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=aikido-security&focus%5B%5D=socradar-extended-threat-intelligence&focus%5B%5D=ctm360-ctm360&focus%5B%5D=cloudsek&focus%5B%5D=cyble&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=check-point-exposure-management)

SurveilX

Surveil-X helps businesses identify and understand their public-facing cybersecurity risks without installing software, writing code, or providing internal system access. Simply enter a company domain, and Surveil-X scans the security signals visible from the outside. Including website vulnerabilities, SSL and HTTPS issues, DNS configuration, email security protections such as SPF, DKIM, and DMARC, and potential credential exposure. The findings are grouped by severity and translated into clear, plain-language explanations with recommended next steps. Within minutes, businesses receive a professional, client-ready cyber risk report that can be used to prioritise security improvements, prepare for procurement reviews, answer client security questions, or demonstrate their external security posture to partners and investors. Surveil-X is designed for founders, SaaS teams, digital agencies, IT consultants, MSPs, and service providers that need fast security clarity before investing in a deeper penetration test or technical audit.

Who Is the Company Behind SurveilX?

swordeye

In late 2018, it developed the first product that provides one-time digital asset issuance, called SwordEye Recon. In this process, it served dozens of customers until 2020. Thanks to the feedback received from customers, it started to develop a new product that constantly monitors digital assets, gives alarms when necessary, and automatically discovers all sub-products and services connected to the domain. With the investment it received in the first quarter of 2020, it developed the SwordEye Attack Surface Monitoring product and started to offer a product that gives a risk letter grade with a unique risk score algorithm that explains the importance of the attack surface and offers solutions.

Who Is the Company Behind swordeye?

  • Seller: SwordSec
  • Year Founded: 2018
  • HQ Location: Ankara, TR
  • LinkedIn® Page: www.linkedin.com
    11 employees on LinkedIn®

Theatmate

Unified Attack Surface Management Built for MSPs ThreatMate empowers MSPs with a single platform to monitor, manage, and secure every attack surface—external, internal, and cloud—all from one powerful dashboard. Find and fix security exposures before adversaries do

Who Is the Company Behind Theatmate?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

ThreatPort Security

ThreatPort is an External Attack Surface Management (EASM) and Cyber Threat Intelligence (CTI) platform built for security-conscious organizations that need continuous visibility into their digital exposure. ThreatPort automatically maps and monitors your organization's attack surface — including subdomains, open ports, SSL/TLS configurations, DNS security posture, web application vulnerabilities, and CVE/KEV matches — and delivers real-time alerts when new risks emerge. Attack Surface Management ThreatPort continuously scans your domain infrastructure to identify exposed assets before attackers do. From subdomain enumeration and open port detection to certificate expiry monitoring and misconfigured security headers, every layer of your external footprint is analyzed and scored. Threat Intelligence Stay ahead of emerging threats with integrated feeds from leading intelligence sources including VirusTotal, Shodan, AbuseIPDB, AlienVault OTX, URLhaus, MalwareBazaar, ThreatFox, and CISA's Known Exploited Vulnerabilities (KEV) catalog. ThreatPort correlates these feeds against your specific assets to surface only the threats that matter to your organization. AI-Powered Penetration Testing ThreatPort includes an autonomous AI pentest agent that performs real-world attack simulations against your web infrastructure — including endpoint discovery, vulnerability scanning with Nuclei, Nmap-based port analysis, and web security checks — all within a consent-gated, non-destructive framework. Remediation & Reporting Security findings are automatically prioritized by severity and mapped to actionable remediation steps. Shareable reports and PDF exports allow security teams to communicate risk to stakeholders without manual effort. Who Uses ThreatPort ThreatPort is designed for IT security teams, managed security service providers (MSSPs), and security-aware businesses that need enterprise-grade threat visibility without the complexity or cost of traditional EASM platforms. Whether you're conducting a security audit, preparing for a compliance review, or building a proactive security monitoring program, ThreatPort gives you the continuous intelligence you need to stay protected.

Who Is the Company Behind ThreatPort Security?

ThreatScope

ThreatScope is an external attack surface management platform built specifically for mid-market companies ($50M–$500M revenue). Unlike enterprise tools that cost six figures and require dedicated analysts, ThreatScope gives lean security teams continuous visibility into their internet-facing attack surface — with AI-powered findings anyone can understand. What it does: Discovers all internet-facing assets (subdomains, IPs, services, certificates) Continuously monitors for vulnerabilities and misconfigurations Cross-references findings with CISA's Known Exploited Vulnerabilities (KEV) catalog Maps threats to MITRE ATT&CK techniques Generates plain-English findings with step-by-step remediation Produces executive, technical, and compliance (NIST CSF) PDF reports What makes it different: Built for mid-market, not enterprise — simple pricing, no complexity AI-powered analysis explains findings in plain English Agentless — no software to install, no network access needed Threat intelligence from 6+ sources (CISA KEV, NVD, MITRE ATT&CK, OTX, Abuse.ch, GitHub Advisories) Includes attack surface discovery (subdomain enumeration, DNS, HTTP probing) Scheduled scans with email alerts for critical findings Pricing: Starting at $500/month (Starter: 5 domains, 10 IPs)

Who Is the Company Behind ThreatScope?

Tresal

Tresal is a European cybersecurity platform that provides visibility into your external attack surface. It scans and monitors internet-facing assets and cloud environments, including domains, IPs, storage buckets, and misconfigured services. Tresal offers real-time alerts, risk-based prioritization, and actionable remediation guidance. Built for lean teams, it simplifies attack surface management without the complexity of enterprise tools.

Who Is the Company Behind Tresal?

  • Seller: Tresal
  • Year Founded: 2024
  • HQ Location: Amsterdam, NL
  • LinkedIn® Page: linkedin.com
    3 employees on LinkedIn®

Trickest Platform

Trickest provides an innovative approach to offensive cybersecurity automation, assets, and vulnerability discovery. The platform combines extensive adversary tactics and techniques with full transparency, hypercustomization, and hyperscalability, making it the go-to platform for offensive security operations. The Trickest platform comes with comprehensive tooling, scripting, managed infrastructure, scaling, ready-to-go solutions, and analytics, serving as a collaborative command center for Offensive Security, Penetration testing, Red teams, Security Analysts, and Security Service providers (MSSPs). What makes us different? Easy customization of logic, inputs, outputs, and integrations, making them adaptable to specific needs and thus producing superior-quality data compared to others. Some of the automation workflows and solutions that our customers deploy and execute: - Attack Surface Discovery - Vulnerability Scanning - Dynamic Application Security Testing (DAST) - Recon/Information Gathering (Passive & Active) - Organization OSINT - CVE scanning - Cloud Scanning - DNS recon & research - Subdomain Enumeration - Subdomain Takeover - Custom Security Automation and Orchestration Main components of the Trickest platform include: Solutions & Analytics - Ready-to-go and transparent solutions for Attack Surface Discovery, Vulnerability Scanning, Dynamic Application Security Testing (DAST), and Open-source intelligence OSINT, offering insight into every step of the process, easy customization, and Analytics on the top. The Builder - Access to 90+ workflow templates, 300+ open-source tools, Bash & Python scripting, CLI for building custom workflows to discover asset, vulnerabilities, scan network & apps, crawl, spider, enumerate, fuzz, bruteforce and much more. Hyperscalability - Whether scanning regional infrastructures with 100s of 1000s of assets or smaller organizational scopes, Trickest supports it all without per-asset costs.

Who Is the Company Behind Trickest Platform?

  • Seller: Trickest
  • Year Founded: 2020
  • HQ Location: Dover, US
  • LinkedIn® Page: www.linkedin.com
    12 employees on LinkedIn®

UltraRed

Continuous monitoring CTEM platform

Who Is the Company Behind UltraRed?

  • Seller: UltraRed
  • Year Founded: 2021
  • HQ Location: Tel Aviv, IL
  • LinkedIn® Page: www.linkedin.com
    23 employees on LinkedIn®

Uni5 Xposure

Uni5 Xposure brings together your most fragmented security data: assets, exploits, vulnerabilities, threat intel, and control gaps into one unified exposure map, revealing what’s truly at risk and what to fix first, fast.

Who Is the Company Behind Uni5 Xposure?

  • Seller: Hive Pro
  • Year Founded: 2019
  • HQ Location: Herndon, US
  • LinkedIn® Page: www.linkedin.com
    96 employees on LinkedIn®

Unisys Attack Surface Discovery

Technological advancements and evolving work habits are expanding the modern attack surface. Adversaries are using AI to rapidly scan and breach networks, making it critical for organizations to identify and mitigate vulnerabilities before they can be exploited. The Unisys Attack Surface Discovery solution scans your modern attack surface, analyzes the results, and reports on insights augmented with risk quantification in business context. Your IT resources can focus on what matters most to your business while gaining visibility into unknown assets, exposure discovery, and contextual threat intelligence.

Who Is the Company Behind Unisys Attack Surface Discovery?

  • Seller: Unisys
  • HQ Location: Blue Bell, PA
  • Twitter: @unisys
    33,730 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,518 employees on LinkedIn®
  • Ownership: NYSE:UIS
  • Total Revenue (USD mm): $2,820

VerifiedThreat

VerifiedThreat (VT) transforms raw threat intelligence into active validation. By deploying autonomous, situational AI agents that chain vulnerabilities exactly like a human hacker, VT stress-tests your external attack surface in real-time—safely providing hard empirical proof, erasing false positives, and automatically updating your compliance ledger at the network edge

Who Is the Company Behind VerifiedThreat?

watchTowr

watchTowr is the Preemptive Exposure Management platform built for AI-driven attack timelines. Attackers now weaponize new vulnerabilities in hours; the average enterprise still takes 43 days to remediate (DBIR 2026). The watchTowr Platform closes that gap by autonomously validating what an attacker can actually reach across your external estate, then mitigating it at the edge, so you answer "are we affected?" in hours, not weeks. Fully external and completely autonomous, the Platform sees your organization exactly as a real threat actor does: no agents, no inside knowledge, no assumptions. It was built by the people who spent decades red-teaming banks, governments and regulators, and it is trusted by Fortune 500 companies, governments, banks, insurers and critical infrastructure providers all over the world. Key features and functionality - watchTowr Intel (Instinct and Attacker Eye): Real-time attacker telemetry from a global honeypot network, combined with proactive vulnerability research from watchTowr Labs, flags which emerging threats are actually being exploited in the wild and which will be next. - Adversary Sight: Continuous external attack surface reconnaissance that discovers and monitors 100+ asset types, including unknown SaaS, cloud, subsidiaries, and shadow IT, using the same techniques real attackers use. - AI-Powered Automated Red Teaming: Validates exploitability against your live estate using real attacker tactics across every MITRE ATT&CK Initial Access vector. Every finding is validated and proven to be exploitable - not theoretical. - AI-Powered Rapid Reaction: The hour a threat emerges, the Platform re-tests your estate and tells you whether you are exposed and where, before in-the-wild exploitation reaches you. - Active Defense: Autonomous mitigation that pushes ready-to-use rules to the WAFs, firewalls, IPS, and IDS you already run, protecting exposed systems while permanent fixes are underway. - Enterprise reporting and integrations: Validated, prioritized findings with proof of exploitability, delivered through dashboards, API, and the ticketing and workflow tools your teams already use. Primary value and problem solved Your exposure changes weekly. Annual penetration tests, self-reported questionnaires and scanners that list theoretical vulnerabilities cannot describe what an attacker can reach today, and they cannot keep pace with exploitation timelines that keep shrinking. The watchTowr Platform runs one continuous loop, from attacker signal to validated exposure to autonomous mitigation, so security teams stop triaging maybes and act only on what is exploitable. The result is a materially smaller exposure window, fewer false positives, and independent proof of your posture for boards, regulators, and cyber insurers.

Who Is the Company Behind watchTowr?

  • Seller: watchTowr
  • Year Founded: 2021
  • HQ Location: Singapore, SG
  • LinkedIn® Page: www.linkedin.com
    53 employees on LinkedIn®

Xhield.tech

Xhield is an AI-powered Continuous Attack Surface Intelligence platform developed by SkureCloud Infosec Pvt Ltd. It helps organizations discover, analyze, prioritize, and remediate cybersecurity risks across applications, open-source dependencies, cloud infrastructure, and interconnected digital assets. Unlike traditional security solutions that produce isolated vulnerability alerts, Xhield uses a Unified Attack Surface Graph (T-UASG) to correlate vulnerabilities, assets, configurations, and potential attack paths. Powered by Graph Neural Networks (GNNs) and Agentic AI, Xhield focuses on contextual risk prioritization, exploitability intelligence, and actionable remediation guidance. Our mission is to transform fragmented security visibility into continuous, intelligence-driven cyber resilience.

Who Is the Company Behind Xhield.tech?

Zscaler Asset Exposure Management (CAASM)

Zscaler Asset Exposure Management gives organizations a complete, accurate, and context-rich inventory of all their cyber assets - across endpoints, cloud, and on-prem environments - to dramatically reduce risk. Built upon the Data Fabric for Security, Asset Exposure Management brings together data from across your security stack, deduplicates it, enriches it with additional context, and groups related entities together. This enables customers to uncover unknown or misconfigured assets, identify coverage gaps, and ensure critical controls are in place. This unified visibility streamlines compliance, supports risk mitigation workflows, and empowers security teams to quickly address coverage gaps. Ultimately, Asset Exposure Management is essential for effective cybersecurity and proactive attack surface management. Key Features and Benefits: • Unified Asset Inventory: Gain a single, accurate view of all assets by consolidating data from 200+ connectors, enabling organizations to trust their asset records and reduce blind spots. • Coverage Gap Identification: Pinpoint missing controls and misconfigurations across assets, allowing security teams to proactively close gaps and strengthen their security posture. • Automated Risk Mitigation Workflows: Initiate and track automated tasks to mitigate policy violation risk, ensure faster issue resolution, and minimize organizational risk before issues can be corrected. • Continuous CMDB Enrichment: Automatically update your CMDB with missing assets and critical details, increasing confidence in inventory accuracy and supporting compliance. • Comprehensive Reporting and Dashboards: Generate robust reports and custom dashboards, fostering cross-team collaboration and supporting audit and compliance efforts."

Who Is the Company Behind Zscaler Asset Exposure Management (CAASM)?

  • Seller: Zscaler
  • Year Founded: 2008
  • HQ Location: San Jose, California
  • Twitter: @zscaler
    17,676 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    9,150 employees on LinkedIn®
  • Ownership: NASDAQ:ZS
Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated April 10, 2026