Tenable
648 reviews
- 10 profiles
- 21 categories
Average star rating
4.5
#1 in 2 categories
Grid® leader
Serving customers since
Tenable Solutions
Discover ready-made solutions that bring related products, reviews, and resources together in one place.
Featured Products
Tenable Reviews

AJ
Aarti J.
Senior Secops consultantEnterprise (> 1000 emp.)Smooth SIEM Integration and Standout Agents
The agents and their smooth integration with the SIEM stand out the most for me.

IC
Verified User in Computer & Network Security
Mid-Market (51-1000 emp.)Comprehensive Vulnerability Scanning with Actionable Remediation Guidance
What I like most about Nessus is its comprehensive vulnerability scanning engine and the depth of information provided in scan results. We regularly use authenticated scans, compliance audits, and scheduled vulnerability assessments to identify security weaknesses across servers, network devices, and Linux systems. The remediation guidance included with each finding is particularly valuable because it helps our team quickly understand the risk and determine the appropriate corrective action.
JA
José Martín A.
Subdirector Seguridad Aplicativa (Especialista Senior)Enterprise (> 1000 emp.)Strong Vulnerability Validation and Prioritization, Even in Software Dependencies
I appreciate the ability to validate vulnerabilities, including those that show up in software dependencies—for example, embedded Java components within Control-M Agent or Veritas.
About
What is Tenable?
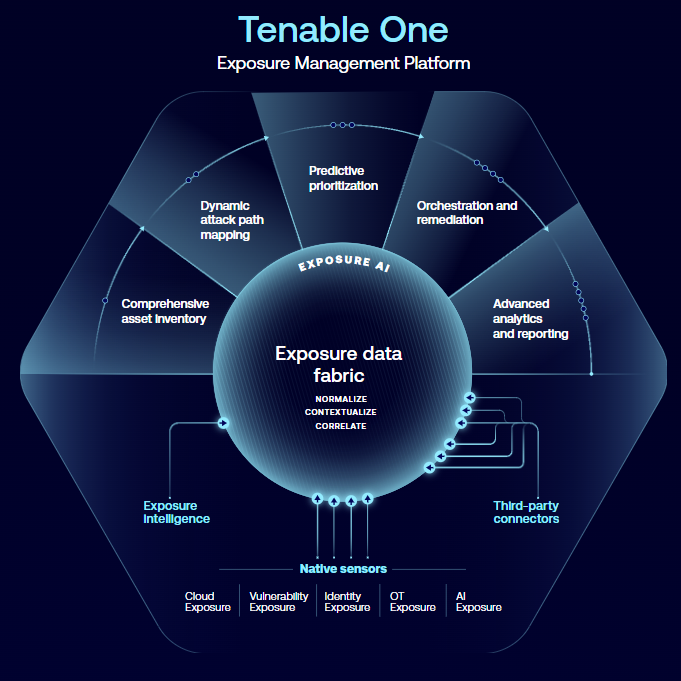
Tenable, the Exposure Management company, empowers organizations to understand and reduce cyber risk.
Details
Ownership
NASDAQ: TENB
Website
www.tenable.com