Tenable
648 reviews
- 10 profiles
- 21 categories
Average star rating
4.5
#1 in 2 categories
Grid® leader
Serving customers since
Tenable Solutions
Discover ready-made solutions that bring related products, reviews, and resources together in one place.
Featured Products
Tenable Reviews
SS
Salvatore S.
Cyber Resilience SpecialistEnterprise (> 1000 emp.)Flexible Vulnerability Visibility, but Plugin Gaps Delay Analysis
I use Tenable Vulnerability Management to scan our company asset inventory and keep an updated, categorized list of findings. I rely on it for complete visibility across our perimeter and as a central source of truth for finding vulnerable software versions on our servers and misconfigurations in server deployments. I especially like the flexibility in tagging, scan options, and VPR scoring, which helps us make informed decisions about vulnerability patching and prioritization.

AG
Verified User in Government Administration
Mid-Market (51-1000 emp.)Easy-to-Use Cloud Vulnerability Scanning with Reliable Performance and Fast Support
It’s very easy to use and really helpful for identifying vulnerabilities. Scheduling scans is convenient and straightforward. Because it’s a cloud product, management is rarely an issue, and it receives automatic updates. Integration has been simple as well—we just need to whitelist the scanner IPs. It’s been reliable for us, so overall performance has been solid. Pricing isn’t bad either, and it seems to be widely used. Whenever I need help, I reach out to support, and they respond quickly and assist. We don’t have an AI/intelligence feature in the product yet, but I’m looking forward to that. Its smart in a way when it decides which plugins to try automatically on whichever server is responding.
AC
Verified User in Computer & Network Security
Mid-Market (51-1000 emp.)Fast, Lightweight Scanning with Clear Results and Actionable Dashboards
Various scanning options whether it be agent, on prem scanner or Cloud scanners.
Scan results are extremely useful and plugin output makes it clear as to why the vulnerability has been identified.
The reports and dashboards make it easy to visualize the data in Tenable.
Remediation projects make it easy to divvy out vulnerabilities to the relevant teams.
Azure data connector makes it easy to get a full asset inventory.
Scans, especially agent-based scans are fast and lightweight.
Onboarding is fairly quick and easy, the nice UI makes it easier to navigate.
Vulnerability intelligence allows me to see what CVEs are being exploited in the wild, allowing me to focus on those patches first.
About
What is Tenable?
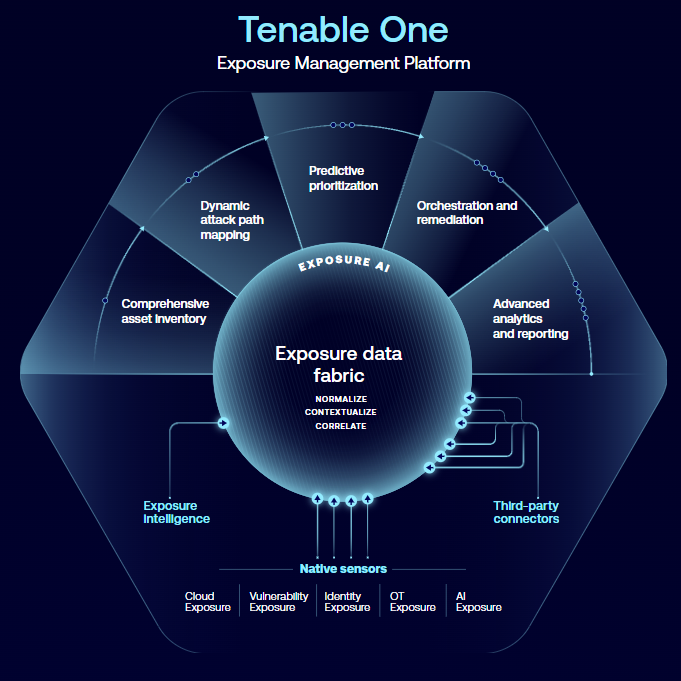
Tenable, the Exposure Management company, empowers organizations to understand and reduce cyber risk.
Details
Ownership
NASDAQ: TENB
Website
www.tenable.com