Best Vulnerability Scanner Software for Small Business

How Many Vulnerability Scanner Software Products Does G2 Track?

Total Products under this Category: 235

Category Stats (Sep 2026)

  • Average Rating: 4.59/5 (↑0.01 vs Aug 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Armis (+0.18%) - Among all products in this category, Armis recorded the largest rating increase compared to last month

Last updated: September 01, 2026

How Does G2 Rank Vulnerability Scanner Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 7,900+ Authentic Reviews
  • 235+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

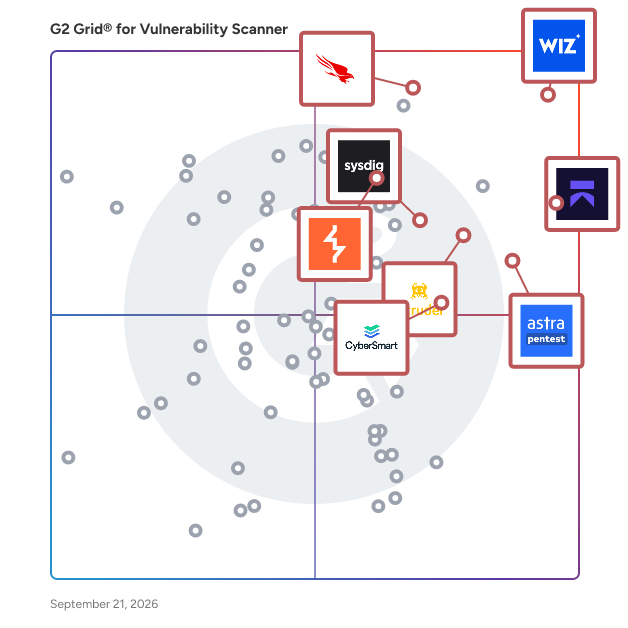
G2 Grid® for Vulnerability Scanner Software

G2 Grid® for Vulnerability Scanner Software plotting products by satisfaction and market presence

Highlighted products: Aikido Security, Wiz, Astra Pentest, CrowdStrike Falcon Cloud Security, Intruder, Sysdig Secure, Burp Suite, and CyberSmart.

Underlying data: [Grid® JSON](https://www.g2.com/categories/vulnerability-scanner/grids.json?focus%5B%5D=aikido-security&focus%5B%5D=wiz-wiz&focus%5B%5D=astra-pentest&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=intruder&focus%5B%5D=sysdig-sysdig-secure&focus%5B%5D=burp-suite&focus%5B%5D=cybersmart&segment=small-business)

Aikido Security

Aikido Security is the developer-first security platform that unifies code, cloud, protection, and attack testing in one suite of best-in-class products. Built by developers for developers, Aikido helps teams of any size ship secure software faster, automate protection, and simulate real-world attacks with AI-driven precision. The platform’s proprietary AI cuts noise by 95%, delivers one-click fixes, and saves developers 10+ hours per week. Aikido Intel proactively uncovers vulnerabilities in open source packages before disclosure, helping secure more than 50,000 organizations worldwide, including Revolut, Niantic, Visma, Montblanc, and GoCardless.

Average Rating: 4.6/5.0

Total Reviews: 263

How Do G2 Users Rate Aikido Security?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Detection Rate: 9.0/10 (Category avg: 9.0/10)
  • Automated Scans: 9.0/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.1/10 (Category avg: 8.5/10)

Who Is the Company Behind Aikido Security?

  • Seller: Aikido Security
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Ghent, Belgium
  • Twitter: @AikidoSecurity
    11,770 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    320 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Founder, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 78% Small, 15% Medium

What Do G2 Reviewers Say About Aikido Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Aikido Security, thanks to its clear insights and seamless integration.
  • Users appreciate Aikido Security's robust security capabilities, providing a comprehensive and seamless integration in their workflow.
  • Users value the intuitive dashboard of Aikido Security, which simplifies security issue identification and management.
  • Users value the easy integrations of Aikido Security, enhancing workflows with seamless connections to existing GitLab repositories.
  • Users find Aikido's easy setup highly efficient, enabling quick implementation and immediate usability for security assessments.
Cons
  • Users note the lack of advanced features in Aikido Security, such as dark mode and in-depth analysis options.
  • Users find the pricing structure expensive for micro businesses, making upgrades difficult to justify.
  • Users note the limited features of Aikido Security, wishing for more customization and advanced options.
  • Users find the pricing issues challenging, especially for micro businesses, due to the steep upgrade costs.
  • Users feel Aikido Security is lacking features like advanced reporting and deeper compliance analysis compared to competitors.

What Are Recent G2 Reviews of Aikido Security?

Astra Pentest

Astra Security is a leading continuous penetration testing platform that combines AI-powered autonomous pentesting with certified expert-led assessments. Powered by Attack AI, trained on 6.8M+ security findings and insights from 5,000+ real-world pentests. Astra deploys intelligent agents that continuously discover, validate, prioritize, and help remediate vulnerabilities at scale. While AI handles speed and scale, Astra’s certified security experts focus on what automation alone cannot: complex business logic flaws, multi-step attack chains, advanced exploit paths, and emerging AI/LLM-specific threats. Built for modern engineering teams, Astra integrates directly into CI/CD workflows, enabling continuous security validation between releases instead of relying on outdated annual pentests. The platform delivers comprehensive Autonomous Pentest powered by AI agents, DAST vulnerability scanner and human-driven pentests across web apps, AI/LLMs, mobile apps, APIs, cloud infrastructure. Astra is CREST-accredited, CERT-IN empaneled, and a PCI ASV-certified vendor. Our team also led the development of the OWASP APTS framework, helping shape the industry standard for continuous security testing. Today, 1,500+ organizations across 70+ countries trust Astra Security, including Ford, Loom, CompTIA, Hitachi, HackerRank, and OLX.

Average Rating: 4.6/5.0

Total Reviews: 242

G2 Deal: For G2 users: 10% off across all pentest plans

Avail Astra Pentest at 10% off, our comprehensive pentest suite scans for 8000+ security tests including OWASP Top 10, SANS 25, known CVEs & security best practices. This offer is exclusive to G2 users!

Price: ~~$5999~~ → $5400

View this exclusive G2 deal

How Do G2 Users Rate Astra Pentest?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Detection Rate: 8.7/10 (Category avg: 9.0/10)
  • Automated Scans: 8.9/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.7/10 (Category avg: 8.5/10)

Who Is the Company Behind Astra Pentest?

  • Seller: ASTRA IT, Inc.
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Bengaluru, IN
  • Twitter: @getastra
    694 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    154 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, CEO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 66% Small, 28% Medium

What Do G2 Reviewers Say About Astra Pentest?

AI-generated summary from verified user reviews

Pros
  • Users commend Astra Pentest's excellent customer support, noting their responsiveness and flexibility throughout the process.
  • Users praise the comprehensive vulnerability detection of Astra Pentest, which simplifies tracking and prioritizing security issues.
  • Users appreciate the user-friendly interface of Astra Pentest, enhancing their experience with clear and efficient vulnerability management.
  • Users commend Astra Pentest for its efficient scanning and penetration testing, enhancing security preparedness and team responsiveness.
  • Users value the vulnerability identification of Astra Pentest, enhancing confidence in security and business growth.
Cons
  • Users report poor customer support with Astra Pentest, noting slow email responses and lack of instant messaging options.
  • Users find the poor interface design of Astra Pentest frustrating, leading to confusion and difficulties in usage.
  • Users report slow performance with Astra Pentest, citing delays in results and instability during use.
  • Users find the UI challenging, particularly with note-taking and clarity on rescan needs during pentests.
  • Users face a lack of information with Astra Pentest, as documentation and updates are often insufficient or slow to arrive.

What Are Recent G2 Reviews of Astra Pentest?

What Are G2 Users Discussing About Astra Pentest?

Wiz

Wiz transforms cloud security for customers – including more than 50% of the Fortune 100 – by enabling a new operating model. With Wiz, organizations can democratize security across the development lifecycle, empowering them to build fast and securely. Its Cloud Native Application Protection Platform (CNAPP) consolidates CSPM, KSPM, CWPP, Vulnerability management, IaC scanning, CIEM, DSPM into a single platform. Wiz drives visibility, risk prioritization, and business agility. Protecting Your Cloud Environments Requires a Unified, Cloud Native Platform. Wiz connects to every cloud environment, scans every layer, and covers every aspect of your cloud security - including elements that normally require installing agents. Its comprehensive approach has all of these cloud security solutions built in. Hundreds of organizations worldwide, including 50 percent of the Fortune 100, to rapidly identify and remove critical risks in cloud environments. Its customers include Salesforce, Slack, Mars, BMW, Avery Dennison, Priceline, Cushman & Wakefield, DocuSign, Plaid, and Agoda, among others. Wiz is backed by Sequoia, Index Ventures, Insight Partners, Salesforce, Blackstone, Advent, Greenoaks, Lightspeed and Aglaé. Visit https://www.wiz.io for more information.

Average Rating: 4.7/5.0

Total Reviews: 841

How Do G2 Users Rate Wiz?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Detection Rate: 8.8/10 (Category avg: 9.0/10)
  • Automated Scans: 9.0/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.8/10 (Category avg: 8.5/10)

Who Is the Company Behind Wiz?

  • Seller: Wiz
  • Company Website:
  • Year Founded: 2020
  • HQ Location: New York, US
  • Twitter: @wiz_io
    24,733 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,147 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CISO, Security Engineer
  • Top Industries: Financial Services, Computer Software
  • Company Size: 53% Large, 39% Medium

What Do G2 Reviewers Say About Wiz?

AI-generated summary from verified user reviews

Pros
  • Users value the robust APIs and user-friendly UI, appreciating ongoing improvements and a wealth of insightful issues.
  • Users value the continuous enhancement of security features by Wiz, appreciating the support and innovation in their tool.
  • Users appreciate the ease of use of Wiz, benefiting from its user-friendly interface and seamless integration.
  • Users value the comprehensive visibility Wiz provides, enhancing security and prioritizing essential aspects of their cloud environment.
  • Users appreciate the easy setup of Wiz, enabling a quick and seamless integration into their workflows.
Cons
  • Users find a significant learning curve in mastering Wiz's extensive features, which can hinder initial usage.
  • Users find the feature limitations of Wiz frustrating, especially with complex management and reporting challenges.
  • Users note that improvement is needed for laggy query responses and better dashboard reporting capabilities.
  • Users identify improvements needed in dashboard reporting and feature streamlining for better usability and budgeting.
  • Users find the interface overwhelming initially, facing a steep learning curve and complex licensing issues.

What Are Recent G2 Reviews of Wiz?

CrowdStrike Falcon Cloud Security

Crowdstrike Falcon Cloud Security is the only CNAPP to stop breaches in the cloud Built for today’s hybrid and multi-cloud environments, Falcon Cloud Security protects the entire cloud attack surface - from code to runtime - by combining continuous agentless visibility with real-time detection and response. At runtime, Falcon Cloud Security delivers best-in-class cloud workload protection and real-time cloud detection and response (CDR) to stop active threats across hybrid environments. Integrated with the CrowdStrike Falcon platform, it correlates signals across endpoint, identity, and cloud to detect sophisticated cross-domain attacks that point solutions miss—enabling teams to respond faster and stop breaches in progress. To reduce risk before attacks occur, Falcon Cloud Security also delivers agentless-driven posture management that proactively shrinks the cloud attack surface. Unlike typical solutions, Crowdstrike enriches cloud risk detections with adversary intelligence and graph-based context, enabling security teams to prioritize exploitable exposures and prevent breaches before they happen. Customers using Falcon Cloud Security consistently see measurable results: 89% faster cloud detection and response 100x reduction in false positives by prioritizing exploitable, business-critical risk 83% reduction in cloud security licenses due to elimination of redundant tools

Average Rating: 4.5/5.0

Total Reviews: 216

How Do G2 Users Rate CrowdStrike Falcon Cloud Security?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.2/10)
  • Detection Rate: 8.6/10 (Category avg: 9.0/10)
  • Automated Scans: 9.7/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 9.2/10 (Category avg: 8.5/10)

Who Is the Company Behind CrowdStrike Falcon Cloud Security?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • Twitter: @CrowdStrike
    110,809 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 48% Large, 33% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their protection in cloud environments.
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their cloud security management significantly.
  • Users value the real-time detection efficiency of CrowdStrike Falcon Cloud Security for enhanced cloud threat management.
  • Users value the real-time vulnerability detection of CrowdStrike Falcon Cloud Security, enhancing proactive risk management and security.
  • Users appreciate the ease of use of CrowdStrike Falcon Cloud Security, making it a top choice for cloud cybersecurity.
Cons
  • Users find CrowdStrike Falcon Cloud Security to be expensive, particularly challenging for small businesses with budget constraints.
  • Users face issues with alert fatigue and response lag, calling for improved prioritization and better support resources.
  • Users experience alert fatigue and desire improved response times and better training resources for CrowdStrike Falcon.
  • Users find the feature complexity of CrowdStrike Falcon Cloud Security can overwhelm new users and necessitate a learning curve.
  • Users report a challenging learning curve with CrowdStrike Falcon, especially for those unfamiliar with similar tools.

What Are Recent G2 Reviews of CrowdStrike Falcon Cloud Security?

Intruder

Intruder's continuous exposure management platform helps security, IT, and engineering teams stop breaches before they start. By unifying AI penetration testing, attack surface monitoring, cloud security, and vulnerability management in one intuitive platform, Intruder gives stretched teams an always-on security source of truth. Our approach focuses on continuous automated scanning using expertise and agentic solutions to ensure that the findings we deliver are accurate, prioritized by real-world risk, and ready to act on. Founded in 2015 by Chris Wallis, a former ethical hacker turned corporate blue teamer, Intruder is now protecting over 3,000 companies worldwide. Intruder has been awarded multiple accolades, was selected for GCHQ’s Cyber Accelerator, included on Deloitte’s Tech Fast 50 2023 list as the fastest-growing cybersecurity company in the UK and was named in G2’s 2026 Best Software Awards.

Average Rating: 4.8/5.0

Total Reviews: 220

How Do G2 Users Rate Intruder?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.2/10)
  • Detection Rate: 9.3/10 (Category avg: 9.0/10)
  • Automated Scans: 9.5/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 9.5/10 (Category avg: 8.5/10)

Who Is the Company Behind Intruder?

  • Seller: Intruder
  • Company Website:
  • Year Founded: 2015
  • HQ Location: London
  • Twitter: @intruder_io
    979 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, Director
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 56% Small, 37% Medium

What Do G2 Reviewers Say About Intruder?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Intruder, with quick setup and intuitive system design enhancing their experience.
  • Users value the clarity and prioritization of Intruder's findings, enabling effective risk management and actionable insights.
  • Users value the quick and efficient customer support from Intruder, enhancing their overall scanning experience.
  • Users appreciate the intuitive interface of Intruder, finding it easy to set up and navigate.
  • Users value the efficient vulnerability identification from Intruder, enhancing their cybersecurity management effortlessly.
Cons
  • Users find the product expensive due to high costs for add-ons and fees per endpoint scanned.
  • Users find the slow scanning process frustrating, leading to inefficiencies and missed vulnerabilities during security assessments.
  • Users find licensing issues challenging, particularly regarding costs and constraints that affect system configurations.
  • Users experience false positives which can obscure the detection of critical vulnerabilities in security monitoring.
  • Users find the limited features of Intruder less accommodating for specific reporting and customization needs.

What Are Recent G2 Reviews of Intruder?

What Are G2 Users Discussing About Intruder?

Sysdig Secure

Sysdig Secure is the real-time cloud-native application protection platform (CNAPP) trusted by organizations of all sizes around the world.. Built by the creators of Falco and Wireshark, Sysdig uniquely delivers runtime-powered visibility and agentic AI to stop cloud attacks instantly, not after the damage is done. With Sysdig, you can: - Stop threats in 2 seconds and respond in minutes - Cut vulnerability noise by 95% with runtime prioritization - Detect real risk instantly across workloads, identities, and misconfigurations - Close permissions gaps in under 2 minutes Sysdig Secure consolidates CSPM, CWPP, CIEM, vulnerability management, and threat detection into a single open, real-time platform. Unlike other CNAPPs, Sysdig connects signals across runtime, identity, and posture to eliminate blind spots, reduce tool sprawl, and accelerate innovation without compromise. No guesswork. No black boxes. Just cloud security, the right way. Learn more at https://sysdig.com

Average Rating: 4.8/5.0

Total Reviews: 110

How Do G2 Users Rate Sysdig Secure?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.2/10)
  • Detection Rate: 9.5/10 (Category avg: 9.0/10)
  • Automated Scans: 9.5/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 9.5/10 (Category avg: 8.5/10)

Who Is the Company Behind Sysdig Secure?

  • Seller: Sysdig
  • Company Website:
  • Year Founded: 2013
  • HQ Location: San Francisco, California
  • Twitter: @Sysdig
    10,284 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    562 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Engineer
  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 47% Large, 40% Medium

What Do G2 Reviewers Say About Sysdig Secure?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the robust security features of Sysdig Secure, providing real-time threat detection and vulnerability insights.
  • Users value the real-time threat detection capabilities of Sysdig Secure, enhancing their security for cloud-native environments.
  • Users appreciate the real-time vulnerability detection of Sysdig Secure, aiding in effective risk prioritization and threat management.
  • Users value the real-time threat detection of Sysdig Secure, enhancing security for cloud-native applications and environments.
  • Users value the comprehensive visibility provided by Sysdig Secure, enhancing security and compliance across environments.
Cons
  • Users face feature limitations with Sysdig Secure, including outdated documentation and challenging integration processes.
  • Users find the complexity during initial setup a challenge, especially for those lacking technical expertise.
  • Users find missing features like runtime detection and tracing hinder sysdig's usability and integration with organizational systems.
  • Users note the difficult learning curve for Sysdig Secure, making it challenging for those unfamiliar with DevSecOps.
  • Users find the initial setup and configuration complex, leading to challenges in utilizing Sysdig Secure effectively.

What Are Recent G2 Reviews of Sysdig Secure?

What Are G2 Users Discussing About Sysdig Secure?

Burp Suite

Burp Suite is a complete ecosystem for web application and API security testing, combining two products: Burp Suite DAST - a best-of-breed, precision DAST solution that automates runtime testing, and Burp Suite Professional - the industry-standard toolkit for manual penetration testing. Developed by PortSwigger, more than 85,000 security professionals rely on Burp Suite to find, verify, and understand vulnerabilities across complex modern web applications. Burp Suite DAST is PortSwigger’s enterprise dynamic application security testing (DAST) solution, purpose-built for continuous, automated scanning of web applications and APIs. Unlike many DAST solutions, which are part of a wider AST offering, Burp Suite DAST is not a bolt-on tool - instead it’s precision-built from over 20 years of dynamic testing experience. Burp Suite DAST reveals the runtime issues that static analysis tools miss, such as authentication flaws, configuration drift, and chained vulnerabilities. Built on the same proprietary scanning engine that powers Burp Suite Professional, it delivers precise, low-noise results that security teams trust. Key capabilities of Burp Suite DAST include: Continuous, automated scanning of web applications and APIs, integration with CI/CD pipelines and vulnerability management tools, flexible deployment across cloud, and on-premise environments, shared scanning logic and configurations between automated and manual testing, accurate, low-noise detection informed by PortSwigger Research. Burp Suite Professional complements DAST with deep manual testing capability. It’s the industry-standard toolkit for penetration testers, consultants, and AppSec engineers who need complete insight and flexibility when validating or exploring vulnerabilities. Findings discovered by DAST can be investigated and verified in Burp Suite Professional, ensuring every result is accurate, contextual, and actionable. Together, Burp Suite DAST and Burp Suite Professional create a unified ecosystem that delivers automation at breadth and manual depth where it counts. Burp Suite is built for AppSec teams who need scalable, trustworthy coverage across web and API environments, enabling a seamless handoff between automated and manual testing.

Average Rating: 4.8/5.0

Total Reviews: 126

How Do G2 Users Rate Burp Suite?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.2/10)
  • Detection Rate: 8.6/10 (Category avg: 9.0/10)
  • Automated Scans: 8.6/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.0/10 (Category avg: 8.5/10)

Who Is the Company Behind Burp Suite?

  • Seller: PortSwigger
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Knutsford, GB
  • Twitter: @Burp_Suite
    138,186 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    345 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Cyber Security Analyst
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 41% Medium, 31% Small

What Do G2 Reviewers Say About Burp Suite?

AI-generated summary from verified user reviews

Pros
  • Users enjoy the user-friendly interface of Burp Suite, making navigation and analysis straightforward for all skill levels.
  • Users highlight the user-friendly interface of Burp Suite, making it easy to navigate and utilize effectively.
  • Users value the deep automation and manual testing capabilities of Burp Suite for effective security assessments.
  • Users appreciate the control and visibility Burp Suite offers, with powerful tools for effective web application testing.
  • Users praise Burp Suite for its clear, user-friendly interface that simplifies web application penetration testing for both beginners and experts.
Cons
  • Users find Burp Suite to be expensive, particularly for the professional version, which may limit accessibility for some users.
  • Users report slow performance with Burp Suite, particularly on lower-end systems during extensive scanning tasks.
  • Users find the steep learning curve of Burp Suite challenging, especially beginners navigating its complex features and tools.
  • Users find the steep learning curve in Burp Suite challenging, particularly for beginners adjusting to its complex setup.
  • Users find the limited customization in Burp Suite restricts exploration, especially for beginners and independent learners.

What Are Recent G2 Reviews of Burp Suite?

What Are G2 Users Discussing About Burp Suite?

Tenable Nessus

Built for security practitioners, by security professionals, Nessus products by Tenable are the de-facto industry standard for vulnerability assessment. Nessus performs point-in-time assessments to help security professionals quickly and easily identify and fix vulnerabilities, including software flaws, missing patches, malware, and misconfigurations - across a variety of operating systems, devices, and applications. With features such as pre-built policies and templates, customizable reporting, group “snooze” functionality, and real-time updates, Nessus is designed to make vulnerability assessment simple, easy, and intuitive. The result: less time and effort to assess, prioritize, and remediate issues.

Average Rating: 4.5/5.0

Total Reviews: 296

How Do G2 Users Rate Tenable Nessus?

  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.2/10)
  • Detection Rate: 8.9/10 (Category avg: 9.0/10)
  • Automated Scans: 9.0/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.4/10 (Category avg: 8.5/10)

Who Is the Company Behind Tenable Nessus?

  • Seller: Tenable
  • Company Website:
  • HQ Location: Columbia, MD
  • Twitter: @TenableSecurity
    87,752 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,361 employees on LinkedIn®
  • Ownership: NASDAQ: TENB

Who Uses This Product?

  • Who Uses This: Security Engineer, Network Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Medium, 33% Large

What Do G2 Reviewers Say About Tenable Nessus?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the extensive vulnerability identification capabilities of Tenable Nessus, enhancing their security risk management efforts.
  • Users value the comprehensive vulnerability detection in Tenable Nessus, enhancing their ability to manage security risks effectively.
  • Users praise the automated scanning of Tenable Nessus for its thoroughness and comprehensive vulnerability reporting.
  • Users value the ease of use of Tenable Nessus, appreciating its simple setup and user-friendly interface.
  • Users value the extensive reporting and automation capabilities of Tenable Nessus for better asset scanning.
Cons
  • Users note that slow scanning can take 2-3 days and may disrupt production environments due to high resource usage.
  • Users highlight the high costs of maintaining Tenable Nessus, which can be a barrier for many organizations.
  • Users find the limited features of Tenable Nessus restrictive, especially regarding host capacity and mobile app testing.
  • Users find the complexity of licensing and features in Tenable Nessus challenging, impacting overall usability and resource management.
  • Users report that false positives from Nessus can create additional workload and complicate vulnerability management processes.

What Are Recent G2 Reviews of Tenable Nessus?

What Are G2 Users Discussing About Tenable Nessus?

CyberSmart

CyberSmart is the UK’s leading cybersecurity platform for small and medium-sized businesses and the organisations that support them. As the UK’s largest provider of Cyber Essentials certification and a National Ambassador to the Cyber Resilience Centres network, CyberSmart plays a central role in raising cyber maturity across the UK economy. We work closely with businesses, managed service providers, and government-backed initiatives to deliver practical, scalable cybersecurity that aligns with real-world commercial pressures. A recognised market leader in delivering Cyber Essentials and Cyber Essentials Plus at scale, CyberSmart helps organisations achieve trusted certification quickly and maintain continuous compliance long after the audit is complete. As regulatory requirements, supply chain scrutiny, and insurance expectations continue to increase, businesses need more than a point-in-time assessment - they need ongoing assurance. The CyberSmart platform brings together people, process and technology in one integrated solution. It combines always-on device monitoring, vulnerability management, automated patch management, security awareness training, certification, privacy management and streamlined access to cyber insurance. By unifying protection and compliance within a single platform, CyberSmart reduces tool sprawl, simplifies security operations, and provides clear, prioritised visibility into risk. CyberSmart also supports larger organisations and supply-chain assurance programmes by enabling certification at scale across supplier tiers, providing executive-level visibility of supplier risk, and leveraging a network of over 1,000 MSP partners to drive adoption without disrupting commercial relationships. Trusted by over 7,000 businesses and partners worldwide, CyberSmart delivers Complete Cyber Confidence - helping organisations stay secure, demonstrate compliance, and build measurable resilience over time.

Average Rating: 4.4/5.0

Total Reviews: 60

How Do G2 Users Rate CyberSmart?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)
  • Detection Rate: 8.8/10 (Category avg: 9.0/10)
  • Automated Scans: 9.8/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 10.0/10 (Category avg: 8.5/10)

Who Is the Company Behind CyberSmart?

  • Seller: CyberSmart
  • Year Founded: 2016
  • HQ Location: London, GB
  • Twitter: @CyberSmartUK
    1,928 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    77 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 66% Small, 21% Medium

What Do G2 Reviewers Say About CyberSmart?

AI-generated summary from verified user reviews

Pros
  • Users praise the ease of use of CyberSmart, highlighting effortless setup and clear organization of device issues.
  • Users appreciate the responsive customer support of CyberSmart, finding it helpful and easy to access for all queries.
  • Users find CyberSmart to be extremely helpful, simplifying deployments and enhancing communication and device management.
  • Users appreciate the implementation ease of CyberSmart, noting its effortless initial setup and clear documentation.
  • Users value the effortless setup of CyberSmart, appreciating its minimal friction and streamlined installation process.
Cons
  • Users face technical issues with CyberSmart, including app stability, installation problems, and inaccurate account reports.
  • Users experience false positives in failures due to the app not staying open, complicating the usability of CyberSmart.
  • Users are concerned about the high costs of CyberSmart's CE+ audits compared to the time and value they provide.
  • Users find the pricing issues with CyberSmart concerning, especially with unexpected costs and value for time spent.
  • Users face improvement needs with CyberSmart, particularly concerning installation and inconsistent assessment feedback processes.

What Are Recent G2 Reviews of CyberSmart?

What Are G2 Users Discussing About CyberSmart?

Indusface WAS

Indusface WAS (Web Application Scanner) provides comprehensive managed dynamic application security testing (DAST) solution. It is a zero-touch, non-intrusive cloud-based solution that provides daily monitoring for web applications, checking for systems and application vulnerabilities, and malware. Indusface WAS with its automated scans & manual pentesting done by certified security experts ensures none of the OWASP Top10, business logic vulnerabilities, and malware go unnoticed. With zero false-positive guarantee and comprehensive reporting with remediation guidance, Indusface web app scanning ensures developers to quickly fix vulnerabilities seamlessly.

Average Rating: 4.6/5.0

Total Reviews: 64

How Do G2 Users Rate Indusface WAS?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Detection Rate: 9.2/10 (Category avg: 9.0/10)
  • Automated Scans: 9.3/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.8/10 (Category avg: 8.5/10)

Who Is the Company Behind Indusface WAS?

  • Seller: Indusface
  • Year Founded: 2012
  • HQ Location: Vadodara
  • Twitter: @Indusface
    3,472 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    172 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 53% Small, 37% Medium

What Do G2 Reviewers Say About Indusface WAS?

AI-generated summary from verified user reviews

Pros
  • Users commend the reliable vulnerability detection of Indusface WAS, ensuring comprehensive scans and quick resolution of issues.
  • Users value the effective vulnerability identification of Indusface WAS, enhancing security with reliable manual and automated scans.
  • Users commend the responsive customer support of Indusface WAS, facilitating quick resolutions and effective communication throughout the process.
  • Users value the scanning efficiency of Indusface WAS, delivering deep insights into vulnerabilities without false positives.
  • Users value the deep-dive security scans of Indusface WAS, enhancing their security accreditation and vulnerability management.
Cons
  • Users feel that the pricing is too high for staging scans and SSL certificates compared to competitors.
  • Users find the interface confusing and suggest improvements for a more intuitive and informative design.
  • Users find the lack of features for staging and development environments limits their testing capabilities before deployment.
  • Users note the limited scope of Indusface WAS regarding staging/development environment scans, impacting functionality and testing.
  • Users find the interface design outdated, expressing a need for a more intuitive and informative experience.

What Are Recent G2 Reviews of Indusface WAS?

What Are G2 Users Discussing About Indusface WAS?

Armor Agent

Armor Agent protects Windows and Linux servers wherever they run, in public cloud, private cloud, or on-premises environments, with a single, lightweight agent that installs with one line of code. The agent combines malware protection, intrusion prevention (IDS/IPS), file integrity monitoring, vulnerability scanning, patch monitoring, and behavioral threat detection into one deployment. Rather than stitching together multiple point tools, Armor Agent consolidates core workload security into a unified agent managed through the Armor platform. Armor Agent is available in two tiers. The Free Tier covers up to 5 endpoints at no cost, with full malware and intrusion defense, vulnerability scanning, patch monitoring, and file integrity monitoring included. The Premium Tier adds security alerts, log search, threat intelligence, threat hunting, dedicated support, and 24×7 SOC monitoring at $99/month per endpoint with no endpoint limit. Both tiers support compliance requirements for HIPAA, PCI DSS, HITRUST, and ISO frameworks. Get started with the Free Tier at https://www.armor.com/free/armor-agent

Average Rating: 4.8/5.0

Total Reviews: 12

How Do G2 Users Rate Armor Agent?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Detection Rate: 9.2/10 (Category avg: 9.0/10)
  • Automated Scans: 9.0/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 10.0/10 (Category avg: 8.5/10)

Who Is the Company Behind Armor Agent?

  • Seller: Armor
  • Year Founded: 2009
  • HQ Location: Plano, Texas
  • Twitter: @Armor
    9,748 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    203 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 83% Small, 17% Medium

What Are Recent G2 Reviews of Armor Agent?

What Are G2 Users Discussing About Armor Agent?

SentinelOne Singularity Cloud Security

Singularity Cloud Security is SentinelOne’s comprehensive, cloud-native application protection platform (CNAPP). It combines the best of agentless insights with AI-powered threat protection, to secure and protect your multi-cloud infrastructure, services, and containers from build time to runtime. SentinelOne’s CNAPP applies an attacker’s mindset to help security practitioners better prioritize their remediation tasks with evidence-backed Verified Exploit Paths™. The efficient and scalable runtime protection, proven over 5 years and trusted by many of the world’s leading cloud enterprises, harnesses local, autonomous AI engines to detect and thwart runtime threats in real-time. CNAPP data and workload telemetry is recorded to SentinelOne’s unified security lake, for easy access and investigation.

Average Rating: 4.9/5.0

Total Reviews: 122

How Do G2 Users Rate SentinelOne Singularity Cloud Security?

  • Has the product been a good partner in doing business?: 9.8/10 (Category avg: 9.2/10)
  • Detection Rate: 9.8/10 (Category avg: 9.0/10)
  • Automated Scans: 9.8/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 9.9/10 (Category avg: 8.5/10)

Who Is the Company Behind SentinelOne Singularity Cloud Security?

  • Seller: SentinelOne
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • Twitter: @SentinelOne
    57,863 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    6,571 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 59% Medium, 30% Large

What Do G2 Reviewers Say About SentinelOne Singularity Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the real-time threat alerts of SentinelOne Singularity Cloud Security, enhancing proactive protection against vulnerabilities.
  • Users appreciate the intuitive and user-friendly interface of SentinelOne Singularity, enhancing security management for everyone.
  • Users value the automated vulnerability detection of PingSafe, enabling proactive security and swift threat identification.
  • Users praise PingSafe for its comprehensive cloud security solutions that enhance threat detection and proactive risk management.
  • Users value the strong visibility and protection offered by SentinelOne Singularity Cloud Security, enhancing their operational efficiency.
Cons
  • Users note the complexity of configuring SentinelOne Singularity Cloud Security, requiring time and experience for effective use.
  • Users find that ineffective alerts require tuning, complicating setup and alignment with organizational workflows.
  • Users find the complex setup of SentinelOne Singularity Cloud Security can be time-consuming and challenging to navigate.
  • Users find the difficult configuration of SentinelOne Singularity Cloud Security can complicate setup and usage experience.
  • Users feel the UI of SentinelOne Singularity is clunky, making the platform harder to navigate and set up.

What Are Recent G2 Reviews of SentinelOne Singularity Cloud Security?

Snyk

Snyk (pronounced sneak) is a developer security platform for securing custom code, open source dependencies, containers, and cloud infrastructure all from a single platform. Snyk’s developer security solutions enable modern applications to be built securely, empowering developers to own and build security for the whole application, from code & open source to containers & cloud infrastructure. Secure while you code in your IDE: find issues quickly using the scanner, fix issues easily with remediation advice, verify the updated code. Integrate your source code repositories to secure applications: integrate a repository to find issues, prioritize with context, fix & merge. Secure your containers as you build, throughout the SDLC: start fixing containers as soon as your write a Dockerfile, continuously monitor container images throughout their lifecycle, and prioritize with context. Secure build and deployment pipelines: Integrate natively with your CI/CD tool, configure your rules, find & fix issues in your application, and monitor your applications. Secure your apps quickly with Snyk’s vulnerability scanning and automated fixes - Try for Free!

Average Rating: 4.5/5.0

Total Reviews: 136

How Do G2 Users Rate Snyk?

  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.2/10)
  • Detection Rate: 8.5/10 (Category avg: 9.0/10)
  • Automated Scans: 9.1/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.3/10 (Category avg: 8.5/10)

Who Is the Company Behind Snyk?

  • Seller: Snyk
  • HQ Location: Boston, Massachusetts
  • Twitter: @snyksec
    21,057 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,764 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 45% Medium, 35% Small

What Do G2 Reviewers Say About Snyk?

AI-generated summary from verified user reviews

Pros
  • Users value Snyk's quick vulnerability detection, significantly improving efficiency in code security and remediation processes.
  • Users appreciate Snyk for its efficient vulnerability identification, significantly aiding in maintaining secure code and streamlining DevOps processes.
  • Users value the easy integration setup of Snyk, enhancing vulnerability detection in their development workflows.
  • Users appreciate the easy setup of Snyk, seamlessly integrating with GitHub for efficient vulnerability management.
  • Users benefit from Snyk's intuitive GUI and customizable features, facilitating effective vulnerability management and developer organization.
Cons
  • Users experience false positives in Snyk, which can hinder efficiency and slow down the scanning process.
  • Users find the poor interface design of Snyk cumbersome, impacting their overall experience with the product.
  • Users note that pricing issues can arise, especially when accessing all features of Snyk, impacting affordability.
  • Users report experiencing false positives and slow scan times, affecting their efficiency and integration within the Snyk product.
  • Users experience false positives and slow scans, complicating overall use and requiring additional tools for code quality.

What Are Recent G2 Reviews of Snyk?

What Are G2 Users Discussing About Snyk?

Pentest-Tools.com

Discover what's possible. Prove what's real. With proprietary tech and key experts in offensive security. Pentest-Tools.com is built for actual security testing, not just detection. We provide the coverage, consolidation, and automation cybersecurity teams need to optimize vulnerability assessment workflows. And we ensure the depth, control, and customization on which professional pentesters count to increase engagement quality and profitability. ✔️ Comprehensive toolkit with real-world coverage ✔️ Validated findings rich with evidence ✔️ Automation options with granular control ✔️ Flexible, high-quality reporting ✔️ Workflow-friendly by design Optimize and scale penetration testing and vulnerability assessment workflows - without sacrificing accuracy, control, or manual testing depth. 🎯 Attack surface mapping and recon 🎯 Comprehensive vulnerability scanning 🎯 Vulnerability exploitation 🎯 Customizable pentest reporting and data exports 🎯 Continuous vulnerability monitoring In our company, we build what we use We launched Pentest-Tools.com in 2017 as a team of professional penetration testers - and we've kept that mindset ever since. Our experts still drive product development today, focusing relentlessly on accuracy, speed, and control. Every new feature, detection, and workflow comes from real-world experience. We constantly improve the product with updated attack techniques, smarter automation, and validation that reflects how malicious hackers actually operate - so your team can deliver security work that's faster, more visible, and built on proof.

Average Rating: 4.8/5.0

Total Reviews: 108

How Do G2 Users Rate Pentest-Tools.com?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Detection Rate: 8.5/10 (Category avg: 9.0/10)
  • Automated Scans: 9.2/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 7.6/10 (Category avg: 8.5/10)

Who Is the Company Behind Pentest-Tools.com?

  • Seller: Pentest-Tools.com
  • Year Founded: 2017
  • HQ Location: Sectorul 1, Bucharest
  • Twitter: @pentesttoolscom
    4,062 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    67 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 66% Small, 19% Medium

What Do G2 Reviewers Say About Pentest-Tools.com?

AI-generated summary from verified user reviews

Pros
  • Users commend the ease of use of Pentest-Tools.com, enabling seamless integration for all skill levels in cybersecurity.
  • Users value the pentesting efficiency of Pentest-Tools.com, appreciating its comprehensive and easy-to-use features for vulnerability testing.
  • Users appreciate the automation features of Pentest-Tools.com, streamlining scans and reporting for enhanced security management.
  • Users commend the responsive customer support at Pentest-Tools.com, highlighting their patience and helpfulness.
  • Users appreciate the ease of scheduling scans with Pentest-Tools.com, significantly saving time on vulnerability management.
Cons
  • Users find difficult customization options in Pentest-Tools.com, hindering their ability to tailor reports effectively.
  • Users are frustrated by the limited features, such as lack of report customization and unexpected asset limitations.
  • Users find the slow scanning process frustrating, impacting efficiency and report customization options significantly limit flexibility.
  • Users find the buggy findings require extra manual work, which can be frustrating despite not being critical.
  • Users find the confusing interface hinders navigation, impacting the efficient use of Pentest-Tools.com.

What Are Recent G2 Reviews of Pentest-Tools.com?

What Are G2 Users Discussing About Pentest-Tools.com?

BugDazz API Scanner

BugDazz API Security Scanner by SecureLayer7 is a comprehensive tool designed to automatically detect vulnerabilities, misconfigurations, and security gaps in API endpoints, aiding security teams in protecting digital assets against increasing API-related threats and potential exploits. It offers real-time scanning capabilities, enabling the automatic detection of vulnerabilities as they arise. It supports authentication and access control management, allowing for the management of API controls within a single platform. BugDazz assists in achieving compliance by accelerating the generation of reports for standards such as PCI DSS and HIPAA. It integrates seamlessly with existing CI/CD pipelines, facilitating the acceleration of product rollouts. The scanner goes beyond standard OWASP Top 10 vulnerabilities, providing comprehensive protection against critical API security risks.

Average Rating: 4.9/5.0

Total Reviews: 11

How Do G2 Users Rate BugDazz API Scanner?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)
  • Detection Rate: 9.8/10 (Category avg: 9.0/10)
  • Automated Scans: 9.5/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 9.3/10 (Category avg: 8.5/10)

Who Is the Company Behind BugDazz API Scanner?

  • Seller: SecureLayer7
  • Year Founded: 2012
  • HQ Location: Pune, Maharshtra
  • Twitter: @SecureLayer7
    2,522 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    122 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 91% Small, 9% Medium

What Do G2 Reviewers Say About BugDazz API Scanner?

AI-generated summary from verified user reviews

Pros
  • Users value the accuracy of results from BugDazz API Scanner, enhancing collaboration and efficiency in workflow processes.
  • Users love the smooth integration with CI/CD pipelines, enabling efficient and timely security scans without delays.
  • Users value the seamless CI/CD integration of BugDazz API Scanner, enhancing efficiency without slowing down builds.
  • Users appreciate the ease of use of BugDazz API Scanner, facilitating quick integration and reliable results.
  • Users value the fast and accurate scans of BugDazz, seamlessly integrating into CI/CD workflows with minimal friction.
Cons
  • Users find documentation lacking, particularly in infrastructure guidance and clarity for Jerkins integration.
  • Users acknowledge a difficult learning curve with BugDazz API Scanner, requiring time to optimize scan configurations effectively.
  • Users suggest that the lack of guidance in documentation hinders effective usage of BugDazz API Scanner.
  • Users find the lack of detailed information in BugDazz API Scanner's documentation limiting for infrastructure-specific guidance.
  • Users note a learning curve in optimizing scans for various scenarios, but find it manageable overall.

What Are Recent G2 Reviews of BugDazz API Scanner?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated