Best Vulnerability Assessment Services Providers - Page 8

Last updated: October 12, 2026

How Many Vulnerability Assessment Services Providers Products Does G2 Track?

Total Products under this Category: 182

Category Stats (Nov 2026)

  • Average Rating: 4.56/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Packetlabs (+0.06%) - Among all products in this category, Packetlabs recorded the largest rating increase compared to last month

Last updated: November 21, 2026

How Does G2 Rank Vulnerability Assessment Services Providers Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,100+ Authentic Reviews
  • 182+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

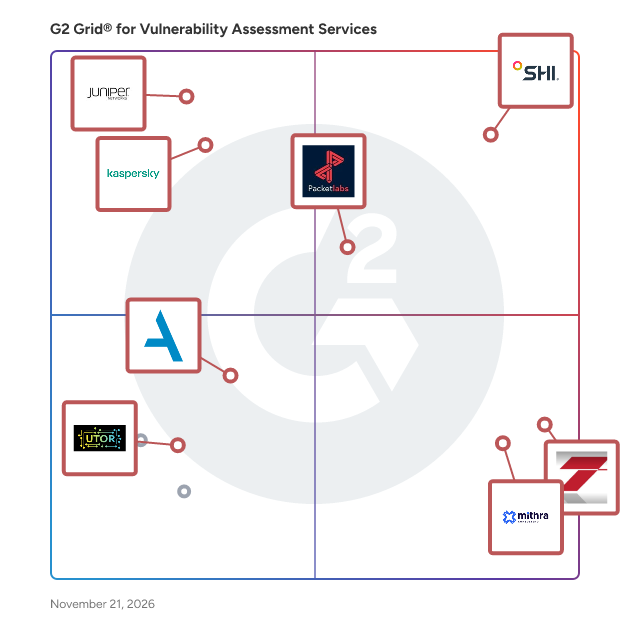
G2 Grid® for Vulnerability Assessment Services Providers

G2 Grid® for Vulnerability Assessment Services Providers plotting products by satisfaction and market presence

Highlighted products: SHI, 7 Layer Solutions, Juniper Services, Packetlabs, Kaspersky Cybersecurity Services, Mithra Consulting, Appsecco, and Security testing.

Underlying data: [Grid® JSON](https://www.g2.com/categories/vulnerability-assessment-services/grids.json?focus%5B%5D=shi&focus%5B%5D=7-layer-solutions-inc-7-layer-solutions&focus%5B%5D=juniper-services&focus%5B%5D=packetlabs-ltd-packetlabs&focus%5B%5D=kaspersky-cybersecurity-services&focus%5B%5D=mithra-consulting&focus%5B%5D=appsecco&focus%5B%5D=utor-security-testing)

KEYW

KeyW is passionate about securing our nation and its allies. Our advanced engineering and technology solutions support the collection, processing, analysis and dissemination of information across the full spectrum of the Intelligence, Cyber and Counterterrorism communities missions.

Who Is the Company Behind KEYW?

  • Seller: KeyW
  • Year Founded: 2008
  • HQ Location: Hanover, US
  • LinkedIn® Page: www.linkedin.com
    299 employees on LinkedIn®

Kratikal

Kratikal, being a CERT-In empanelled business, brings a level of credibility and expertise that makes our Penetration Testing and Compliance Services stand out as a pillar in securing your IT infrastructure. Our diverse range VAPT services include: Application Testing: Web and Mobile Network Penetration Testing Cloud Penetration Testing Internet of Things (IoT) Testing Thick Client Threat Modeling Red Teaming Secure Code Review Medical Device Testing Our compliance services span across: Regulatory Compliance: Customized services for SEBI, SAR, IRDAI, IS AUDIT(RBI), and CERT-In requirements, focusing on integrating a security and compliance culture at the core of your organization. Standard Compliance: Assistance in achieving and maintaining standards such as PCI DSS, GDPR, HIPAA, ISO 27001, and SOC 2, ensuring your business remains at the forefront of compliance management. Our integrated VAPT and Compliance services ensure that your organization not only meets today's security standards but is also prepared for tomorrow's challenges.

Average Rating: 4.0/5.0

Total Reviews: 2

Who Is the Company Behind Kratikal?

Who Uses This Product?

  • Company Size: 67% Small, 33% Medium

What Are Recent G2 Reviews of Kratikal?

Kroll

Kroll experts provide rapid response to more than 3,000 cyber incidents of all types annually. We help countless more clients with litigation support (including expert witness services); managed detection and response services for both active threats and as an integral part of network security; notification solutions, including multilingual call center support; and proactive services, including general and threat-focused risk assessments, response planning, tabletop exercises and more. With years of public and private sector experience and law enforcement service, our cyber security experts can provide invaluable leadership at any point in the cyber risk continuum. Our experts are able to deliver best-in-class network, endpoint and cloud security through our managed detection and response solution, Kroll Responder. Responder handles every step, with 24x7 managed detection and response services fueled by threat hunting and superior incident response. Our collaborative team culture ensures you always benefit from the latest threat intelligence, best practices and technological advancements for every challenge, start to finish. Kroll is also a preferred/approved cyber security vendor for more than 50 cyber insurance carriers, including some of the largest underwriters in the world, and offers client-friendly retainers that cover both incident response and proactive services.

Average Rating: 3.8/5.0

Total Reviews: 3

Who Is the Company Behind Kroll?

  • Seller: Kroll
  • Year Founded: 1932
  • HQ Location: New York, US
  • LinkedIn® Page: www.linkedin.com
    7,233 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 67% Small, 33% Medium

What Are Recent G2 Reviews of Kroll?

What Are G2 Users Discussing About Kroll?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Kudelski Security

Kudelski Security is a premier cybersecurity solutions provider, working with the most security-conscious organizations in Europe and across the United States.

Who Is the Company Behind Kudelski Security?

Leviathan Security Group

Founded in 2006, Leviathan has focused on the world's most challenging cybersecurity problems. We are looked to by industry leaders for our unique perspective on how to solve these challenges. Our professional services experts perform security assessments on the world's most critical infrastructure and provide guidance on governance, risk and compliance services for highly regulated environments.

Who Is the Company Behind Leviathan Security Group?

Lighthouse Security

Lighthouse Security's Business Continuity and Incident Management services provide a comprehensive framework designed to ensure organizational resilience in the face of unforeseen events. By maintaining critical services and safeguarding brand reputation, these services help businesses navigate disruptions such as accidents, criminal activities, or natural disasters, thereby ensuring long-term survivability. Key Features and Functionality: - Business Continuity: - Risk Assessments - Business Impact Analysis - Risk Management - Business Continuity Planning - Incident Management: - Emergency Response - Disaster Recovery - Incident Management Public Relations - Planning, Training, and Testing Exercises The primary value of these services lies in their ability to equip organizations with the necessary tools and strategies to effectively manage and recover from disruptions. By proactively identifying risks and implementing tailored continuity plans, Lighthouse Security ensures that businesses can maintain operations, protect their reputation, and minimize the impact of unexpected events.

Who Is the Company Behind Lighthouse Security?

Loginsoft

Loginsoft is a Cybersecurity services company providing comprehensive cybersecurity solutions tailored to meet the unique needs of organizations. Loginsoft is trusted by several leading security product and Enterprise companies as their best kept secret Technology partner. For over 20 years, leading companies in Telecom, Cybersecurity, Healthcare, Banking, New Media, and more have come to rely on Loginsoft as a trusted resource for technology talent. Loginsoft offers a comprehensive range of Cybersecurity solutions including, but not limited to: 𝟭) 𝗦𝗼𝗳𝘁𝘄𝗮𝗿𝗲 𝗖𝗼𝗺𝗽𝗼𝘀𝗶𝘁𝗶𝗼𝗻 𝗔𝗻𝗮𝗹𝘆𝘀𝗶𝘀 (𝗦𝗖𝗔): Loginsoft has researched over 30,000+ CVEs across several open-source packages, helping Application Security teams to prioritize the vulnerabilities. - Security Advisory Research and Generating Metadata for Vulnerabilities in Open-Source Components/Software for OWASP Top 10. - Discovering Zero-Day Vulnerabilities in Open-Source Components. - SAST & DAST Analysis. 𝟮) 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 & 𝗧𝗵𝗿𝗲𝗮𝘁 𝗜𝗻𝘁𝗲𝗹𝗹𝗶𝗴𝗲𝗻𝗰𝗲 𝗜𝗻𝘁𝗲𝗴𝗿𝗮𝘁𝗶𝗼𝗻𝘀: - Threat Intelligence Integrations and Connector Development with TIP, SOAR, SIEM, Ticketing Platforms. - Implementation of Security Products and support. - Security Integrations for Cloud SIEM. - Integrations Maintenance and Support. 𝟯) 𝗩𝘂𝗹𝗻𝗲𝗿𝗮𝗯𝗶𝗹𝗶𝘁𝘆 & 𝗖𝗼𝗻𝗳𝗶𝗴𝘂𝗿𝗮𝘁𝗶𝗼𝗻 𝗠𝗮𝗻𝗮𝗴𝗲𝗺𝗲𝗻𝘁 𝗶𝗻 𝗢𝗩𝗔𝗟, 𝗦𝗖𝗔𝗣: - Generate Security Content to support Vulnerability Management, Patch Management and Compliance Management in SCAP supported formats like Open Vulnerability and Assessment Language (OVAL) Extensible Configuration Checklist Description Format (XCCDF). 𝟰) 𝗖𝗩𝗘 𝗩𝘂𝗹𝗻𝗲𝗿𝗮𝗯𝗶𝗹𝗶𝘁𝘆 𝗜𝗻𝘁𝗲𝗹𝗹𝗶𝗴𝗲𝗻𝗰𝗲: - Vulnerability intelligence on emerging CVEs on watch, Pre-NVD insights & trending OSS CVEs. 𝟱) 𝗥𝗲𝘀𝗲𝗮𝗿𝗰𝗵 𝗮𝘀 𝗮 𝗦𝗲𝗿𝘃𝗶𝗰𝗲: - Developing rules for Threat Detection supporting formats in Sigma, OSquery, Splunk which could complement Incident Response Activities & Ransomware Protection Solutions. - Developing fingerprints to track the threat actor infrastructure such as Malware C2 Panels, Phishing Kits etc. to complement Threat Intelligence & Botnet Protection Solutions. - Developing Human-Readable fingerprints to detect wide-varieties of Software/Hardware products to complement External+Internal Attack Surface Management Solutions. Loginsoft is a partner with industry leading technology vendors such as Palo Alto, Splunk, Elastic, IBM Security, ThreatConnect, and so on.

Who Is the Company Behind Loginsoft?

Lyon Tech

Lyon is a specialist IT and technology services provider for London's creative industry. With years of experience, we tackle complex security and technology challenges swiftly and efficiently. Our comprehensive services include IT support, disaster recovery, business continuity, IT governance, cloud services, and advanced cybersecurity. Our team of certified engineers is equipped to handle a wide range of IT needs, from office-to-home working transitions to data security concerns and everyday technical issues. We transform your IT experience, ensuring seamless infrastructure at every level. By partnering with Lyon, you'll enhance your efficiency, security, and ultimately, your creative potential.

Who Is the Company Behind Lyon Tech?

Managed Services

IT Outlet’s Managed Services program works as an extension of your business. Entirely offloading your IT needs to our team, ensuring that your business is running the way you want, all the time. IT Outlet offers hassle-free services that pride themselves on creating authentic relationships everyday. With 24/7 support, quick response times and staff members that want to see your business succeed, we are here to support you and your IT needs.

Who Is the Company Behind Managed Services?

ManageX

ManageX was born out of the need to simplify the process of onboarding engineering resources for organizational needs. With countless hours of development going into designing a swift user journey, ManageX allows our customers to quickly get access to the best IT resources in the region at the click of a button.

Who Is the Company Behind ManageX?

  • Seller: VaporVM
  • Year Founded: 2011
  • HQ Location: Dubai, United Arab Emirates
  • LinkedIn® Page: www.linkedin.com
    183 employees on LinkedIn®

Microland Services

Delivering technology services to global clients, enables businesses to strategize, build and integrate powerful new technologies with existing services, infrastructure and processes.

Who Is the Company Behind Microland Services?

Mirox

Mirox Cyber Security & Technology Pvt Ltd is a provider of comprehensive security audit and penetration testing services, dedicated to safeguarding organizations' critical data and systems. As a CERT-In empanelled cyber security auditor, Mirox offers real-world security assessments across various industries, ensuring compliance with established standards and regulations. Key Features and Functionality: - Vulnerability Assessment and Penetration Testing : Conducts thorough evaluations of applications, networks, and mobile platforms to identify and mitigate vulnerabilities. - Specialized Security Testing: Offers assessments for IoT devices, automotive systems, SCADA environments, and cloud applications to address unique security challenges. - Compliance Audits: Ensures adherence to industry standards such as PCI DSS, ISO 27001, and SOC 2 through detailed audits and assessments. - Risk Assessments and Mitigation Strategies: Provides accurate risk profiling and develops strategies to support organizational objectives. - Security Architecture Review: Evaluates and enhances the security framework of organizations to strengthen overall defense mechanisms. Primary Value and Solutions Provided: Mirox addresses the critical need for robust cyber security by offering tailored solutions that protect organizations from evolving threats. By identifying vulnerabilities and ensuring compliance with industry standards, Mirox helps reduce liability, streamline business processes, and enhance overall security posture. Their cost-effective services, delivered by experienced professionals, provide organizations with the confidence that their critical data and systems are well-protected.

Who Is the Company Behind Mirox?

Modus Create

Modus Create is a digital product engineering partner for forward-thinking businesses. Our global teams work side-by-side with clients to design, build, and scale custom solutions that achieve real results and lasting change.

Who Is the Company Behind Modus Create?

Money Back Ltd.

Payback’s cybersecurity services help businesses and individuals identify security weaknesses and vulnerabilities in their digital systems through simulated cyberattacks and penetration testing. They provide users with reports and detailed insights to understand security flaws and prioritize necessary fixes. The services are designed for organizations of all sizes and individuals who want to enhance their security posture by proactively discovering and addressing potential threats before malicious actors can exploit them. Furthermore, Payback offers Cyber Investigation services for companies and individuals. Key Services and Benefits: Comprehensive Vulnerability Scanning: Scanning web applications, networks, and systems for common vulnerabilities, misconfigurations, and exploitable weaknesses. Realistic Penetration Testing: Simulating real-world hacking techniques to assess the security resilience of your systems, providing actionable recommendations for mitigation. Continuous Monitoring: Providing ongoing security assessments and updates, ensuring the systems are constantly monitored and up-to-date with the latest threat intelligence. Detailed Reporting and Analytics: Users receive in-depth reports with clear explanations, risk assessments, and remediation steps to improve security. Online Fraud Investigation: Providing in-depth Investigation Reports to companies or individuals on the perpetrators of various online frauds and scams. Target Audience: Small to Medium Enterprises (SMEs): Organizations looking to secure their systems without the resources for in-house security teams. Large Enterprises: Businesses with complex infrastructures that require continuous vulnerability scanning and penetration testing. Security Professionals: Penetration testers, security consultants, and IT teams seeking a tool to streamline security assessments and vulnerability management. Individuals: People who seek to improve their online security effectiveness or the investigation of wrongdoers who scammed them online. Use Cases: Penetration Testing: Simulate attacks on networks and applications to identify vulnerabilities before they can be exploited. Security Audits: Conduct regular audits to ensure compliance with security standards and best practices. Vulnerability Management: Discover vulnerabilities and manage remediation efforts to reduce overall risk exposure. Fraud Investigation: Complie a collection of evidence and other crucial information on companies or persons who took funds from our clients in a fraudulent manner.

Who Is the Company Behind Money Back Ltd.?

Musubu

Musubu provides IP cyber threat intelligence APIs, the MusubuApp IP & Network Threat Intelligence Web Portal, and various integrations with platforms such as SIEM, SOAR, TIP, website (Wordpress) and more. Musubu APIs: Allows organizations to have easy access to detailed network information from their own endpoints efficiently and in bulk using simple queries to the Musubu API. With the latest version of the service, customers can easily assess the security risk posed by their publicly exposed networks, as well as survey their network environments to identify both potential threats and misleading false positive results. This allows customers to quickly filter out non-actionable [false positive] data and focus on the true threats to their organization. These are measured in the API results via: threat_potential_score_pct – Numeric threat score between 0-100. The Score is calculated using “blacklist class”, “blacklist neighbors”, number of recent observations and country of origin. threat_classification – Classification derived from “threat potential score pct” High – Threat score >70 Medium – Threat score from >40 but<70 Low – Any IP unlisted with a threat score <20 Nuisance – Threat score<40 blacklist_class – Field classifying the specific threat vector that has been identified. Contains one of the following values: apache, blacklisted, botnet, botnetcnc, brute force, compromised, ftp, http, imap, mail, malware, phishing, ransomware, shunned, sips, ssh, TOR, worm, zeus blacklist_class_cnt – Field providing the number of sources which have identified the address as malicious. blacklist_network_neighbors – Field providing the number of addresses present on the same subnet which have been identified as malicious. blacklist_observations – Field providing the number of observations (of this IP) in the last 90 days. As well, Musubu's KnownNetworks® data sets also show you the following for any IP address: - Network Name - Network Type - Network Group MusubuApp IP & Network Intelligence Web Portal: MusubuApp is a simple, highly-affordable web application that delivers practical, immediately usable threat intelligence around IP-driven cyber threats – the number one vector of cybercrime for businesses large and small. MusubuApp allows security and information technology (IT) professionals to quickly research, identify malicious servers and clients making connections with their websites, apps, mail servers, cloud servers, and other networked assets. MusubuApp allows users to search in bulk for suspicious IP addresses (IPs) and instantly see a detailed set of data about the IPs such as: The level and severity of cyber threat per IP The types of threats associated with each IP The total volume of cyber threats per IP Other risky IPs in the same subnet The network IPs belong to and what type of network As well, MusubuApp provides key usability features to help operators be more efficient when hunting threats: Bulk IP Search – Users can import up to 500 IPs via JSON or CSV for immediate search and monitoring. Users can also export any results to CSV or JSON for integration elsewhere. Watchlists – Users can create lists of IPs, name and describe them for alerting as well as subject them to advanced data analytics and intelligence modules. Geolocation – Users can see IP addresses and their threat profiles on Google Maps embedded in the application and click to street addresses for individual IPs. They can also search IPs straight onto the map. Tags – Users can tag IPs with useful labels and share them across the user community. Users can also map entire tag sets instantly. Trends & Analytics – Users can instantly gain intelligence from their Watchlists via modules that show things like new threats, rising threat ratings, time-series threat analytics, and much more. 3rd Party Integrations – MusubuApp accommodates things like “click-to-query” for sending entire Watchlist lists into other complementary cyber tools and platforms. As a result of its powerful, but simple features and low cost, MusubuApp is a natural complement to more expensive, enterprise tools such as Security Information and Event Management (SIEM), Threat Intelligence Platforms (TIP), Security Orchestration, Automation and Response (SOAR), and Incident Response (IR). Musubu IP Threat Data for Splunk: "NOTE: Request Free 7-Day Trial API Key via support@musubu.io" Use Musubu’s unique IP & Network cyber threat scoring and profiling API right in your Splunk instance to determine the following for each IP: - Cyber Threat Score: A 0-100 rating of how much of a cyber threat the IP may be based on the output of our analytics and algorithms. - Cyber Threat Classification: High-Medium-Nuisance-Low rating of an IPs cyber threat potential for quick identification. - Blacklist Class: The predominant cyber threat vector seen as associated with the IP address (e.g. Phishing, Ransomware, TOR, etc.). - Blacklist Count: The number of major IP blacklisting services that have blacklisted the IP address. - Blacklist Neighbors: The number of other IP addresses in the same subnet that have been blacklisted. - Blacklist Count: The number of times in the last 90 days the IP address has been blacklisted. Simply add one or more data sources to the Musubu Add-on and then you will be able to mouse over each IP address to see our threat profiling data. Use it to perform faster threat detection, threat identification, response, and mitigation. Leverage the “showipthreatdata” custom command within the add-on to make direct calls to the Musubu API from the Splunk search view. See example below - Musubu results for the specified IP are returned in a Tableview.

Who Is the Company Behind Musubu?
Lauren Worth
LW
Researched and written by Lauren Worth