Best Threat Intelligence Software - Page 5

How Many Threat Intelligence Software Products Does G2 Track?

Total Products under this Category: 222

Category Stats (Sep 2026)

  • Average Rating: 4.59/5 (↑0.01 vs Aug 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Darktrace / EMAIL (+1.92%) - Among all products in this category, Darktrace / EMAIL recorded the largest rating increase compared to last month

Last updated: September 29, 2026

How Does G2 Rank Threat Intelligence Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,700+ Authentic Reviews
  • 222+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

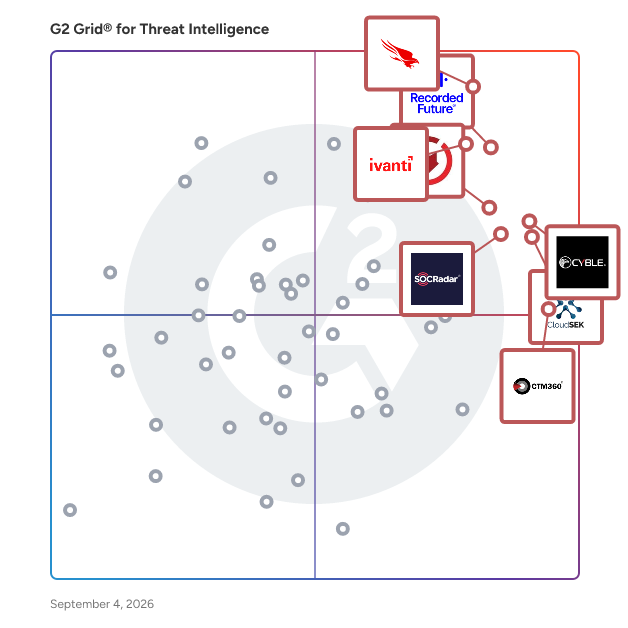
G2 Grid® for Threat Intelligence Software

G2 Grid® for Threat Intelligence Software plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Recorded Future, Ivanti Autonomous Endpoint Management, Cyble, CloudSEK, ZeroFox, SOCRadar Extended Threat Intelligence, and CTM360.

Underlying data: [Grid® JSON](https://www.g2.com/categories/threat-intelligence/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=recorded-future&focus%5B%5D=ivanti-autonomous-endpoint-management&focus%5B%5D=cyble&focus%5B%5D=cloudsek&focus%5B%5D=zerofox&focus%5B%5D=socradar-extended-threat-intelligence&focus%5B%5D=ctm360-ctm360)

Hunto AI

Hunto AI is an agentic, 100% autonomous platform purpose-built for monitoring and quantifying your external threats. We proactively monitor external assets, detect real-world brand impersonation and fraud infrastructure, and execute rapid takedowns, while mapping every finding to audit-ready proof. - CTOs get measurable breach-probability reduction and time-to-mitigation SLAs. - CEOs/CMOs get brand-abuse suppression and revenue protection. - Compliance gets reports your auditors actually accept. Hunto AI offers a live, quantified view of exposure, external risk, and the fastest path to fix.

Average Rating: 4.8/5.0

Total Reviews: 16

How Do G2 Users Rate Hunto AI?

  • Security Validation: 7.5/10 (Category avg: 9.1/10)
  • Intelligence Reports: 8.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.2/10 (Category avg: 8.7/10)
  • Ease of Use: 9.1/10 (Category avg: 9.1/10)

Who Is the Company Behind Hunto AI?

  • Seller: Hunto AI
  • Year Founded: 2023
  • HQ Location: Melbourne, AU
  • LinkedIn® Page: www.linkedin.com
    11 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 50% Medium, 44% Small

What Do G2 Reviewers Say About Hunto AI?

AI-generated summary from verified user reviews

Pros
  • Users value the continuous monitoring by Hunto AI, appreciating its seamless integration for robust threat management.
  • Users value the seamless automation in Hunto AI, effectively enhancing threat detection and incident response efficiency.
  • Users value the proactive risk identification and automation features of Hunto AI, enhancing security management efficiency.
  • Users value the comprehensive integration of security features in Hunto AI, enhancing overall cyber resilience and efficiency.
  • Users commend Hunto AI for its quick threat detection, enhancing security and reducing human cyber risk effectively.
Cons
  • Users desire greater automation capabilities in Hunto AI to enhance efficiency and simplify their workflow.
  • Users desire more automation in Hunto AI to enhance efficiency and streamline their tasks.
  • Users believe that the few modules of Hunto AI could significantly improve with added risk scoring features.

What Are Recent G2 Reviews of Hunto AI?

IDARK360

IDARK360 is an advanced platform offering 360-degree protection against modern cyber risks, focusing on four key areas: Dark Web Discovery and Monitoring: Accurate identification of your stolen data trading (credentials, IP, customer data) for early threat neutralization. Brand Identity Protection: Immediate monitoring for impersonation and phishing, with rapid removal of fraudulent content to safeguard your reputation. Security Controls Governance: Continuous and precise assessment of compliance with global controls (NIST, NCA) and gap management via a unified dashboard. Cyber Awareness and Culture Building: Employee Training: Providing simulated and realistic training programs to enhance employee vigilance. Phishing Simulation: Periodically testing the effectiveness of the human defence layer and identifying individual and collective weaknesses. Transforming Employees into a Defence Line: Reducing human errors that cause a significant percentage of breaches.

Average Rating: 5.0/5.0

Total Reviews: 9

How Do G2 Users Rate IDARK360?

  • Intelligence Reports: 10.0/10 (Category avg: 9.1/10)
  • Ease of Use: 9.6/10 (Category avg: 9.1/10)

Who Is the Company Behind IDARK360?

  • Seller: IDARK360
  • Year Founded: 2025
  • HQ Location: Riyadh , SA
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of IDARK360?

Palo Alto Networks Cortex XSOAR

Palo Alto Networks' Cortex XSOAR is a comprehensive Security Orchestration, Automation, and Response (SOAR) platform designed to streamline and enhance security operations. By integrating automation, case management, real-time collaboration, and threat intelligence management, Cortex XSOAR empowers security teams to respond to incidents more efficiently and effectively. Key Features and Functionality: - Process Standardization and Automation: Cortex XSOAR offers over 270 out-of-the-box playbooks, enabling the automation of numerous security use cases. These playbooks orchestrate response actions across more than 350 third-party products, facilitating seamless integration and operational consistency. - Security-Focused Case Management: The platform unifies alerts, incidents, and indicators from various sources into a single case management framework. This consolidation accelerates incident response by providing a comprehensive view of security events. - Real-Time Collaboration: Cortex XSOAR includes a Virtual War Room equipped with built-in ChatOps and a command-line interface. This feature allows security teams to collaborate in real time, execute commands across the entire product stack, and manage incidents more effectively. - Threat Intelligence Management: The platform aggregates disparate threat intelligence sources, customizes and scores feeds, and matches indicators against the organization's specific environment. This capability enables security teams to take informed actions swiftly. Primary Value and Problem Solving: Cortex XSOAR addresses the challenges faced by security teams, such as the overwhelming volume of alerts and the need for rapid incident response. By automating repetitive tasks and standardizing processes, the platform reduces the time spent on incidents by up to 90%, allowing analysts to focus on critical threats. The integration of threat intelligence management with SOAR capabilities ensures that organizations can operationalize threat feeds effectively, enhancing their overall security posture. Additionally, the platform's extensive integration ecosystem, with over 360 third-party integrations, enables organizations to orchestrate complex workflows across their existing security infrastructure without extensive custom development.

Average Rating: 4.6/5.0

Total Reviews: 28

How Do G2 Users Rate Palo Alto Networks Cortex XSOAR?

  • Security Validation: 9.2/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.2/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.3/10 (Category avg: 8.7/10)
  • Ease of Use: 8.7/10 (Category avg: 9.1/10)

Who Is the Company Behind Palo Alto Networks Cortex XSOAR?

  • Seller: Palo Alto Networks
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 50% Large, 32% Medium

What Do G2 Reviewers Say About Palo Alto Networks Cortex XSOAR?

AI-generated summary from verified user reviews

Pros
  • Users value the powerful automation capabilities of Cortex XSOAR for enhancing incident response and threat detection.
  • Users appreciate the great UI of Palo Alto Networks Cortex XSOAR, enhancing data clarity and integration efficiency.
  • Users appreciate the clean and accurate data provided by Palo Alto Networks Cortex XSOAR, enhancing efficiency and safety.
  • Users value the powerful automation capabilities for incident response in Palo Alto Networks Cortex XSOAR.
  • Users appreciate the direct customer support from Palo Alto Networks Cortex XSOAR, enhancing their incident response experience.
Cons
  • Users find the learning curve steep, requiring significant time to become proficient with Cortex XSOAR.
  • Users desire more customization options for reporting, indicating limitations in the current capabilities of Cortex XSOAR.
  • Users find the logging issues in Cortex XSOAR frustrating, as readability is hindered by window size constraints.
  • Users find log management issues frustrating as data logs are hard to read quickly without opening new tabs.
  • Users feel that the reporting features lack customization, leading to a need for improvement in functionality.

What Are Recent G2 Reviews of Palo Alto Networks Cortex XSOAR?

What Are G2 Users Discussing About Palo Alto Networks Cortex XSOAR?

ReversingLabs

ReversingLabs is the trusted name in file and software security. We provide the modern cybersecurity platform to verify and deliver safe binaries. Trusted by the Fortune 500 and leading cybersecurity vendors, RL Spectra Core powers the software supply chain and file security insights, tracking over 422 billion searchable files with the ability to deconstruct full software binaries in seconds to minutes. Only ReversingLabs provides that final exam to determine whether a single file or full software binary presents a risk to your organization and your customers.

Average Rating: 4.7/5.0

Total Reviews: 10

How Do G2 Users Rate ReversingLabs?

  • Security Validation: 9.2/10 (Category avg: 9.1/10)
  • Intelligence Reports: 8.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.3/10 (Category avg: 8.7/10)
  • Ease of Use: 9.3/10 (Category avg: 9.1/10)

Who Is the Company Behind ReversingLabs?

  • Seller: ReversingLabs
  • Year Founded: 2009
  • HQ Location: Cambridge, US
  • Twitter: @ReversingLabs
    7,022 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    321 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 80% Small, 10% Medium

What Do G2 Reviewers Say About ReversingLabs?

AI-generated summary from verified user reviews

Pros
  • Users commend the accuracy of information offered by ReversingLabs, utilizing an extensive repository of files for effective risk management.
  • Users commend the excellent customer support from ReversingLabs, enhancing their onboarding and overall experience effectively.
  • Users commend the efficient onboarding process of ReversingLabs, facilitating a seamless and effective transition to their services.
  • Users appreciate the effective prioritization of risk management with ReversingLabs, enhancing their security processes significantly.
  • Users commend the high reliability of ReversingLabs, citing exceptional support and a vast repository of files.
Cons
  • Users find the endpoints for checking usage confusing, which complicates their overall experience with the product.
  • Users find the confusing interface for usage endpoints makes it difficult to navigate the product effectively.
  • Users find the navigation issues related to usage endpoints somewhat confusing, impacting their overall experience.
  • Users feel the UI could be nicer, yet it doesn't hinder the overall functionality of ReversingLabs.

What Are Recent G2 Reviews of ReversingLabs?

ThreatWorx

ThreatWorx is a next-gen proactive cybersecurity platform that protects servers, cloud, containers and source code from malware and vulnerabilities without scanner appliances or bulky agents. ThreatWorx serves multiple use cases including threat intelligence, DevSecOps, cloud security, vulnerability management and third party risk assessment.

Average Rating: 4.7/5.0

Total Reviews: 9

How Do G2 Users Rate ThreatWorx?

  • Security Validation: 8.9/10 (Category avg: 9.1/10)
  • Intelligence Reports: 8.9/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.2/10 (Category avg: 8.7/10)
  • Ease of Use: 9.2/10 (Category avg: 9.1/10)

Who Is the Company Behind ThreatWorx?

  • Seller: Threatwatch
  • Year Founded: 2016
  • HQ Location: LOS GATOS, US
  • Twitter: @threatwatch
    100 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    5 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 40% Medium, 40% Small

What Are Recent G2 Reviews of ThreatWorx?

What Are G2 Users Discussing About ThreatWorx?

CybelAngel

CybelAngel protects its customers with External Attack Surface Management (EASM) solutions that are powered by the most comprehensive external asset discovery and threat detection technologies available. Built upon close to a decade of machine learning, our advanced platform scans the entirety of the internet every 24 hours to uncover unknown assets and shadow IT, cloud services, connected devices, fraudulent domains and exposed credentials — the sources attackers use to access confidential data, launch phishing campaigns or initiate destructive ransomware attacks. CybelAngel's combination of machine learning and expert human analysis provides deep visibility into the most critical threats, long before they’re exploited.

Average Rating: 4.6/5.0

Total Reviews: 7

How Do G2 Users Rate CybelAngel?

  • Intelligence Reports: 10.0/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.3/10 (Category avg: 8.7/10)
  • Ease of Use: 9.0/10 (Category avg: 9.1/10)

Who Is the Company Behind CybelAngel?

  • Seller: CybelAngel
  • Year Founded: 2013
  • HQ Location: Clichy, FR
  • Twitter: @CybelAngel
    3,408 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    154 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 86% Large, 14% Medium

What Are Recent G2 Reviews of CybelAngel?

MetaDefender

MetaDefender Platform is an advanced threat prevention solution that lets organizations embed multi-layer file security into existing applications and security architectures, especially to protect common attack vectors like malicious file uploads, untrusted file transfers, and file-based supply chain risk. It’s designed for environments that need stronger protection against highly evasive malware, zero-day attacks, and APTs, including IT and OT/critical infrastructure use cases. MetaDefender easily integrates into your existing IT solutions and can be deployed on-premises (including air-gapped), in cloud/IaaS, or as SaaS. We offer flexible implementation options for ICAP enabled devices, containerized applications, AWS, Azure, NAS/Storage workflows and Rest API. Overview: Multi-engine malware scanning: Quickly scan files with 30+ antivirus engines and detect over 99% of known malware. Deep CDR (Content Disarm & Reconstruction): Recursively sanitize and rebuild 200+ file types to neutralize embedded threats while maintaining file usability, with extensive reconstruction and file conversion options. Proactive DLP: Remove, redact, or watermark sensitive data in files before content enters or leaves the organization; also supports AI-powered document classification. File-based Vulnerability Assessment: Identify vulnerabilities in installers, binaries, and applications before they are installed/executed and reduce exposure to known software flaws. Threat intelligence-driven detection: Identify malicious domains and IPs embedded in documents and support near real-time blocking using curated threat intelligence. Adaptive threat analysis (sandboxing): Detonate and analyze suspicious files in a controlled environment and improve zero-day detection. SBOM & software supply chain visibility: Generate SBOMs and identify vulnerabilities in source code and containers. Reputation Engine: Use file hash reputation (known good/known bad/unknown) and advanced analysis to remediate false positives faster. Visibility, reporting, and policy control: Gain operational visibility, use automated reports for remediation, and configure workflow/analysis rules based on user, business priority, file source, and file type. Free Training - OPSWAT Academy: https://www.opswat.com/academy

Average Rating: 4.3/5.0

Total Reviews: 15

How Do G2 Users Rate MetaDefender?

  • Security Validation: 7.2/10 (Category avg: 9.1/10)
  • Intelligence Reports: 7.8/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 6.7/10 (Category avg: 8.7/10)
  • Ease of Use: 9.0/10 (Category avg: 9.1/10)

Who Is the Company Behind MetaDefender?

  • Seller: OPSWAT
  • Company Website:
  • Year Founded: 2002
  • HQ Location: Tampa, Florida
  • Twitter: @OPSWAT
    7,257 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,185 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 40% Small, 40% Medium

What Do G2 Reviewers Say About MetaDefender?

AI-generated summary from verified user reviews

Pros
  • Users find MetaDefender to be reliable and simple to manage, enhancing their cybersecurity experience effortlessly.
  • Users appreciate the exceptional security of MetaDefender, highlighting its reliability and effectiveness in threat elimination.
  • Users value the reliable protection of MetaDefender, praising its effectiveness against malware and ease of management.
  • Users benefit from the scanning efficiency of MetaDefender, confidently eliminating threats swiftly and effectively.
  • Users value the effective scanning capabilities of MetaDefender, enhancing security and providing thorough threat detection.
Cons
  • Users find the complex configuration requirements challenging, necessitating significant upfront planning and policy tuning effort.
  • Users experience a difficult setup process during rollout due to extensive policy tuning and adjustment needs.
  • Users experience excessive blocking issues during initial policy tuning, leading to unnecessary restrictions on business files.
  • Users find that overblocking can be an issue, requiring careful policy adjustments to ensure safe files aren't hindered.
  • Users find that policy tuning requires significant effort initially, particularly with archives and mixed file types.

What Are Recent G2 Reviews of MetaDefender?

What Are G2 Users Discussing About MetaDefender?

TechOwl Shield

TechOwl's Attack Surface Dashboard epitomizes the sophistication of our SaaS solution, providing a comprehensive view of your digital threat landscape. This state-of-the-art dashboard offers an interactive heatmap of active alerts, enabling you to effortlessly discern the severity and age of potential threats.

Average Rating: 4.7/5.0

Total Reviews: 6

How Do G2 Users Rate TechOwl Shield?

  • Security Validation: 9.3/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.0/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.0/10 (Category avg: 8.7/10)
  • Ease of Use: 8.6/10 (Category avg: 9.1/10)

Who Is the Company Behind TechOwl Shield?

Who Uses This Product?

  • Company Size: 83% Medium, 17% Small

What Do G2 Reviewers Say About TechOwl Shield?

AI-generated summary from verified user reviews

Pros
  • Users value the strong threat detection capabilities of TechOwl Shield, ensuring comprehensive real-time protection effortlessly.
  • Users appreciate the real-time alerting system of TechOwl Shield, ensuring proactive threat detection effortlessly.
  • Users value the ease of use of TechOwl Shield, enjoying its seamless protection and user-friendly dashboard.
  • Users value the comprehensive monitoring features of TechOwl Shield, enhancing security against various cyber threats.
  • Users commend the exceptional reporting features of TechOwl Shield, enhancing their security and monitoring capabilities effectively.
Cons
  • Users find the false positive alerts of TechOwl Shield to be overly sensitive, sometimes flagging non-threats.
  • Users note the limited customization options for notifications in TechOwl Shield, affecting their overall experience.
  • Users find the intimidating UX of TechOwl Shield challenging, particularly for newcomers, despite its impressive capabilities.

What Are Recent G2 Reviews of TechOwl Shield?

BLINDSPOT

With BLINDSPOT, keep your supply chain safe by exposing hidden risks and predicting future threats. Our risk intelligence platform keeps watch on your organization's digital footprint to quickly identify and manage weak links on your supply chain before they have a chance to harm your business.

Average Rating: 5.0/5.0

Total Reviews: 5

How Do G2 Users Rate BLINDSPOT?

  • Ease of Use: 10.0/10 (Category avg: 9.1/10)

Who Is the Company Behind BLINDSPOT?

  • Seller: PRODAFT
  • Year Founded: 2012
  • HQ Location: Yverdon-les-Bains, CH
  • LinkedIn® Page: www.linkedin.com
    57 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 20% Large, 20% Medium

What Do G2 Reviewers Say About BLINDSPOT?

AI-generated summary from verified user reviews

Pros
  • Users value the accuracy of information in Blindspot, enabling better decision-making in supply chain management.
  • Users appreciate the responsive customer support of BLINDSPOT, simplifying question resolution and enhancing user experience.
  • Users find Blindspot to have a clean interface and easy handling, enhancing their experience in supply risk management.
  • Users find the setup process easy, aided by helpful team support for integrating suppliers into BLINDSPOT.
  • Users value the real-time visibility and clean interface of Blindspot, enhancing proactive insights and resilience in security.
Cons
  • Users find the initial complexity of BLINDSPOT off-putting, though the information becomes clearer with time.
  • Users find the difficult learning curve of BLINDSPOT challenging, impacting their overall experience with the product.

What Are Recent G2 Reviews of BLINDSPOT?

Check Point ThreatCloud AI

Check Point offers comprehensive intelligence to proactively stop threats, manage security services to monitor networks and incident response to quickly respond to and resolve attacks.

Average Rating: 4.7/5.0

Total Reviews: 5

How Do G2 Users Rate Check Point ThreatCloud AI?

  • Security Validation: 9.2/10 (Category avg: 9.1/10)
  • Intelligence Reports: 8.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.2/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind Check Point ThreatCloud AI?

Who Uses This Product?

  • Company Size: 40% Large, 40% Medium

What Do G2 Reviewers Say About Check Point ThreatCloud AI?

AI-generated summary from verified user reviews

Pros
  • Users find the deployment ease of ThreatCloud AI beneficial, enhancing security and efficiency in their systems.
  • Users appreciate the ease of use of Check Point ThreatCloud AI, simplifying deployment and enhancing security efficiency.
  • Users value the enhanced security provided by Check Point ThreatCloud AI, benefiting from updated threat data easily.
  • Users value the updated threat data provided by ThreatCloud AI, enhancing security and saving time effectively.

What Are Recent G2 Reviews of Check Point ThreatCloud AI?

What Are G2 Users Discussing About Check Point ThreatCloud AI?

Domain and IP Intelligence Feeds

Domain and IP Threat Intelligence feeds enable cybersecurity vendors and security operations to make their products and teams faster and more secure. By utilizing machine learning to assess the risk and determine content classifications of hosts, alphaMountain provides real-time threat verdicts for any domain or IP address on the internet. alphaMountain's approach to domain risk is based on three key differentiators: Freshness - real-time domain and IP threat assessments based on first-party algorithms; Fidelity - granularity and context that enable better security outcomes; Factors - contributing rationale that drive all investigations to quick, confident conclusions; By integrating alphaMountain's data into their products, cybersecurity vendors improve the accuracy and performance of their solutions. Security operations teams speed up their investigations through alphaMountain's integrations with leading intelligence platforms including Splunk, SecureX, Maltego, VirusTotal, and more.

Average Rating: 4.7/5.0

Total Reviews: 6

How Do G2 Users Rate Domain and IP Intelligence Feeds?

  • Security Validation: 10.0/10 (Category avg: 9.1/10)
  • Intelligence Reports: 7.5/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 7.5/10 (Category avg: 8.7/10)
  • Ease of Use: 9.3/10 (Category avg: 9.1/10)

Who Is the Company Behind Domain and IP Intelligence Feeds?

  • Seller: alphaMountain AI
  • Year Founded: 2020
  • HQ Location: Salt Lake City, US
  • Twitter: @alphamountainai
    56 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    9 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Medium, 33% Small

What Do G2 Reviewers Say About Domain and IP Intelligence Feeds?

AI-generated summary from verified user reviews

Pros
  • Users value the high accuracy of Domain and IP Intelligence Feeds, ensuring reliable identification of malicious sites.
  • Users value the responsive alerts that effectively enhance security by quickly identifying and blocking emerging threats.
  • Users value the consistent customer support from Domain and IP Intelligence Feeds, enhancing their overall experience and satisfaction.
  • Users appreciate the ease of use of Domain and IP Intelligence Feeds, finding integration seamless and support helpful.
  • Users appreciate the automation capabilities of the Domain and IP Intelligence Feeds, enhancing security and efficiency in investigations.
Cons
  • Users report issues with false positives, leading to mis-categorizations and missed detections of malicious webpages.
  • Users find the product reasonably expensive, but believe the quality justifies the higher price.
  • Users experience poor detection performance with missed threats and overly generic categorizations of malicious webpages.

What Are Recent G2 Reviews of Domain and IP Intelligence Feeds?

DomainTools

DomainTools is the global leader for internet intelligence and the first place security practitioners go when they need to know. The world's most advanced security teams use our solutions to identify external risks, investigate threats, and proactively protect their organizations in a constantly evolving threat landscape. DomainTools constantly monitors the Internet and brings together the most comprehensive and trusted domain, website and DNS data to provide immediate context and machine-learning driven risk analytics delivered in near real-time. Visit domaintools.com to experience firsthand why DomainTools is the first stop for advanced security teams when they need to know.

Average Rating: 3.8/5.0

Total Reviews: 13

How Do G2 Users Rate DomainTools?

  • Security Validation: 7.2/10 (Category avg: 9.1/10)
  • Intelligence Reports: 6.7/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 7.8/10 (Category avg: 8.7/10)
  • Ease of Use: 8.1/10 (Category avg: 9.1/10)

Who Is the Company Behind DomainTools?

  • Seller: DomainTools
  • Year Founded: 2004
  • HQ Location: Seattle, WA, Washington
  • Twitter: @DomainTools
    13,250 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    147 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 62% Small, 31% Large

What Are Recent G2 Reviews of DomainTools?

What Are G2 Users Discussing About DomainTools?

ThreatBolt

ThreatBolt is the only Intelligence-sharing platform thoughtfully designed to meet SOC/MSSP needs. It utilizes AI/ML Powered engine for threat analysis and classification, delivering high-fidelity threat intelligence feeds in real-time with precise scores and industry’s best enrichment.

Average Rating: 4.6/5.0

Total Reviews: 5

How Do G2 Users Rate ThreatBolt?

  • Security Validation: 9.6/10 (Category avg: 9.1/10)
  • Intelligence Reports: 10.0/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 7.8/10 (Category avg: 8.7/10)
  • Ease of Use: 9.3/10 (Category avg: 9.1/10)

Who Is the Company Behind ThreatBolt?

Who Uses This Product?

  • Company Size: 60% Large, 20% Medium

What Do G2 Reviewers Say About ThreatBolt?

AI-generated summary from verified user reviews

Pros
  • Customers value the responsive and knowledgeable customer support offered by ThreatBolt, enhancing their overall experience with the product.
  • Users appreciate the rapid deployment of ThreatBolt, enabling seamless integration and improved threat management efficiency.
  • Users value the ease of use of ThreatBolt, enjoying its intuitive interface and streamlined management of threats.
  • Users value the integration capabilities of ThreatBolt, simplifying threat management with seamless connections to existing security stacks.
  • Users appreciate the robust threat detection capabilities of ThreatBolt, enhancing their overall security management experience.
Cons
  • Users find the lack of customization in ThreatBolt's reporting dashboard limits its effectiveness for diverse organizational needs.

What Are Recent G2 Reviews of ThreatBolt?

Cisco Secure Malware Analytics (Threat Grid)

Threat Grid combines advanced sandboxing with threat intelligence into one unified solution to protect organizations from malware. With a robust, context-rich malware knowledge base, you will understand what malware is doing, or attempting to do, how large a threat it poses, and how to defend against it.

Average Rating: 4.9/5.0

Total Reviews: 4

How Do G2 Users Rate Cisco Secure Malware Analytics (Threat Grid)?

  • Security Validation: 10.0/10 (Category avg: 9.1/10)
  • Intelligence Reports: 10.0/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 10.0/10 (Category avg: 8.7/10)
  • Ease of Use: 8.8/10 (Category avg: 9.1/10)

Who Is the Company Behind Cisco Secure Malware Analytics (Threat Grid)?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • Twitter: @Cisco
    720,366 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO

Who Uses This Product?

  • Company Size: 75% Large, 25% Medium

What Are Recent G2 Reviews of Cisco Secure Malware Analytics (Threat Grid)?

PreCrime Intelligence

PreCrime Intelligence is cybersecurity’s fastest, most accurate predictive intelligence solution, using behavioral AI to predict and preempt attacks weeks before they happen. The exponential growth of network infrastructure has created more attack surfaces than ever before. We use continuous threat exposure management (CTEM) to proactively monitor the internet for suspicious behaviors and dangerous domains. We raise the flag on anomalous activities, before they become a security breach. We go beyond reactive blocklists to equip your team with the most extensive dataset of future malicious infrastructure. Our intelligence feed deliver indicators of future attacks instead of reactive alerts and allows you to establish a proactive security posture. The result: Only 3% overlap with traditional TI, or: 97% unique, proactive data. Every 10 minutes, we monitor the entire internet and evaluate infrastructures based on their behavior. Our AI continuously evolves, requiring less human input while sharpening its accuracy in anomaly detection and risk assessment. Deny malicious infrastructure in near real-time before they launch attacks. Features: - 18 days ahead of traditional intelligence feeds (median) - 99.95% accuracy (less than 0.05% false positives) - ~100,000 proactive indicators of future attacks (IoFA) every day - 20+ million suspicious infrastructures continuously monitored - Easy integration into Firewalls, SIEM/SOAR/TIP, XDR/EDR or DNS resolvers

Average Rating: 5.0/5.0

Total Reviews: 4

How Do G2 Users Rate PreCrime Intelligence?

  • Intelligence Reports: 10.0/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.3/10 (Category avg: 8.7/10)
  • Ease of Use: 8.8/10 (Category avg: 9.1/10)

Who Is the Company Behind PreCrime Intelligence?

  • Seller: BforeAI
  • Year Founded: 2024
  • HQ Location: New York City, US
  • LinkedIn® Page: www.linkedin.com
    65 employees on LinkedIn®
  • Ownership: Privately owned

Who Uses This Product?

  • Company Size: 50% Small, 25% Medium

What Do G2 Reviewers Say About PreCrime Intelligence?

AI-generated summary from verified user reviews

Pros
  • Users value the proactive alerts and unique predictive feed from PreCrime Intelligence, enhancing their investigation management capabilities.
  • Users value the proactive threat detection of PreCrime Intelligence, allowing timely investigations to fortify vulnerable systems.
  • Users value the proactive alerts from PreCrime, allowing timely investigation and fortification of at-risk systems.
  • Users find the unique predictive feed of PreCrime Intelligence invaluable for proactive threat investigation and response.
  • Users praise the easy integrations of PreCrime Intelligence, enhancing their ability to stay ahead of threats seamlessly.
Cons
  • Users report occasional slow performance during high load times, which can hinder their overall experience with PreCrime Intelligence.

What Are Recent G2 Reviews of PreCrime Intelligence?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 22, 2025