Best Enterprise Threat Intelligence Software - Page 2

How Many Threat Intelligence Software Products Does G2 Track?

Total Products under this Category: 217

Category Stats (Sep 2026)

  • Average Rating: 4.58/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: UpGuard Breach Risk (+0.92%) - Among all products in this category, UpGuard Breach Risk recorded the largest rating increase compared to last month

Last updated: September 01, 2026

How Does G2 Rank Threat Intelligence Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,600+ Authentic Reviews
  • 217+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

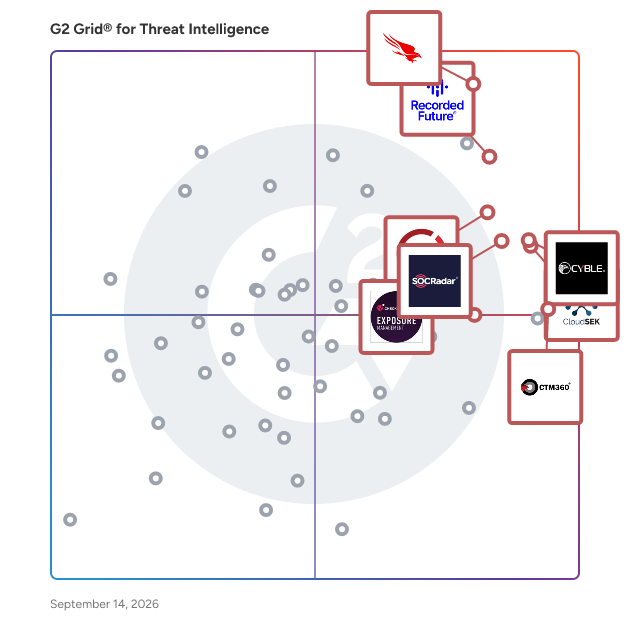
G2 Grid® for Threat Intelligence Software

G2 Grid® for Threat Intelligence Software plotting products by satisfaction and market presence

Highlighted products: Recorded Future, CrowdStrike Falcon Endpoint Protection Platform, CloudSEK, ZeroFox, Cyble, SOCRadar Extended Threat Intelligence, Check Point Exposure Management, and CTM360.

Underlying data: [Grid® JSON](https://www.g2.com/categories/threat-intelligence/grids.json?focus%5B%5D=recorded-future&focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=cloudsek&focus%5B%5D=zerofox&focus%5B%5D=cyble&focus%5B%5D=socradar-extended-threat-intelligence&focus%5B%5D=check-point-exposure-management&focus%5B%5D=ctm360-ctm360&segment=enterprise)

DeCYFIR by CYFIRMA

DeCYFIR is an AI-powered preemptive External Threat Landscape Management platform engineered to help organizations predict and prevent cyberattacks before they occur. Adopting a hacker's perspective, it delivers early warnings, prioritized insights, and actionable intelligence across the full external threat landscape. Built on a proprietary 9-pillar architecture — spanning Attack Surface Discovery & Intelligence, Vulnerability Intelligence & Threat Prioritization, Brand & Online Exposure Management, Digital Risk & Identity Protection, Third Party Risk Management, Situational Awareness & Emerging Threats, Predictive Threat Intelligence, Threat Adaptive Awareness & Training, and Sector Tailored Deception Intelligence. DeCYFIR correlates signals across all pillars to cut through noise, surface what is truly critical, and empower security teams to stay decisively ahead of emerging threats.

Average Rating: 4.8/5.0

Total Reviews: 46

How Do G2 Users Rate DeCYFIR by CYFIRMA?

  • Security Validation: 9.2/10 (Category avg: 9.0/10)
  • Intelligence Reports: 9.1/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.2/10 (Category avg: 8.7/10)
  • Ease of Use: 9.2/10 (Category avg: 9.1/10)

Who Is the Company Behind DeCYFIR by CYFIRMA?

  • Seller: CYFIRMA
  • Year Founded: 2017
  • HQ Location: Singapore, SG
  • Twitter: @cyfirma
    1,002 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    135 employees on LinkedIn®
  • Phone: marketing@cyfirma.com

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 50% Medium, 26% Large

What Do G2 Reviewers Say About DeCYFIR by CYFIRMA?

AI-generated summary from verified user reviews

Pros
  • Users value the thorough threat detection capabilities of DeCYFIR, enhancing cybersecurity measures against potential attacks.
  • Users value the informative threat intelligence from DeCYFIR, aiding in proactive prevention of cyber incidents.
  • Users value DeCYFIR for its contextual and predictive intelligence, enhancing threat visibility and strategic risk management.
  • Users value DeCYFIR's comprehensive threat intelligence features, enhancing proactive defense against cyber threats effectively.
  • Users value the advanced security insights from DeCYFIR, enhancing their ability to prevent and respond to threats.
Cons
  • Users find DeCYFIR not user-friendly, citing a confusing UI and technical complexity for less experienced individuals.
  • Users find DeCYFIR's interface to be complex and overwhelming, particularly for those unfamiliar with threat intelligence workflows.
  • Users find DeCYFIR's learning curve daunting, as its complexity may overwhelm new users without proper training.
  • Users find the platform's limited customization options challenging, impacting their overall user experience.
  • Users find DeCYFIR's complex setup challenging, particularly for newcomers and those needing customized dashboards or API integration.

What Are Recent G2 Reviews of DeCYFIR by CYFIRMA?

UpGuard Breach Risk

UpGuard Breach Risk is an AI-powered attack surface management solution that empowers lean security teams to see what attackers see and take control of their external risk. As part of the UpGuard Cyber Risk Posture Management (CRPM) platform, it integrates seamlessly with Vendor Risk and User Risk to provide a unified defense against modern cyber threats. As organizations scale, their digital footprint expands beyond the firewall, creating dangerous blind spots. Traditional tools often miss these external signals, leaving teams vulnerable to shadow IT, exposed credentials, and brand abuse. Breach Risk solves this by combining Attack Surface Management (ASM), Digital Risk Protection (DRP), and advanced Threat Monitoring into a single, automated platform. Key Capabilities: • Continuous Attack Surface Discovery: You can’t protect what you can’t see. Breach Risk continuously maps your internet-facing assets like domains, IPs, and cloud resources, to uncover shadow IT and misconfigurations. We automatically inventory your digital footprint to close the gaps that attackers exploit, ensuring no asset goes unmonitored. • AI-Powered Threat Monitoring: Move beyond static feeds. Our Threat Monitoring engine scans the open, deep, and dark web to detect leaked employee credentials, infostealer logs, and malware signals before they are weaponized. Unlike traditional threat intelligence that floods you with raw data, our AI Threat Analyst triages signals to filter out noise and prioritize high-fidelity threats for immediate action. • Brand Protection & Disinformation Defense: Safeguard your reputation against fraud. We proactively detect lookalike domains (typosquatting) and fraudulent social media profiles used to launch phishing attacks and disinformation campaigns. Our integrated workflows help you identify and neutralize these impersonation attempts before they erode customer trust. • Actionable Remediation: We don’t just find problems; we help you fix them. Breach Risk provides guided remediation plans and integrates with your security tech stack, allowing lean teams to accelerate response times without adding headcount. By translating complex technical risks into a quantifiable Cyber Risk Score, UpGuard enables security leaders to benchmark performance, justify budget, and prove risk reduction to the board.

Average Rating: 4.5/5.0

Total Reviews: 27

How Do G2 Users Rate UpGuard Breach Risk?

  • Security Validation: 10.0/10 (Category avg: 9.0/10)
  • Intelligence Reports: 8.3/10 (Category avg: 9.1/10)
  • Ease of Use: 9.4/10 (Category avg: 9.1/10)

Who Is the Company Behind UpGuard Breach Risk?

  • Seller: UpGuard
  • Company Website:
  • Year Founded: 2012
  • HQ Location: Mountain View, California
  • Twitter: @UpGuard
    8,705 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    402 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 59% Large, 37% Medium

What Are Recent G2 Reviews of UpGuard Breach Risk?

Dataminr

Dataminr provides a revolutionary real-time AI platform for detecting events, risks and critical information from public data signals. Recognized as one of the world's leading AI companies, Dataminr enables faster real-time response and more effective risk management for public and private sector organizations, including multinational corporations, governments, NGOs, and newsrooms. Dataminr Pulse for Corporate Security With Dataminr Pulse for Corporate Security, you can detect, visualize, and respond to events and threats in real-time to: • Improve People Safety: Improve the safety of your employees, executives, customers, and contractors against external risks and threats wherever they are—in the office, working from home, or on a business trip. • Secure Facilities and Events: Protect all your global premises—including offices, manufacturing plants, warehouses, data centers, retail stores, stadiums, arenas, and temporary work locations—against external threats and hazards. • Increase Operational Resilience: Safeguard your revenue-generating activities against external threats and disruptive events that could directly or indirectly affect core business operations. Dataminr Pulse for Cyber Risk Enhance cyber resilience with Dataminr Pulse for Cyber Risk, a real-time, external cyber threat detection solution that empowers your team to: • Identify Digital Risk: Respond quickly to early warnings of threats to and exposures of your organization's digital assets. • Expose Third-Party Risk: Mitigate risk to your organization with increased visibility into threats to your subsidiaries, vendors, and service providers. • Receive Vulnerability Intelligence: Improve prioritization of patching with visibility into the full lifecycle of vulnerabilities. Get alerts about exploits, emerging and trending vulnerabilities, and more. • Respond to Cyber-Physical Risks: Respond to real-time alerts on cyber threats affecting physical assets and physical threats affecting digital assets.

Average Rating: 4.5/5.0

Total Reviews: 48

How Do G2 Users Rate Dataminr?

  • Security Validation: 7.6/10 (Category avg: 9.0/10)
  • Intelligence Reports: 7.6/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.0/10 (Category avg: 8.7/10)
  • Ease of Use: 8.5/10 (Category avg: 9.1/10)

Who Is the Company Behind Dataminr?

  • Seller: Dataminr
  • Year Founded: 2009
  • HQ Location: New York, NY
  • Twitter: @Dataminr
    16,454 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    880 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Security and Investigations
  • Company Size: 56% Large, 33% Small

What Do G2 Reviewers Say About Dataminr?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Dataminr, noting quick setup and real-time alert capabilities for critical events.
  • Users value the real-time alerts from Dataminr, significantly enhancing their awareness and proactive risk management capabilities.
  • Users appreciate the real-time monitoring capabilities of Dataminr, significantly enhancing awareness and proactive risk management.
  • Users value the real-time alert notifications from Dataminr, enhancing situational awareness and proactive decision-making.
  • Users value Dataminr for its ability to provide timely and invaluable information across various applications like breaking news.
Cons
  • Users experience inefficient alerts with Dataminr, struggling with irrelevant notifications that lead to information overload.
  • Users find the complexity of Dataminr to be overwhelming, leading to information overload and challenges in customization.
  • Users frequently experience false positives with Dataminr alerts, leading to irrelevant notifications and potential overwhelm.
  • Users often experience information overload with Dataminr due to an excess of notifications that complicate focus on relevant updates.
  • Users note a steep learning curve with Dataminr, requiring time and effort to fully leverage its capabilities.

What Are Recent G2 Reviews of Dataminr?

What Are G2 Users Discussing About Dataminr?

Trellix Threat Intelligence Exchange

Trellix Threat Intelligence Exchange is a software that facilitates the real-time sharing, management, and integration of threat intelligence across an organization’s security infrastructure. The software enables automated detection and response to threats by correlating data from multiple security sources to identify malicious files, URLs, or other indicators of compromise. It centralizes threat intelligence, allowing security teams to enhance protection by leveraging collective data from endpoints, networks, and other systems. The software helps streamline workflows by reducing manual analysis and supports the investigation and containment of security incidents. Trellix Threat Intelligence Exchange is designed to address the challenge of timely threat identification and unified intelligence management in enterprise environments.

Average Rating: 4.0/5.0

Total Reviews: 52

How Do G2 Users Rate Trellix Threat Intelligence Exchange?

  • Security Validation: 8.8/10 (Category avg: 9.0/10)
  • Intelligence Reports: 8.6/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.1/10 (Category avg: 8.7/10)
  • Ease of Use: 8.4/10 (Category avg: 9.1/10)

Who Is the Company Behind Trellix Threat Intelligence Exchange?

  • Seller: Trellix
  • Year Founded: 2004
  • HQ Location: Plano, TX
  • Twitter: @Trellix
    241,168 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,811 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 46% Medium, 37% Small

What Are Recent G2 Reviews of Trellix Threat Intelligence Exchange?

What Are G2 Users Discussing About Trellix Threat Intelligence Exchange?

ThreatMon

ThreatMon is an AI-powered cyber risk intelligence platform designed to assist organizations in detecting, analyzing, and responding to external cyber threats that may impact their digital assets, brand reputation, and third-party ecosystem. This comprehensive solution provides real-time visibility into an organization’s attack surface exposure, the evolving threat landscape, and overall cyber risk posture, all accessible from a single, unified platform. The platform is particularly beneficial for security and risk management teams who require a holistic view of their cyber environment. ThreatMon integrates various functionalities including attack surface management, threat intelligence, dark web monitoring, fraud detection, surface web monitoring, and supply chain risk intelligence. This integration eliminates the need for multiple, disconnected tools, streamlining the process of threat detection and risk assessment. By consolidating these capabilities, ThreatMon allows organizations to efficiently manage their cyber risk landscape while reducing operational complexity. Key features of ThreatMon include the ability to discover exposed assets, detect phishing attempts, monitor for brand impersonation, and track leaked credentials and data breaches. Additionally, it provides insights into threat actors and assesses vendor and third-party risks, which is crucial for organizations that rely on a complex ecosystem of partners and suppliers. The platform’s built-in governance, risk, and compliance (GRC) capabilities further enhance its utility by mapping compliance requirements and generating executive-level reports. This functionality translates technical findings into actionable business-level insights, enabling stakeholders to make informed decisions regarding their cyber risk management strategies. By unifying external exposure monitoring, threat intelligence, fraud detection, supply chain risk visibility, and governance-level reporting, ThreatMon empowers both security operations teams and executives to understand, prioritize, and respond to cyber risks more effectively. This shift from fragmented, reactive security measures to a proactive, intelligence-driven approach allows organizations to better safeguard their assets and maintain their reputation in an increasingly complex digital landscape. With ThreatMon, organizations can enhance their overall security posture and foster a culture of proactive risk management, ensuring they remain resilient against evolving cyber threats.

Average Rating: 4.9/5.0

Total Reviews: 26

How Do G2 Users Rate ThreatMon?

  • Security Validation: 9.8/10 (Category avg: 9.0/10)
  • Intelligence Reports: 9.9/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.6/10 (Category avg: 8.7/10)
  • Ease of Use: 9.7/10 (Category avg: 9.1/10)

Who Is the Company Behind ThreatMon?

  • Seller: ThreatMon
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Sterling VA
  • Twitter: @MonThreat
    17,241 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    43 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 38% Large, 38% Medium

What Do G2 Reviewers Say About ThreatMon?

AI-generated summary from verified user reviews

Pros
  • Users value the advanced threat detection capabilities of ThreatMon, offering actionable insights and early warnings.
  • Users value the reliable threat intelligence of ThreatMon, enhancing security through proactive threat detection and response.
  • Users value the constant monitoring and AI-driven analysis of ThreatMon, enhancing their cybersecurity posture effectively.
  • Users value the real-time notifications from ThreatMon, enhancing their ability to stay ahead of potential threats.
  • Users value the robust security protection offered by ThreatMon, enhancing confidence and proactive threat management.
Cons
  • Users find the threat data overwhelming, making it challenging to effectively manage and understand the Mobile Application Monitoring Module.
  • Users find the limited reporting features restrictive, desiring more customization and clarity for specific needs.
  • Users find the excessive notifications from ThreatMon create unnecessary work and can be overwhelming initially.
  • Users highlight a lack of customization in reporting features, making it difficult to tailor data to specific needs.
  • Users find the missing features in ThreatMon's reporting limits customization and flexibility for tailored insights.

What Are Recent G2 Reviews of ThreatMon?

Intezer

Intezer automates the entire alert triage process, like an extension of your team handling Tier 1 SOC tasks for every alert at machine-speed. Intezer monitors incoming incidents from endpoint, reported phishing pipelines, or SIEM tools, then autonomously collects evidence, investigates, makes triage decisions, and escalates only the serious threats to your team for human intervention. Power your SOC with artificial intelligence that makes sure every alert is deeply analyzed (including every single artifact like files, URLs, endpoint memory, etc.), detecting malicious code in memory and other evasive threats. Fast set up and integrations with your SOC team's workflows (EDR, SOAR, SIEM, etc.) means Intezer's AI can immediately start filtering out false positives, giving you detailed analysis about every threat, and speeding up your incident response time. With Intezer: • Reduce Tier 1 escalation, sending only 4% of alerts on average to your team for immediate action. • Identify up to 97% of false positive alerts without taking any time from your analysts. • Reduce average triage time to 5 minutes or less, while giving your analysts deep context about every alert to prioritize critical treats and respond faster.

Average Rating: 4.5/5.0

Total Reviews: 187

How Do G2 Users Rate Intezer?

  • Security Validation: 8.8/10 (Category avg: 9.0/10)
  • Intelligence Reports: 9.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.0/10 (Category avg: 8.7/10)
  • Ease of Use: 9.1/10 (Category avg: 9.1/10)

Who Is the Company Behind Intezer?

  • Seller: Intezer
  • Year Founded: 2015
  • HQ Location: New York
  • Twitter: @IntezerLabs
    10,170 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    89 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Student
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 54% Small, 23% Medium

What Do G2 Reviewers Say About Intezer?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the robust security features of Intezer, ensuring timely detection and blocking of malware.
  • Users value the effective malware detection and security features of Intezer that enhance system protection.
  • Users value Intezer for its effective malware detection and response capabilities, enhancing overall security and incident management.
  • Users value the high detection accuracy of Intezer, ensuring timely malware detection and enhanced system security.
  • Users appreciate the ease of use of Intezer, making malware detection and incident response straightforward and efficient.
Cons
  • Users feel the inability to control file visibility limits their privacy and management options in certain situations.
  • Users report complex interface issues with Intezer, making navigation challenging and less intuitive.
  • Users are concerned about limited file visibility control, which may impact their data privacy and access management.
  • Users find the difficult navigation of Intezer frustrating, with a less-than-ideal UI and small text affecting readability.
  • Users find the expensive pricing of Intezer problematic, especially with the limited free tier and some GUI issues.

What Are Recent G2 Reviews of Intezer?

What Are G2 Users Discussing About Intezer?

Pentera

Pentera is the category leader for Automated Security Validation, allowing every organization to test with ease the integrity of all cybersecurity layers, unfolding true, current security exposures at any moment, at any scale. Thousands of security professionals and service providers around the world use Pentera to guide remediation and close security gaps before they are exploited. Its customers include Casey's General Stores, Emeria, LuLu International Exchange, IP Telecom PT, BrewDog, City National Bank, Schmitz Cargobull, and MBC Group. Pentera is backed by leading investors such as K1 Investment Management, Insight Partners, Blackstone, Evolution Equity Partners, and AWZ. Visit https://pentera.io for more information.

Average Rating: 4.6/5.0

Total Reviews: 181

How Do G2 Users Rate Pentera?

  • Security Validation: 8.2/10 (Category avg: 9.0/10)
  • Intelligence Reports: 8.9/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 7.8/10 (Category avg: 8.7/10)
  • Ease of Use: 8.7/10 (Category avg: 9.1/10)

Who Is the Company Behind Pentera?

  • Seller: Pentera
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Boston, MA
  • Twitter: @penterasec
    3,291 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    460 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Government Administration, Banking
  • Company Size: 51% Large, 35% Medium

What Do G2 Reviewers Say About Pentera?

AI-generated summary from verified user reviews

Pros
  • Users value the effective vulnerability scanning and remediation capabilities of Pentera, enhancing overall security posture.
  • Users value the automation capabilities of Pentera, enhancing their security testing and validation processes efficiently.
  • Users value the responsive customer support from Pentera, enhancing their experience and facilitating smooth operations.
  • Users value the time-saving automation of Pentera, enabling more efficient focus on critical cybersecurity tasks.
  • Users value the fully automated testing of Pentera, appreciating its ease of use and quick implementation.
Cons
  • Users find the reporting inadequate, suggesting it requires improvement for better enterprise-level insights.
  • Users are concerned about the missing features in Pentera, including updates on vulnerabilities and insufficient RBAC options.
  • Users find Pentera to be resource intensive, as it demands significant system resources for optimal performance.
  • Users express concern about the lack of a robust RBAC system, limiting proper access control and user rights management.
  • Users are frustrated by access restrictions due to insufficient RBAC, limiting user capabilities and adaptability.

What Are Recent G2 Reviews of Pentera?

CYREBRO

CYREBRO is an AI-native Managed Detection and Response solution, providing the core foundation and capabilities of a state-level Security Operations Center delivered through its cloud-based, interactive SOC Platform. CYREBRO rapidly detects, analyzes, investigates and responds to cyber threats, for businesses of all sizes.

Average Rating: 4.3/5.0

Total Reviews: 128

How Do G2 Users Rate CYREBRO?

  • Security Validation: 8.9/10 (Category avg: 9.0/10)
  • Intelligence Reports: 8.6/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.8/10 (Category avg: 9.1/10)

Who Is the Company Behind CYREBRO?

  • Seller: CYREBRO
  • Year Founded: 2013
  • HQ Location: Tel Aviv, IL
  • Twitter: @CYREBRO_IO
    307 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 64% Medium, 25% Small

What Do G2 Reviewers Say About CYREBRO?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of CYREBRO, thanks to its intuitive UI and quick access to investigations.
  • Users value the responsive and knowledgeable customer support of CYREBRO, enhancing their overall experience and satisfaction.
  • Users value the dashboard usability of CYREBRO, benefiting from easy management and seamless incident response.
  • Users value the real-time alerts and actionable insights from CYREBRO, enhancing their security response and peace of mind.
  • Users value the real-time alerts from CYREBRO that enhance response time and simplify incident management effectively.
Cons
  • Users report experiencing update issues with alert management, leading to overwhelmed users and hindered onboarding processes.
  • Users face communication issues with Cyrebro support, experiencing slow response times and vague information that complicates problem resolution.
  • Users report poor customer support with slow response times and limited availability, impacting their overall experience.
  • Users often find ineffective alerts from CYREBRO, struggling with overwhelming volume and vague details requiring further support.
  • Users report an inefficient alert system, with overwhelming notifications and redundant alerts complicating their experience.

What Are Recent G2 Reviews of CYREBRO?

What Are G2 Users Discussing About CYREBRO?

Zignal Labs

Zignal's real-time intelligence technology helps the world's largest organizations protect their people, places, and position.

Average Rating: 4.0/5.0

Total Reviews: 40

How Do G2 Users Rate Zignal Labs?

  • Ease of Use: 7.2/10 (Category avg: 9.1/10)

Who Is the Company Behind Zignal Labs?

  • Seller: Zignal Labs
  • Year Founded: 2011
  • HQ Location: San Francisco, California
  • Twitter: @ZignalLabs
    3,330 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    64 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Public Relations and Communications
  • Company Size: 40% Large, 30% Small

What Are Recent G2 Reviews of Zignal Labs?

What Are G2 Users Discussing About Zignal Labs?