Best Enterprise Threat Intelligence Software

How Many Threat Intelligence Software Products Does G2 Track?

Total Products under this Category: 217

Category Stats (Sep 2026)

  • Average Rating: 4.58/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: UpGuard Breach Risk (+0.92%) - Among all products in this category, UpGuard Breach Risk recorded the largest rating increase compared to last month

Last updated: September 01, 2026

How Does G2 Rank Threat Intelligence Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,600+ Authentic Reviews
  • 217+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

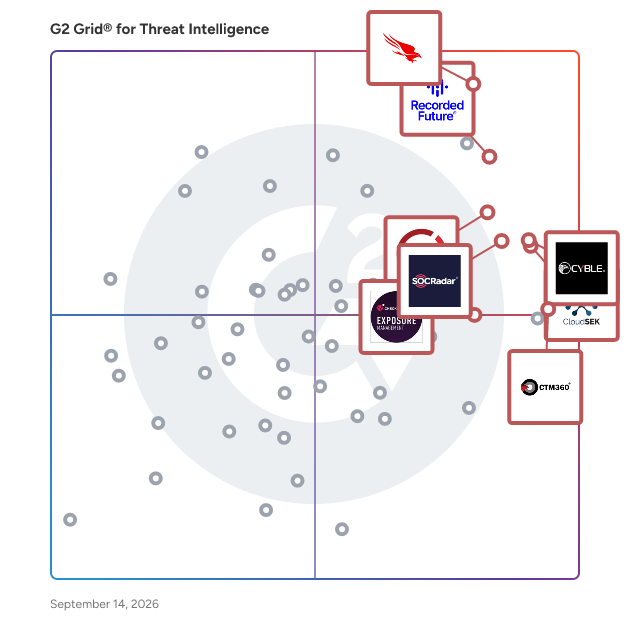
G2 Grid® for Threat Intelligence Software

G2 Grid® for Threat Intelligence Software plotting products by satisfaction and market presence

Highlighted products: Recorded Future, CrowdStrike Falcon Endpoint Protection Platform, CloudSEK, ZeroFox, Cyble, SOCRadar Extended Threat Intelligence, Check Point Exposure Management, and CTM360.

Underlying data: [Grid® JSON](https://www.g2.com/categories/threat-intelligence/grids.json?focus%5B%5D=recorded-future&focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=cloudsek&focus%5B%5D=zerofox&focus%5B%5D=cyble&focus%5B%5D=socradar-extended-threat-intelligence&focus%5B%5D=check-point-exposure-management&focus%5B%5D=ctm360-ctm360&segment=enterprise)

Recorded Future

Recorded Future is the world’s largest threat intelligence company. Recorded Future’s Intelligence Cloud provides end-to-end intelligence across adversaries, infrastructure, and targets. Indexing the internet across the open web, dark web, and technical sources, Recorded Future provides real-time visibility into an expanding attack surface and threat landscape, empowering clients to act with speed and confidence to reduce risk and securely drive business forward. Headquartered in Boston with offices and employees around the world, Recorded Future works with over 1,900 businesses and government organizations across 80 countries to provide real-time, unbiased and actionable intelligence. Learn more at recordedfuture.com.

Average Rating: 4.5/5.0

Total Reviews: 226

How Do G2 Users Rate Recorded Future?

  • Security Validation: 8.2/10 (Category avg: 9.0/10)
  • Intelligence Reports: 8.8/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 7.8/10 (Category avg: 8.7/10)
  • Ease of Use: 8.4/10 (Category avg: 9.1/10)

Who Is the Company Behind Recorded Future?

  • Seller: Recorded Future
  • Company Website:
  • Year Founded: 2009
  • HQ Location: Somerville, US
  • Twitter: @RecordedFuture
    107,965 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,150 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Cyber Threat Intelligence Analyst, Threat Intelligence Analyst
  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 65% Large, 20% Medium

What Do G2 Reviewers Say About Recorded Future?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Recorded Future, finding the interface intuitive and features beneficial for daily tasks.
  • Users enjoy the advanced customization features of Recorded Future, providing in-depth insights and alerts for cyber threats.
  • Users value the intelligent insights from Recorded Future, enhancing their understanding of critical data relationships effectively.
  • Users value the effective threat detection capabilities of Recorded Future, enabling prompt response to potential security risks.
  • Users value the actionable threat intelligence from Recorded Future, enhancing their vulnerability management and overall security posture.
Cons
  • Users find the navigation complex in Recorded Future, leading to difficulties in creating accurate queries and managing data.
  • Users often mention the high cost of Recorded Future, which can be challenging for teams with tight budgets.
  • Users find the learning curve steep for Recorded Future, making quick adjustments and navigation challenging.

What Are Recent G2 Reviews of Recorded Future?

What Are G2 Users Discussing About Recorded Future?

CrowdStrike Falcon Endpoint Protection Platform

Organizations today face a serious challenge: managing numerous security vendors and tools while confronting an ever-evolving threat landscape. Sophisticated adversaries are becoming smarter, faster, and more evasive, launching complex attacks that can strike in minutes or even seconds. Traditional security approaches struggle to keep pace, leaving businesses vulnerable. The CrowdStrike Falcon Platform addresses this by offering a unified, cloud-native solution. It consolidates previously siloed security solutions and incorporates third-party data into a single platform with one efficient and resource-conscious agent, leveraging advanced AI and real-time threat intelligence. This approach simplifies security operations, speeds analyst decision making, and enhances protection to stop the breach, allowing organizations to reduce risk with less complexity and lower costs. CrowdStrike's Falcon Platform includes: - Endpoint Security: Secure the endpoint, stop the breach - Identify Protection: Identity is the front line, defend it - Next-Gen SIEM: The future of SIEM, today - Data Protection: Real-time data protection from endpoint to cloud - Exposure Management: Understand risk to stop breaches - Charlotte AI: Powering the next evolution of the SOC

Average Rating: 4.7/5.0

Total Reviews: 543

How Do G2 Users Rate CrowdStrike Falcon Endpoint Protection Platform?

  • Security Validation: 9.4/10 (Category avg: 9.0/10)
  • Intelligence Reports: 9.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.4/10 (Category avg: 8.7/10)
  • Ease of Use: 9.0/10 (Category avg: 9.1/10)

Who Is the Company Behind CrowdStrike Falcon Endpoint Protection Platform?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • Twitter: @CrowdStrike
    110,809 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Analyst, Security Engineer
  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 46% Large, 40% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Endpoint Protection Platform?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the lightweight performance and powerful threat detection of CrowdStrike Falcon, enhancing security without slowing down systems.
  • Users commend the effective threat detection capabilities of CrowdStrike Falcon, ensuring robust security without system slowdowns.
  • Users appreciate the ease of use of CrowdStrike Falcon, benefiting from its lightweight impact and efficient incident management.
  • Users appreciate the advanced real-time threat protection of CrowdStrike Falcon, ensuring efficient security without system performance issues.
  • Users praise the exceptional threat detection of CrowdStrike Falcon, noting its effectiveness against both known and unknown threats.
Cons
  • Users find the cost prohibitive for smaller organizations, especially with additional modules increasing overall expenses.
  • Users find the complexity of the user interface and additional costs challenging, complicating their overall experience.
  • Users face a steep learning curve with CrowdStrike’s query language, making transitions from other platforms challenging.
  • Users find the limited features challenging, especially concerning cost and technical accessibility for smaller businesses.
  • Users find that pricing can be a barrier for smaller organizations, complicating access to advanced features.

What Are Recent G2 Reviews of CrowdStrike Falcon Endpoint Protection Platform?

What Are G2 Users Discussing About CrowdStrike Falcon Endpoint Protection Platform?

CloudSEK

CloudSEK is a contextual AI company that predicts Cyber Threats. We combine the power of Cyber Crime monitoring, Brand Monitoring, Attack Surface monitoring, and Supply Chain intelligence to give context to our customers’ digital risks.

Average Rating: 4.8/5.0

Total Reviews: 137

How Do G2 Users Rate CloudSEK?

  • Security Validation: 9.4/10 (Category avg: 9.0/10)
  • Intelligence Reports: 9.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.4/10 (Category avg: 8.7/10)
  • Ease of Use: 9.6/10 (Category avg: 9.1/10)

Who Is the Company Behind CloudSEK?

  • Seller: CloudSEK
  • Year Founded: 2015
  • HQ Location: Singapore, SG
  • Twitter: @cloudsek
    2,417 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    247 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Analyst, Analyst
  • Top Industries: Financial Services, Airlines/Aviation
  • Company Size: 53% Large, 31% Medium

What Do G2 Reviewers Say About CloudSEK?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of CloudSEK, noting its smooth functions and intuitive dashboard for seamless monitoring.
  • Users value the continuous monitoring and real-time alerts provided by CloudSEK for effective brand oversight.
  • Users praise the responsive customer support of CloudSEK, which effectively resolves issues quickly and efficiently.
  • Users praise CloudSEK's excellent coverage and AI-driven threat intelligence, enhancing cybersecurity and providing invaluable insights.
  • Users value the real-time visibility into external threats offered by CloudSEK, enhancing proactive risk management.
Cons
  • Users are frustrated by the high rate of false positives in alerts for credential breaches and domain impersonation.
  • Users experience inefficient alerts from CloudSEK, often overwhelming them with false positives and complicating threat prioritization.
  • Users experience dashboard issues with false positives, cluttered layouts, and a need for further customization and basic features.
  • Users experience inefficient alert systems, struggling with false positives and difficulty in managing genuine threats effectively.
  • Users find the complex UI of CloudSEK overwhelming, making it challenging to interpret key information effectively.

What Are Recent G2 Reviews of CloudSEK?

ZeroFox

ZeroFox is the solution used to illuminate threat actor intent, mitigate threats and exposures, remove threats from the internet, and preemptively safeguard your reputation. ZeroFox uniquely fuses the core capabilities of Cyber Threat Intelligence, Brand and Domain Protection, Attack Surface Intelligence, Executive Protection and Physical Security Intelligence in one platform packed with intelligence you’ll actually use. ZeroFox defends your business from the everyday attacks that impact revenue, erode trust, and frustrate teams by: Discovering exposed assets, brands, domains, accounts, and emerging threats Validating the risks that matter most to you and your digital estate Disrupting attacks before they harm your business, your customers, and your people Our continuous cycle—Discover, Validate, Disrupt—delivers outcomes and helps organizations achieve deeper threat contextualization, faster detection and response times, and longer-term cost savings by anticipating, understanding, and mitigating external digital threats at scale. Join thousands of customers, including some of the largest public sector organizations and leaders in finance, media, technology, retail, and healthcare, and let ZeroFox deliver timely, personal, and usable intelligence so you can stay ahead of what’s next and reclaim what’s right.

Average Rating: 4.4/5.0

Total Reviews: 169

How Do G2 Users Rate ZeroFox?

  • Security Validation: 8.5/10 (Category avg: 9.0/10)
  • Intelligence Reports: 8.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 7.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.8/10 (Category avg: 9.1/10)

Who Is the Company Behind ZeroFox?

  • Seller: ZeroFox
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Baltimore, MD
  • Twitter: @ZeroFOX
    5,205 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    856 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Cyber Security Analyst
  • Top Industries: Financial Services, Banking
  • Company Size: 50% Large, 28% Medium

What Do G2 Reviewers Say About ZeroFox?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use in ZeroFox, appreciating smooth onboarding and effortless setup for brand protection.
  • Users value ZeroFox for its effective scam site detection and exceptional brand protection, enhancing overall security effortlessly.
  • Users value the real-time threat visibility ZeroFox provides, enhancing external security across various digital platforms.
  • Users value the quick and effective alert notifications from ZeroFox, enhancing their daily operational efficiency and response.
  • Users value the effective alert system of ZeroFox, which enhances daily operations and decision-making through timely notifications.
Cons
  • Users express frustration with inefficient alerts from ZeroFox, as takedowns may take too long or remain incomplete.
  • Users experience false alarms from ZeroFox, leading to time-consuming manual reviews of repetitive alerts.
  • Users experience slow performance with ZeroFox, including delays in alert reporting and slow UI loading times.
  • Users experience frequent false positive alerts with ZeroFox, leading to time-consuming manual reviews and inefficiencies.
  • Users experience an inefficient alert system with delays and false positives affecting timely threat response.

What Are Recent G2 Reviews of ZeroFox?

What Are G2 Users Discussing About ZeroFox?

Cyble

Cyble is an AI-native cybersecurity solution designed to help organizations enhance their digital security posture through real-time intelligence, detection, and response capabilities. By leveraging advanced agentic AI and processing vast amounts of data, Cyble empowers businesses to navigate the complexities of the cyber threat landscape effectively. Its unique approach involves collecting and enriching signals from various sources, including the dark web, deep web, and surface web, providing unparalleled visibility into emerging threats and adversarial activities. Targeting a wide range of industries, Cyble's platform is particularly beneficial for security teams, risk management professionals, and organizations that prioritize safeguarding their digital assets. The comprehensive suite of solutions offered by Cyble includes Threat Intelligence, Dark Web & Deep Web Monitoring, Attack Surface Management (ASM), and Brand Intelligence, among others. These tools are designed to address specific use cases such as identifying vulnerabilities, monitoring brand reputation, and managing third-party risks, making it an essential resource for organizations aiming to bolster their cybersecurity measures. Cyble's key features are centered around its unified platform, which integrates multiple cybersecurity functions into a single interface. This integration allows for seamless communication between different security components, enabling teams to anticipate, identify, and neutralize threats with remarkable speed and precision. For instance, the Digital Forensics & Incident Response (DFIR) capabilities equip organizations with the tools needed to investigate and respond to incidents effectively, while the DDoS Protection and Cloud Security Posture Management (CSPM) features ensure that businesses can maintain operational integrity even under attack. Moreover, Cyble stands out in its category by combining vast data intelligence with cutting-edge AI automation. This proactive defense strategy not only helps organizations react to cyber threats but also empowers them to stay ahead of potential risks. By enhancing visibility into the threat landscape and providing actionable insights, Cyble enables enterprises to protect their assets, safeguard brand trust, and operate with confidence in an increasingly complex digital environment. The result is a robust cybersecurity framework that supports organizations in navigating the ever-evolving challenges of the cyber world.

Average Rating: 4.8/5.0

Total Reviews: 147

How Do G2 Users Rate Cyble?

  • Security Validation: 9.3/10 (Category avg: 9.0/10)
  • Intelligence Reports: 9.6/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.3/10 (Category avg: 8.7/10)
  • Ease of Use: 9.5/10 (Category avg: 9.1/10)

Who Is the Company Behind Cyble?

  • Seller: Cyble
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Alpharetta, US
  • Twitter: @cybleglobal
    16,252 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    233 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 39% Large, 17% Medium

What Do G2 Reviewers Say About Cyble?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the intuitive dashboard and user-friendly UI of Cyble, enhancing their overall experience with the platform.
  • Users value Cyble for its comprehensive threat intelligence, ensuring quick responses and seamless integrations within their security operations.
  • Users value Cyble's state-of-the-art tools for threat hunting, seamlessly combining protection and monitoring in one solution.
  • Users value the real-time insights and ease of use of Cyble for effective cybersecurity management.
  • Users appreciate the real-time threat detection of Cyble, greatly enhancing their digital risk protection and response capabilities.
Cons
  • Users report inefficient alerts with Cyble, experiencing duplicate notifications and unreliable delivery leading to alert fatigue.
  • Users are frustrated with the limited customization options in Cyble, impacting their efficiency and dashboard usability.
  • Users find the poor customer support of Cyble lacking in staff and effective timezone assistance.
  • Users experience poor support management, often facing slow responses that hinder timely resolution of urgent issues.
  • Users experience significant false positives in alerts from Cyble, leading to confusion and inefficient threat management.

What Are Recent G2 Reviews of Cyble?

Check Point Exposure Management

Exposure Management is changing how organizations react to vulnerabilities that put them in risk. Attackers exploit exposed assets, leaked credentials, and misconfigurations within hours using sophisticated AI attack tools. Meanwhile, security teams are left sorting through dashboards, alerts, and disconnected tools. For a limited time only, we are providing an Agentic Exposure Validation Scan at no cost. It delivers proven, evidence-backed findings your team can act on immediately. Request scan here - https://checkpoint.cyberint.com/limited-time-offer-aev-scan Check Point Exposure Management closes that gap by combining billions of external intelligence signals into a Unified Intelligence Fabric. The platform continuously identifies, validates, prioritizes, and safely remediates the exposures attackers are most likely to exploit. With Cyber Asset Attack Surface Management (CAASM), security teams gain a real-time inventory across cloud, SaaS, on-premises infrastructure, endpoints, and identities through 150+ agentless integrations. Unlike traditional vulnerability management, Check Point prioritizes exposures based on real-world exploitability, active threat intelligence, business context, and existing security controls, eliminating duplicate alerts and reducing remediation noise. It does so while maintaining business continuity. Safe-by-design remediation then validates every action before enforcement, enabling capabilities such as virtual patching, IPS activation, configuration hardening, and policy enforcement without disrupting business operations. Organizations using the platform achieve a 93% true positive rate, 12-hour average takedown MTTR, and 504 safe remediations per organization every month. Built around Gartner's Continuous Threat Exposure Management (CTEM) framework, Check Point helps organizations move from visibility to measurable risk reduction. Gartner predicts organizations adopting CTEM with mobilization will experience 50% fewer successful cyberattacks by 2028. Ready to see Exposure Management in action? Get a 15-minute demo: https://l.cyberint.com/exposure-management-demo

Average Rating: 4.6/5.0

Total Reviews: 192

How Do G2 Users Rate Check Point Exposure Management?

  • Security Validation: 8.8/10 (Category avg: 9.0/10)
  • Intelligence Reports: 9.0/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.4/10 (Category avg: 8.7/10)
  • Ease of Use: 9.1/10 (Category avg: 9.1/10)

Who Is the Company Behind Check Point Exposure Management?

Who Uses This Product?

  • Who Uses This: Security Threat Analyst, Cyber Security Analyst
  • Top Industries: Banking, Financial Services
  • Company Size: 67% Large, 21% Medium

What Do G2 Reviewers Say About Check Point Exposure Management?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Check Point Exposure Management, enjoying its intuitive interface for threat detection.
  • Users value the comprehensive threat intelligence from Cyberint, enhancing detection and response to potential threats effectively.
  • Users commend the enhanced threat detection capabilities of Check Point Exposure Management, improving situational awareness and response efficiency.
  • Users value the comprehensive intelligence feeds of Check Point Exposure Management, enhancing threat detection and situational awareness.
  • Users value the responsive and proactive customer support from Cyberint, enhancing their overall threat management experience.
Cons
  • Users face challenges with inefficient alerts due to false positives, complicating the verification process for analysts.
  • Users experience false positives that necessitate additional validation time, complicating the overall alert management process.
  • Users find the inefficient alert system complicates handling excessive alerts and delays threat intel on compromised accounts.
  • Users note integration issues with Check Point Exposure Management, particularly regarding centralizing alerts and connecting security tools.
  • Users note the limited features of Check Point Exposure Management, specifically regarding alert tuning and user account restrictions.

What Are Recent G2 Reviews of Check Point Exposure Management?

What Are G2 Users Discussing About Check Point Exposure Management?

SOCRadar Extended Threat Intelligence

Since 2019, SOCRadar has been a pioneer in SaaS cybersecurity, now serving over 900 customers across 75 countries. Our mission is to provide accessible, proactive threat intelligence. Today, SOCRadar empowers security teams with our groundbreaking Extended Threat Intelligence (XTI) platform and is leading the charge toward the future with Agentic Threat Intelligence (ATI). What does SOCRadar do? At its core, SOCRadar provides a unified, cloud-hosted platform designed to enrich your cyber threat intelligence by contextualizing it with data from your attack surface, digital footprint, dark web exposure, and supply chain. We help security teams see what attackers see by combining External Attack Surface Management, Cyber Threat Intelligence, and Digital Risk Protection into a single, easy-to-use solution. This enables your organization to discover hidden vulnerabilities, detect data leaks, and shut down threats like phishing and brand impersonation before they can harm your business. By combining these critical security functions, SOCRadar replaces the need for separate, disconnected tools. Our holistic approach offers a streamlined, modular experience, providing a complete, real-time view of your threat landscape to help you stay ahead of attackers. Our vision for Agentic Threat Intelligence (ATI) goes beyond today's chatbots and LLMs. We are focused on making it practical for security teams to use AI agents to solve real-world problems. Our initiative will empower you to either deploy pre-built agents or easily create your own, leveraging deep integrations to automate complex tasks that were previously difficult to perform accurately. SOCRadar is dedicated to pioneering this change, making autonomous security an accessible reality for your team.

Average Rating: 4.7/5.0

Total Reviews: 118

How Do G2 Users Rate SOCRadar Extended Threat Intelligence?

  • Security Validation: 8.9/10 (Category avg: 9.0/10)
  • Intelligence Reports: 9.1/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.5/10 (Category avg: 8.7/10)
  • Ease of Use: 9.2/10 (Category avg: 9.1/10)

Who Is the Company Behind SOCRadar Extended Threat Intelligence?

  • Seller: SOCRadar
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Delaware
  • Twitter: @socradar
    5,748 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    195 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 42% Medium, 41% Large

What Do G2 Reviewers Say About SOCRadar Extended Threat Intelligence?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of SOCRadar, enjoying its intuitive dashboards and centralized threat data management.
  • Users value the comprehensive Threat Intelligence features of SOCRadar, enabling effective risk awareness and proactive security measures.
  • Users value the comprehensive and actionable alert notifications from SOCRadar, enhancing their security monitoring and response efforts.
  • Users appreciate the exceptional visibility into external threats, benefiting from a centralized and proactive intelligence platform.
  • Users value the exceptional visibility SOCRadar provides into external threats, enhancing proactive security measures significantly.
Cons
  • Users are frustrated by the inefficient alerts, leading to noise and fatigue from duplicate notifications and false positives.
  • Users report that the inefficient alert system leads to alert fatigue and necessitates extensive tuning for effectiveness.
  • Users struggle with false positives and duplicate notifications, leading to alert fatigue and a need for extensive tuning.
  • Users note the limited features in SOCRadar Extended Threat Intelligence, hindering deeper analysis without upgrading.
  • Users find the insufficient information from SOCRadar Extended Threat Intelligence to hinder effective decision-making.

What Are Recent G2 Reviews of SOCRadar Extended Threat Intelligence?

CTM360

CTM360 is a consolidated external security platform that integrates External Attack Surface Management, Digital Risk Protection, Cyber Threat Intelligence, Brand Protection & Anti-phishing, Surface, Deep, & Dark Web Monitoring, Security Ratings, Third-party risk Management, and fully managed unlimited Takedowns. As a pioneer and innovator in preemptive security, CTM360 operates as an external CTEM technology platform outside an organization’s perimeter. Seamless and turn-key, CTM360 requires no configurations, installations or inputs from the end-user, with all data pre-populated and specific to your organization. All aspects are managed by CTM360.

Average Rating: 4.6/5.0

Total Reviews: 172

How Do G2 Users Rate CTM360?

  • Security Validation: 8.6/10 (Category avg: 9.0/10)
  • Intelligence Reports: 8.7/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.0/10 (Category avg: 8.7/10)
  • Ease of Use: 9.3/10 (Category avg: 9.1/10)

Who Is the Company Behind CTM360?

  • Seller: CTM360
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Manama, BH
  • Twitter: @teamCTM360
    999 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    136 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Banking, Financial Services
  • Company Size: 37% Large, 37% Medium

What Do G2 Reviewers Say About CTM360?

AI-generated summary from verified user reviews

Pros
  • Users commend the top-notch customer support of CTM360, highlighting responsive and knowledgeable assistance at every level.
  • Users commend the ease of use of CTM360, appreciating its straightforward setup and user-friendly interface.
  • Users admire the comprehensive platform of CTM360, which effectively enhances proactive cybersecurity and incident response.
  • Users commend the effective monitoring capabilities of CTM360, aiding quick identification of risks and enhancing security posture.
  • Users praise the high detection efficiency of CTM360, appreciating its accuracy and proactive risk management capabilities.
Cons
  • Users note the limited features of CTM360, particularly on the Android app compared to the web portal.
  • Users are frustrated by the integration issues with existing security infrastructures, seeking better compatibility and usability.
  • Users note a lack of features in CTM360, particularly compared to the web portal and community edition limitations.
  • Users face a lack of integration with existing security systems, limiting automated data feeds and user experience.
  • Users find the lack of integrations with existing security tools limits automated daily security feeds and functionality.

What Are Recent G2 Reviews of CTM360?

Ivanti Neurons for Unified Endpoint Management

Ivanti Neurons for UEM unifies the management and security of every device across the enterprise—Windows, macOS, Linux, mobile, rugged, IoT, and VR/XR headsets—within a single platform. Powered by AI, it automates patching, compliance, onboarding, and remediation, eliminating manual effort while strengthening protection across the entire device estate. With Ivanti Neurons for UEM, organizations gain risk based patching, zero touch onboarding, self healing device capabilities, proactive digital experience optimization, and continuous compliance, all reinforced by automated AI insights that surface issues before they impact productivity. Ivanti Neurons for UEM delivers full visibility across your environment, eliminating blind spots and enabling IT and Security teams to shift from reactive firefighting to strategic action. Its native integrations streamline workflows, enhance cross team alignment, and help strengthen an organization’s overall security posture. The result: organizations reduce risk, scale IT efficiency, and deliver seamless, resilient, and secure digital experiences for every user.

Average Rating: 4.3/5.0

Total Reviews: 384

How Do G2 Users Rate Ivanti Neurons for Unified Endpoint Management?

  • Ease of Use: 8.2/10 (Category avg: 9.1/10)

Who Is the Company Behind Ivanti Neurons for Unified Endpoint Management?

  • Seller: Ivanti
  • Company Website:
  • Year Founded: 1985
  • HQ Location: South Jordan, UT
  • Twitter: @GoIvanti
    6,761 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,026 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 47% Large, 34% Medium

What Do G2 Reviewers Say About Ivanti Neurons for Unified Endpoint Management?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the strong automation features of Ivanti Neurons, making endpoint management seamless and efficient.
  • Users value the strong automation and self-healing features of Ivanti Neurons, enhancing device management and visibility.
  • Users value the strong automation and AI-driven features of Ivanti Neurons, streamlining device management and enhancing productivity.
  • Users find the ease of use of Ivanti Neurons invaluable for seamless management and efficient operations across environments.
  • Users find easy implementation of Ivanti Neurons for Unified Endpoint Management greatly simplifies their management processes.
Cons
  • Users experience poor customer support, with inconsistent response times hampering troubleshooting during critical incidents.
  • Users experience communication delays in support responsiveness, impacting critical troubleshooting during high-priority incidents.
  • Users report feature issues such as a cluttered UI and sluggish performance with large device counts.
  • Users find the steep learning curve challenging, particularly with the setup and the cluttered interface hindering usability.
  • Users face patching issues with inconsistent deployment timelines and sluggish performance during critical updates and management tasks.

What Are Recent G2 Reviews of Ivanti Neurons for Unified Endpoint Management?

What Are G2 Users Discussing About Ivanti Neurons for Unified Endpoint Management?

Netcraft

Netcraft is a type of digital risk protection solution designed to help organizations safeguard their online presence against brand impersonation, phishing, and various cyber threats. This comprehensive platform offers automated detection and takedown services, ensuring that brands can effectively manage their digital reputation and mitigate risks associated with malicious activities on the internet. Targeted primarily at businesses, financial institutions, technology companies, and government agencies, Netcraft's solutions cater to organizations that require robust online protection. The platform is particularly beneficial for those who face the constant threat of brand impersonation, where malicious actors create lookalike domains or fraudulent profiles to deceive customers. By providing a proactive approach to brand protection, Netcraft enables organizations to maintain trust and credibility in their digital interactions. One of the key features of Netcraft is its automated brand impersonation and protection capabilities. This includes the rapid identification and removal of lookalike domains, fake social media profiles, and fraudulent mobile applications. The platform's phishing and fraud disruption services offer swift takedown of phishing sites and related infrastructure, significantly reducing the window of opportunity for cybercriminals. Additionally, Netcraft provides real-time cybercrime intelligence, delivering machine-readable threat data that integrates seamlessly into Security Operations Center (SOC) and Security Information and Event Management (SIEM) systems. The impact of Netcraft's solutions is evident in its market-leading performance. The platform is responsible for nearly one-third of the world's phishing takedowns, demonstrating its effectiveness in combating cyber threats. With a median phishing takedown time of just 33 minutes, Netcraft ensures that threats are neutralized quickly, preventing potential harm to organizations and their customers. Furthermore, the platform processes over 23 billion data points annually, allowing it to uncover and validate threats with remarkable speed and accuracy. Netcraft's global network effect enhances its value proposition, as its threat intelligence feeds are licensed by major browsers and antivirus companies, thereby protecting billions of users worldwide. This extensive reach not only reinforces the platform's credibility but also contributes to a safer online environment for all. By leveraging decades of internet infrastructure expertise and advanced artificial intelligence, Netcraft stands out as a leader in brand protection and digital risk management, providing organizations with the tools they need to navigate the complexities of the online threat landscape.

Average Rating: 4.6/5.0

Total Reviews: 49

How Do G2 Users Rate Netcraft?

  • Security Validation: 7.8/10 (Category avg: 9.0/10)
  • Intelligence Reports: 8.0/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 7.9/10 (Category avg: 8.7/10)
  • Ease of Use: 9.0/10 (Category avg: 9.1/10)

Who Is the Company Behind Netcraft?

  • Seller: Netcraft
  • Company Website:
  • Year Founded: 1994
  • HQ Location: London, England, United Kingdom
  • Twitter: @Netcraft
    4,472 Twitter followers
  • LinkedIn® Page: linkedin.com
    299 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services, Banking
  • Company Size: 69% Large, 16% Medium

What Do G2 Reviewers Say About Netcraft?

AI-generated summary from verified user reviews

Pros
  • Users praise the ease of use of Netcraft, enjoying its intuitive dashboard and seamless integration with other tools.
  • Users value the timely alerts from Netcraft, enhancing security and helping to protect against phishing attacks.
  • Users value the accuracy of information from Netcraft, ensuring reliable and timely threat detection and takedowns.
  • Users find the automation features of Netcraft invaluable, simplifying their workflow and enhancing operational efficiency.
  • Users value the effective security protection provided by Netcraft against online threats, enhancing brand safety significantly.
Cons
  • Users find the complexity of the interface challenging, making navigation and customization difficult and overwhelming.
  • Users find Netcraft's pricing to be expensive and confusing, complicating budget decisions and service selection.
  • Users find a lack of customization in Netcraft, making specific report requirements and security prioritization challenging.
  • Users find poor reporting in Netcraft limiting due to complexity and lack of essential features for analysis.
  • Users experience false positives, where some valid pages are not recognized, leading to frustration and confusion.

What Are Recent G2 Reviews of Netcraft?

Group-IB Threat Intelligence

The first line of defense shouldn’t be your infrastructure; optimize your security and defeat attacks before they begin with knowledge of who, how, and when you will be attacked. Group-IB’s Threat Intelligence provides unparalleled insight into your adversaries and maximizes the performance of every component of your security ecosystem. Equip your team with it to strengthen your security with the strategic, operational and tactical intelligence. Understand threat trends and anticipate specific attacks with thorough knowledge of your threat landscape. Group-IB provides precise, tailored and reliable information for data-driven strategic decisions. - Revolutionize risk management with tailored on-demand, and regular monthly and quarterly threat reports written by analysts specifically for the board and executives - Enable growth with actionable threat intelligence before expanding into a new region/business line, and get industry-specific threats before digital transformation - Lower the cost of cyber security by avoiding unnecessary purchases and postponing upgrades by maximizing the efficacy of your existing security investments Strengthen defenses with detailed insight into attacker behaviors and infrastructure. Group-IB delivers the most comprehensive insight into past, present and future attacks targeting your organization, industry, partners and clients. - Transform security and adapt instantly, use the insights to block malicious network and endpoint activity the moment it is first observed anywhere in the world - Identify and remove weaknesses before they are exploited by arming your Red Team with detailed knowledge of threat actor’s tools, tactics and processes - Automate workflows and improve team efficiency by enriching your SIEM, SOAR, EDR and vulnerability management platforms with out-of-the-box API integrations supporting TAXII and STIX Identify attacks faster and reduce response time with comprehensive visibility of the stages of attack used by threat actors. Group-IB gives your teams the best possible insight into the methods used by adversaries. - Prioritize vulnerability patching for your technology stack with automated alerts that inform you the moment vulnerabilities are discovered or exploited by threat actors targeting your industry - Eliminate false positive alerts and focus on legitimately risky events with a database of indicators of compromise for cybercriminals in your threat landscape - Reduce response time and quickly remove attackers from your network with knowledge of the cyber kill chain used by threat actors in the MITRE ATT&CK matrix format

Average Rating: 4.7/5.0

Total Reviews: 29

How Do G2 Users Rate Group-IB Threat Intelligence?

  • Security Validation: 8.8/10 (Category avg: 9.0/10)
  • Intelligence Reports: 9.0/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.7/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind Group-IB Threat Intelligence?

  • Seller: Group-IB
  • Company Website:
  • Year Founded: 2003
  • HQ Location: Singapore
  • Twitter: @GroupIB
    9,646 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    572 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Banking, Financial Services
  • Company Size: 59% Large, 21% Medium

What Do G2 Reviewers Say About Group-IB Threat Intelligence?

AI-generated summary from verified user reviews

Pros
  • Users value the automation for early detection of compromised accounts, enhancing organizational security significantly.
  • Users value the early detection capabilities of Group-IB Threat Intelligence for compromised accounts and detailed insights.
  • Users value the ease of use of Group-IB Threat Intelligence, finding it straightforward and feature-rich for their needs.
  • Users value the strong local support and appreciate the easy-to-use features provided by Group-IB Threat Intelligence.
  • Users value the tailored threat intelligence provided by Group-IB, enhancing their ability to analyze information efficiently.
Cons
  • Users find the subscription price of Group-IB Threat Intelligence to be expensive, though they acknowledge its value for investment.

What Are Recent G2 Reviews of Group-IB Threat Intelligence?

What Are G2 Users Discussing About Group-IB Threat Intelligence?

Cisco Talos

Cisco Talos is a threat intelligence organization dedicated to providing protection before, during, and after cybersecurity attacks.

Average Rating: 4.4/5.0

Total Reviews: 38

How Do G2 Users Rate Cisco Talos?

  • Security Validation: 9.2/10 (Category avg: 9.0/10)
  • Intelligence Reports: 9.1/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind Cisco Talos?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • Twitter: @Cisco
    720,366 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 42% Medium, 33% Large

What Do G2 Reviewers Say About Cisco Talos?

AI-generated summary from verified user reviews

Pros
  • Users value the strong threat intelligence of Cisco Talos, enhancing security decisions with real-time updates and accurate detections.
  • Users value the accuracy of information provided by Cisco Talos, enhancing their understanding of global security threats.
  • Users value the vast visibility and real-time intelligence of Cisco Talos, enhancing their overall security posture.
  • Users value the reliable and timely threat intelligence from Cisco Talos, aiding informed security decisions and understanding trends.
  • Users value the reliable and timely threat intelligence from Cisco Talos, enhancing confidence in security-related decisions.
Cons
  • Users find the interface complex for new users, along with limited customization and reporting for non-Cisco tools.
  • Users find integration issues with Cisco Talos, particularly in mixed environments, can limit its effectiveness and flexibility.
  • Users find a lack of customization in Cisco Talos, making it challenging, particularly for those using non-Cisco tools.
  • Users face poor reporting and limited customization, making it hard for new users to navigate efficiently.
  • Users find the time-consuming nature of Cisco Talos' technical details challenging to fully comprehend.

What Are Recent G2 Reviews of Cisco Talos?

What Are G2 Users Discussing About Cisco Talos?

OpenCTI by Filigran

OpenCTI is an open-source threat intelligence platform designed to help users manage and operationalize threat intelligence effectively. Built by practitioners for practitioners, OpenCTI aims to break down data silos and ensure that threat intelligence is not only accessible but also actionable. This platform facilitates the seamless flow of threat intelligence across various security systems, making it relevant by integrating business context and enabling the creation of comprehensive threat exposure reports for enhanced executive visibility. The target audience for OpenCTI includes cybersecurity professionals, threat analysts, and organizations looking to improve their threat intelligence capabilities. By providing a centralized platform for threat data, OpenCTI allows users to visualize, link, and enrich threat intelligence, fostering collaboration among teams and enhancing the overall security posture of an organization. The platform is particularly beneficial for organizations that need to streamline their threat intelligence processes and ensure that critical information is readily available to decision-makers. Key features of OpenCTI include its unified and consistent data model based on the Structured Threat Information Expression (STIX) standard. This allows users to integrate diverse threat data sources into a single framework, making it easier to analyze and respond to threats. The platform supports various data formats and can ingest information from multiple feeds, enabling users to maintain a comprehensive view of the threat landscape. Additionally, OpenCTI offers advanced visualization tools that help users identify patterns and relationships within the data, facilitating more informed decision-making. Moreover, OpenCTI enhances the operationalization of threat intelligence by providing users with the tools to enrich their data with contextual information. This capability allows organizations to tailor their threat intelligence to their specific business needs, ensuring that the information is not only relevant but also actionable. By generating detailed threat exposure reports, OpenCTI empowers executives with the insights needed to understand their organization's risk landscape and make informed strategic decisions regarding cybersecurity investments and initiatives. Overall, OpenCTI stands out in the realm of threat intelligence platforms by prioritizing collaboration, accessibility, and contextual relevance. Its open-source nature encourages community involvement and continuous improvement, making it a valuable resource for organizations seeking to enhance their threat intelligence capabilities and strengthen their cybersecurity defenses.

Average Rating: 4.6/5.0

Total Reviews: 47

How Do G2 Users Rate OpenCTI by Filigran?

  • Intelligence Reports: 9.0/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.1/10 (Category avg: 8.7/10)
  • Ease of Use: 8.0/10 (Category avg: 9.1/10)

Who Is the Company Behind OpenCTI by Filigran?

  • Seller: Filigran
  • Company Website:
  • Year Founded: 2022
  • HQ Location: New York, US
  • Twitter: @FiligranHQ
    841 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    270 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 57% Large, 28% Medium

What Do G2 Reviewers Say About OpenCTI by Filigran?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of OpenCTI, enabling efficient threat analysis and integration without administration hassles.
  • Users value the powerful automation and flexibility of OpenCTI, enhancing teamwork and streamlining threat analysis.
  • Users commend the excellent customer support of OpenCTI, praising their eagerness to assist and provide guidance.
  • Users value the great bi-directional integrations in OpenCTI, enhancing their ability to link diverse data sources.
  • Users value the great bi-directional integration capabilities of OpenCTI, enhancing their threat intelligence and response workflows.
Cons
  • Users find the graphing functionality and dashboards limited, wishing for more flexibility and customization options.
  • Users find the complexity of dashboards and workflows challenging, affecting effective use and leading to frustration.
  • Users experience poor customer support with slow improvements and inadequate documentation, impacting overall satisfaction with OpenCTI.
  • Users express concern over poor documentation, finding it difficult to connect resources and use features effectively.
  • Users find the dashboard issues frustrating due to limitations in outputs and display options, despite potential improvements.

What Are Recent G2 Reviews of OpenCTI by Filigran?

Flashpoint

Flashpoint is the largest privately held threat intelligence provider, enabling mission-critical organizations to proactively confront security challenges globally. Flashpoint Ignite, our unified threat intelligence platform, harnesses the power of primary-source collections, curated human insight, and artificial intelligence to deliver decisive action against a comprehensive range of critical threats. Core Capabilities: → Identify and remediate cyber threats, fraud, vulnerabilities, physical security, and national security risks. → Access over 3.6 petabytes of continuously collected data from the internet’s open and difficult-to-access spaces. Add new channels and data sources in minutes to track sources as they surface. → Operationalize intelligence across your entire security stack with seamless integrations throughout the intelligence lifecycle.

Average Rating: 4.5/5.0

Total Reviews: 83

How Do G2 Users Rate Flashpoint?

  • Security Validation: 7.1/10 (Category avg: 9.0/10)
  • Intelligence Reports: 8.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 7.0/10 (Category avg: 8.7/10)
  • Ease of Use: 8.4/10 (Category avg: 9.1/10)

Who Is the Company Behind Flashpoint?

Who Uses This Product?

  • Top Industries: Financial Services, Security and Investigations
  • Company Size: 63% Large, 23% Small

What Do G2 Reviewers Say About Flashpoint?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Flashpoint, highlighting its intuitive navigation and quick deployment for teams.
  • Users appreciate the raw, actionable threat actor visibility provided by Flashpoint, enhancing proactive fraud detection.
  • Users appreciate the impressive quality of data and advanced filtering options that enhance their research experience.
  • Users appreciate the extensive data collection of Flashpoint, benefiting from streamlined searches and rich actionable insights.
  • Users value Flashpoint's efficient search functionality, enabling easy access to relevant data from various channels.
Cons
  • Users express frustration over the lack of features in Flashpoint, impacting efficiency and integration capabilities.
  • Users find the complexity of the query system in Flashpoint makes navigation and alert customization challenging.
  • The confusing interface of Flashpoint can hinder user experience, especially with navigation and alert management.
  • Users find some features limited and under-developed, especially in investigation and customization options.
  • Users experience frustration with Flashpoint due to confusing queries and noisy alerts that complicate their workflow.

What Are Recent G2 Reviews of Flashpoint?

What Are G2 Users Discussing About Flashpoint?

Lookout

Lookout is a mobile app that fights cybercriminals by predicting and stopping mobile attacks before they do harm.

Average Rating: 4.3/5.0

Total Reviews: 67

How Do G2 Users Rate Lookout?

  • Security Validation: 8.8/10 (Category avg: 9.0/10)
  • Intelligence Reports: 9.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.6/10 (Category avg: 8.7/10)
  • Ease of Use: 8.8/10 (Category avg: 9.1/10)

Who Is the Company Behind Lookout?

  • Seller: Lookout
  • Year Founded: 2007
  • HQ Location: San Francisco, CA
  • Twitter: @Lookout
    44,263 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    512 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 43% Small, 41% Large

What Do G2 Reviewers Say About Lookout?

AI-generated summary from verified user reviews

Pros
  • Users love the ease of use of Lookout, finding it user-friendly and efficient for monitoring their devices.
  • Users love the complete security Lookout provides for online privacy, data security, and device protection.
  • Users love the user-friendly safety features of Lookout, appreciating the compact app and comprehensive management view.
  • Users love Lookout for its complete online security, providing end-to-end protection for privacy and devices.
  • Users appreciate the management ease of Lookout, finding the management view covers all cybersecurity needs efficiently.
Cons
  • Users are disappointed by the limited features of Lookout, requiring additional apps for essential functions and security.
  • Users experience update issues due to frequent requirements and unwanted automatic installations on their devices.
  • Users experience alert issues due to insufficient reporting, leaving them without site-specific information after alerts are generated.
  • Users find the configuration complexity time-consuming and frustrating due to unwanted automatic installations on devices.
  • Users often face deployment issues due to frequent updates, and suggest improvements for the app design.

What Are Recent G2 Reviews of Lookout?

What Are G2 Users Discussing About Lookout?