Best Threat Intelligence Services Providers - Page 3

How Many Threat Intelligence Services Providers Products Does G2 Track?

Total Products under this Category: 82

Category Stats (Sep 2026)

  • Average Rating: 4.41/5 The average rating of products in this category, based on all submitted ratings

Last updated: September 12, 2026

How Does G2 Rank Threat Intelligence Services Providers Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 200+ Authentic Reviews
  • 82+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

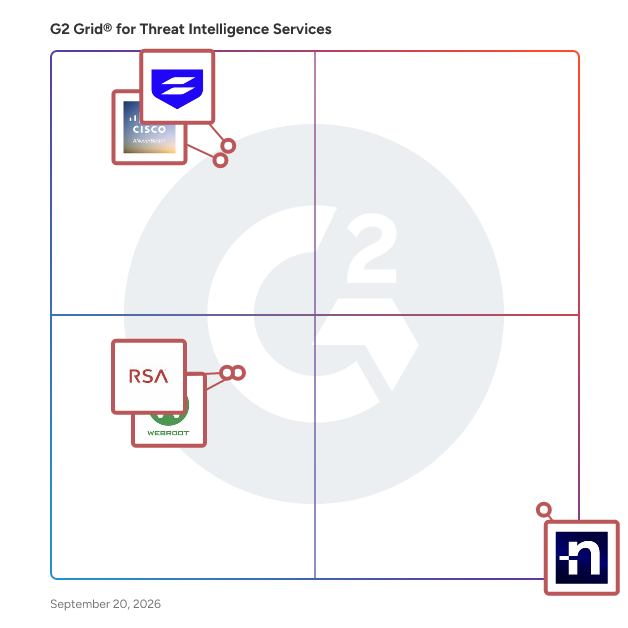
G2 Grid® for Threat Intelligence Services Providers

G2 Grid® for Threat Intelligence Services Providers plotting products by satisfaction and market presence

Highlighted products: Sophos Professional Services, Cisco Security Services, Nomic Networks, Webroot Threat Intelligence, and RSA Services.

Underlying data: [Grid® JSON](https://www.g2.com/categories/threat-intelligence-services/grids.json?focus%5B%5D=sophos-professional-services&focus%5B%5D=cisco-security-services&focus%5B%5D=nomic-networks&focus%5B%5D=webroot-threat-intelligence&focus%5B%5D=rsa-services)

CIPHER

At Cipher, a Prosegur company, we are a leading Managed Security Services (MSS) provider, renowned for our world-class Managed Detection and Response (xMDR) service. We meet you where you are with flexible and open support for your technology needs, providing localized expertise and global reach. In addition to xMDR, we offer professional services that encompass installation, deployment, integration, optimization, and seamless transition to Business as Usual (BAU) operations. Cipher’s world class penetration testing services are recognized in the marketplace for our specialized ability to integrate penetration testing, red teaming, and purple teaming exercises into Security Operations. Cipher’s Governance, Risk and Compliance (GRC) services address the ever changing and increasingly complex landscape encountered by our customers. We facilitate true end-to-end lifecycle services including technology procurement, management, and maintenance of your tech stack, ensuring a streamlined process. Our end-to-end MSS solutions cater to all your cybersecurity needs and our comprehensive approach ensures that we meet the diverse security requirements of our clients, maintaining excellence in all aspects of cybersecurity.

Who Is the Company Behind CIPHER?

  • Seller: Cipher
  • HQ Location: Miami, Florida, United States
  • LinkedIn® Page: www.linkedin.com
    354 employees on LinkedIn®

Claritas Intelligence

Claritas Intelligence exists to transform complex market dynamics into actionable strategic intelligence — enabling leaders to see around corners, anticipate disruption, and seize opportunities with confidence.

Who Is the Company Behind Claritas Intelligence?

Cloud4C Services

Cloud4C, named a Visionary in the 2021 Gartner Magic Quadrant for Public Cloud IT Transformation Services is the world’s leading automation-driven, application-focused Cloud Managed Services Provider (MSP). As one of the global leaders in multi-cloud migration and managed services, we support native and hybrid cloud environments with multi-availability zones, offering four-way disaster recovery architecture at zero data loss guarantee, military-grade security under a single SLA. Whatever cloud solution an enterprise is looking for, we can deploy it in their existing operational landscape – and transform the way they work. Cloud4C’s managed service processes adhere to best industry standards such as ITIL and COBIT using our proprietary Self-Healing Operations Platform (SHOP), an automation platform driving industry-leading services delivered through multiple products, garnering the best NPS scores from clients. We command presence across 25 countries in the Americas, Europe, Middle East, Africa, and APAC and serve 4000+ global enterprises. These enterprises include 60 Fortune 500 companies and 80+ enterprises with over $1Bn revenue. Cloud4C is a pioneer in offering advanced IT evolution solutions with a Collaborative Integration delivery Model - A perfect collaborative alliance of people, systems, business structures, and practices customized to optimize results, increase value delivered to you, reduce waste, and maximize efficiency through all phases of plan, design, development, and management. We engage through an award-winning Hybrid Managed Services approach that pools in resources on-demand from 25 Centers of Excellence based on a firm’s needs and objectives, walking all the way through from transformation strategy blueprinting, deployment, management, support, and end business outcome delivery. As certified Azure, GCP, AWS, and Oracle Cloud partners, Cloud4C promises seamless, cost-effective digital transformation on public/private/hybrid/multi-cloud set-ups

Who Is the Company Behind Cloud4C Services?

  • Seller: Cloud4C Services
  • HQ Location: Singapore, SG
  • Twitter: @Cloud4Cservices
    420 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,518 employees on LinkedIn®

Cupid Fraud

Romance scammers create fake profiles on dating sites and apps or contact you through popular social media sites.

Who Is the Company Behind Cupid Fraud?

cybernality

We, addoptIO GmbH, are a start-up company from Germany founded in 2021. We make the world a better place by helping individuals, companies and organizations overcome cybersecurity challenges. Speed is an important key to success in order to avoid offering attackers unnecessary targets. That’s why we built cybernality.com. We provide RELEVANT information on cyber defense exactly when it is NECESSARY for you. cybernality is a 360° cybersecurity information service that provides you with topics tailored exclusively to your needs in the quickest and easiest way. Comprehensive cybersecurity search index as a central information hub: We scour the internet for you for the latest cybersecurity information, normalize the data into a standardized format, enrich the data with additional context and make it available in a search index. With the help of professional search options, you can find the right information quickly and easily. Automatic notifications always keep you up to date: Whether you want to be informed about new vulnerabilities in certain products or follow the activities of an APT group, with cybernality you will never miss any relevant news. Automated searches, so-called feeds, keep an eye on our extensive cybersecurity database for you and send you every new result that matches your feed. You can either receive these notifications by email or connect any third-party software, such as ITSM tools, SOAR solutions, vulnerability management systems, etc. via API endpoint. Extensive filters put an end to information overload: In 2022, over 25,000 new vulnerabilities (CVEs) were listed in the National Vulnerability Database (NVD), and the trend is rising. In addition, there are daily reports of successful hacker attacks and activities by advanced persistent threat (APT) groups. Countless sources on the Internet contain important information on cybersecurity topics. All this makes finding information like looking for a needle in a haystack. cybernality offers extensive filters to make your searches as specific as possible. Enriched context makes you 100% effective: Information must be placed in a larger context in order to gain meaning. That is why all entries in our search index are provided with a context that enables you to quickly grasp the meaning of the information, understand the context and find the information quickly. Context means that we classify search results into, for example, security advisories, threat information, hacking attacks, etc. We provide MITRE Att&ck TTPs (Tactics, Techniques, Procedures) that match the vulnerabilities and attacks mentioned, for example. We list the named product details (name, version, platform, CPE string etc.) and manufacturer as well as authors and security researchers. We provide NVD and manufacturer severity information and much more. Central account management for comprehensive teamwork: Successful cybersecurity work is based on effective teamwork. cybernality was designed from the outset to enable heterogeneous and distributed teams to use the platform together. This means you can, for example, manage the various team members and settings centrally, share feeds within the team or send individual feeds to different recipients. Users with admin rights maintain an overview and manage all central settings. Multi-client capability for sophisticated account management: In more complex organizations or for use cases with external end customers, the use of different clients via a central dashboard can be an important function. cybernality allows you to create several “Payment Accounts”, whereby each “Payment Account” can contain any number of subscriptions. The cybernality users are assigned to individual subscriptions by central administrators and remain exclusively within the scope of the respective subscription. It is also possible for a user to be assigned several subscriptions at the same time. This gives you maximum flexibility in structuring your accounts and you can, for example, map group structures with your own cost center management or offer cybernality as a managed service for external customers. In addition, a strict distinction is always made between personal subscriptions and company subscriptions. This means that every user can use cybernality for both private and business purposes independently of each other. Single sign-on for maximum security and user-friendliness: As a cybersecurity startup, we also have high IT security standards for our service. That’s why we only allow third-party identity providers, such as Google or Microsoft, to be used for authentication at cybernality. This not only increases security, but also brings more convenience for you as a user, because you can register with cybernality using your company account or your private Google account, for example. It couldn’t be quicker or easier!

Who Is the Company Behind cybernality?

  • Seller: addoptIO
  • Year Founded: 2021
  • HQ Location: Kressbronn, DE
  • LinkedIn® Page: www.linkedin.com
    4 employees on LinkedIn®
Cybersecurity Fact Checker

Cybersecurity Fact Checker is a specialized tool designed to validate and verify cybersecurity claims, news, and content. It helps ensure the accuracy and reliability of information by cross-referencing credible sources, analyzing data, and flagging inaccuracies. This tool empowers professionals, writers, and businesses to create trusted content, avoid misinformation, and build authority in the cybersecurity domain.

Who Is the Company Behind Cybersecurity Fact Checker?

  • Seller: Gracker AI
  • Year Founded: 2025
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    16 employees on LinkedIn®

Cyberseer

Cyberseer offers Advanced Threat Detection and a 24×7 Managed Security Service (MSS). We fuse both machine learning and behavioural analytics from industry-leading vendor technologies with Cyberseer’s automation and contextualisation platform to equip analysts with a prioritised view of potential threats that an organisation will face. All threats are reviewed and managed to closure by Cyberseer in collaboration with the customer. For more information on our Advanced Threat Detection Solutions & Managed Security Services, then please visit - https://www.cyberseer.net/

Who Is the Company Behind Cyberseer?

Cyren Threat InDepth

Cyren’s unique and fresh threat intelligence is gathered by analyzing, processing, and correlating billions of daily transactions across email content, suspicious files, and web traffic to provide timely and accurate insights.

Who Is the Company Behind Cyren Threat InDepth?

  • Seller: Cyren
  • Year Founded: 1991
  • HQ Location: Research Triangle Park, US
  • Twitter: @CYRENInc
    2,278 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    40 employees on LinkedIn®
  • Ownership: NASDAQ: CYRN

Digital Asset Redemption

Digital Asset Redemption uses undercover, forward-deployed intelligence, negotiations expertise, and compliant payment options to combat and disrupt the cybercrime economy. The DRK_MDR suite is composed of three products: Operative: Managed detection and response platform for the dark web. Our operatives have infiltrated the inner circles of the cyber criminal ecosystem, giving you the power to detect and respond to threats where they start. Engage: A ransomware readiness and recovery ally who will engage threat actors, understand who the threat actors are, and, when necessary, provide compliant payments, all ready to deploy at a moment’s notice. Cybercrime Preparedness: The total package of managed dark web monitoring and response as well as ransomware response readiness with negotiation and payment services. Platform and Service Detailed Description DRK_MDR is a managed suite of monitoring and response services that extend protections into the dark web. This means both proactively monitoring and responding to emerging threats in the far reaches of the dark web as well as having ransomware negotiation and compliant payment solutions ready to deploy in the event of an extortion incident.

Who Is the Company Behind Digital Asset Redemption?

EMDYN Threat Intelligence

EMDYN Threat Intelligence is a comprehensive solution designed to transform complex data into actionable insights, enabling organizations to effectively identify, assess, and mitigate potential threats. By integrating advanced analytics and real-time data processing, EMDYN empowers decision-makers to safeguard critical assets and enhance operational security. Key Features and Functionality: - Data Integration: Aggregates information from diverse digital sources to provide a holistic view of potential threats. - Advanced Analytics: Utilizes sophisticated algorithms to analyze data patterns, identifying anomalies and potential risks. - Real-Time Monitoring: Offers continuous surveillance of digital environments, ensuring timely detection of emerging threats. - Customizable Alerts: Delivers tailored notifications to relevant stakeholders, facilitating prompt response to identified risks. - User-Friendly Interface: Provides an intuitive platform for users to access and interpret intelligence reports efficiently. Primary Value and Problem Solved: EMDYN Threat Intelligence addresses the critical need for organizations to proactively manage and neutralize security threats. By converting vast amounts of data into clear, actionable intelligence, it enables businesses to make informed decisions, protect vital assets, and maintain operational continuity in an increasingly complex digital landscape.

Who Is the Company Behind EMDYN Threat Intelligence?

  • Seller: EMDYN
  • Year Founded: 2008
  • HQ Location: Rotkreuz, CH
  • Twitter: @_emdyn
    3,052 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    8 employees on LinkedIn®

ESET Threat Intelligence Services

THREAT INTELLIGENCE FROM ESET’S WORLD-RENOWNED EXPERTS. GET A UNIQUE PERSPECTIVE ON THE THREAT LANDSCAPE AND IMPROVE YOUR CYBERSECURITY POSTURE. GET UNIQUE INSIGHTS from a unique range of sources and the unparalleled in-the-field experience that helps you fight increasingly sophisticated cybersecurity attacks. STAY AHEAD OF ADVERSARIES. ESET monitors APT groups – with a focus on the activities of Russian, Chinese, North Korean, and Iranian actors, and the TTPs they use to target Western organizations – in order to help you understand their motives. MAKE CRUCIAL DECISIONS, FASTER. Anticipate threats and make faster, better decisions thanks to comprehensive ESET reports and curated feeds. Reduce your exposure to prevailing threats, forewarned by experts. IMPROVE YOUR SECURITY POSTURE. Informed by ESET intelligence feeds, enhance your threat hunting and remediation capabilities, block APTs and ransomware, and improve your cybersecurity architecture. AUTOMATE THREAT INVESTIGATION. ESET technology searches for threats constantly, across multiple layers, from pre-boot to resting state. Benefit from telemetry in all countries where ESET detects emerging threats. ACCESS UNPARALLELED EXPERTISE. ESET has invested in building the world’s leading cybersecurity team, and 11 R&D centers worldwide. We use machine learning to help automate decisions, but our people stand behind threat evaluation.

Who Is the Company Behind ESET Threat Intelligence Services?

  • Seller: ESET
  • Year Founded: 1992
  • HQ Location: Bratislava, Slovak Republic
  • Twitter: @ESET
    275,702 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,014 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Large, 50% Medium

Experian Partner Solutions

Experian Partner Solutions offers a comprehensive and growing suite of financial wellness and identity protection products that help businesses drive customer engagement and retention. The suite includes: -Credit monitoring and alerts -Credit scores and reports -Identity monitoring and alerts (including dark web monitoring) -Digital privacy tools -Financial management tools -Identity restoration We work with you to deliver the experience you envision in less time via multiple deployment options: APIs, embeddable experiences, and fully hosted solutions. Our team partners with you to continually improve your customers’ experience to ultimately scale and achieve your business objectives. Learn more about how we can partner with you to stand out from the crowd with innovative value-added services at experian.com/partner-solutions.

Who Is the Company Behind Experian Partner Solutions?

  • Seller: Experian
  • Year Founded: 1826
  • HQ Location: Dublin, Ireland
  • Twitter: @Experian_US
    38,771 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    26,648 employees on LinkedIn®
  • Ownership: LSE: EXPNL

Exponential-e

Innovation is at the core of Exponential-e, and has been since our inception in 2002. We wholly own our superfast Network, and our fusion of complementary technologies - a carrier-class Network and Cloud infrastructure - means we can deliver enterprise applications at wire speed for a superior end-user experience. Technology is the beating heart of your business, and is undoubtedly fuelling your growth and sustaining your competitive advantage. What you don’t need is the complexity that comes with multiple service providers and varying service levels. At Exponential-e, we strive to constantly exceed expectations in innovation and service; what’s more we can provide a single end-to-end SLA. At Exponential-e, our Cloud services do not transcend the public Internet. Instead, they reside on a customer's LAN, on the clean side of the firewall, so security and privacy concerns are negated. Our vast product portfolio enables us to create tailored solutions for each individual customer, ensuring that we meet their exact needs and requirements – whether that be for Data Centre, Cloud, Unified Communications, Security, or IT Services. Exponential-e has been awarded 9 ISO accreditations and is supported by a UK based 24 / 7 x 365 service desk.

Who Is the Company Behind Exponential-e?

  • Seller: Exponential-e
  • Year Founded: 2002
  • HQ Location: London, England, United Kingdom
  • Twitter: @Exponential_e
    2,823 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    691 employees on LinkedIn®

Five Years Out

Things Evolved is our perspective on the possibilities and future of IoT. Arrow eVolve is our Offering. It's the way we connect customers to those possibilities.

Who Is the Company Behind Five Years Out?

  • Seller: Arrow Electronics
  • Year Founded: 1935
  • HQ Location: Centennial, US
  • Twitter: @Arrow_dot_com
    5,002 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    21,346 employees on LinkedIn®
  • Ownership: NYSE: ARW

goMISP

The service goMISP provides cloud-based, ready-to-use MISP instances, fully managed and continuously updated, so you can focus on staying ahead of cyber threats and not worry about the operation and security of the platform. With goMISP, you get all the benefits of MISP - without the operational burden! In addition to the goMISP managed service, our on-demand Professional Services include expert support for integrating MISP with your existing security stack, as well as tailored configurations, custom automations, and strategic advisory to help you maximize the value of your threat intelligence program. For more information visit www.gomisp.com

Who Is the Company Behind goMISP?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024