Best Software Composition Analysis Tools - Page 5

How Many Software Composition Analysis Tools Products Does G2 Track?

Total Products under this Category: 79

Category Stats (Nov 2026)

  • Average Rating: 4.48/5 (↓0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: DigiCert ONE (+0.99%) - Among all products in this category, DigiCert ONE recorded the largest rating increase compared to last month

Last updated: November 02, 2026

How Does G2 Rank Software Composition Analysis Tools Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,800+ Authentic Reviews
  • 79+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

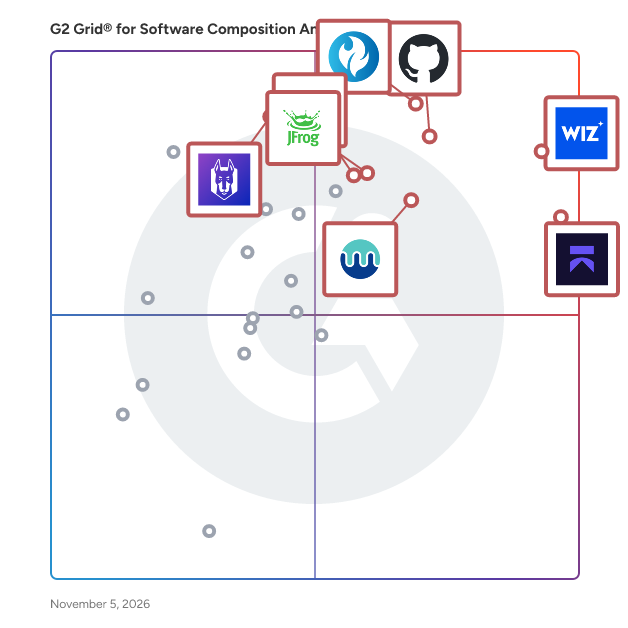
G2 Grid® for Software Composition Analysis Tools

G2 Grid® for Software Composition Analysis Tools plotting products by satisfaction and market presence

Highlighted products: Wiz, Aikido Security, HCL AppScan, GitHub, Mend.io, JFrog, DigiCert ONE, and Snyk.

Underlying data: [Grid® JSON](https://www.g2.com/categories/software-composition-analysis/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=aikido-security&focus%5B%5D=hcl-appscan&focus%5B%5D=github&focus%5B%5D=mend-io&focus%5B%5D=jfrog-2024-03-28&focus%5B%5D=digicert-one&focus%5B%5D=snyk)

DepWarden

DepWarden is a free, anonymous software composition analysis (SCA) and static application security testing (SAST) platform that runs in the browser with no account. SCA: scans manifests, lockfiles, SBOMs and JARs across 11 ecosystems (npm, PyPI, Maven, Gradle, Go, Cargo, Composer, RubyGems, NuGet, Dart, Swift) against live OSV, CISA KEV and EPSS data. It also flags typosquatting, maintainer changes, install scripts and abandoned packages. SAST: pattern and taint analysis across 14 languages with 300+ rules, plus secret scanning and IaC checks for Dockerfiles, Terraform, GitHub Actions and Kubernetes. Findings are ranked by real-world exploitability (KEV, EPSS, fix availability) with compatibility-aware upgrade guidance. Export CycloneDX SBOMs with VEX; the CLI, Maven plugin and CI integrations can gate builds. Sessions are isolated and purged after 30 days.

Who Is the Company Behind DepWarden?

DigiCert Software Trust Manager

Software Trust Manager code signing solution combines centralized governance of key and certificate management, granular team- and role-based access control, malware and vulnerability scanning, and SBOM management to create a policy-driven approach to securely signing, releasing and maintaining software.

Who Is the Company Behind DigiCert Software Trust Manager?

  • Seller: DigiCert
  • Year Founded: 2003
  • HQ Location: Lehi, UT
  • Twitter: @digicert
    6,675 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,957 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

Eracent SBOM-HQ

SBOM-HQ™ - from Eracent SBOM-HQ™ provides a well-rounded set of data, reporting and analysis features that help organizations minimize risks and comply with cyber mandates and directives. While SBOM-HQ™ provides value to in-house and commercial application development teams, it is also unique in its approach to meeting the requirements of organizations that purchase or subscribe to software from numerous publishers. These “software consumers” will have to manage dozens, hundreds, or even thousands of SBOMs for products that they use, and this is impractical or impossible to do one SBOM at a time. SBOM-HQ™ is based around a centralized, single-source repository of libraries, components, and other related data from SBOMs. It dramatically reduces response time when a vulnerability is reported since it eliminates the need to review SBOMs individually. How does SBOM-HQ™ work? Customers upload their SBOM files via the user interface. During this straightforward process, users can assign related information that can be used to support reporting, filters, data access, and more. This information includes Publisher, Line of Business, Application Component, and more. SBOM-HQ™ “deconstructs” each uploaded SBOM and records the software product to which the SBOM belongs and all the SBOM’s content. This results in an index of components and libraries mapped to products. If a vulnerability is reported by NIST or another organization, customers get an immediate report of every product in use in their organization that includes the affected component or library. SBOM-HQ™ is continuously monitored and updated, and it leverages vulnerability data from NIST and other trusted global sources. It uses this data to display risk scores, levels of criticality, and more. SBOM-HQ™ also provides visibility into license types for each component and library, reducing the risk of unknowingly using a library that has excessive restrictions when less risky options are available. The system offers version tracking – the version in use, newer available versions, and version history – as well as lifecycle dates that support obsolescence management. The dedicated open source library within Eracent’s IT-Pedia® product data library provides a solid foundation for SBOM-HQ™’s analysis and reporting. Who can benefit from using SBOM-HQ? SBOM-HQ is designed to support all teams engaged in the use and operation of software. DevOps – SBOM-HQ integrates into CI/CD to generate and enrich SBOMs with real time risk data, ensuring secure and compliant releases. Procurement – SBOM-HQ equips procurement teams with SBOM-driven insights into software quality and licensing risks, enabling smarter vendor selection and safer software purchases. CyberSec teams – SBOM-HQ evaluates cyber security aspects of purchased software and monitors new vulnerabilities that appear. ITOps – SBOM-HQ exposes software weaknesses and helps mitigate the risks. Legal and Licensing teams – SBOM-HQ delivers clear visibility into open source licenses, flags conflicts early, and provides audit-ready compliance reports. Why SBOM-HQ? SBOM-HQ is designed to support software buyers and users, not just software publishers. While most SBOM solutions stop at the software development life cycle, SBOM-HQ goes further. It empowers software consumers to continuously monitor not only what they build, but also what they buy - from design and procurement, through integration, all the way to production in their own data centers. With SBOM-HQ, transparency extends beyond development, delivering visibility and control across the entire software supply chain. To learn more about SBOM-HQ™, register for a free trial at sbomhq.com or contact Eracent today!

Who Is the Company Behind Eracent SBOM-HQ?

  • Seller: Eracent
  • Year Founded: 2000
  • HQ Location: Riegelsville, Pennsylvania
  • Twitter: @eracent
    141 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    69 employees on LinkedIn®

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

FuzzLand

FuzzLand is a Web3 security and analytics company dedicated to enhancing the safety and resilience of the blockchain ecosystem. By integrating advanced fuzzing techniques, formal verification, and artificial intelligence, FuzzLand offers automated solutions for smart contract analysis. These tools enable developers, auditors, and traders to swiftly identify and address vulnerabilities, ensuring the integrity and security of decentralized applications.

Who Is the Company Behind FuzzLand?

  • Seller: FuzzLand
  • Year Founded: 2022
  • HQ Location: Palo Alto, US
  • LinkedIn® Page: www.linkedin.com
    9 employees on LinkedIn®

Heeler

Heeler empowers application security teams to shift left with the context they need to reduce noise, accelerate remediation, and move beyond traditional vulnerability management. By combining ASPM, SCA with static and runtime context, and runtime threat modeling, Heeler transforms AppSec programs from reactive firefighting to proactive, scalable security. How Heeler Helps AppSec Teams • Reduce Noise: AppSec teams and developers are drowning in findings. Heeler delivers unified code, runtime, business and security context, reducing alert noise by up to 95%, so teams can focus on critical issues and fix what matters most. • Fix Remediation: Remediation is broken. Most effort is spent reaching a fix—not implementing it. Heeler automates the remediation lifecycle, cutting effort and time, enabling AppSec teams to scale alongside engineering. • Move Beyond Vulnerabilities: With Heeler, continuous runtime threat modeling becomes a reality. Decompose running applications, track changes, compare deployments, and stop risks in real time—all before they reach production. Why Heeler is Essential Modern applications are more complex and dynamic than ever, expanding attack surfaces and making end-to-end security modeling nearly impossible without the right tools. Heeler bridges this gap, addressing the root causes of unscalable AppSec programs: • Lack of Context: Disparate data silos make understanding application behavior and identifying risks challenging. • Labor-Intensive Processes: Without unified context, security efforts are manual, unscalable, and push risk identification too far right. • Firefighting Mode: Security and engineering teams are trapped addressing too many findings and often focus their time on the wrong threats, leaving no bandwidth for secure-by-design initiatives. Key Capabilities • ProductDNA (Unified Context): Automates a real-time service catalog, mapping changesets to deployments and modeling every service with integrated code, runtime, business, and security context. • Runtime Threat Modeling: Enables continuous threat modeling with tools to decompose applications, track changes, compare deployments, and uncover risks in real time. • ASPM: Heeler reduces alert noise by up to 95% and automates remediation workflows, scaling security seamlessly with engineering demands. • SCA with Static and Runtime Context: Combines static and runtime data with business and deployment context, delivering next-gen SCA that prioritizes what matters, strengthens security, and simplifies AppSec workflows. Heeler ensures AppSec teams and developers have the context they need to shift left and build secure-by-design applications—effortlessly.

Who Is the Company Behind Heeler?

Hoss

Hoss helps teams make better API-driven products. Our simple drop-in solution makes it easy to track and manage third-party APIs. Get visibility into API performance, be alerted of errors before your customers notice, reduce the amount of time spent debugging integrations, and much more.

Who Is the Company Behind Hoss?

  • Seller: Hoss
  • Year Founded: 2019
  • HQ Location: Mountain View, US
  • LinkedIn® Page: www.linkedin.com
    6 employees on LinkedIn®

IRIS

CodeEye's IRIS is a next-generation application security posture management (ASPM) platform, offers an all-in-one solution with real-time, AI-powered vulnerability and threat detection, correlation, prioritization, and remediation, easing the tension between time-to-market and risk mitigation. How it Works? Unlike traditional ASPM Solutions, IRIS detects vulnerabilities within the product development lifecycle and application infrastructure, while simultaneously providing continuous penetration testing and attack surface management to production environments. IRIS detects, correlates, provides risk-based analysis, and prioritizes application security findings in real time with automated workflows for remediation – all within one platform. IRIS seamlessly integrates with your tools, pipelines, and workflows, and supports your favourite languages. Unlock the Benefits: 1) Centralize detection, prioritization, and remediation of application threats and vulnerabilities. 2) Real-time actionable insights. 3) Establish resilient DevSecOps processes based on risk management. 4) Implement automated workflows to accelerate the identification and resolution of application risks. 5) Adopt a straightforward licensing model. 6) Ability to measure the effectiveness of your application security program. 7) Deploy within 24 hours with simplicity and ease of operation. 8) Built-in policy compliance measures. Next-Gen ASPM Managed Service In today's digital landscape, organizations grapple with deciphering and prioritizing the criticality of code and application related threats and vulnerabilities. The scarcity and expense of specialized talent capable of bridging the gap between DevOps and SecOps exacerbates this challenge. CodeEye's expertise in Application Security provides a Continuous AppSec Partner, accelerating program maturity with expert guidance and advanced technology. Our IRIS Managed Service centralizes application risk management, helping you define compliance measures and policies for prioritization and remediation, ensuring you grasp and address program risk in real-time. Key Features - Static Application Security Testing (SAST): Scans your source code for security risks before an issue goes to production. - Software Composition Analysis (SCA): Continuously monitors your code for known vulnerabilities and other security risks. - Container Scanning: Scans your container in real time for packages that contain security threats and vulnerabilities. - Dynamic Application Security Testing (DAST): Dynamically tests your production applications for vulnerabilities through simulated attacks. - Attack Surface Management (ASM): Continuously identifies, monitors, and manages external internet-connected assets for potential attack vectors and exposures. - Risk and Compliance: Continuously evaluates regulatory and internal security policy compliance using real-time and historical reporting. Vendor of Record Award CodeEye's IRIS is recognized as a Vendor of Record by the Ministry of Government and Consumer Services for IT Security Products In 2024, NIST updated its Cyber Security Framework (CSF) with significant implications for security by design and secure SDLC. Our Risk and Compliance module supports compliance with NIST CSF 2.0 throughout the software development lifecycle. Gain a comprehensive view of various scanning modules aligned with the CSF's five core functions: Identify, Protect, Detect, Respond, and Recover. Our Difference: An all-in-one platform with straight forward licensing and seamless integration. Your Results: A tool that works with your existing tools and workflows, providing security without hidden costs or complexities. Our Difference: Continuous penetration testing and attack surface management. Your Results: Identify and close gaps before an attacker exploits them across your ever-changing attack surface. Our Difference: Quick and Easy Deployment Your Results: Security monitoring and testing within 24 hours, without extensive setup or training. Our difference: Built-in risk and compliance policy module Your Results: Ensure regulatory and internal compliance with built-in policy measures aligned with industry standards like NIST CSF 2.0. Our Difference: Automated Workflows for remediation. Your Results: Rapid risk mitigation, reducing the time, effort and cost of finding and fixing vulnerabilities to ensure continuous protection. Our Difference: Real-Time, AI-powered vulnerability Your Results: Immediately identify and address security threats with precise, actionable intelligence. Our Difference: Threat and vulnerability detection, correlation, and risk-based analysis. Your Results: Simplified security operations where critical vulnerabilities are addressed first.

Who Is the Company Behind IRIS?

  • Seller: CodeEye
  • Year Founded: 2015
  • HQ Location: Toronto, CA
  • Twitter: @CodeEyeAI
    6 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    18 employees on LinkedIn®

Nullify

The post-human product security program. Nullify continuously allocates AI capacity toward the highest-impact product security work, maximizing outcomes from every engineer hour and every token spent.

Who Is the Company Behind Nullify?

  • Seller: Nullify
  • Company Website:
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    27 employees on LinkedIn®

OpenText Core Software Composition Analysis

OpenText™ Core Software Composition Analysis (Debricked) is a comprehensive solution designed to enhance open source security by automating the identification, remediation, and prevention of vulnerabilities within software applications. By integrating seamlessly into the development pipeline, it provides organizations with a swift and efficient means to manage open source components, ensuring compliance and bolstering overall security posture. Key Features and Functionality: - End-to-End Open Source Security Integration: Supports the incorporation of open source security measures throughout all phases of application development, from initial intake to final deployment. - Advanced Machine Learning for Accurate Results: Utilizes sophisticated machine learning algorithms to deliver high-quality data, resulting in more precise vulnerability detection and analysis. - Comprehensive Vulnerability Management Toolkit: Offers a suite of tools, including dynamic dashboards and support resources, tailored for developers, analysts, and team leads to effectively manage open source vulnerabilities. - Automated License Compliance: Ensures adherence to open source licenses through automated, enforceable pipeline rules, and assesses repository risk levels based on intended use. - Extensive Open Source Project Data: Provides access to data from over 40 million open source projects, offering transparency into dependencies, vulnerabilities, and licensing information. - Security, License, and Health Metrics: Delivers insights into the vitality of open source projects, identifying declining communities and highlighting popular projects with diverse maintainers to ensure longevity. - Automated Policy Compliance: Allows organizations to set policies within Open Source Select, enabling developers to immediately determine project compliance status. - CycloneDX SBOM Export: Facilitates the export of a CycloneDX Software Bill of Materials (SBOM), providing a comprehensive record of supply chain relationships among software components. - User-Friendly Dashboard: Enables quick integration, scanning, and results retrieval within minutes, offering a complete overview of all open source vulnerabilities present in the software. Primary Value and Problem Solved: OpenText Core Software Composition Analysis addresses the critical challenge of managing open source vulnerabilities that can impede development processes and compromise security. By automating the detection and remediation of these vulnerabilities, the solution empowers organizations to maintain robust security standards, ensure compliance with open source licenses, and streamline development workflows. This proactive approach not only mitigates potential security risks but also enhances the efficiency and reliability of software development initiatives.

Who Is the Company Behind OpenText Core Software Composition Analysis?

  • Seller: OpenText
  • Year Founded: 1991
  • HQ Location: Waterloo, ON
  • Twitter: @OpenText
    21,565 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    22,835 employees on LinkedIn®
  • Ownership: NASDAQ:OTEX

PrivJs Safe

PrivJs Safe blocks the installation of malicious npm packages and provides with an ESLint plugin to detect vulnerable dependencies in a project.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate PrivJs Safe?

  • Quality of Support: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind PrivJs Safe?

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of PrivJs Safe?

Protean Labs

Protean Labs is a software-as-a-service company that specializes in DevOps and DevSecOps tools. Our main offering is a powerful and easy to use tool that does Software Composition Analysis on your project's third party dependencies, checking for known CVEs and alerting you if found!

Who Is the Company Behind Protean Labs?

Sonatype Guide

AI coding assistants help teams move fast — but they operate without the context needed to choose secure, high-quality dependencies, often introducing vulnerable components and rework. Sonatype Guide fills that gap by giving AI assistants real-time open source intelligence, ensuring they select the right components so your team can move fast, safely.

Who Is the Company Behind Sonatype Guide?

  • Seller: Sonatype
  • Year Founded: 2008
  • HQ Location: Fulton, US
  • Twitter: @sonatype
    10,589 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    582 employees on LinkedIn®

Sonatype Repository Firewall

Sonatype Repository Firewall helps protect your software supply chain by blocking open source malware and other high-risk components before they enter your artifact repositories and development workflows. Repository Firewall evaluates components at the point of download using automated analysis plus policy enforcement, so risky packages can be prevented (or quarantined) before they spread across builds, teams, and environments. Key capabilities: - Detect and block known and suspicious open source malware before it reaches developers - Enforce security, license, and quality policies early, at the repository perimeter - Identify risky or malicious components already present in repositories to support cleanup and response - Provide clear, auditable policy decisions and guidance so teams understand why a component was blocked and what to use instead - Integrate with common repository managers (including Nexus Repository and JFrog Artifactory) to add protection without slowing delivery Repository Firewall is ideal for organizations that depend heavily on public registries and want a preventative control to reduce supply chain attacks, lower rework, and keep development moving with trusted components.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Sonatype Repository Firewall?

  • Quality of Support: 5.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Sonatype Repository Firewall?

  • Seller: Sonatype
  • Year Founded: 2008
  • HQ Location: Fulton, US
  • Twitter: @sonatype
    10,589 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    582 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Do G2 Reviewers Say About Sonatype Repository Firewall?

AI-generated summary from verified user reviews

Pros
  • Users value the control over security that Sonatype Repository Firewall provides, preventing unapproved components from advancing applications.
  • Users value the network security benefits of Sonatype Repository Firewall, ensuring data safety and policy enforcement.
  • Users value the protection against malicious activities that Sonatype Repository Firewall provides, ensuring data security.
Cons
  • Users note a lack of technical support expertise, requiring knowledge of SDLC, DevOps, and Nexus Repository Manager.
  • Users face inadequate learning resources with Sonatype Repository Firewall, lacking proper support and understanding of key solutions.
  • Users face challenges with poor customer support, highlighting the need for knowledgeable assistance in technical issues.

What Are Recent G2 Reviews of Sonatype Repository Firewall?

Sonatype Software Supply Chain Management

Align teams to accelerate digital innovation without sacrificing security or quality.

Who Is the Company Behind Sonatype Software Supply Chain Management?

  • Seller: Sonatype
  • Year Founded: 2008
  • HQ Location: Fulton, US
  • Twitter: @sonatype
    10,589 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    582 employees on LinkedIn®

Sparrow Enterprise

Sparrow Enterprise is an integrated, on-premises application security solution that combines Static Application Security Testing (SAST), Dynamic Application Security Testing (DAST), and Software Composition Analysis (SCA) in a single platform. Designed for organizations that require robust security and full control over their environment, Sparrow Enterprise enables comprehensive detection and management of vulnerabilities in source code, web applications, and open source components. Its unified interface and workflow automation support systematic risk management and compliance throughout the Software Development Life Cycle (SDLC).

Who Is the Company Behind Sparrow Enterprise?

Adam Crivello
AC
Researched and written by Adam Crivello
Updated October 3, 2024