Best Software Composition Analysis Tools - Page 4

How Many Software Composition Analysis Tools Products Does G2 Track?

Total Products under this Category: 79

Category Stats (Nov 2026)

  • Average Rating: 4.48/5 (↓0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: DigiCert ONE (+0.99%) - Among all products in this category, DigiCert ONE recorded the largest rating increase compared to last month

Last updated: November 02, 2026

How Does G2 Rank Software Composition Analysis Tools Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,800+ Authentic Reviews
  • 79+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

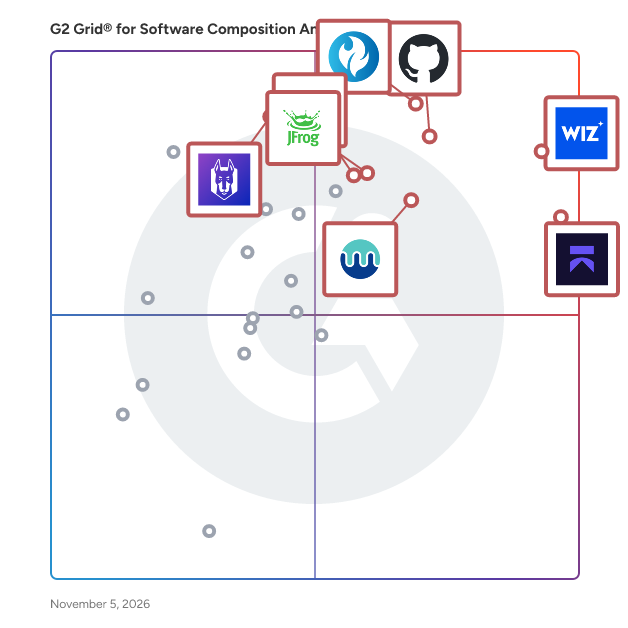
G2 Grid® for Software Composition Analysis Tools

G2 Grid® for Software Composition Analysis Tools plotting products by satisfaction and market presence

Highlighted products: Wiz, Aikido Security, HCL AppScan, GitHub, Mend.io, JFrog, DigiCert ONE, and Snyk.

Underlying data: [Grid® JSON](https://www.g2.com/categories/software-composition-analysis/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=aikido-security&focus%5B%5D=hcl-appscan&focus%5B%5D=github&focus%5B%5D=mend-io&focus%5B%5D=jfrog-2024-03-28&focus%5B%5D=digicert-one&focus%5B%5D=snyk)

Qwiet AI

Qwiet AI delivers comprehensive application security by combining agentic AI with advanced code analysis. In a single scan, the platform provides uniquely accurate SAST, SCA, SBOM, secrets detection, and container analysis that helps dev and security teams find and fix vulnerabilities faster. With its proprietary Code Property Graph (CPG) technology and AI/ML models, Qwiet AI achieves up to 95% reduction in false positives compared to traditional tools, while offering contextual AutoFix that understands the unique context of your code, even across complex enterprise applications. Q: What makes Qwiet AI different from other AppSec solutions? A: Qwiet AI stands out through its agentic AI approach, which enables autonomous vulnerability detection and remediation. The platform's Code Property Graph technology allows for deeper code analysis and more accurate vulnerability detection, resulting in dramatically fewer false positives than traditional tools. This advanced technology enables the platform to understand code relationships and context at a deeper level, leading to precise vuln detection and contextually appropriate fixes. Q: What security capabilities does the platform include? A: The platform provides comprehensive security coverage including: - Static Application Security Testing (SAST) using a patented CPG-based approach, for vuln detection that is objectively the fastest and most accurate available per the OWASP benchmark - Software Composition Analysis (SCA) for third-party dependency scanning and vulnerability detection in open source components - Automated SBOM generation for supply chain transparency and compliance requirements - Advanced secrets detection to prevent credential exposure and secure sensitive information - Container security analysis built in - AI-powered AutoFix for automated vulnerability remediation with contextually aware patches, powered by the CPG and a custom AI/ML engine with its own LLM - Custom rule creation capabilities for organization-specific security requirements Q: How does Qwiet AI improve development workflows? A: Qwiet AI integrates seamlessly into existing CI/CD pipelines and developer workflows. The platform's speed (up to 40x faster than traditional scanners) and accuracy mean developers spend less time investigating false positives and more time coding. The AutoFix capability helps developers resolve issues quickly with AI-generated patches that are contextually aware and tailored to your codebase. Additionally, the platform provides IDE integrations and pull request analysis to catch vulnerabilities early in the development process. Q: What do customers think? A: Qwiet AI provides enterprise-grade support with dedicated customer success representatives and technical account managers. The platform consistently receives high marks for customer support, with a 97% "would recommend" rate in Gartner's Voice of the Customer. Customers receive comprehensive onboarding assistance, ongoing technical support, and regular check-ins to ensure successful implementation and adoption. Q: How can I get started with Qwiet AI? A: Qwiet AI offers self-service access, self-guided demos, and AE-guided demos, depending on your needs. You can request a personalized demo through the company website at qwiet.ai to see how the platform addresses their specific security challenges. You can also sign up for self-service access through the web site, or access documentation and integration guides there.

Average Rating: 4.8/5.0

Total Reviews: 3

How Do G2 Users Rate Qwiet AI?

  • Quality of Support: 10.0/10 (Category avg: 9.0/10)
  • Language Support: 8.3/10 (Category avg: 8.5/10)
  • Continuous Monitoring: 10.0/10 (Category avg: 8.8/10)
  • Integration: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Qwiet AI?

  • Seller: Qwiet AI
  • HQ Location: San Jose, US
  • Twitter: @ShiftLeftInc
    1,164 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    14 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 67% Large, 33% Small

What Do G2 Reviewers Say About Qwiet AI?

AI-generated summary from verified user reviews

Pros
  • Users value the collaborative support from Qwiet AI, facilitating seamless integration into CI/CD pipelines.
  • Users commend the highly responsive customer support of Qwiet AI, enhancing their integration experience significantly.
  • Users value the easy integrations of Qwiet AI, facilitating seamless incorporation into CI/CD pipelines effortlessly.
  • Users value the thorough documentation of Qwiet AI, facilitating seamless integration into CI/CD pipelines.
  • Users value the strong team collaboration facilitated by Qwiet AI, enhancing integration and support for their workflows.
Cons
  • Users find the command line difficulty frustrating, as custom policies require technical expertise without a user-friendly interface.
  • Users express frustration over limited customization as custom policies can only be created via CLI, not a user interface.
  • Users are frustrated by the limited features of Qwiet AI, lacking a user interface for custom policies.
  • Users find the lack of user interface for policy creation limits accessibility and ease of use in Qwiet AI.

What Are Recent G2 Reviews of Qwiet AI?

Scanmycode.io

Code and Infra Security for Small and medium business A simple and powerful Cloudnative and Code Security and Compliance software for small businesses, agencies and startups

Average Rating: 5.0/5.0

Total Reviews: 2

Who Is the Company Behind Scanmycode.io?

Who Uses This Product?

  • Company Size: 50% Medium, 50% Small

What Are Recent G2 Reviews of Scanmycode.io?

SCANOSS

SCANOSS is the industry-leading open source software intelligence provider, offering the largest database of open source information available. SCANOSS delivers cutting-edge tools and services that help businesses and developers detect, manage, and secure their open source components. By identifying license obligations, security vulnerabilities, and other risk concerns, SCANOSS ensures that organisations can harness the power of open source safely and securely throughout the development pipeline.

Average Rating: 4.3/5.0

Total Reviews: 2

Who Is the Company Behind SCANOSS?

  • Seller: SCANOSS
  • Year Founded: 2021
  • HQ Location: Madrid, ES
  • LinkedIn® Page: www.linkedin.com
    25 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of SCANOSS?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Apiiro

Apiiro is the leader in application security posture management (ASPM), unifying risk visibility, prioritization, and remediation with deep code analysis and runtime context. Get complete application and risk visibility: Apiiro takes a deep, code-based approach to ASPM. Its Cloud Application Security Platform analyzes source code and pulls in runtime context to build a continuous, graph-based inventory of application and software supply chain components. Prioritize with code-to-runtime context: With its proprietary Risk Graph™️, Apiiro contextualizes security alerts from third-party tools and native security solutions based on the likelihood and impact of risk to uniquely minimize alert backlogs and triage time by 95%. Fix faster and prevent risks that matter: By tying risks to code owners, providing LLM-enriched remediation guidance, and embedding risk-based guardrails directly into developer tools and workflows, Apiiro improves remediation times (MTTR) by up to 85%. Apiiro's native security solutions include API security testing in code, secrets detection and validation, software bill of materials (SBOM) generation, sensitive data exposure prevention, software composition analysis (SCA), and CI/CD and SCM security.

Average Rating: 4.8/5.0

Total Reviews: 2

How Do G2 Users Rate Apiiro?

  • Quality of Support: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Apiiro?

  • Seller: Apiiro
  • Year Founded: 2019
  • HQ Location: New York, New York, United States
  • Twitter: @apiiroSecurity
    7,397 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    135 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of Apiiro?

What Are G2 Users Discussing About Apiiro?

CodeSentry

CodeSentry is GrammaTech’s binary Software Composition Analysis (SCA) solution which achieves deep scalable analysis without the need for source code and is suitable for enterprise-wide adoption. By enabling developers to interrogate software at the binary level for both open-source software and the third-party software that is now so commonly used, GrammaTech CodeSentry provides visibility into component vulnerabilities after the build process to identify risk. This helps software developers solve challenging issues throughout the software development life cycle (SDLC), and protect mission-critical software and devices from failure and cyberattack. GrammaTech CodeSentry is a multi- programming language SCA solution supporting binary analysis across numerous formats such as endpoints, mobile devices, embedded systems, and firmware. CodeSentry uses multiple component matching algorithms that provide speed and accuracy of detection across different Instruction Set Architectures (ISAs), compilers, and interpretive languages such as JavaScript and Python. CodeSentry allows security professionals to measure and manage the risk associated with open-source vulnerabilities in third-party software quickly and easily, and generates detailed Software Bill of Materials (SBOM) for release support and compliance.

Average Rating: 4.5/5.0

Total Reviews: 1

Who Is the Company Behind CodeSentry?

  • Seller: CodeSecure
  • Year Founded: 1988
  • HQ Location: Ithaca, NY
  • Twitter: @GrammaTech
    684 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    47 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of CodeSentry?

FlexNet Code Insight

An on-premise Software Composition Analysis solution using automated scans to help organizations understand their license compliance and security vulnerability exposure to open source packages. FlexNet Code Insight easily provides users with a Software Bill of Materials from across the software supply chain and offers continuous monitoring of assets, proactive vulnerability alerts, and recommended remediation actions. The solution helps development teams deliver secure products to customers while protecting IP and avoiding reputation damaging litigation.

Average Rating: 4.0/5.0

Total Reviews: 1

How Do G2 Users Rate FlexNet Code Insight?

  • Quality of Support: 8.3/10 (Category avg: 9.0/10)

Who Is the Company Behind FlexNet Code Insight?

  • Seller: Revenera
  • HQ Location: Itasca, IL
  • Twitter: @GetRevenera
    6,331 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    161 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of FlexNet Code Insight?

Fluid Attacks

Implement Fluid Attacks' comprehensive, AI-powered solution into your SDLC and develop secure software without delays. As an all-in-one solution, Fluid Attacks accurately finds and helps you remediate vulnerabilities throughout the SDLC and ensures secure software development. The solution integrates its AI, automated tool, and team of pentesters to perform SAST, SCA, DAST, CSPM, SCR, PtaaS and RE to help you improve your security posture. This way, Fluid Attacks delivers accurate knowledge of the security status of your application. This means security goes alongside innovation without hindering your speed. Fluid Attacks provides you with expert knowledge about vulnerabilities and support options that enable you to remediate the security issues in your application.

Average Rating: 4.5/5.0

Total Reviews: 1

How Do G2 Users Rate Fluid Attacks?

  • Quality of Support: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Fluid Attacks?

  • Seller: Fluid Attacks
  • Year Founded: 2001
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    181 employees on LinkedIn®
  • Phone: +14154042154

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Fluid Attacks?

Invicti

Invicti (formerly known as Netsparker) is an enterprise application and API security testing platform that helps organizations secure thousands of web applications and APIs at scale while dramatically reducing the risk of attack. Combining advanced DAST and IAST capabilities in a single platform, Invicti enables security teams to continuously identify, prioritize, and remediate vulnerabilities across complex modern environments with confidence and automation. With Invicti, security teams can: - Automate application security testing workflows and save hundreds of hours every month - Discover and secure all web applications and APIs, including forgotten, unmanaged, and shadow assets - Deliver actionable, developer-friendly feedback that helps teams remediate vulnerabilities faster and build more secure code over time - Reduce false positives with proof-based scanning technology that validates exploitable vulnerabilities - Scale application security programs across large enterprises without slowing development teams - Integrate security seamlessly into existing DevSecOps and CI/CD workflows Built for organizations with the most demanding security requirements, Invicti empowers teams to confidently secure their entire attack surface with accuracy, scalability, and automation.

Average Rating: 4.5/5.0

Total Reviews: 69

How Do G2 Users Rate Invicti?

  • Quality of Support: 8.9/10 (Category avg: 9.0/10)
  • Language Support: 10.0/10 (Category avg: 8.5/10)
  • Integration: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Invicti?

  • Seller: Invicti Security
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Austin, Texas
  • Twitter: @InvictiSecurity
    2,557 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    326 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 46% Large, 29% Medium

What Do G2 Reviewers Say About Invicti?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Invicti, facilitating quick setup and effective vulnerability scanning in their workflow.
  • Users value the quick and easy scanning technology of Invicti, enhancing workflow efficiency and accuracy in vulnerability detection.
  • Users value the simplicity and integration of Invicti, enhancing security measures through user-friendly report generation and detailed views.
  • Users value the easy-to-read and well-formatted reports from Invicti, enhancing efficiency and supporting ISO certification needs.
  • Users value the high accuracy and ease of use in Invicti's vulnerability detection, effectively identifying true issues.
Cons
  • Users find the customer support lacking, often experiencing slow responses and inadequate technical assistance.
  • Users experience slow performance during scans and setups, impacting overall efficiency and satisfaction.
  • Users experience slow scanning issues with Invicti, often leading to frustrating delays during the scanning process.
  • Users face API scanning issues with Invicti, limiting its effectiveness for their specific needs despite decent support.
  • Users find the complex setup of Invicti challenging initially, hindering their ability to quickly navigate configurations.

What Are Recent G2 Reviews of Invicti?

What Are G2 Users Discussing About Invicti?

ReversingLabs Spectra Intelligence

ReversingLabs is the trusted name in file and software security. We provide the modern cybersecurity platform to verify and deliver safe binaries. Trusted by the Fortune 500 and leading cybersecurity vendors, RL Spectra Core powers the software supply chain and file security insights, tracking over 422 billion searchable files with the ability to deconstruct full software binaries in seconds to minutes. Only ReversingLabs provides that final exam to determine whether a single file or full software binary presents a risk to your organization and your customers.

Average Rating: 4.7/5.0

Total Reviews: 10

How Do G2 Users Rate ReversingLabs Spectra Intelligence?

  • Quality of Support: 9.4/10 (Category avg: 9.0/10)

Who Is the Company Behind ReversingLabs Spectra Intelligence?

  • Seller: ReversingLabs
  • Year Founded: 2009
  • HQ Location: Cambridge, US
  • Twitter: @ReversingLabs
    7,022 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    323 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 80% Small, 10% Medium

What Do G2 Reviewers Say About ReversingLabs Spectra Intelligence?

AI-generated summary from verified user reviews

Pros
  • Users commend the accuracy of information offered by ReversingLabs, utilizing an extensive repository of files for effective risk management.
  • Users commend the excellent customer support from ReversingLabs, enhancing their onboarding and overall experience effectively.
  • Users commend the efficient onboarding process of ReversingLabs, facilitating a seamless and effective transition to their services.
  • Users appreciate the effective prioritization of risk management with ReversingLabs, enhancing their security processes significantly.
  • Users commend the high reliability of ReversingLabs, citing exceptional support and a vast repository of files.
Cons
  • Users find the endpoints for checking usage confusing, which complicates their overall experience with the product.
  • Users find the confusing interface for usage endpoints makes it difficult to navigate the product effectively.
  • Users find the navigation issues related to usage endpoints somewhat confusing, impacting their overall experience.
  • Users feel the UI could be nicer, yet it doesn't hinder the overall functionality of ReversingLabs.

What Are Recent G2 Reviews of ReversingLabs Spectra Intelligence?

Black Duck Security Composition Analysis (SCA)

Black Duck® SCA helps teams manage the security, quality, and license compliance risks in open source and third-party code.

Who Is the Company Behind Black Duck Security Composition Analysis (SCA)?

  • Seller: Black Duck
  • Year Founded: 2024
  • HQ Location: Burlington, US
  • LinkedIn® Page: www.linkedin.com
    1,317 employees on LinkedIn®

CAST SBOM Manager

CAST SBOM Manager enables users to automatically create, customize, and maintain Software Bill of Materials (SBOMs) with the ultimate level of control and flexibility. It detects open source dependencies and related risks (vulnerabilities and security advisories, licenses, obsolescence) directly from scanning source code, and allows you to create and maintain SBOM metadata over time (proprietary components, custom licenses, vulnerabilities) and much more.

Who Is the Company Behind CAST SBOM Manager?

  • Seller: CAST
  • Year Founded: 1990
  • HQ Location: New York
  • Twitter: @SW_Intelligence
    1,887 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,270 employees on LinkedIn®
  • Ownership: Bridgepoint

CodeAnt AI Code Security Platform

CodeAnt AI covers code, cloud, and runtime security in one platform. Code security: AI SAST detects vulnerabilities during development and establishes which are reachable before surfacing them, with 95% fewer false positives than pattern-matching scanners and findings mapped to OWASP and CWE. Software composition analysis identifies vulnerable and malicious packages across direct and transitive dependencies, protecting more than 2 billion monthly package downloads. Secret detection scans full commit history for hardcoded credentials, API keys, and tokens. SBOM generation runs continuously across every repository. Cloud security: Cloud security posture management detects misconfigurations across your cloud accounts and maps them to compliance frameworks. Threat detection surfaces active adversary behavior in the cloud environment. Container scanning inspects images and registries for vulnerable packages and embedded secrets. Virtual machine scanning covers running workloads and their installed dependencies. Runtime security: Dynamic application security testing probes running applications for exploitable behavior. Attack surface management continuously discovers exposed assets, domains, and services outside the perimeter. Grey box AI pentesting runs more than 500 AI agents against that surface, chaining weaknesses into complete attack paths. Remediation arrives as a fix inside the pull request. Continuous AI learning draws on more than 1 billion lines of codebase history. Our security research team has discovered over 150 CVEs in production software, and CodeAnt has pentested more than 1,000 companies.

Who Is the Company Behind CodeAnt AI Code Security Platform?

  • Seller: CodeAnt AI
  • Year Founded: 2023
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    22 employees on LinkedIn®

Cycode

Cycode’s AI-Native Application Security Platform unites security and development teams with actionable context from code to runtime to identify, prioritize, and fix the software risks that matter. Powered by proprietary scanners, third-party integrations, and the Context Intelligence Graph (CIG), Cycode delivers unified, correlated insight across the Software Factory. Its unique ability to sense, reason, and act with context in the AI-Era comes from its foundational convergence of AST, ASPM, and Software Supply Chain Security—purpose-built to secure both AI- and human-generated code.

Average Rating: 4.0/5.0

Total Reviews: 2

How Do G2 Users Rate Cycode?

  • Quality of Support: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Cycode?

  • Seller: Cycode
  • Year Founded: 2019
  • HQ Location: New York, New York, United States
  • LinkedIn® Page: www.linkedin.com
    149 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 67% Medium, 33% Large

What Are Recent G2 Reviews of Cycode?

Depna

Depna is a dependency security scanner that finds known vulnerabilities without needing access to your source code. Instead of connecting to your repository, you upload a single dependency file such as package.json, requirements.txt or pom.xml and get a full report in under 2 minutes. This no repo access model fits teams working under strict security policies. The file is processed in memory then deleted right after the scan. It covers 8 ecosystems and ranks findings by severity from Critical to Low, with the CVE, the CVSS score and the exact fixed version for each one. Lock files add full transitive coverage. Every finding is explained by AI in three layers for engineers, managers and executives, and Depna generates audit ready ISO 27001 and SOC 2 Type II PDF reports that you can white label. Scan from the dashboard or add one command to your CI/CD pipeline for GitHub Actions, GitLab CI or Bitbucket. Get alerts in Slack, Teams, Discord or email when something critical lands. Built for startups and small teams, with a free plan and paid tiers that scale by projects.

Who Is the Company Behind Depna?

  • Seller: Depna
  • Year Founded: 2001
  • HQ Location: Tehran, IR
  • LinkedIn® Page: www.linkedin.com
    39 employees on LinkedIn®

depthfirst

depthfirst is an AI-native security platform offering continuous cyber defense. It reasons through code, infrastructure, and business logic to understand how systems work and build a threat model. That context helps depthfirst find and verify vulnerabilities, prioritize what is exploitable, block malicious dependencies, and help teams remediate security issues. The platform covers three broad areas: Code Security reviews repositories and pull requests for vulnerabilities, secrets, insecure dependencies, and business-logic flaws. It connects findings to application context so security and engineering teams can focus on the issues that matter and fix them in the code. Agentic Pentesting uses autonomous agents to attack running applications like a team of elite security researchers. It supports black-, gray-, and white-box testing for new vulnerability discovery, but can also confirm whether code scan findings are exploitable and replay attacks to verify that fixes work. Dependency Firewall blocks malicious packages before installation to prevent supply chain attacks. It applies a shared security policy at the artifact-repository layer and on managed devices, protecting both people and AI agents. depthfirst routes each task to the best-suited AI model to optimize performance and cost. It also includes dfs-large1, depthfirst’s own frontier cybersecurity model, which performs comparably to frontier general-purpose models on vulnerability detection tasks at a fraction of the cost. depthfirst works with enterprises such as ServiceNow, government agencies, and innovative AI and fintech companies including Lovable, Supabase, Ripple, Listen Labs, fal, and MoonPay.

Who Is the Company Behind depthfirst?

Adam Crivello
AC
Researched and written by Adam Crivello
Updated October 3, 2024